News related to
flaw

Donald Trump is poised to repeat a pattern of missteps that have troubled his foreign policy approach throughout his presidency. His handling of international relations often seems to confuse the appropriate balance between clarity and ambiguity, with significant consequences for both the United States and its global partners. This issue will come into sharp focus during his upcoming meeting with Saudi Arabia’s Crown Prince Mohammed bin Salman […]

SINGAPORE – Media OutReach Newswire – 17 November 2025 – Madame Tussauds Singapore is excited to announce the arrival of beloved actor Ahn Hyo Seop’s wax figure on Tuesday, 2 December 2025. Known for captivating audiences with his performances in popular dramas and movies like “Business Proposal”, “Omniscient Reader: The Prophet” and “A Time Called You,” Ahn Hyo Seop has established himself as a true heartthrob among […]

The shift towards subscription-based streaming and the rise in unauthorised distribution is exposing fundamental flaws in how consumers acquire digital media. Many users believe they “own” films, music or books that they purchase online, but industry analysts say what they actually hold is a license to access content under strict terms and conditions. One expert writes: “Most of us don’t control the files, formats, keys and servers. […]

European authorities’ push to regulate stablecoins under the Markets in Crypto‑Assets Regulation has brought order to a previously opaque market, but analysts warn it might also be sowing the seeds of a fresh risk for financial stability. The regulation mandates that issuers of e-money tokens and asset-referenced tokens must hold matching reserves, provide transparency on custody and investment of assets, and submit to governance and wind-down planning. […]

A study by the European Broadcasting Union in collaboration with the BBC has found that leading artificial-intelligence news assistants deliver flawed responses in nearly half of the cases evaluated. The analysis assessed over 3,000 replies from major tools including ChatGPT, Copilot, Gemini and Perplexity, across 14 languages and involving 22 public-service media organisations from 18 countries. According to the report, 45 per cent of all answers contained […]

HONG KONG / SINGAPORE – Media OutReach Newswire – 23 October 2025 – Regent Hong Kong has etched its name in hospitality history by becoming the first and only hotel in Asia with the best views to secure a flawless 100/100 rating from The Most Perfect View Certified Program. This recognition cements the luxury waterfront hotel’s reputation as the hotel with the best views of Victoria Harbour, […]

Multiple posts flooding social media demand accountability—users call for a regulator-led probe, the CEO’s arrest, and deep scrutiny of Binance’s internal systems. The outcry follows recent chaos around synthetic tokens USDe, BNSOL, and wBETH, which lost their pegs on Binance amid massive liquidations. Compensation is flowing, but the narrative now centers on whether the crash was a desperate scramble or a deeply orchestrated exploit.

When Binance announced it would pay $283 million to users affected by depegging and associated liquidations, it framed the move as a goodwill gesture to restore stability. The payout applies to users whose positions used USDe, BNSOL, or wBETH as collateral between 21:36 UTC and 22:16 UTC on October 10. The exchange said compensation covers the difference between liquidation price and market price at 00:00 UTC on October 11, plus fees. It also promised to improve its risk-control systems and change how its indices weigh collateral assets..

These remedial steps, however, have not assuaged skeptics. Analysts at Uphold argued the event was no accident: they see the crash as a coordinated exploit of a vulnerability in Binance’s unified margin system, in which USDe, BNSOL, and wBETH were accepted as collateral. Because the exchange valued collateral based on internal order-book data instead of aggregated external prices, they say the system could be manipulated from within the venue itself. That, they believe, allowed an attacker to locally crash prices and trigger a cascade of liquidations.

One widely cited theory points to timing. Binance announced on October 6 it would update its pricing mechanisms to rely more on external oracles, with the changes scheduled for October 14. The incident happened on October 10—right in the middle of that eight-day window. In effect, critics argue, the exchange had acknowledged the flaw but had not yet implemented the fix, leaving a vulnerability no one should have touched. On-chain data shows USDe dropped to as low as $0.65 on Binance while remaining near parity across other markets, and wBETH and BNSOL showed similar divergence. The fact that only these three tokens—and only on Binance—were massively disrupted raises the specter that this was a targeted strike, not a systemic weak spot.

The theory gains further support from social media researchers. A thread by a user called “ElonTrades” describes how roughly $60–90 million of USDe was dumped on Binance to manipulate its order book, triggering forced liquidations in unified-account positions. That thread also links to outsized short positions opened elsewhere in anticipation of a broad market drop. Combined, the strategy would allow the attacker to profit while setting off mayhem across crypto markets.

Binance has rejected claims of an external exploit. In its public statement, the company argues that extreme market volatility predated the depegs, and that local platform issues amplified rather than initiated the crash. It also suggests some of the price distortions stemmed from interface display glitches—tokens with very small values were rendered as zero on users’ screens—while others reflect execution of long-dormant limit orders. The company contends liquidation volume occurring on its platform was only a fraction of broader market activity.

Even some industry voices have pushed back against blanket condemnation of Binance. One analyst told reporters that attributing the crash entirely to internal failure is premature, and that extreme leverage and macro market turmoil may have interacted with, not originated from, the exchange’s anomalies.

Yet the optics are harsh and the damage is real. The crypto community remains intensely uneasy. Many traders point to how precisely the exploit—or crash—focused on three collateral tokens, how it preceded a planned patch, and how quickly the stains were cleaned up by compensation. To many, the $283 million seems less like accountability than a strategic PR move to calm markets and buy time.

BNB, the exchange’s native token, soared after the compensation announcement, reaching a high near $1,370. That rally suggests some market participants interpreted the payout as a signal that Binance could backstop risks if needed. But it has not quelled deeper anxieties: users are now demanding full transparency about trades, collateral decisions, and the CEO’s role in risk oversight.

Amanda, a margin trader who lost funds in the incident, told crypto forums: “This wasn’t a market tantrum. The order flow was too precise, too surgical. It felt like someone pulled the plug on us.” Other users posted examples of margin calls executed within fractions of seconds after the depeg, with little time or warning to react.

The sequence of events presents too many coincidences: a pricing flaw known and scheduled for repair, large collateral-related token dumps executed mid-window, massive liquidations cascading in an insular system, and a rapid compensation move. Taken together, the evidence aligns with a narrative of design-level risk exploited rather than location-level chaos.

If the worst scenario proves true—that Binance’s unified margin design was manipulable from inside its own infrastructure—the implications ripple far beyond a single crash. Centralized exchanges, hailed for their convenience and liquidity, might now be exposed as fragile ecosystems. Traders could demand stricter oversight, regulators more frequent audits, and entire collateral frameworks could be reassessed.


Advertisements

Deloitte Australia has agreed to partially refund AU$440,000 to the federal government after a commissioned report attributed to it was found to include fabricated citations, invented legal quotations, and other inaccuracies. The firm disclosed that the report’s drafting had involved the use of a generative AI system, prompting sharp debate over how much control and transparency clients should demand when consultants deploy such tools in high-stakes settings. […]

Deloitte has agreed to repay a portion of its contract with the Australian government following the discovery of errors generated by artificial intelligence in a series of reports. The company acknowledged the involvement of Azure OpenAI, a generative AI language system, in producing the erroneous documents, which prompted a review of its practices and the government’s decision to seek financial restitution. The AI errors were identified in […]

The U. S. Cybersecurity and Infrastructure Security Agency has designated CVE-2021-43226, a privilege-escalation vulnerability in Microsoft’s Common Log File System driver, as actively exploited and added it to its Known Exploited Vulnerabilities catalog. The flaw allows a local, authenticated user to bypass security controls and elevate privileges to the SYSTEM level—a shift that can lead to full system compromise. Microsoft rates the vulnerability with a CVSS 3.1 […]

Broadcom has issued patches for a VMware vulnerability—CVE-2025-41244—that was already under exploitation by a China-linked hacking group, but failed to disclose that fact in its public advisory. The flaw allows a non-administrative user in a virtual machine to escalate privileges to root, provided VMware Tools is installed and Aria Operations is managing the VM with the Service Discovery Management Pack enabled. Broadcom’s advisory, published on 29 September, […]

A compact secondary display called WebScreen is being promoted as a hacker-friendly add-on for gaming and creator setups, with crowdfunding underway. It is designed to perch atop a primary monitor and display notifications, stats or reminders without distracting the user from full-screen work. WebScreen emerges from HW Media Lab, conceived by Pedro Martin and Eleo Basili. It features a 1.9–2.1 inch AMOLED panel at 240×536 resolution, powered […]

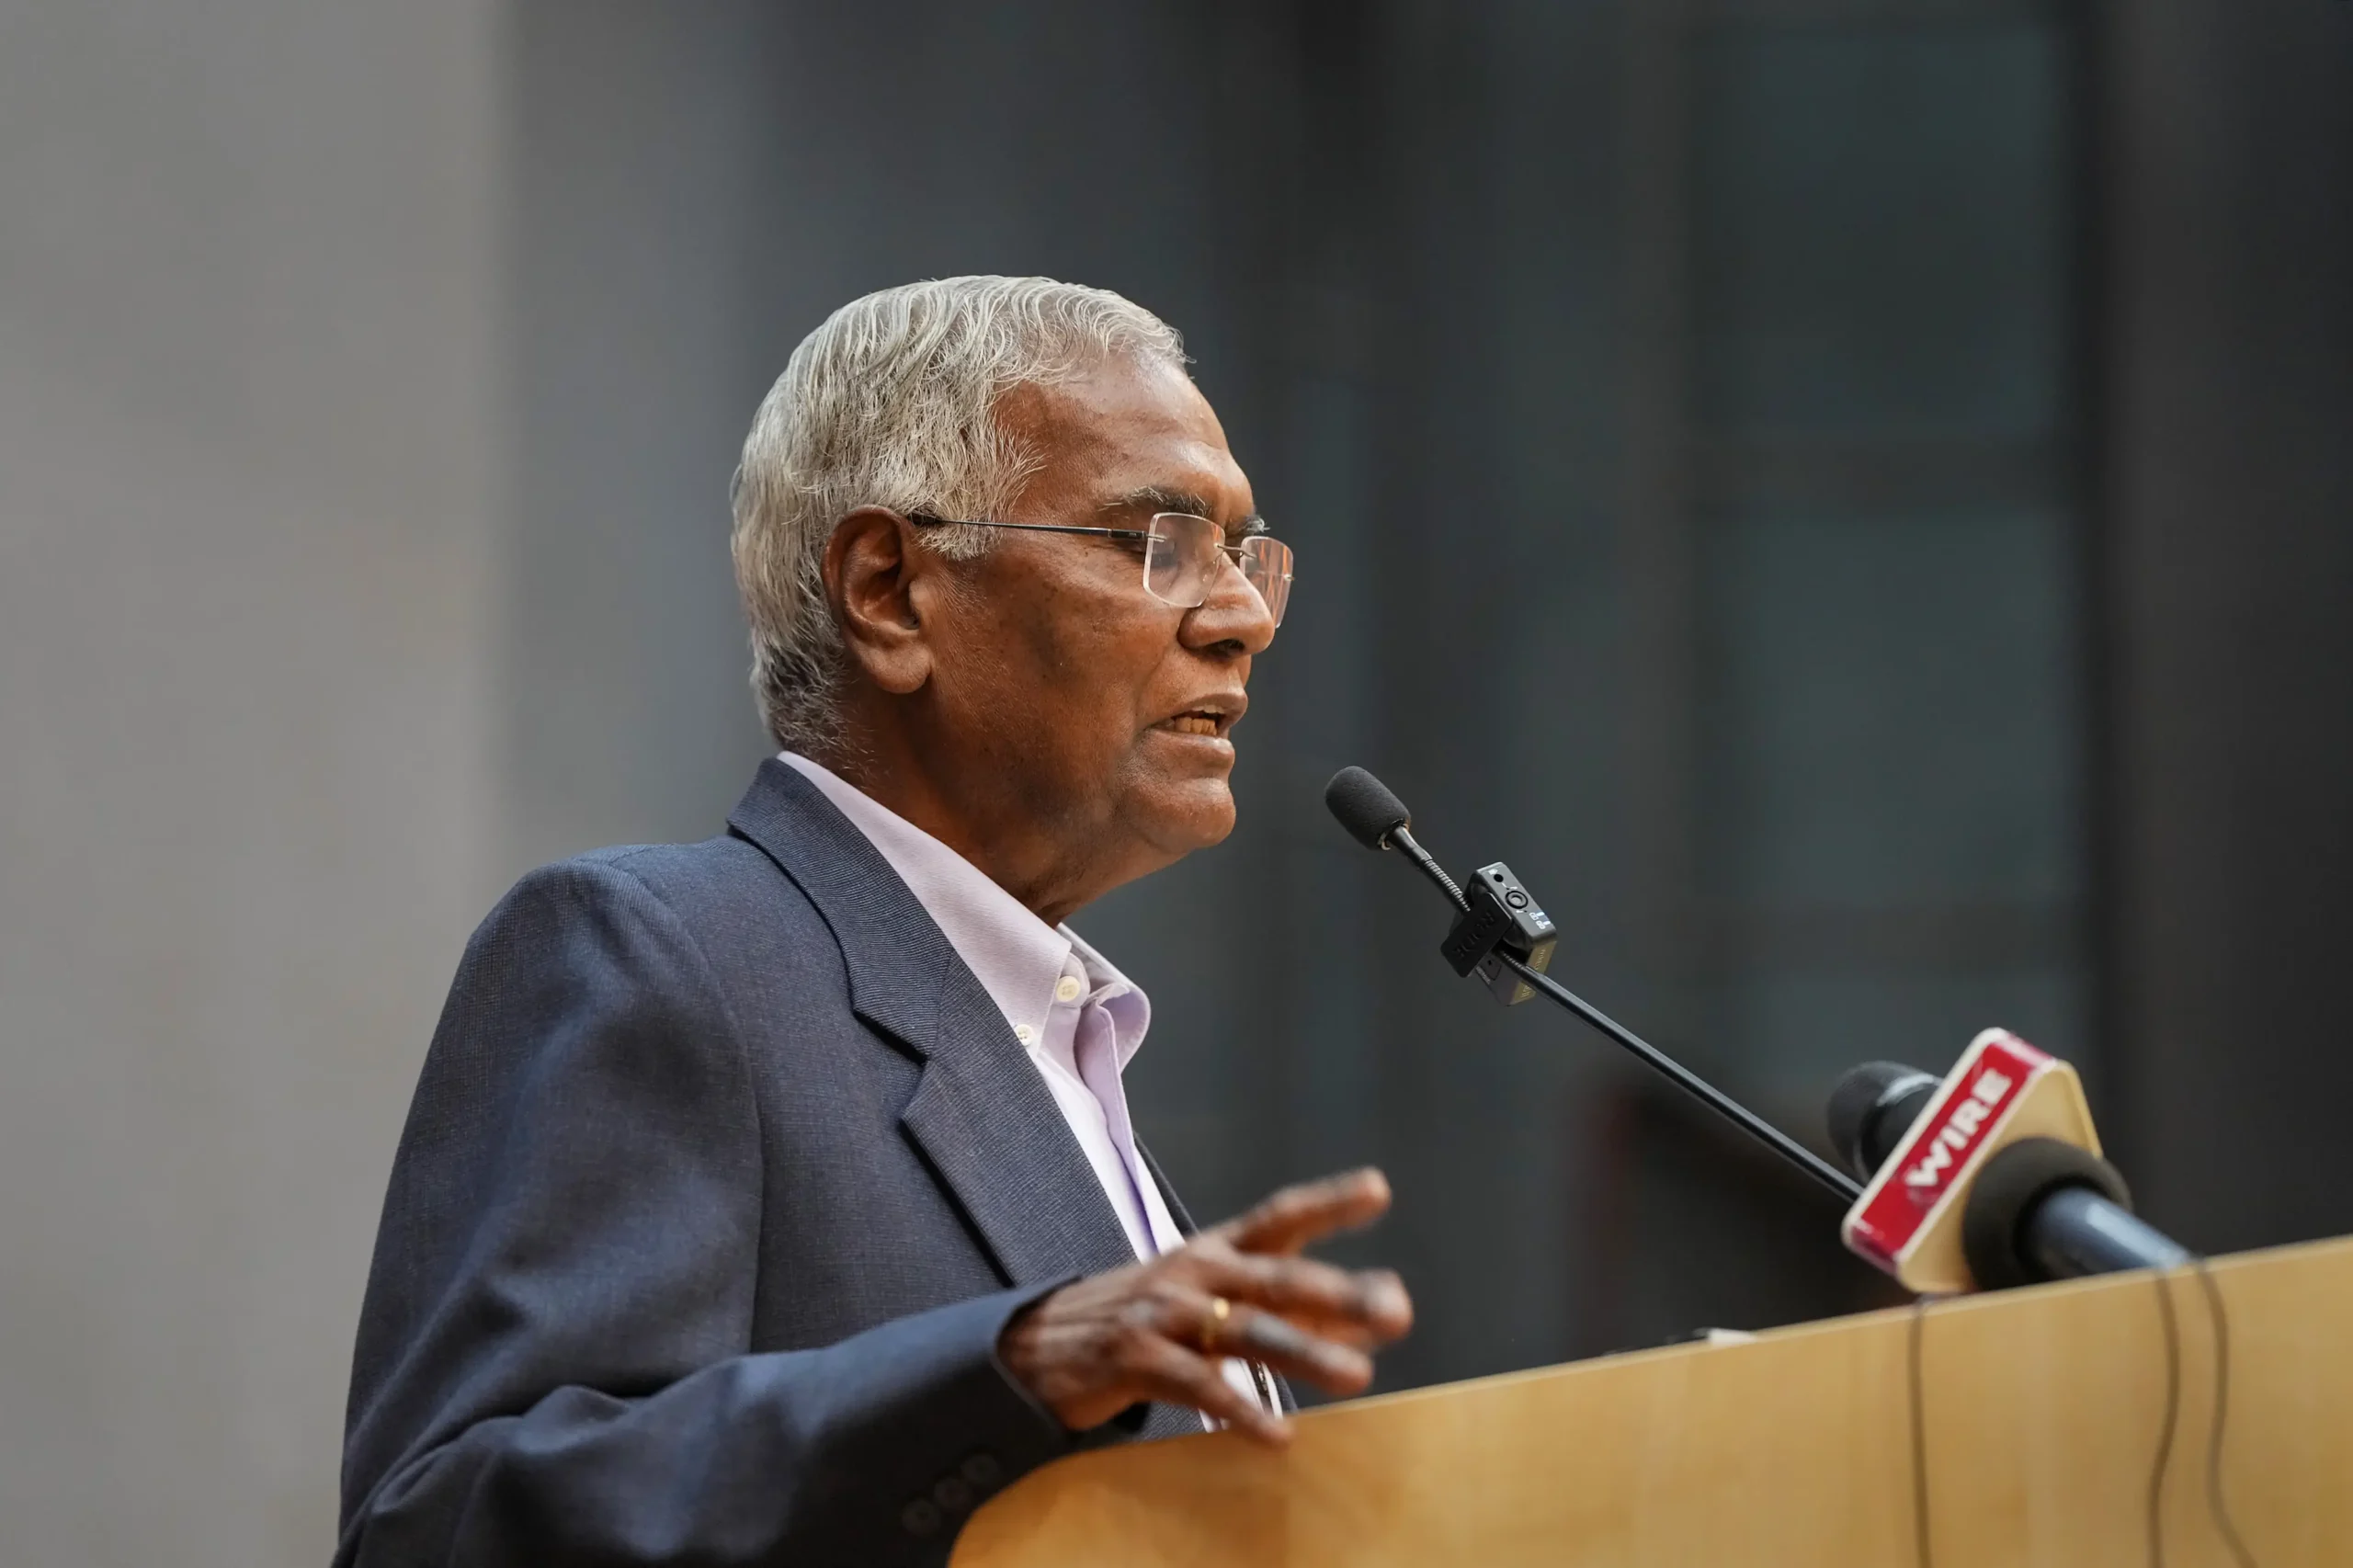
By Satyaki Chakraborty The Communist Party of India(CPI) concluded its five day Party Congress at Chandigarh on September 25 reelecting D. Raja as the general secretary of the CPI for another three year term. Raja is the first dalit leader to head the CPI in 2019 after the then party secretary S Sudhakar Reddy sought […]

The article CPI’s 25th Party Congress Elects D Raja As The General Secretary For The Third Time appeared first on Latest India news, analysis and reports on Newspack by India Press Agency).

A critical security flaw in NVIDIA’s Merlin Transformers4Rec framework allows threat actors to execute code remotely with root-level access, raising alarm across the AI ecosystem. The vulnerability, tracked as CVE-2025-23298, stems from unsafe deserialization in the model checkpoint loading routine. Attackers exploiting this flaw can submit crafted model files that, when deserialized via Python’s built-in mechanisms, trigger arbitrary command execution within the process’s context. Given that AI […]

A newly disclosed vulnerability allows threat actors to surreptitiously install arbitrary extensions on Chromium-based browsers within Windows domain environments, circumventing typical user alerts and security checks. The technique hinges on manipulating how Chrome and its derivatives store extension settings and validations in preference files. Security researchers demonstrated that by editing specific preference files in a user’s profile, an attacker can mark a malicious extension as a “component” […]

A federal judge dismissed Donald Trump’s $15 billion defamation lawsuit against The New York Times and Penguin Random House, ruling that the complaint was legally insufficient and procedurally improper. U. S. District Judge Steven Merryday criticised the 85-page document for lacking a “short and plain statement” required by the federal rules, and for including excessive laudatory language and irrelevant attacks rather than cogent legal allegations. Judge Merryday […]

The Trump administration has filed a motion in U. S. District Court, Maryland, to cancel the 2024 approval of the Maryland Offshore Wind Project established under the previous administration. It asserts that the authorisation underestimated impacts on search-and-rescue operations and commercial fisheries, and argues the permitting process was flawed under the Outer Continental Shelf Lands Act. The planned wind farm, developed by US Wind, would include 114 […]

Senator Ron Wyden is pressing the Federal Trade Commission to investigate Microsoft over what he terms its “gross cybersecurity negligence,” asserting that inherent weaknesses in Microsoft’s security framework enabled a damaging ransomware attack on a hospital system. Wyden’s letter, dated 10 September 2025, identifies how default encryption settings and flawed user-interface design played pivotal roles in the infiltration of Ascension, one of the largest non-profit health systems […]

A newly revealed flaw in Apple’s CarPlay ecosystem enables attackers to achieve remote code execution with root privileges, raising serious cybersecurity concerns for connected vehicles. Tracked as CVE-2025-24132 and identified by the Oligo Security Research team, the weakness stems from a stack-based buffer-overflow flaw in AirPlay protocol implementations used by CarPlay systems. It remains exploitable over Wi-Fi via a wormable, zero-click exploit—allowing attackers to take full control […]

Award-winning consultant Judd Labarthe launches a much-anticipated book, Swimming Downstream, challenging conventional marketing wisdom with practical, evidence-based guidance SINGAPORE – Media OutReach Newswire – 9 September 2025 – Judd Labarthe, the US-born founder of Singapore-based consultancy Planner at Large LLP, today announced the release of his début book, Swimming Downstream: How To Stop Struggling & Start Winning With Marketing That Actually Works, published by Marshall Cavendish Business. […]

European regulators have slapped Google with a €2.95 billion fine for leveraging its dominance in ad-tech to favour its own services, while President Trump has launched warnings of retaliatory trade measures—even as the €2.95 billion ad-tech sanction on Google marks the latest escalation in transatlantic friction. The European Commission’s investigation, which began in mid-2021, concluded that Google distorted competition across the 27-member bloc by prioritising its AdX […]

Rocket Lab has expanded its in‑house manufacturing strength by successfully incorporating Planetary Systems Corporation, a Maryland‑based specialist in satellite separation systems. The deal, announced on 15 November 2021 and concluded by December that year, involved $42 million in cash and 1.72 million shares of Rocket Lab stock, with an additional performance‑based stock earn‑out dependent on PSC’s performance through 2022 and 2023.

PSC, celebrated for its “Canisterized Satellite Dispenser” and Lightband separation systems, boasts a flawless 100 percent mission‑success record across more than 100 launches. Its hardware has served a broad spectrum of launch platforms—from Rocket Lab’s own Electron vehicles to those managed by SpaceX, United Launch Alliance, Northrop Grumman, and international agencies such as Arianespace, the Indian Space Research Organisation, and JAXA.

By bringing PSC into its fold, Rocket Lab enhances its vertically integrated Space Systems division, now including Photon satellite buses, Maxwell dispensers, reaction wheels, star trackers, solar solutions, flight software, and the newly added separation hardware. PSC will continue operations in Maryland under the leadership of Mike Whalen as CEO, with founder Walter Holemans remaining chief engineer.

Chunked behind this strategic move is Rocket Lab’s intent to streamline the satellite deployment value chain, offering customers a one‑stop solution—from launch services to the final separation of payloads in orbit. Founder and CEO Peter Beck noted that integrating PSC’s proven hardware “simplifies the journey to orbit” by aligning hardware, software, spacecraft, and launch into a seamless package.

Alongside the acquisition of Advanced Solutions, Inc. in October 2021, this move aligns with Rocket Lab’s broader objective to secure technology, talent, and production capacity internally, reducing external dependencies. Industry observers have characterised this as a deliberate backward integration effort. A participant in an online space‑industry discussion observed:

“It seems like they are reverse integrating into their supply chain… instead of paying for products, buy the company, make the products for yourself, and make the margin on selling to others.”

Operationally, the acquisition has borne tangible returns. In November 2022, Rocket Lab secured two contracts totalling $14 million to supply Lightband separation systems for the Space Development Agency’s Tranche 1 transport layer constellation, reinforcing its position in national security‑oriented space architecture. The Lightbands, inherited from PSC, now supply critical satellite deployments with demonstrated reliability in specialised environments.

Rocket Lab’s expanded suite of capabilities positions it advantageously within a market increasingly dominated by fully integrated space services providers. By combining its Electron launch vehicle, Photon spacecraft, separation hardware, and on‑orbit software offerings, the company provides end‑to‑end mission support—a compelling proposition for both commercial and government customers.

With growth in space demand showing no signs of abating, particularly in low-Earth orbit constellations and defence networks, consolidating key enabling technologies under one roof offers Rocket Lab both operational efficiencies and competitive edge. The PSC acquisition stands as a pivotal building block in that strategy.

A client‑side remote code execution flaw in Google Web Designer for Windows poses a severe threat, allowing attackers to inject malicious CSS into configuration files to subvert internal APIs and seize full control of affected systems. The bug impacts every build prior to version 16.4.0.0711, and a fix has already been deployed in that release. Security researcher Bálint Magyar publicly disclosed the vulnerability, tracked as CVE‑2025‑4613, by demonstrating […]

WhatsApp has rolled out an urgent update for its iOS and macOS apps after detecting a zero‑click exploit—one that required no user interaction—to deliver spyware to a small number of targeted users. The vulnerability allowed attackers to bypass authorisation checks when processing linked-device synchronization messages—specifically in WhatsApp for iOS before version 2.25.21.73, WhatsApp Business for iOS before version 2.25.21.78, and WhatsApp for Mac before version 2.25.21.78. This flaw was chained […]

VISHNU RAJA
RYO YAMADA
HITORI GOTOH
IKUYO KITA