News related to
cyberattack

Appknox, a leading mobile application security firm, has launched a suite of advanced artificial intelligence features aimed at strengthening mobile ecosystem protection in the Gulf Cooperation Council region. This move comes in response to the escalating security risks posed by Generative AI technologies and the increasing reliance on mobile applications across various industries. The new security capabilities leverage AI to provide businesses with real-time visibility into potential […]

The content delivery network market is on track for remarkable growth, with estimates showing a surge in revenue from $26.8 billion in 2024 to $121.9 billion by 2033. This trajectory represents a compound annual growth rate of 18%, driven by a confluence of technological advancements, including artificial intelligence and the widespread adoption of 5G networks. As businesses worldwide increasingly rely on digital content delivery, the demand for […]

Bitwarden, a prominent password management service, has introduced a new security feature aimed at enhancing account protection for users who have not enabled two-factor authentication . This latest update adds an additional layer of defense against unauthorized access, catering specifically to accounts that may still be vulnerable due to the absence of 2FA. With cyber threats continuously evolving, password management platforms have increasingly become targets for hackers […]

The Electronic Frontier Foundation has called for the dismissal of charges against Roman Storm, a key figure involved in the creation of the Tornado Cash cryptocurrency mixer. The EFF, a prominent digital rights advocacy group, argues that the prosecution of Storm and the broader case surrounding Tornado Cash represents a dangerous overreach of U.S. criminal law, extending far beyond its intended scope.

Tornado Cash, a decentralized, privacy-enhancing tool built on the Ethereum blockchain, has been a controversial figure in the growing debate over privacy and regulation in the cryptocurrency world. The platform allowed users to obscure the origin and destination of transactions, which made it popular for those seeking anonymity in their financial dealings. However, this anonymity has also made it a target for governments and regulators, who have voiced concerns about its potential use in illegal activities such as money laundering and terrorist financing.

In August 2022, the U.S. Treasury Department’s Office of Foreign Assets Control sanctioned Tornado Cash, effectively blacklisting the platform by prohibiting U.S. persons from interacting with it. This move was grounded in allegations that Tornado Cash had been used to launder over $7 billion, including proceeds from North Korean cyberattacks. Despite its focus on criminal activity, Tornado Cash’s developers, including Storm, have maintained that their platform was designed for privacy and had legitimate uses.

The legal battle escalated when Storm was arrested in the summer of 2023, charged with conspiracy to violate U.S. sanctions and facilitating the laundering of criminal proceeds. The prosecution has sparked widespread controversy in the crypto and privacy communities, with critics asserting that the case threatens to set a dangerous precedent for the broader tech and blockchain industries. The EFF’s involvement has underscored the growing concern about privacy rights and the reach of U.S. government actions over global technologies.

EFF’s stance in the case is rooted in its belief that the prosecution of Tornado Cash developers, and specifically Storm, ignores the fundamental principles of free speech and software development. The organization contends that creating open-source software, like Tornado Cash, is akin to publishing code that can be used for a variety of purposes, both legal and illegal. EFF’s legal experts argue that prosecuting developers for the potential misuse of their software would set a precedent where coders could be held liable for the actions of users, a stance they believe undermines the principles of free speech and innovation.

EFF also claims that the prosecution of Roman Storm stretches the scope of U.S. criminal laws beyond their original intent, potentially criminalizing activity that was not meant to be illegal. They point to the vagueness in the charges, asserting that the government has not demonstrated sufficient evidence to link the Tornado Cash protocol itself to any specific criminal activity. The EFF’s position is that the mere existence of a technology that can be used for illegal purposes should not result in criminal charges for its creators, especially when it is otherwise designed for legitimate use cases such as privacy protection.

The Tornado Cash case also highlights the broader tension between privacy and regulation in the digital age. Supporters of the platform argue that privacy-enhancing technologies are vital in an increasingly digital world, where financial transactions and personal data are increasingly vulnerable to surveillance. They emphasize that privacy is a fundamental right that should not be compromised, even in the face of potential misuse by criminals.

On the other hand, the U.S. government’s stance reflects growing concerns over the use of cryptocurrencies in illegal activities. The government has expressed its intent to regulate the cryptocurrency space more tightly, citing national security risks and the need to prevent financial crimes. The sanctions on Tornado Cash were seen as part of this broader effort to curb illicit activity in the crypto ecosystem. However, critics argue that such measures may inadvertently harm legitimate users who rely on privacy tools for lawful purposes.

As the case proceeds, it is expected to set a significant legal precedent for the regulation of privacy-focused technologies. The outcome could have wide-ranging implications for developers and users of privacy-enhancing tools, especially in the context of a rapidly evolving regulatory landscape surrounding digital currencies and blockchain technologies. The EFF’s push for dismissal emphasizes the need for clear legal boundaries that protect innovation and free speech while addressing legitimate concerns about criminal activity.

Roman Storm’s legal team has strongly denied the charges, maintaining that he was simply a developer of an open-source software project with no knowledge of any illicit use of Tornado Cash. They argue that the prosecution is an overreach that misrepresents the nature of the technology and the role of its developers. Storm’s case has drawn attention from a variety of legal and tech experts, many of whom argue that criminalizing the development of software based on its potential misuse is both legally and ethically problematic.

HONG KONG SAR – Media OutReach Newswire – 15 January 2025 – As technology rapidly evolves, the number and complexity of cyberattacks have increased significantly. To enhance the response capabilities of its cybersecurity team in addressing various threats, DYXnet, a leading enterprise network service provider in Greater China, organized the “DYXnet Cyber Defense Exercise Competition 2025” yesterday (January 14), marking the company’s first cross-regional simulated attack and […]

SINGAPORE / BARCELONA, SPAIN – Media OutReach Newswire – 16 January 2025 – CDNetworks, the APAC-leading network to deliver edge as a service, will present its latest gaming solutions at ICE 2025 in Barcelona, Spain on 20th – 22nd January. At the event, the company will demonstrate how its advanced solution enables game providers to deliver seamless, secure, and high-performance gaming experiences on a global scale. The […]

Companies identify Business interruption as their top business concern for the year ahead (37% of overall responses) Cyber ranks #2 (31%), with data breaches identified as the cyber exposure companies fear most Natural catastrophes retain #3 rank (27%) in Asia, which is heating up faster than the global average SINGAPORE – Media OutReach Newswire – 15 January 2025 – Business interruption is the biggest worry for Asian […]

Advertisements

TORTOLA, BRITISH VIRGIN ISLANDS – Media OutReach Newswire – 2 January 2025 – In a significant milestone that underscores its dominance in the blockchain and cryptocurrency sectors, Venkate Exchange has proudly announced that its user base has exceeded 1 million. This achievement highlights Venkate’s status as the preferred platform in Southeast Asia, known for its innovative solutions and cutting-edge technology, serving a rapidly growing community with a […]

Amazon Web Services (AWS) has announced a significant $10 billion investment in Ohio’s data center infrastructure, aimed at transforming the state into a major technological hub by 2030. The move, which aligns with AWS’s broader expansion plans in the U.S., will lead to the creation of hundreds of new jobs and bolster the local economy while enhancing cloud services to meet growing demand. AWS’s investment will primarily […]

The Delhi High Court has mandated a renewed investigation into the July 2024 cyberattack on cryptocurrency exchange WazirX, which resulted in the theft of approximately $235 million in digital assets. This directive comes after the court dismissed an earlier status report from the Delhi Police that concluded no criminal case could be substantiated.

Advocate Jaivir Bains had petitioned the court, seeking criminal proceedings against WazirX’s management concerning the hack. Justice Sanjeev Narula, presiding over the case, found the initial police findings inadequate and has instructed the Deputy Commissioner of Police to submit a fresh status report by February 13, 2025.

The cyberattack, attributed to the North Korean hacking group Lazarus, compromised WazirX’s multisignature wallet, leading to the unauthorized transfer of substantial funds. Despite efforts to recover the assets, including a bounty program and collaboration with cybersecurity firm Cyfirma, approximately 43% of customer funds remain unrecovered.

In a related development, Binance, a leading global cryptocurrency exchange, announced on December 18, 2024, its decision to delist WazirX’s native token, WRX, citing non-compliance with its standards. This announcement precipitated a significant decline in WRX’s value, with reports indicating a drop of up to 59%.

Binance’s delisting notice stated that trading pairs involving WRX would be removed by December 25, 2024, with deposits ceasing on December 26, 2024, and withdrawals permitted until February 25, 2025. The exchange advised users to manage their holdings accordingly to avoid potential issues.

The delisting has intensified scrutiny on WazirX’s operations, especially concerning its compliance and security protocols. Binance has previously denied ownership of WazirX, asserting that the exchange is controlled by Zanmai Labs, operating under India’s Financial Intelligence Unit.

In response to these challenges, WazirX has announced plans to relaunch its platform with enhanced services and a focus on recovery for its creditors. The exchange also intends to introduce a decentralized exchange (DEX) as part of its restructuring efforts.

Zand, a prominent player in the digital finance sector, has been strengthening its custody services with advanced security protocols aimed at protecting client assets. This move highlights the increasing importance of safeguarding digital assets amid growing concerns about cyber threats in the evolving financial landscape.

The company has invested significantly in both technology and expert security teams to fortify its custodial framework, ensuring that it remains at the forefront of security in digital asset management. Zand’s approach combines state-of-the-art encryption methods, multi-layered security systems, and a continuous audit process to maintain asset integrity. These measures are intended to offer clients a high level of confidence in the safety of their holdings, even as global attention on cybersecurity intensifies.

A key component of Zand’s security architecture is its reliance on encryption technologies, which serve as the first line of defense against unauthorized access. The encryption processes are designed to ensure that sensitive data, such as private keys and transaction details, are only accessible to the rightful owners. These measures are backed by continuous real-time monitoring systems that detect and respond to any potential breaches, ensuring that the platform remains secure at all times.

Zand employs a robust audit process, working with third-party security firms to conduct regular evaluations of its systems. This independent verification ensures that the company’s security protocols are effective and compliant with the latest industry standards. The constant review of its custodial operations reflects the company’s commitment to transparency and operational integrity.

Zand’s security framework also includes a dedicated team of cybersecurity experts who provide ongoing oversight. These professionals are tasked with identifying vulnerabilities and responding to emerging threats in real time. By employing a proactive approach, Zand ensures that any potential risks are mitigated before they can affect clients’ assets.

In the rapidly expanding world of digital finance, the need for secure custodial services has never been more crucial. With the rise in cyberattacks targeting financial institutions and digital platforms, companies like Zand are under increasing pressure to adopt advanced security measures. As digital assets gain popularity among both individual investors and institutional players, the stakes are high. Any breach in security could undermine trust in digital finance platforms, making robust security a top priority for companies operating in this space.

Zand’s emphasis on continuous audits and expert oversight sets it apart from many of its competitors, who may not invest as heavily in regular system evaluations or specialized security teams. This distinction has made Zand a trusted name for those seeking secure storage and management of their digital assets.

Despite the sophisticated security mechanisms, Zand is not resting on its laurels. The company continues to evolve its systems to stay ahead of emerging threats in the cybersecurity landscape. As cybercriminals become more sophisticated, financial institutions must adapt rapidly to counteract new forms of attacks, which range from phishing schemes to more complex forms of hacking and fraud.

As part of its commitment to staying at the cutting edge of security, Zand has also begun exploring the integration of blockchain-based solutions for asset management. The decentralized nature of blockchain offers an additional layer of security, as it makes it harder for attackers to alter or corrupt data. By incorporating these technologies into its existing security framework, Zand aims to offer clients an even more resilient solution to protect their assets.

Zand’s efforts reflect broader trends within the financial services industry, where the demand for secure and efficient digital asset management continues to rise. The growing involvement of institutional investors in the digital finance space has placed increased pressure on custodians to adopt best practices in security. These investors require assurance that their assets are being managed by platforms with stringent controls in place, and Zand’s comprehensive approach to security meets these high expectations.

The company has also worked to ensure that its custodial services are user-friendly, allowing both novice and experienced investors to manage their digital assets with ease. By prioritizing security without compromising on accessibility, Zand is positioning itself as a leading player in the evolving digital finance sector.

Byte Federal, a prominent Bitcoin ATM network in the United States, has disclosed a security breach that compromised the personal data of 58,000 customers. The company revealed the incident after identifying unauthorized access to its systems, which reportedly led to the exposure of sensitive user information, including names, email addresses, and transaction details.

The breach has raised concerns about cybersecurity measures in the cryptocurrency sector. Byte Federal, known for operating over 1,000 Bitcoin ATMs across more than 40 states, has positioned itself as a major player in the digital asset ecosystem, facilitating cryptocurrency transactions for thousands of users daily. This incident underscores the vulnerabilities even in established networks within the fintech space.

Byte Federal’s systems were reportedly targeted in a sophisticated cyberattack, exploiting vulnerabilities in its data storage infrastructure. While the company has not confirmed whether financial information, such as bank account or credit card details, was accessed, it has assured customers that immediate steps were taken to address the breach and secure its systems. Additionally, Byte Federal is cooperating with law enforcement agencies and third-party cybersecurity firms to investigate the breach thoroughly and prevent future incidents.

This data breach follows Byte Federal’s expansion of its service offerings, including the integration of the Bitcoin Lightning Network, which enables faster and more cost-efficient transactions. The company’s focus on innovation has drawn significant attention, but this breach may lead to heightened scrutiny over its cybersecurity protocols. Industry experts have noted that companies in the cryptocurrency domain must balance innovation with robust security measures to protect user data.

Affected customers are being notified individually and advised to monitor their accounts for any unauthorized activity. Byte Federal has also recommended users to reset their passwords and adopt additional security measures, such as enabling two-factor authentication, to safeguard their accounts. The company is offering complimentary identity theft protection services to those impacted by the breach.

The incident has prompted discussions about regulatory oversight and the need for stricter cybersecurity compliance in the fintech and cryptocurrency sectors. Analysts argue that the growing adoption of digital assets necessitates a parallel emphasis on security standards to protect consumers and maintain trust in the ecosystem. This breach serves as a stark reminder of the challenges faced by firms operating in an increasingly digital financial landscape.

The Department of Government Efficiency (DOGE) disclosed that a significant portion of the U.S. federal government’s annual IT budget, approximately 80% of the total $100 billion, is allocated to maintaining outdated technology systems. This allocation raises concerns about the long-term sustainability of the federal IT infrastructure and its vulnerability to security threats.

Despite the substantial budget, the government faces a challenge in modernizing its technology while managing legacy systems that have become both inefficient and costly to maintain. Many of these systems were initially developed decades ago and have struggled to keep pace with rapid advancements in technology. As a result, maintaining these aging systems has grown more expensive, consuming a disproportionate share of the federal IT budget.

The situation has sparked debates about the federal government’s ability to balance its technological needs with its security priorities. Outdated systems are not only more costly to maintain but are also significantly more vulnerable to cyberattacks, raising concerns about national security risks. Experts argue that continued reliance on legacy systems could expose sensitive government data to increasing cybersecurity threats, further straining the government’s IT security efforts.

The revelation by DOGE comes at a time when federal agencies have faced criticism for their inability to modernize critical infrastructure quickly enough. A number of high-profile cyberattacks in recent years have underscored the urgency of addressing vulnerabilities in government systems. These incidents, which have targeted various agencies, have raised alarms about the resilience of federal IT networks and their capacity to defend against modern-day threats.

A primary issue is the government’s inability to fully transition from legacy technology to more secure, efficient, and adaptable systems. Experts argue that the high costs associated with maintaining outdated systems may be hindering the government’s ability to invest in cutting-edge technologies like artificial intelligence, cloud computing, and blockchain, all of which have the potential to enhance government operations and improve security.

There are concerns about the lack of skilled personnel required to manage these older systems effectively. Many IT professionals with expertise in outdated technologies are retiring or leaving the workforce, creating a knowledge gap that is challenging to fill. This lack of qualified personnel further complicates the effort to modernize federal IT infrastructure.

The burden of maintaining legacy systems has also led to inefficiencies within government operations. Modern systems are typically more agile, cost-effective, and scalable, which allows for improved service delivery and greater responsiveness to changing needs. However, due to the reliance on outdated systems, government agencies are often unable to take advantage of the efficiencies offered by newer technologies, leading to delays and increased operational costs.

In response to these challenges, DOGE has called for a reevaluation of how federal IT budgets are allocated. The department has urged a shift towards prioritizing investments in modernization initiatives, which could provide long-term savings by reducing the costs of maintaining legacy systems. Some experts suggest that adopting a more incremental approach to modernization—updating critical systems first while gradually phasing out older technologies—may offer a more practical solution.

The federal government’s struggle with outdated technology systems is not unique to the United States. Many governments around the world are facing similar issues as they attempt to navigate the complex landscape of digital transformation. However, given the scale of the U.S. government’s operations, the consequences of failing to modernize could have far-reaching implications, both in terms of efficiency and security.

Despite the challenges, there have been some steps taken towards modernization. Federal agencies have begun pilot programs to experiment with new technologies and test their applicability in government operations. Some agencies are already seeing positive results from these efforts, although the pace of change remains slow.

The financial implications of maintaining outdated systems are significant. According to estimates, the government spends billions annually on software upgrades, hardware maintenance, and security patches for legacy systems. As these systems continue to age, the costs associated with upkeep are expected to rise, further straining the federal IT budget.

As the government moves forward with its modernization efforts, the success of these initiatives will depend largely on the ability to balance cost, security, and innovation. A comprehensive, long-term strategy will be required to overhaul the federal IT infrastructure while addressing the immediate needs of maintaining legacy systems.

In light of the revelations by DOGE, there are growing calls for more transparency in the government’s IT spending, with some lawmakers pushing for increased oversight of federal IT contracts. Critics argue that without greater accountability, the government may continue to waste taxpayer dollars on outdated systems, undermining efforts to modernize and secure its infrastructure.


Fortinet has unveiled its new cloud-delivered platform, FortiAppSec Cloud, a cutting-edge solution designed to address the escalating complexities of securing modern web applications across multiple cloud environments. The launch marks a significant step in the cybersecurity provider’s ongoing efforts to offer a unified approach to web application security, ensuring businesses can safeguard their digital infrastructure in an era of rapidly evolving threats. The FortiAppSec Cloud platform is […]

The Caribbean and the United States are now seamlessly connected through the newly unveiled Caribbean Elite Alliance (CELIA) undersea cable, marking a transformative leap in digital infrastructure for both regions. This high-capacity cable, which spans more than 5,000 kilometers, promises to revolutionize data transfer and telecommunications, providing faster, more reliable internet access for millions of people in the Caribbean and on the U.S. East Coast. CELIA, which […]

From wars in Eastern Europe and the Middle East to rising tensions in the Taiwan Strait, geopolitical instability has become the defining characteristic of our time. There are now more active armed conflicts than at any point since World War II. Simultaneously, the digital realm has become a battleground, with cyberattacks escalating in frequency and sophistication, targeting both national infrastructures and private enterprises. While these developments are […]

Online casino platform MetaWin experienced a significant security breach on November 3, resulting in the loss of approximately $4 million in user funds. According to reports from cybersecurity experts and industry insiders, the exploit appears to have been orchestrated by a sophisticated hacking group, leading to widespread concerns about the safety of online gambling sites. Following the attack, the CEO of MetaWin reassured users that the funds […]

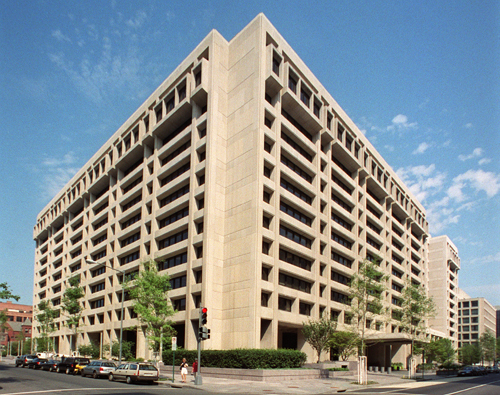
The International Monetary Fund has raised concerns that global markets are underestimating the potential economic impact of geopolitical tensions. Amid signs of improving economic stability, especially as global disinflation enters its final stages, the IMF has identified several medium-term risks that could significantly disrupt financial markets. According to its latest Global Financial Stability Report, while short-term global financial stability risks have receded, major vulnerabilities persist.

The IMF’s warning comes at a time when many market participants are hopeful about the prospects of a “soft landing” for the global economy, aided by disinflation and easing monetary policies. Emerging markets have shown resilience, and international debt issuance has picked up in some frontier economies. Despite these optimistic signs, there are concerns that the financial system remains fragile, especially in light of potential external shocks.

One of the key areas flagged by the IMF is the growing strain in the commercial real estate sector. Rising interest rates over the past year have exposed vulnerabilities within the sector, and further shocks could worsen these conditions. The IMF also points to signs of credit deterioration among corporations, which could intensify if adverse economic conditions continue.

The report highlights that geopolitical tensions remain a significant factor that global markets may be neglecting. Escalating geopolitical conflicts, such as the war in Ukraine and ongoing trade disputes between major economies, present long-term threats that could disrupt financial systems worldwide. These risks are further compounded by cyber threats, which the IMF notes have been on the rise. Although no major systemic disruptions have been caused by cyber incidents so far, the increasing probability of severe cyberattacks poses a looming threat to global macroeconomic stability.

In addition to geopolitical and cyber risks, the IMF underscores the vulnerability of the corporate credit market, which has expanded rapidly in recent years. This market, particularly in private credit, now rivals more traditional forms of lending, including commercial banking. While private credit markets have served as an important source of capital for mid-sized firms, they are also exposed to higher risks. A sudden downturn in economic conditions or a sharp increase in interest rates could leave many of these firms struggling to meet their debt obligations, creating ripple effects throughout the global financial system.

While the IMF acknowledges the progress made in global disinflation and the efforts of central banks to maintain stability, it is urging policymakers and financial institutions to remain vigilant. The report recommends that governments and central banks continue to assess and address medium-term risks while maintaining a focus on geopolitical and cyber threats that could lead to severe disruptions.

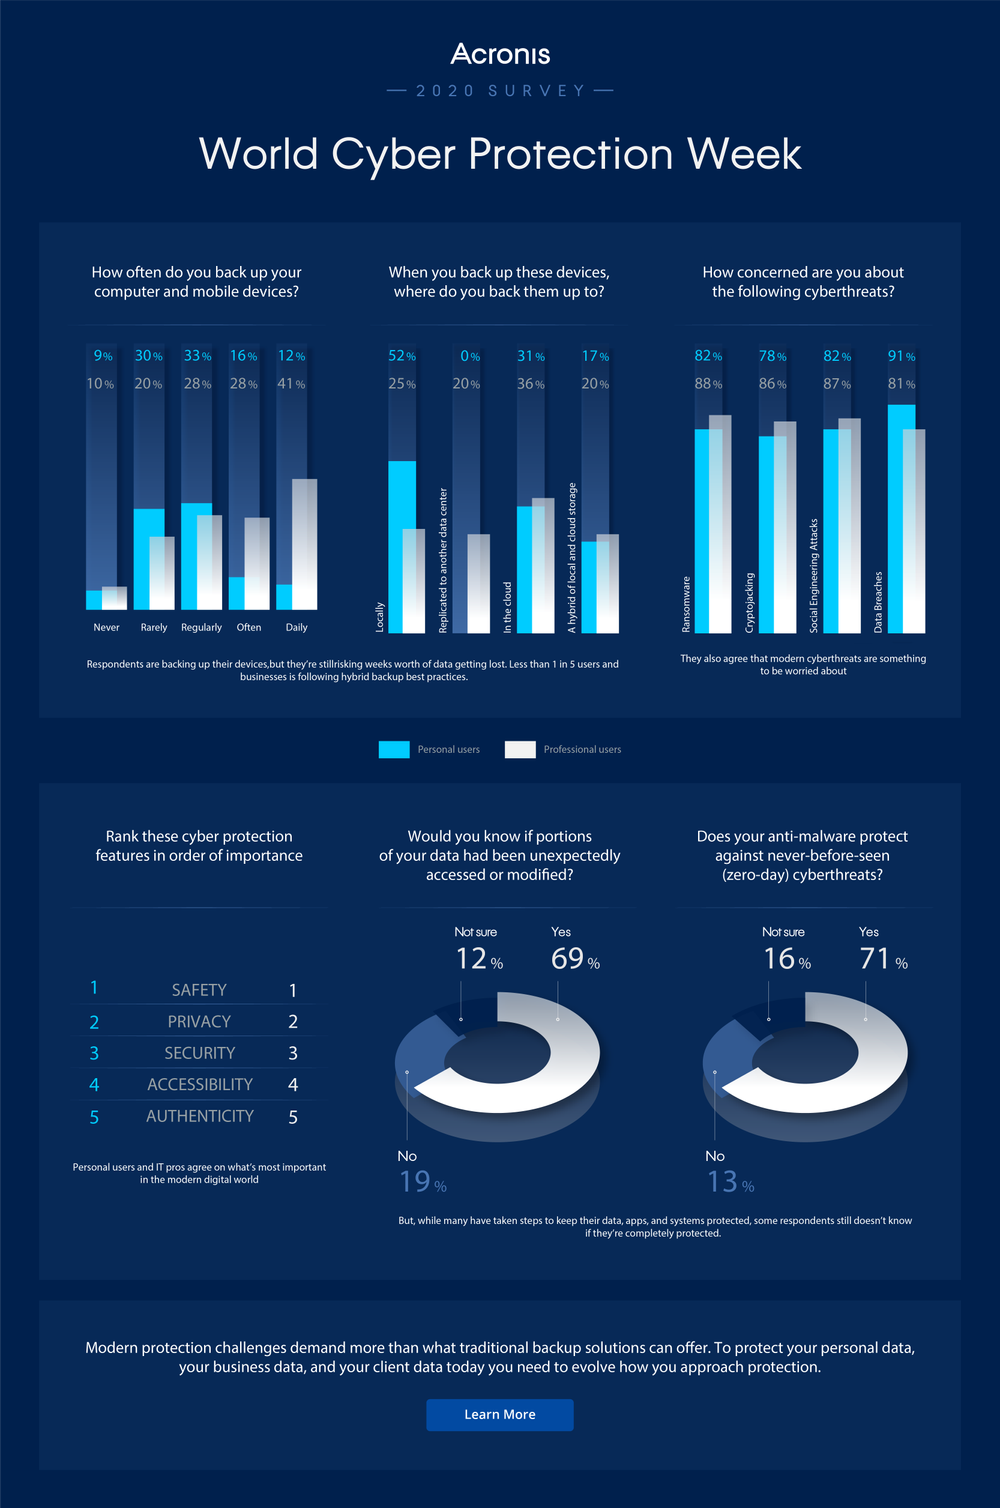
The cybersecurity sector in the UAE is experiencing unprecedented pressure, as highlighted by Acronis’ recent report indicating a staggering 68% revenue increase. This growth is attributed to the rising prevalence of cyber threats, which have intensified in 2024. Malware detections have surged by 65.3%, while URL-based threats have escalated by 36.9%, creating a pressing need for robust cybersecurity solutions across various industries.

Acronis’ findings come amid a backdrop of increased global cybercrime, with businesses in the UAE becoming prime targets. The growing digital transformation across sectors such as finance, healthcare, and government has expanded the attack surface for malicious actors. As organizations adopt cloud services and remote work policies, they inadvertently expose themselves to a myriad of vulnerabilities. The result is a burgeoning market for cybersecurity services, compelling companies like Acronis to adapt quickly to meet the evolving demands of clients.

This surge in revenue reflects not only Acronis’ successful strategic initiatives but also a broader trend within the cybersecurity industry. Organizations are increasingly prioritizing their cybersecurity frameworks, investing in comprehensive solutions to protect sensitive data and ensure business continuity. Acronis has positioned itself effectively within this landscape by offering integrated protection solutions, including data backup, disaster recovery, and cybersecurity services tailored to combat emerging threats.

Key players in the cybersecurity market are rapidly innovating to keep pace with the evolving threat landscape. The rise of sophisticated cyberattacks has prompted a shift toward proactive cybersecurity measures. Companies are now prioritizing advanced threat detection and response capabilities, leveraging artificial intelligence and machine learning to enhance their defenses. These technologies enable organizations to identify and neutralize threats before they cause significant damage, underscoring the importance of adopting a proactive rather than reactive approach to cybersecurity.

The implications of these developments are profound for businesses in the UAE. With cyber threats on the rise, organizations must reassess their cybersecurity strategies to ensure they are not only compliant with regulations but also adequately protected against potential breaches. Cybersecurity frameworks are evolving to encompass not just IT security but also physical security and personnel training, creating a comprehensive approach to risk management.

The UAE government has been proactive in addressing these challenges. Initiatives aimed at enhancing the nation’s cybersecurity posture include the establishment of the UAE Cybersecurity Council, which seeks to unify efforts across public and private sectors. This collaborative approach aims to create a resilient digital ecosystem, reinforcing the importance of cybersecurity awareness and education among employees and the wider community.

As Acronis continues to grow in this dynamic environment, its emphasis on innovation will be critical. The company has committed to enhancing its cybersecurity offerings by integrating cutting-edge technologies and expanding its global footprint. Such strategies are vital for maintaining a competitive edge and meeting the diverse needs of clients navigating this complex landscape.

The increase in cyber threats is also prompting a reevaluation of regulatory frameworks in the UAE. Businesses are now under greater scrutiny to comply with stringent cybersecurity regulations, emphasizing the need for transparency and accountability in their operations. Companies that fail to meet these requirements face not only financial penalties but also reputational damage, making cybersecurity a board-level concern.

Emerging trends indicate that small and medium-sized enterprises (SMEs) are becoming more aware of their cybersecurity needs. Historically, SMEs have been less equipped to handle cyber threats due to limited resources. However, with increased awareness and the availability of scalable cybersecurity solutions, these businesses are now taking proactive steps to safeguard their operations.

The challenge of recruiting and retaining cybersecurity talent continues to plague the industry, further complicating efforts to bolster defenses. As the demand for skilled cybersecurity professionals grows, companies face intense competition in attracting top talent. Educational institutions and training programs are responding by developing specialized curricula aimed at preparing the next generation of cybersecurity experts, a move crucial for addressing the skills gap in the sector.

Another critical aspect of the evolving cybersecurity landscape is the role of cyber insurance. As organizations recognize the potential financial impact of cyber incidents, interest in cyber insurance policies is increasing. These policies can help mitigate losses resulting from data breaches, ransomware attacks, and other cyber threats. However, the complexities involved in underwriting such policies highlight the need for comprehensive risk assessments, ensuring that organizations understand their vulnerabilities and the appropriate measures to address them.

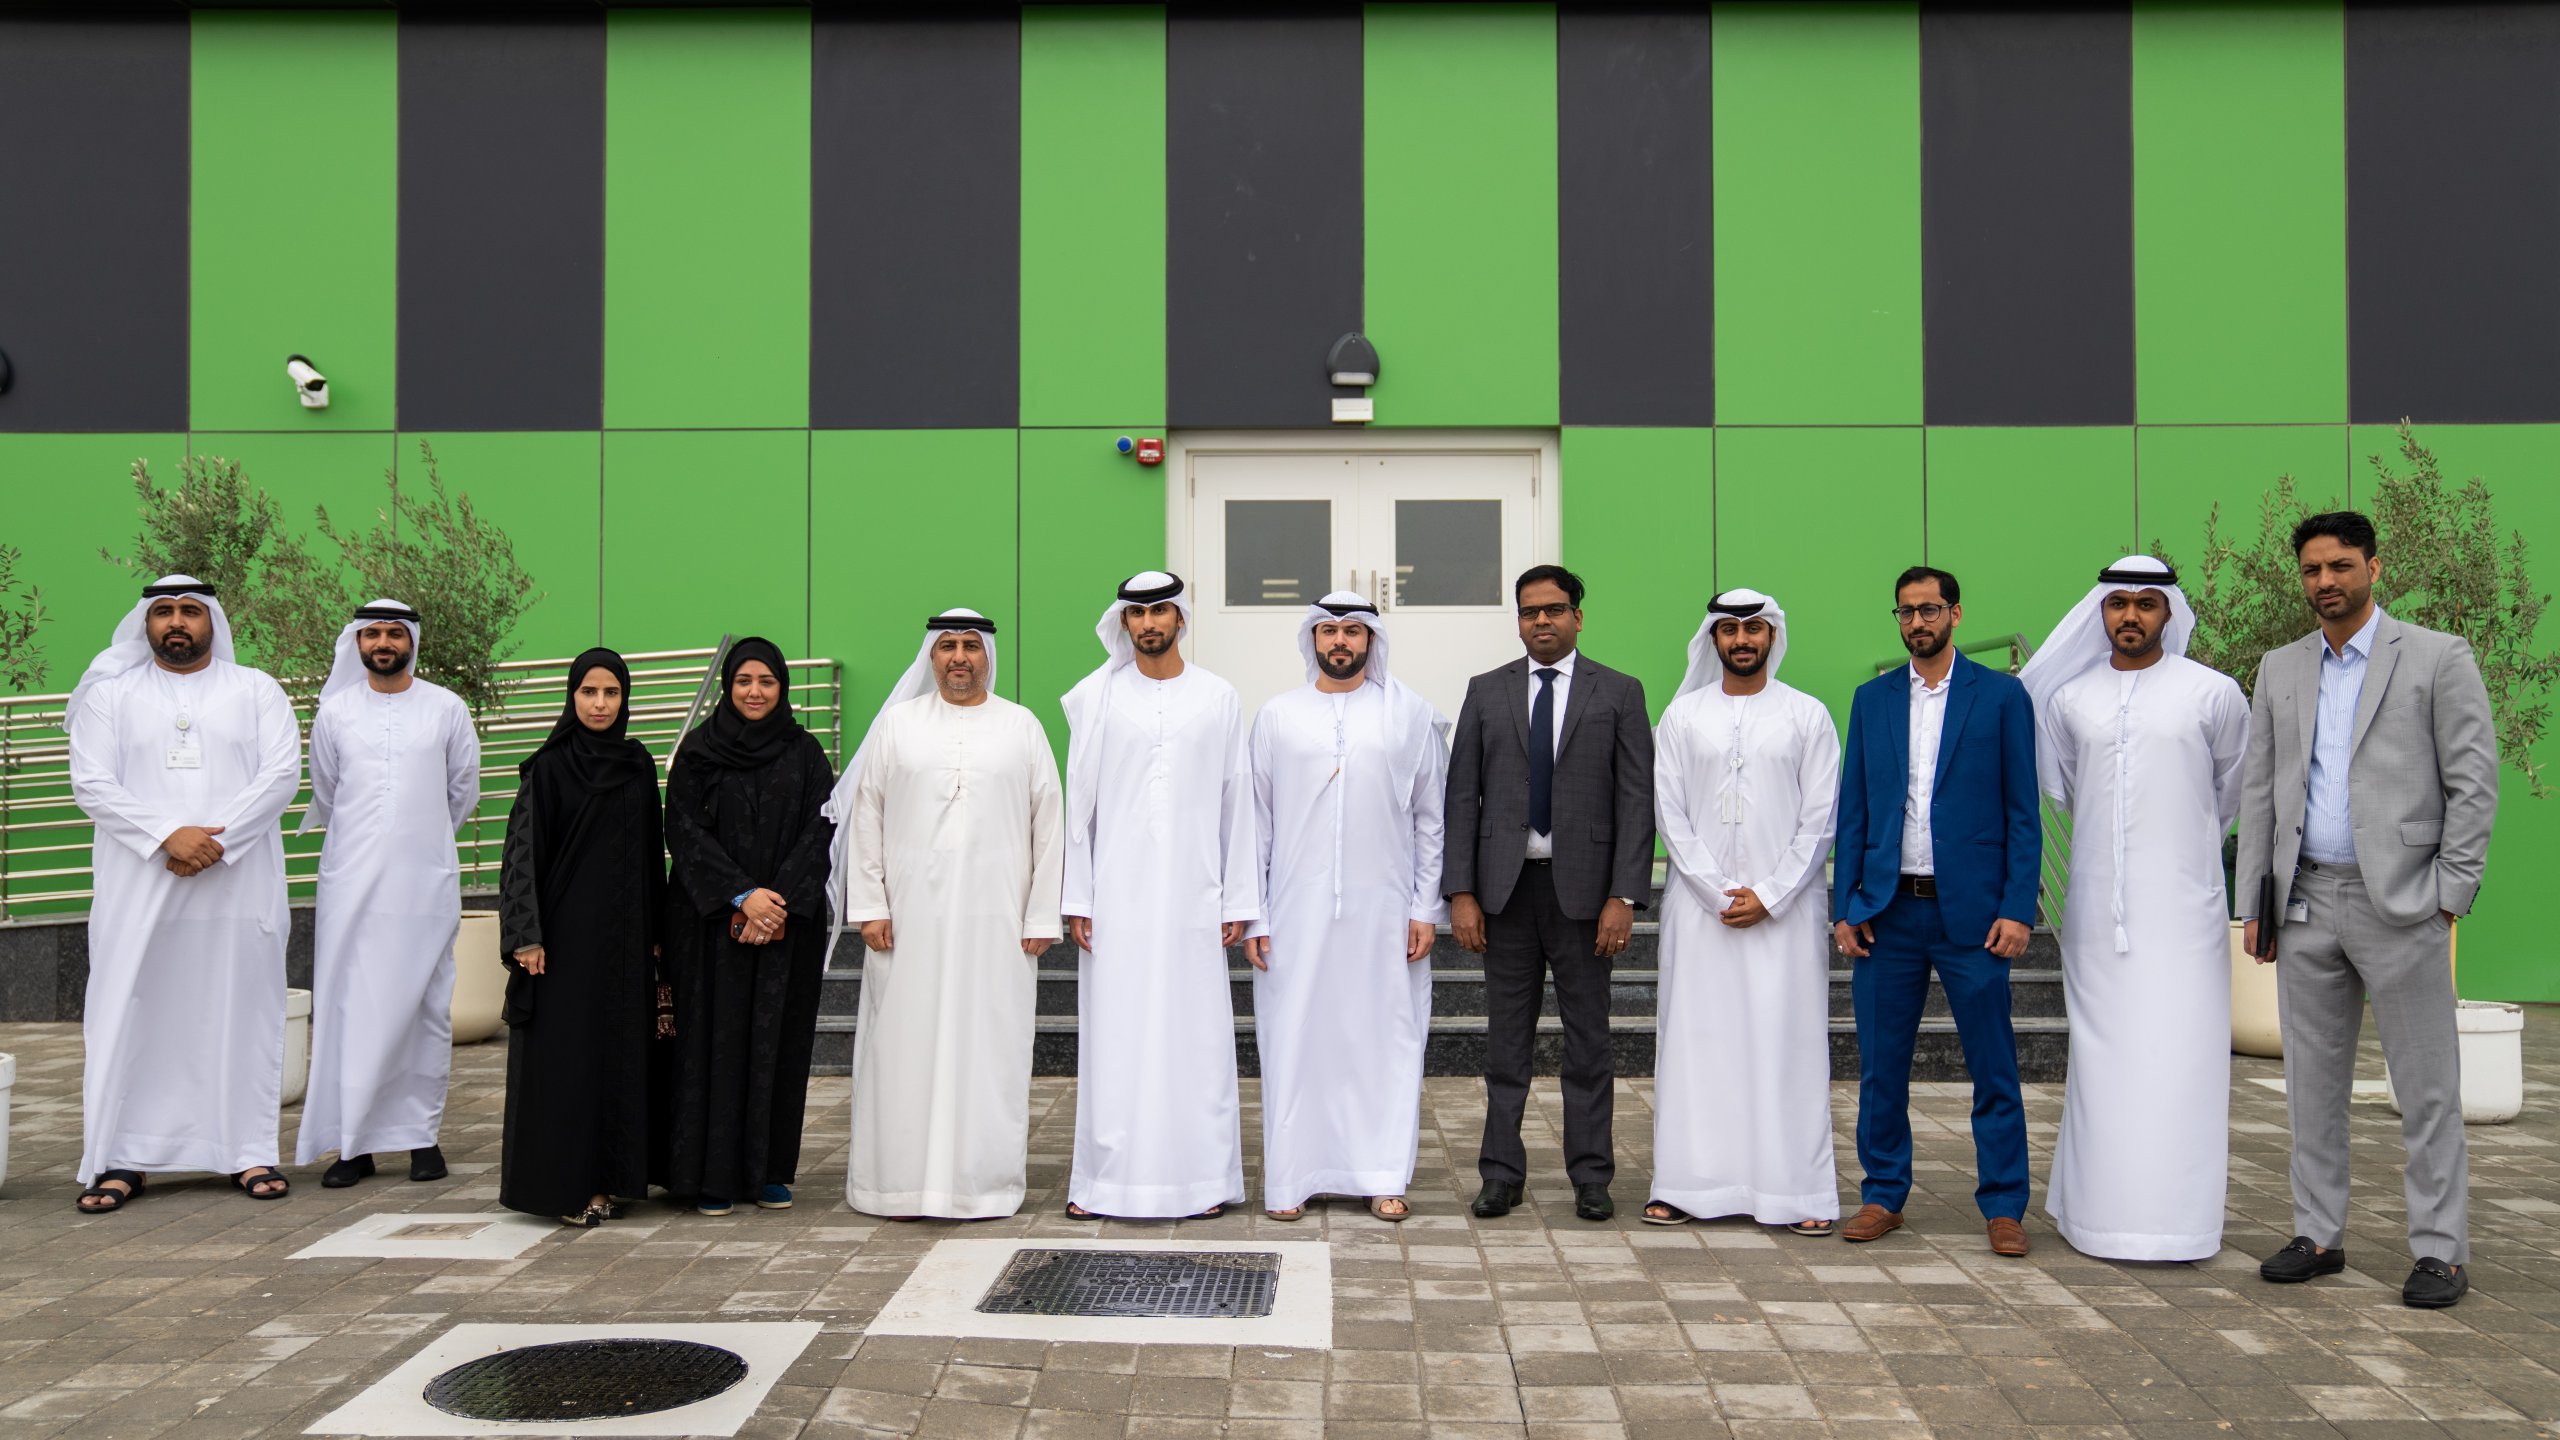
Moro Hub, a subsidiary of Digital DEWA, has formalized a partnership with Dubai Islamic Bank (DIB) aimed at enhancing the bank’s cybersecurity capabilities. The collaboration focuses on the provision of advanced colocation services and a comprehensive cybersecurity suite, ensuring the security and resilience of DIB’s IT infrastructure. This development is expected to boost Dubai Islamic Bank’s efforts to safeguard its operations and data against an evolving threat landscape while expanding its digital footprint.

The Memorandum of Understanding (MoU) signed between Moro Hub and Dubai Islamic Bank underscores the growing need for robust digital infrastructure in the financial sector. As part of the agreement, Moro Hub will provide DIB with secure colocation services in a state-of-the-art data center, alongside a suite of cybersecurity solutions tailored to meet the specific needs of the financial institution. These services aim to mitigate the risk of cyberattacks and ensure the bank’s compliance with regulatory standards, reflecting the increasing pressures on banks globally to adopt enhanced security measures.

Colocation, a service allowing businesses to rent space for their servers and other computing hardware within a third-party data center, offers banks like DIB the advantage of enhanced physical security, disaster recovery, and operational efficiency. Moro Hub’s colocation services will enable Dubai Islamic Bank to host its critical systems in a secure environment, benefiting from the company’s advanced infrastructure, which is designed to meet the stringent security requirements of financial institutions.

This partnership comes at a time when financial institutions in the UAE and around the world are grappling with a surge in sophisticated cyber threats. With the rise of digital banking services and the increased reliance on online platforms, banks have become prime targets for cybercriminals. By leveraging Moro Hub’s expertise in cybersecurity, Dubai Islamic Bank aims to strengthen its defenses against these threats, ensuring the protection of its clients’ sensitive information.

The global banking sector has witnessed a dramatic rise in cybersecurity incidents over the past few years, prompting financial institutions to invest heavily in protective measures. From phishing attacks to sophisticated ransomware campaigns, banks are constantly under siege by attackers seeking to exploit vulnerabilities in their systems. Dubai Islamic Bank’s decision to partner with Moro Hub reflects a proactive approach to dealing with these challenges, as the bank seeks to stay ahead of the curve in an increasingly digitalized world.

Moro Hub, established as part of Dubai’s broader Smart City initiative, has positioned itself as a key player in the region’s digital transformation efforts. The company’s data centers and cybersecurity services are aligned with international standards, making it a trusted partner for businesses seeking to secure their digital operations. For Dubai Islamic Bank, this partnership offers a significant opportunity to enhance the security and efficiency of its IT operations while also reducing the operational costs associated with maintaining in-house data centers.

Cybersecurity is no longer just a technological challenge; it has become a critical component of business strategy for banks and other financial institutions. Regulatory bodies in the UAE and across the globe have tightened their requirements for data protection, mandating that banks adopt stricter security protocols to safeguard customer data and prevent breaches. Failure to comply with these regulations can result in hefty fines and damage to the institution’s reputation. By partnering with Moro Hub, Dubai Islamic Bank aims to ensure full compliance with these regulatory standards while also minimizing the risk of operational disruptions caused by cyberattacks.

Beyond the immediate security benefits, this partnership is also expected to have broader implications for Dubai Islamic Bank’s digital transformation journey. The bank has been steadily expanding its digital services, offering customers a range of online banking options, including mobile banking apps and digital payment platforms. As customer expectations continue to evolve, DIB’s ability to provide seamless and secure digital services will be crucial to maintaining its competitive edge in the market.

The digital banking landscape is undergoing rapid transformation, with customers increasingly favoring online and mobile services over traditional banking methods. This shift has forced banks to rethink their operational strategies, with a focus on enhancing the digital experience for customers while ensuring robust security measures are in place. For Dubai Islamic Bank, the partnership with Moro Hub is a strategic move to ensure that its digital infrastructure is capable of meeting these demands while also safeguarding against the growing threat of cyberattacks.

Financial institutions across the UAE have been accelerating their investments in digital infrastructure in response to changing market conditions and regulatory pressures. With initiatives such as the UAE’s National Cybersecurity Strategy and Dubai’s push towards becoming a global fintech hub, banks are under increasing pressure to enhance their cybersecurity frameworks. Dubai Islamic Bank’s collaboration with Moro Hub is in line with these national priorities, positioning the bank as a leader in digital security within the financial sector.

While the specific financial terms of the MoU were not disclosed, the partnership between Moro Hub and Dubai Islamic Bank represents a significant step forward in the bank’s efforts to strengthen its IT infrastructure. The bank’s leadership has emphasized the importance of cybersecurity as a core component of its business strategy, and this collaboration with Moro Hub is expected to play a key role in achieving those objectives.

IIT Madras has inaugurated the Centre for Cybersecurity, Trust, and Reliability (CyStar), marking a significant step towards advancing India’s cybersecurity capabilities. The newly established CyStar is expected to play a pivotal role in fortifying the nation’s cyber defenses amid growing threats across various industries, including finance, healthcare, and critical infrastructure. The Center’s focus is both broad and ambitious, covering sectors from artificial intelligence to post-quantum cryptography, while aiming to create an ecosystem of innovation and collaboration.

Speaking at the launch, IIT Madras Director Prof. V. Kamakoti emphasized the increasing prevalence of cyberattacks, which are not limited to financial motives but often target key infrastructure sectors. To counter this evolving threat landscape, CyStar will focus on developing proactive defense mechanisms to safeguard the country’s digital assets. The initiative is part of the institution’s broader strategy to contribute to the global cybersecurity ecosystem, incorporating interdisciplinary research and technological advancement to meet today’s complex security demands.

CyStar has been structured with a vision to drive innovation through fundamental and applied research, fostering collaboration between academia, industry, and government. The Center will partner with prominent organizations, including the Ministry of Electronics and Information Technology, the Ministry of Education, Kaspersky, IDBI Bank, LG India, and numerous other local and international players. These partnerships aim to tackle a range of cybersecurity issues, from data privacy to the protection of critical infrastructure.

At the heart of CyStar’s mission is the desire to address cybersecurity challenges in India’s diverse social and business environments. The Center’s multi-disciplinary team will focus on developing cutting-edge solutions, including security frameworks for artificial intelligence, blockchain technology, and quantum computing. The ultimate goal is to secure vital sectors of the economy, especially those that rely heavily on digital infrastructure.

CyStar’s key coordinators, including Prof. Shweta Agrawal and Prof. Chester Rebeiro, outlined the Center’s approach, which spans fundamental research to practical applications. Agrawal stressed the importance of a collaborative environment that brings together experts from varied fields to tackle the complex problem of cybersecurity. Rebeiro added that the Center’s outreach programs and industry-academia relationships would help foster innovation and secure India’s critical industries.

By integrating cybersecurity advancements into real-world applications, the Center also aims to contribute to startup ecosystems, helping to cultivate new companies that focus on cybersecurity solutions. This aligns with India’s broader ambition to become a global leader in technology-driven innovation. Furthermore, the center will explore advanced cybersecurity applications in sectors such as healthcare, electronics, and automotive, industries that are highly dependent on secure and reliable digital systems.

In the keynote address, internationally renowned cybersecurity experts, including Prof. Shafi Goldwasser of MIT and Prof. Christian Scheideler of Paderborn University, emphasized the importance of innovative research to counter emerging cyber threats. They noted that as technology evolves, particularly in areas such as AI and quantum computing, cyber threats will become more sophisticated, requiring a comprehensive and forward-thinking approach. CyStar’s work, they suggested, is poised to meet these challenges head-on by developing next-generation solutions for AI security, quantum encryption, and IoT security.

Fortinet has launched its Security Awareness and Training Service to over 30,000 primary and secondary schools throughout Saudi Arabia, marking a significant advancement in the country’s cybersecurity education landscape. This initiative aligns with the Saudi government’s commitment to enhancing cybersecurity awareness among the youth and bridging the existing skills gap in the nation. The service, which is being provided at no cost, aims to equip students and […]

A significant surge in data breaches attributed to artificial intelligence has emerged as a pressing concern for cybersecurity leaders across the Asia-Pacific region, according to a comprehensive survey by Cloudflare. The study highlights that a staggering 87% of cybersecurity professionals view AI as a factor contributing to the increasing sophistication of cyberattacks, raising alarms about the evolving landscape of digital threats. The survey results underscore a growing […]

The expansion of smart cars is introducing a range of privacy and cybersecurity challenges that demand immediate attention. With vehicles evolving into data-collecting machines, privacy experts and regulators are sounding alarms about the vast amount of personal data being harvested. As modern cars are now equipped with sensors, cameras, and GPS systems, they gather data about drivers’ locations, driving habits, and even contacts stored in smartphones. This trend is raising significant concerns about who controls this data and how it is being used.

Automakers, eager to enhance the driving experience, have equipped their latest models with state-of-the-art connectivity features, from Wi-Fi to cloud services, making these vehicles resemble smartphones on wheels. However, the rise of connected cars has simultaneously led to an increase in the collection and monetization of personal information. Companies are gathering sensitive data through multiple channels, including onboard systems that monitor everything from driving behavior to entertainment preferences. What happens to this data, where it is stored, and how it is shared are questions that car owners are increasingly asking.

Privacy advocates have raised alarms about the potential risks posed by these vehicles. Smart cars can track driver behavior, record routes, and even monitor interactions with third-party services, creating a detailed profile of individual users. The data being collected is staggering, with some estimates suggesting that the average car could generate over a terabyte of data annually. Automakers have started to capitalize on this data, using it to optimize services, and in some cases, sharing it with third parties for targeted marketing and other purposes. However, transparency about what data is collected and how it is used remains limited, creating a troubling scenario for users who are often unaware of the extent of the data being harvested.

Regulatory frameworks are lagging behind technological advancements, leaving a regulatory vacuum in many parts of the world. China has made strides in addressing these concerns by tightening rules around data collection from connected vehicles. Meanwhile, other major markets, including the United States and Europe, have yet to introduce comprehensive regulations governing how carmakers handle user data. In the absence of robust laws, automakers have relied on vague privacy policies, which often lack clarity on what data is being shared and with whom.

The push for regulatory oversight is intensifying, with cybersecurity experts warning of the growing vulnerability of smart cars to hacking and cyberattacks. Hackers could potentially exploit weak points in a car’s digital systems to access personal data or even take control of the vehicle. As smart cars become more autonomous and connected, the risk of malicious attacks increases, prompting calls for automakers to bolster their cybersecurity measures and increase transparency around data usage.

At the heart of this debate is the question of consumer consent. Many car owners are unaware of the extent to which their vehicles collect data, and even when privacy policies are available, they are often filled with legal jargon that makes it difficult for users to understand what they are agreeing to. Automakers have generally not been proactive in educating consumers about their data rights, and the onus often falls on users to navigate complex policies and settings to protect their information.

Despite these concerns, some automakers have started to take steps toward greater transparency. For example, certain manufacturers have implemented clearer policies regarding the sharing of personal data, pledging not to sell data to third-party advertisers or resellers without explicit consent. These moves, however, are the exception rather than the rule, and much more needs to be done to ensure that consumers are fully informed and protected in the age of smart cars.

VISHNU RAJA
RYO YAMADA
HITORI GOTOH
IKUYO KITA