Thousands of fraudulent FIFA-themed domains are being positioned to exploit supporters before the 2026 World Cup, with cyber-security researchers tracking more than 4,300 suspicious registrations since August 2025. The domains mimic FIFA’s official web presence and are designed to lure fans seeking tickets, merchandise, travel packages, streaming access, betting platforms and hospitality deals. Some use names close to FIFA, the World Cup, host cities or national teams, […]
Hackers are exploiting shared content delivery network infrastructure to hide malicious traffic behind trusted domains, exposing a weakness in DNS-based security controls used by enterprises to block command-and-control activity, data theft and unauthorised tunnelling. The technique, named Underminr by ADAMnetworks, takes advantage of the way large CDNs host many unrelated websites on the same edge IP addresses. A compromised device can make a legitimate DNS lookup for […]
Microsoft has issued fixes for a high-severity SharePoint Server vulnerability that could allow authenticated attackers to run code remotely on affected on-premises systems, sharpening security concerns for organisations that continue to rely on self-managed collaboration platforms. Tracked as CVE-2026-45659, the flaw affects SharePoint Server Subscription Edition, SharePoint Server 2019 and SharePoint Enterprise Server 2016. The vulnerability has been assigned a CVSS score of 8.8, placing it in […]
Code4Mzansi highlights the growing strength of South Africa’s developer ecosystem and the role of youth-led innovation in shaping the country’s digital future
JOHANNESBURG, SOUTH AFRICA – Media OutReach Newswire – 26 May 2026 – South Africa’s emerging developers are building close to the ground, with many of the strongest solutions at the inaugural Huawei Code4Mzansi finals focused on systems people use every day: township retail, healthcare, energy, agriculture, payments and the creative economy.
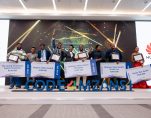
The winners at the Huawei Developer Competition, Code4Mzansi
The competition was held in partnership with the Department of Small Business Development. “The Code4Mzansi competition is not just a celebration of achievement, it is a launchpad for the future,” said Minister Stella Ndabeni, whose department co-hosted the event and delivered the closing address.
The finals revealed a clear shift from building abstract digital products to practical tools that help small businesses trade better, communities access services more easily, and local industries solve problems faster.
Four finalist teams focused directly on the township economy, with solutions covering food safety verification for spaza shops, offline point-of-sale systems built for load-shedding, WhatsApp-native marketplaces for informal retailers, and community credit systems for SASSA grant recipients.
Others addressed AI-driven healthcare access, electricity theft detection, smart agriculture, financial infrastructure for the creator economy, and AI-generated African music.
Held at Huawei Office Park in Woodmead, the finals brought together more than 100 attendees, including government representatives, academic partners, industry leaders and media.
“The quality of the finalist solutions demonstrated the potential of local innovation to respond to real market needs,” said Steven Chen, Cloud CEO of Huawei Technologies South Africa.
Academic partners included the University of Pretoria, the University of Johannesburg, the University of the Witwatersrand and the University of Cape Town.
“Small businesses are the backbone of our economy, and technology is their greatest accelerator. The participants here today are future entrepreneurs who will drive South Africa’s digital economy forward,” said Professor Thokozani Shongwe, Vice Dean of Postgraduate Studies, Research and Internationalisation at the University of Johannesburg’s Faculty of Engineering and the Built Environment.
Industry partner rain also attended. Leon Nortje, Principal and Senior Architect at rain, said the competition offered a strong view of the country’s emerging technology pipeline.
“It is always good to see new projects and new teams working on solutions that are valuable and industry-related. We will be looking out for potential new employees,” said Nortje.
The winners
The finalists competed for a prize pool of R800,000. MAAT by SIMVAK was named the overall grand winner and received the Business Value Award, taking home R300,000. The platform addresses food safety and regulatory compliance in South Africa’s informal retail sector through AI agents, real-time product recall alerts, and counterfeit detection for the spaza shop ecosystem.
“The spaza network is the supply chain for most South African households,” said SIMVAK founder Shingirayi Mandebvu.
HealthHive by FTCK received second prize in the Business Value Award category, taking home R200,000, for its AI telemedicine platform that matches patients with the right medical practitioners based on their symptoms.
Auraa received the Grand Innovation Award for its AI music engine built to generate authentic African sound. The platform has been associated with an album that has crossed one million streams.
The Future Star Award went to e-Khadi, a community credit and stokvel platform giving SASSA grant recipients access to essentials at their local spaza shops, supported by AI-assisted credit scoring and fraud detection.
The People’s Choice Award, voted by the public on Huawei’s social media channels, went to DevRift, a semi-finalist in the competition, who took home R100,000.
Minister Ndabeni delivered the closing address, positioning Code4Mzansi within the government’s agenda for youth entrepreneurship, small business development and digital inclusion.
“Our task is to ensure that innovation does not remain a moment of applause, but becomes a pathway to enterprise creation, digital inclusion, and sustainable growth,” she said.
“Thank you to Huawei for being a perfect partner on the journey that we are travelling, and of course, those that matter most, the developers who dared to compete,” she said.
Code4Mzansi forms part of the global Huawei Cloud Developer Competition. In its inaugural edition, South Africa attracted more participants than any other country: 1,041 across 353 teams, including 176 enterprise teams, resulting in the highest enterprise participation rate among all competing markets. Twenty semi-finalists were selected before the top nine advanced to the final.
For the finalists, the work is just beginning. As Minister Ndabeni said, “Go home today proud. But tomorrow, wake up, build again.”
The issuer is solely responsible for the content of this announcement.
About Huawei
Founded in 1987, Huawei is a leading global provider of information and communications technology (ICT) infrastructure and smart devices. With 213,000 employees operating in over 170 countries, we serve more than three billion people worldwide.
Huawei is committed to bringing digital to every person, home, and organisation for a fully connected, intelligent world. In 2025, Huawei generated CNY880.9 billion in revenue, reinvesting 21.8% (CNY192.3 billion) into R&D, with about 53.7% of its employees working in R&D. As a private company fully owned by its employees, Huawei focuses on customer-centric innovation and open collaboration to create lasting value and drive technological breakthroughs globally.
For more information, please visit Huawei online at www.huawei.com or follow us on:
NightSpire has moved from an emerging ransomware operation to a fast-scaling cyber-extortion threat, using exposed Remote Desktop Protocol access, legitimate administration tools and a Tor-based leak site to pressure victims across multiple sectors. First observed in early 2025, the group has built its campaign around double extortion, stealing sensitive files before encrypting systems and then threatening public exposure if victims refuse to pay. Its operations show a […]
Iran-linked hackers have expanded cyber-espionage operations against aviation and software organisations in the United States, Europe and the Middle East, using fake recruitment pitches and search-engine manipulation to deliver malware capable of long-term surveillance and data theft. The campaign has been tied to Nimbus Manticore, also tracked as UNC1549, Screening Serpens, Smoke Sandstorm and Iranian Dream Job. The group is assessed to be aligned with Iran’s Islamic […]
Take-Two Interactive Software ended its 2026 financial year with a sharp rise in net bookings and revenue, as sustained demand for NBA 2K, Grand Theft Auto and Zynga’s mobile portfolio strengthened the company’s position ahead of the planned launch of Grand Theft Auto VI later this year. The New York-based games publisher reported fiscal-year net bookings of $6.72 billion for the year ended March 31, 2026, up […]
Security researchers have flagged a privacy weakness in WhatsApp’s Apple apps, warning that chat databases on macOS and iOS may sit unencrypted inside shared app group containers, creating a gap between the platform’s end-to-end encryption claims and the way messages are handled after they reach a user’s device. The concern centres on local storage, not message transmission. WhatsApp’s end-to-end encryption is designed to prevent outsiders, network operators […]
North Korea-linked hackers have upgraded the InvisibleFerret malware to bypass script-based security tools, converting its Python code into compiled modules that are harder for defenders to inspect and block. The campaign is attributed to Void Dokkaebi, also tracked as Famous Chollima, a threat group associated with operations against software developers, cryptocurrency firms and technology workers. The latest version uses Cython-compiled files, appearing as. pyd modules on Windows […]
THORChain has halted core network activity after a coordinated exploit drained about $10.7 million from one of its liquidity vaults, putting fresh scrutiny on the security model behind decentralised cross-chain swaps. The incident took place on May 15 and affected a single vault within the protocol’s infrastructure. Early estimates placed the loss lower, but subsequent checks revised the figure to about $10.7 million. The remaining vaults were […]
Hackers have compromised the Laravel-Lang open-source ecosystem, turning trusted PHP localisation packages into a vehicle for credential theft and remote code execution across developer machines and build systems. The attack, detected on May 22, targeted packages used by Laravel applications to manage translations, attributes and HTTP status messages. Security teams tracking the incident identified malicious activity across laravel-lang/lang, laravel-lang/http-statuses, laravel-lang/attributes and laravel-lang/actions, with more than 700 historical […]
Bitcoin’s long-term security debate has sharpened after Glassnode mapped more than 6 million coins whose public keys have already been exposed on-chain, placing assets worth about $469 billion under theoretical risk from future quantum computers. Glassnode’s analysis estimates that 6.04 million Bitcoin, or 30.2 per cent of issued supply, sit in formats or usage patterns that could become vulnerable if quantum machines become powerful enough to derive […]
Hackers are exploiting unsupported F5 BIG-IP appliances to gain SSH access to enterprise Linux systems, turning trusted edge infrastructure into entry points for deeper attacks on identity systems and internal applications. A May 22 threat intelligence disclosure detailed a multi-stage intrusion that began with an exposed F5 BIG-IP load balancer and moved through Linux infrastructure, an internal Atlassian Confluence server and eventually Active Directory. The case underlines […]
India’s rapid AI adoption is exposing weak points in software supply chain security, with enterprises expanding automated development faster than their ability to detect compromised packages, unsafe containers and unverified AI components.
A 2026 software supply chain security assessment shows that about 65 per cent of organisations in India cannot detect malicious packages, while 71 per cent do not use container security tools. The findings underline a widening gap between the speed of AI-led software development and the controls needed to secure code, dependencies, models and deployment pipelines before they reach production systems.
Security teams are facing a more complex threat environment as AI coding assistants, model registries, agent frameworks and machine-learning libraries become embedded in day-to-day software engineering. AI is no longer confined to application features or analytics layers. It is becoming part of the software supply chain itself, influencing how code is written, tested, packaged and deployed.
Enterprises in India have been quick to adopt AI tools to improve developer productivity, reduce repetitive work and accelerate product releases. Yet the same shift has increased reliance on open-source packages, pre-trained models, plug-ins and automated build systems. Each of these components can introduce hidden risks if provenance, integrity and behaviour are not continuously verified.
Global software repositories are now attracting sustained attacks because they provide a direct route into enterprise development environments. Malicious npm packages rose by 451 per cent during 2025, while more than 48,000 new Common Vulnerabilities and Exposures were disclosed worldwide, a rise of about 20 per cent from the previous year.
The pressure on security teams is being amplified by the volume of AI-generated code. Developers in India are spending about 51 per cent of their time reviewing, validating and hardening code produced by AI tools. About 53 per cent treat such output only as a starting point and review every line before use, while 11 per cent rewrite AI-generated fixes from scratch.
This shift has altered the economics of software engineering. AI may reduce the time needed to draft code, but it can also transfer effort to verification, testing and security review. Weaknesses such as cross-site scripting, SQL injection and missing authorisation checks can still be reproduced by automated tools, particularly when developers rely on generated code without adequate scrutiny.
Governance is emerging as another area of concern. Nearly 97 per cent of organisations surveyed said they had certified AI model governance programmes, but only 59 per cent claimed full provenance visibility across production environments. About 48 per cent still needed a week or longer to produce audit-ready compliance evidence.
That gap points to a difference between policy and enforceable control. Many enterprises have AI governance frameworks on paper, but fewer can prove where every model, library, container image and software artefact came from, how it changed, who approved it and whether it complies with internal policy.
CERT-In has also warned that software supply chain compromises are increasingly targeting developer tools and trusted repositories. Its April 2026 activity note referred to attacks affecting npm, PyPI, GitHub Actions and container registries, including incidents involving Checkmarx, Trivy, LiteLLM, Axios, Telnyx and npm packages linked to the CanisterWorm campaign. The payloads observed in these attacks included credential harvesting, data exfiltration, remote execution and persistence within developer systems.
Model registries have added another layer to the risk. Around 1.4 million new AI artefacts were published on Hugging Face during 2025, representing 58 per cent of all new software packages tracked in one assessment. Researchers identified 495 malicious AI models in public repositories with active payloads capable of credential theft, command execution and reverse-shell activity, along with 969 malicious AI-agent skills designed to exploit developer environments and automation workflows.
For enterprises in India, the challenge is sharpened by the country’s role as a major software engineering and global capability centre hub. Bengaluru, Hyderabad, Pune, Chennai and Gurugram host large engineering teams serving banking, retail, telecoms, manufacturing and cloud services. These centres are increasingly responsible not only for maintenance work but also for product development, AI integration and security-sensitive digital platforms.
Regulatory and customer expectations are also tightening. Buyers are asking for software bills of materials, vulnerability disclosure processes, provenance records and proof that build pipelines are protected. CERT-In’s technical guidance on SBOM, QBOM, CBOM, AIBOM and HBOM has emphasised regular updates, vulnerability exploitability exchange documents and staff training around software supply chain visibility.
Security leaders are therefore moving towards stronger controls across development pipelines. These include automated malicious package detection, container image scanning, secrets detection, signed artefacts, dependency pinning, model provenance checks, policy enforcement in CI/CD systems and continuous monitoring of developer environments.
The investment case is becoming harder to ignore. Software supply chain attacks can bypass perimeter defences because they enter through trusted development channels. Once inside, malicious packages can steal credentials, alter builds, move into cloud environments or compromise downstream customers. AI raises the stakes because it can accelerate both legitimate development and attacker experimentation.
Take-Two Interactive has moved to quiet speculation over another Grand Theft Auto VI delay, reaffirming that Rockstar Games’ blockbuster open-world title remains scheduled for release on 19 November 2026. The confirmation, issued alongside Take-Two’s fiscal 2026 results, places the game at the centre of the company’s next financial year and signals that management is still planning around one of the most consequential launches in entertainment. Chief executive […]
Apache OFBiz users have been urged to move to version 24.09.06 after disclosure of an authentication bypass flaw that can be chained to remote code execution, exposing enterprise resource planning systems to takeover through a manipulated password-change workflow. Tracked as CVE-2026-45434, the vulnerability affects Apache OFBiz versions before 24.09.06. It stems from improper authentication handling in the platform’s password-change logic, where a forced password reset condition may […]
Hackers stole parts of Grafana Labs’ codebase after gaining access to its GitHub environment through a compromised token, prompting fresh concern over software supply-chain security at a company whose observability tools are embedded across enterprise technology operations. The New York-based open source software developer said an unauthorised party accessed its GitHub environment and downloaded code after obtaining a token with repository access. The attackers then tried to […]
A fast-moving supply-chain attack has hit a broad set of npm packages linked to the @antv ecosystem, exposing developers and organisations to credential theft through malicious package versions tied to the maintainer account “atool”. The campaign, identified on May 19, 2026, appears to form part of the Mini Shai-Hulud malware wave, a self-spreading operation that has already affected other developer ecosystems through compromised open-source packages. The latest […]
Ukrainian state bodies are facing a sustained phishing campaign by the Russia-linked Gamaredon group, with attackers using weaponised WinRAR archives to deploy GammaDrop and GammaLoad malware in a multi-stage espionage operation aimed at government networks. The campaign, active since September 2025 and still evolving, has targeted Ukrainian state institutions through spoofed messages and compromised government email accounts. The emails are written in Ukrainian and designed to resemble […]
Authorities across the Middle East and North Africa have arrested 201 people in a coordinated cybercrime sweep that targeted phishing, malware and online financial fraud networks operating across 13 jurisdictions. Operation Ramz, coordinated by Interpol from October 2025 to 28 February 2026, also identified 382 further suspects and 3,867 victims, marking the first cyber operation of this scale led by the international police body across the MENA […]
Paper Werewolf has expanded its campaign against Russian industrial, financial and transport organisations, using phishing emails, fake Adobe software updates and the EchoGather remote access trojan to deepen access inside targeted networks. The Russian-language threat cluster, also tracked as GOFFEE, was active in the March-April 2026 window with a toolset that shows a clear shift from conventional phishing toward layered intrusion chains. The latest campaign begins with […]
Kelp DAO has moved rsETH back towards normal operations after a $292 million April exploit exposed weaknesses in cross-chain verification and triggered one of decentralised finance’s largest recovery efforts of the year. The liquid restaking protocol, working with Aave and other ecosystem participants, has completed the burn of exploiter-linked rsETH on Arbitrum and begun restoring the token’s backing through a staged refill into the LayerZero OFT adapter […]
Arabian Post Staff -Dubai Manama has gained another marker in its shift towards cash-light commerce as stc Bahrain became the first telecommunications provider in the kingdom to introduce Mastercard’s Click to Pay, adding a faster checkout option for customers making digital payments. The launch places the telecom operator deeper into Bahrain’s expanding financial technology ecosystem, where mobile wallets, instant transfers and tokenised card payments are becoming part […]
Security teams are racing to contain a high-severity PraisonAI flaw after exploitation attempts were detected within hours of public disclosure, underscoring how quickly attackers are probing exposed artificial intelligence infrastructure. The vulnerability, tracked as CVE-2026-44338, affects PraisonAI versions from 2.5.6 to before 4.6.34. It stems from a legacy Flask API server shipped with authentication disabled by default. Where that server is reachable over a network, any unauthorised […]



 https://www.huawei.com/za/
 https://www.linkedin.com/company/Huawei
 https://twitter.com/HuaweiSAR
 https://www.facebook.com/HuaweiSAR
 http://www.youtube.com/Huawei




