News related to
theft

Ilya Lichtenstein, the convict at the centre of one of the largest bitcoin thefts in history, has walked free from federal custody ahead of his full sentence, publicly attributing his early release to the First Step Act, a criminal justice reform law enacted in 2018 under President Donald Trump. Lichtenstein’s abrupt return to civilian life after serving about 14 months of a five-year term for laundering nearly […]

Coinbase has said a former customer-support agent has been arrested in India following an investigation into a security breach that exposed limited user data on the US-based cryptocurrency exchange, marking a significant step in efforts to trace accountability for one of the platform’s most closely watched incidents. The exchange said the individual, who had worked for a third-party support contractor, was taken into custody by law-enforcement authorities […]

  European Space Agency officials are assessing the impact of another cyber intrusion after a criminal group claimed it is offering around 200 gigabytes of agency data for sale on underground forums, raising fresh questions about the resilience of public-sector space infrastructure to sustained digital threats. The alleged breach, disclosed by the attackers through dark-web postings and shared among cybersecurity monitoring firms, is described as involving internal […]

Hackers have siphoned about $2.7 million worth of digital assets from old wallets linked to Aevo, a decentralised options and perpetuals exchange, underscoring persistent security risks tied to legacy infrastructure in the crypto market. The breach did not affect Aevo’s core trading systems or user funds held in active contracts, but it has revived scrutiny of how exchanges manage dormant or transitional wallets long after platform upgrades. […]

A sophisticated cyber-espionage campaign attributed to North Korean state-linked hackers has exploited a critical vulnerability in React Server Components to deploy a stealthy remote access trojan known as EtherRAT, security researchers and incident responders say. The operation highlights a convergence of web application flaws and blockchain-based command-and-control techniques that complicates detection and response for organisations running modern JavaScript stacks. The attack chain centres on a flaw dubbed […]

A decision to withdraw a controversial directive on compulsory smartphone app preinstallation has been taken by the authorities after sustained objections from device makers and technology firms. The policy reversal follows intense debate over whether phone manufacturers should be required to preload the government’s Sanchar Saathi platform, amid concerns about user privacy, operating system integrity and compliance burdens. The shift comes less than two days after reports that Apple had declined to adopt the mandate, setting off a wider industry pushback that accelerated the measure’s rollback.

Officials confirmed that the mandatory installation plan has been shelved, indicating that further consultations will be held before any such directive is reconsidered. The original order sought to ensure that every new smartphone sold in the country carried Sanchar Saathi, a platform designed to help users trace lost devices, block stolen handsets and verify mobile connections. While the tool is already available for voluntary download, stakeholders argued that forcing manufacturers to embed it at the system level risked creating fragmentation across devices, complicating software updates and compromising user choice.

Senior executives from major handset brands expressed relief at the reversal, noting that the directive had introduced uncertainty at a time when the phone market is preparing for a competitive year-end cycle. Apple, which typically restricts preinstalled third-party apps to maintain strict control over its ecosystem, had reportedly conveyed through official channels that compliance would conflict with long-standing platform policies. That position highlighted the technical complexities of enforcing a uniform preinstallation rule across operating systems that function on entirely different architectures. Android phone makers had also raised procedural questions, cautioning that mandatory system additions could require extensive vetting, security reviews and manufacturer-specific testing.

The broader industry reaction underscored concerns about data governance and user rights. Digital rights groups argued that preloading state-linked applications without explicit user consent could set a troubling precedent, even if the stated aim of the app was consumer protection. Cybersecurity specialists added that any software embedded at the system level must undergo rigorous, transparent auditing to prevent vulnerabilities that malicious actors could exploit. They warned that compulsory integration could expand the attack surface on devices at a time when financial fraud, phone cloning and identity theft cases continue to grow.

Officials involved in policymaking acknowledged that the industry’s logistical and legal objections played a decisive role in halting the order. They said the withdrawal would allow departments to reassess the technical feasibility of the measure and examine alternative ways to boost the adoption of Sanchar Saathi without imposing new conditions on manufacturers. The platform, launched by the Department of Telecommunications, has gained traction through voluntary use, particularly for blocking stolen phones via the Central Equipment Identity Register. Policymakers are studying whether awareness campaigns, improved onboarding flows and coordination with telecom operators could enhance user uptake more effectively than preinstallation.

Market analysts described the reversal as a pragmatic move aimed at preventing friction between the government and global technology firms, particularly at a time when the country’s digital manufacturing ambitions remain in focus. Apple, which has expanded iPhone assembly through local partners, is seen as a critical participant in that strategy. Analysts said any regulatory action that appears to conflict with its operating standards risks diluting investment momentum. They added that Android manufacturers, many of whom operate extensive local supply chains, would also have faced significant re-engineering work to align with the directive.

Industry groups emphasised that while supporting consumer safety initiatives, they prefer interventions that preserve user autonomy and maintain consistent software governance standards. Stakeholders reiterated that preinstallation mandates, unless narrowly tailored and transparently justified, can lead to compatibility issues and unintended consequences across a diverse device ecosystem. They also highlighted that global smartphone markets increasingly recognise the importance of limiting bloatware and avoiding compulsory system-level apps that cannot be removed by users.

United Kingdom legislation now formally recognises digital assets such as cryptocurrencies and stablecoins as personal property, offering holders protections under established property law. The Property Act 2025 — previously a bill — received royal assent, confirming that digital tokens may be treated as a third category of personal property alongside traditional “things in possession” and “things in action.” This marks a decisive shift from earlier reliance on case-by-case rulings by courts.

Legal recognition ensures that crypto-owners gain enforceable rights in instances of theft, fraud or insolvency, and enables digital assets to be included in estates or bankruptcy proceedings under the same protections afforded to conventional property. The Act does not itself define which digital assets qualify — courts will decide those details over time.

Judicial developments had already begun to lay the groundwork for this change. As early as 2019, the UK Jurisdiction Taskforce concluded that crypto-assets met criteria for property under English law: they could be defined, identified, transferred and treated as assets capable of value retention. A key case, AA v Persons Unknown, saw the High Court of England and Wales recognise Bitcoin provided as ransom in a cyber-attack as property, granting the insurer a proprietary injunction.

Advocates of the law hailed it as providing clarity long sought by individuals and businesses holding crypto-assets. CryptoUK, a leading trade body for digital assets, noted that while courts had already treated crypto as property in some cases, codifying the principle into statute removes uncertainty and streamlines legal protections across theft, insolvency and estate-related scenarios.

Legal experts say the Act reflects the recommendations laid out by the Law Commission in a 2023 report, which urged reform to ensure the law could accommodate emerging digital assets under a flexible yet robust framework. The Commission argued that existing categories of personal property under law were too rigid to account for assets that lacked physical form or contractual rights.

This statutory change arrives as UK regulators concurrently refine the broader regime for crypto-assets. Draft legislation published earlier this year already seeks to amend the Financial Services and Markets Act 2000 to designate certain “qualifying cryptoassets” and “qualifying stablecoins” as regulated investments, bringing market-level rules for trading, custody and compliance under formal oversight.

While the law does not render cryptocurrency a legal tender — meaning it still cannot be used to settle debts in substitute for currency — its classification as property gives holders legal certainty over ownership and enforceable rights. Taxation and regulatory treatment will continue to follow established frameworks, though this legal milestone reduces ambiguity over the status of crypto-assets in private law contexts.

Judges, lawyers and market participants anticipate that the Act will lead to a more stable and predictable legal environment for crypto-asset ownership, enabling individuals and institutions to treat tokens with the same legal respect accorded to traditional assets. As the courts start applying the new law in real cases, the boundaries of which digital assets qualify will grow clearer — and the UK’s position as a regulatory pioneer in digital asset law will be reaffirmed.

Advertisements

Smartphone makers in India have been instructed by the telecom ministry to preload a government-owned cybersecurity app on all new devices sold in the country, blocking users from deleting the application once installed. Under a directive issued on November 28, companies such as Apple, Samsung, Vivo, Oppo and Xiaomi have been given a 90-day window to ensure all handset models destined for India include the Sanchar Saathi app. For devices already in the retail pipeline or those awaiting sale, manufacturers must deliver the app via over-the-air software updates and ensure it appears prominently during first-use setup.

Authorities say the app plays a key role in telecom security by giving users tools to verify device authenticity through IMEI checks, report suspected thefts or fraud, and block lost or stolen phones. Since the app’s launch in January 2025, government data indicates it has helped recover over 700,000 lost devices and block millions of connections flagged as fraudulent. Officials argue that this move is critical to counter growing misuse of duplicate or tampered IMEI numbers—a problem that fuels scams and the resale of stolen phones across India’s vast second-hand device market.

This mandate marks the first time the government has required a permanently installed, non-removable application on all smartphones sold in the country. The decision reflects a broader tightening of regulatory oversight over telecom infrastructure and device authenticity, drawing parallels with security measures in other jurisdictions.

The requirement has triggered sharp criticism from technology companies and privacy advocates alike. For example, the policy of Apple prohibits pre-installation of third-party or government apps prior to device sale—an approach that could force the company to either seek exemptions or find workarounds. Industry representatives have warned that the mandate may strain compliance operations, increase production costs, and undermine relationships with handset vendors.

Beyond logistical concerns, digital rights groups argue the rule tramples on user consent and privacy. Critics contend that embedding a state-run app with potentially broad access on every phone amounts to unwarranted surveillance and sets a troubling precedent. Some lawmakers and civil liberties advocates dubbed the move “a Big Brother measure,” warning that once entrenched, such mandates could be expanded further, eroding individual privacy without adequate data-protection safeguards.

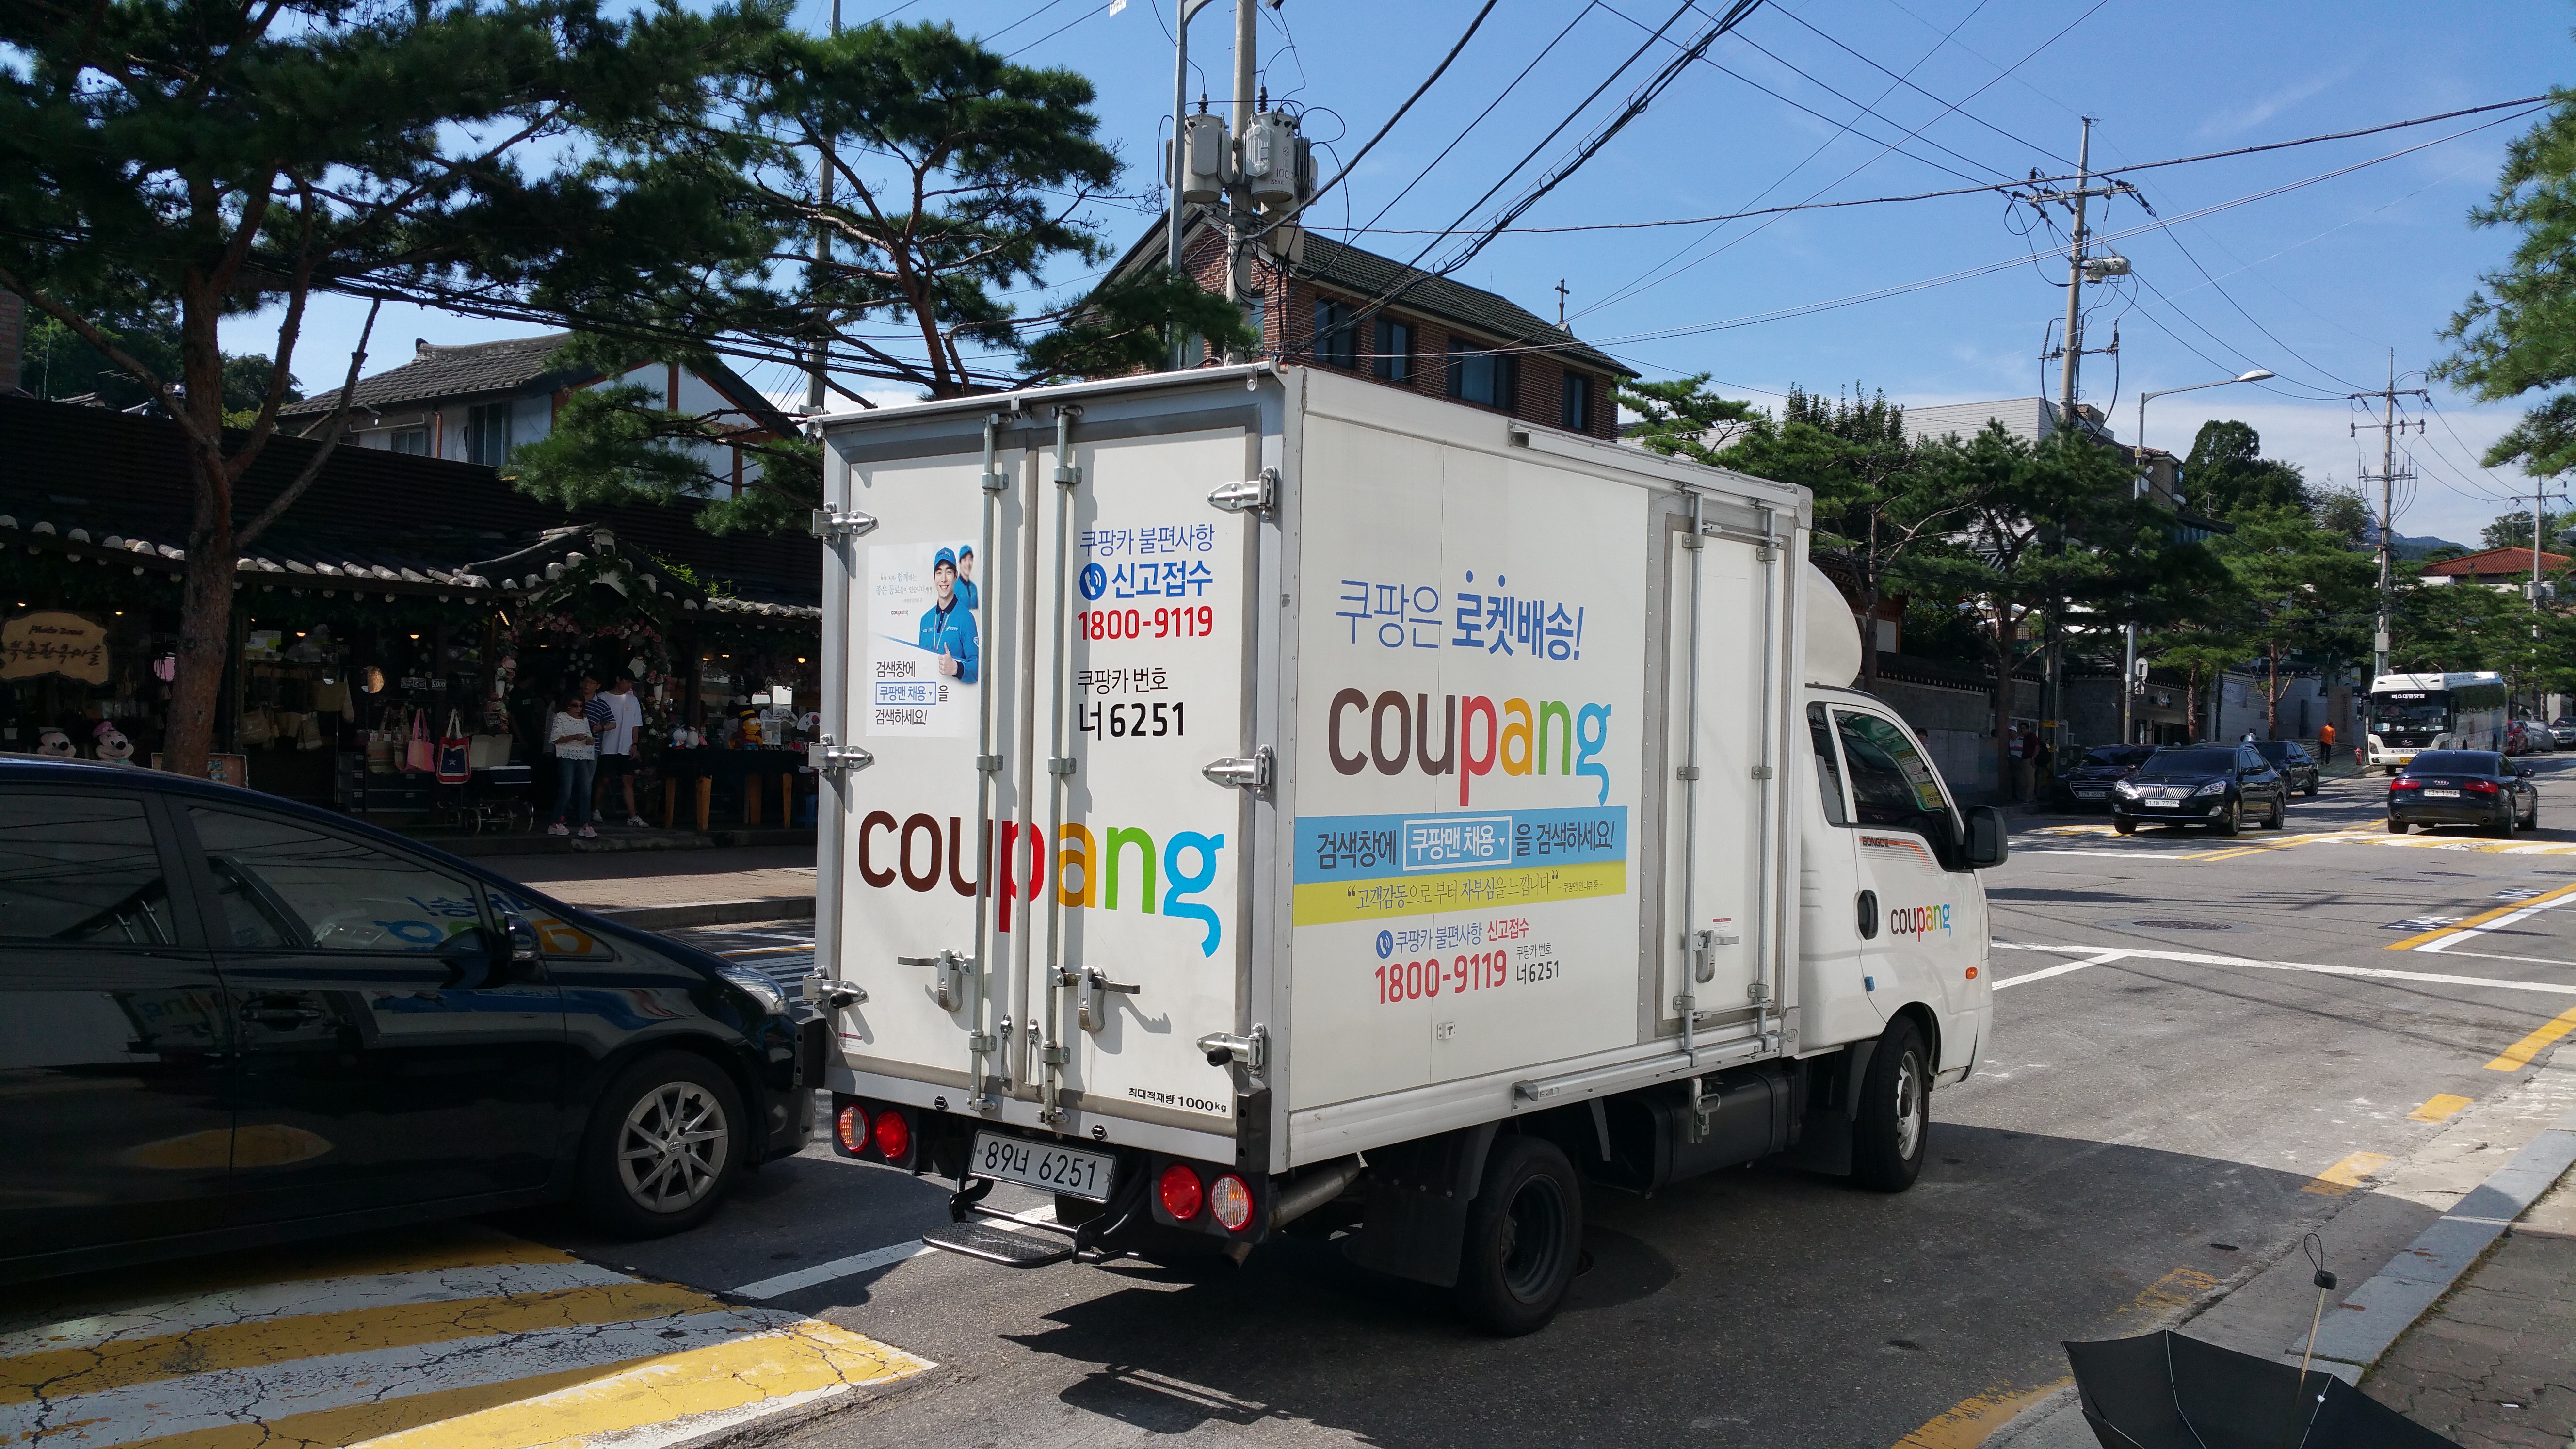
Coupang has admitted that unauthorised access exposed the personal information of 33.7 million customer accounts, marking the worst data leak in South Korean history. The leaked data includes names, email addresses, phone numbers, delivery addresses and some order histories, while payment credentials and login details are said to remain secure. The breach first began on 24 June and remained undetected until 18 November, when the company discovered suspicious access affecting about 4,500 accounts — a figure swiftly revised upward as investigators uncovered the full scale of the leak.

Police investigators are analysing server logs and have identified the IP address used in the attack, triggering efforts to trace the suspect. Authorities have not confirmed the nationality of the person under suspicion, though local media have pointed to a former employee of Chinese origin. Coupang filed a formal complaint on 25 November under legislation covering unauthorised access and data theft, and the probe has since turned into a full-fledged criminal investigation.

In response to mounting public concern, the Ministry of Science and ICT convened an emergency meeting to examine whether Coupang violated national data-protection laws. The government has warned that the exposed information — though not financial in nature — could easily be used for phishing, identity theft or other scams, particularly given the extent of the leak and the volume of personal data involved.

Coupang says it blocked the breach route as soon as the intrusion was confirmed and has engaged external cybersecurity experts to strengthen internal monitoring. The firm also issued a public apology through its chief executive, pledging full cooperation with law enforcement and regulatory bodies.

OpenAI disclosed a data breach involving its analytics provider Mixpanel, confirming that a security lapse allowed unauthorised access to certain API user details but did not compromise ChatGPT message data or model-generated content. The company informed affected developers that the incident, traced to November 2025, exposed names, email addresses and limited account-related metadata, prompting a broader review of third-party integrations across its platform. OpenAI stated that the […]

South Korea’s largest cryptocurrency exchange saw roughly $36 million drained from its hot wallet linked to the Solana network in what officials describe as an “abnormal withdrawal”. The breach triggered an immediate freeze on deposits and withdrawals. The operator, Dunamu, moved remaining assets into cold storage and pledged to fully reimburse all affected users.

Authorities in Seoul identified the hacking group Lazarus Group — long associated with previous crypto thefts — as the prime suspect behind the intrusion. Investigators plan an on-site inspection of Upbit’s systems to determine how attackers bypassed security protocols.

The tokens siphoned off included SOL alongside several Solana-ecosystem assets. Observers noted that the attack bears striking resemblance to a prior Upbit breach in 2019 — when 342,000 ETH disappeared under circumstances later attributed to Lazarus and associated groups.

Security firms monitoring on-chain flows report that the speed and pattern of withdrawals mirror those from Lazarus-linked incidents. Analysts warn that the hack underscores persistent vulnerabilities when hot wallets — the always-online accounts exchanges use for frequent transactions — remain exposed to governance failures or credential compromises.

The timing of the incident coincided with a corporate milestone for Dunamu: the day saw the public announcement of a planned merger with technology firm Naver. Some security experts speculate that the attackers might have deliberately chosen the moment to maximise impact on market confidence and regulatory attention.

Upbit’s management emphasised that user assets held in cold storage remained untouched. The company began working immediately with token issuers and blockchain-analytics firms to freeze traceable stolen funds. Officials involved in the probe noted the laundering techniques — rapid mixing of tokens across multiple wallets and networks — reflect a refined modus operandi honed over several high-profile attacks.

Malaysia’s national utility firm Tenaga Nasional Berhad recorded losses of about RM 4.57 billion stemming from illegal electricity usage linked to cryptocurrency-mining operations between 2020 and August 2025. The Ministry of Energy Transition and Water Transformation disclosed that 13,827 premises were identified for unauthorised power use in bitcoin-mining setups.

The scale of the issue has triggered coordinated action by TNB alongside law-enforcement agencies, the communications regulator and the anti-corruption commission to shut down illegal crypto-mining hubs and recover mining equipment. Monitoring and detection systems have been upgraded, including the deployment of smart meters and a database of suspect premises created to track owner-tenant information.

The ministry emphasised that tampering with electricity meters or bypassing supply connections remains a breach of the Electricity Supply Act, even though crypto-mining per se is not illegal in Malaysia provided it meets regulatory registration, environmental assessment and energy-efficiency requirements.

Experts note that large-scale crypto-mining demands heavy and continuous power consumption, making utilities vulnerable to theft and grid stress. Analysts warn that if unaddressed, rampant unauthorised mining can undermine revenue streams, force higher tariffs for compliant users and increase risk of transformer or grid overload. TNB has reported that illicit mining not only deprives the utility of revenue, but often leaves behind damaged equipment, fire hazards and voltage instability.

TNB’s response includes launching a pilot “Distribution Transformer Meter” project that monitors usage at the transformer level to detect anomalies, and rolling out smart-metering at substations for real-time tracking of energy flows. These technical steps complement legal and enforcement action, with the utility and authorities conducting raids, seizing mining machines, and pursuing criminal charges under offences related to meter interference.

Regulators say the problem is acute because of Malaysia’s relatively affordable electricity and benign regulatory regime for data-centres, making it an attractive venue for crypto-miners operating on razor-thin margins for global digital-asset mining operations. Observers say tighter regulation globally of crypto-mining, along with rising power costs, have driven more miners to jurisdictions with weaker enforcement or cheaper energy. This trend adds urgency for utilities worldwide to bolster monitoring and enforcement frameworks.

Smart cities have emerged as a transformative vision for the future of urban life, integrating cutting-edge technologies to enhance living standards, boost sustainability, and improve service efficiency. However, as these cities evolve, they face growing concerns regarding cybersecurity. With vast amounts of sensitive data being collected, processed, and transmitted across networks, securing these data exchanges is paramount. The role of modern cryptographic solutions in safeguarding these environments […]

DoorDash, the popular food delivery service, has confirmed that a cyber attack has compromised the personal data of millions of users. The breach, which has sparked significant concern, was the result of a sophisticated social engineering attack targeting the company’s systems. This incident has exposed sensitive user information, including names, email addresses, phone numbers, and in some cases, delivery addresses. The breach reportedly affected users across four […]

Cybersecurity breaches are becoming an increasingly costly issue for Indian enterprises, with nearly a quarter of organisations reporting losses exceeding $1 million over the past three years. This has prompted a sharp uptick in cybersecurity spending, especially in artificial intelligence and cloud security solutions, as businesses aim to protect themselves from sophisticated cyber threats. However, the sector still faces significant challenges, particularly in securing skilled talent to manage the growing complexity of cyber risks.

A recent report by PricewaterhouseCoopers highlights that 23% of Indian businesses have incurred losses of over $1 million due to cyber incidents, underscoring the severity of the issue. These breaches range from data theft and ransomware attacks to more advanced persistent threats targeting critical infrastructure. PwC’s findings suggest that the financial impact on Indian firms is only likely to rise as cybercriminals become more organised and capable, exploiting vulnerabilities in emerging technologies and systems.

The shift towards digital transformation and cloud adoption has undoubtedly exposed businesses to greater risk, with sensitive data being increasingly stored and accessed online. According to PwC, the cloud is now seen as both a critical business enabler and a potential vulnerability. As cloud infrastructures evolve, they are often targeted by cybercriminals seeking to exploit misconfigurations and inadequate security protocols.

In response, Indian businesses are ramping up their cybersecurity investments. Spending on AI-driven security solutions is one of the key focus areas. These technologies allow businesses to proactively identify and neutralise threats in real-time, enabling a faster response to evolving attack patterns. AI is particularly useful for detecting abnormal behaviour and potential risks that traditional security systems might miss. It is also being leveraged for predictive analytics to foresee potential vulnerabilities before they can be exploited by malicious actors.

However, despite the increased allocation of funds towards cybersecurity, the shortage of skilled professionals remains a significant roadblock. The demand for cybersecurity experts far outweighs the supply, with firms struggling to recruit individuals with the necessary expertise in areas such as AI, cloud security, and threat intelligence. The PwC report indicates that many organisations are forced to rely on third-party vendors to manage their cybersecurity needs, further driving up costs.

Experts suggest that to address the talent gap, Indian firms must invest in long-term solutions, such as upskilling existing employees and forging partnerships with educational institutions to nurture the next generation of cybersecurity professionals. The government has also been urged to play a more proactive role by fostering public-private collaborations to enhance the country’s overall cybersecurity ecosystem.

The rise of AI and cloud technologies has, however, brought additional complexities. While these tools can greatly improve security, they also introduce new attack vectors. Cloud environments, if not managed properly, can expose businesses to significant risks, including data breaches and unauthorised access. Moreover, the increased use of AI-driven solutions can create new challenges, such as ensuring the ethical deployment of AI and protecting against adversarial AI attacks.

Despite these hurdles, the Indian cybersecurity landscape is expected to see significant improvements over the coming years. As businesses continue to embrace AI and cloud technologies, security budgets are likely to increase, with a stronger emphasis on automated security measures and real-time threat detection. Additionally, as the global cyber threat landscape evolves, businesses are expected to collaborate more closely with government agencies and international organisations to stay ahead of cybercriminals.


AI video tool Sora 2, developed by OpenAI, has drawn sharp criticism from privacy advocates, Hollywood, and creators over the potential risks it poses in generating deepfake content. Advocacy group Public Citizen is among those calling for the tool’s immediate withdrawal, citing concerns that the app could be misused to produce non-consensual imagery and undermine democracy. The tool, which uses AI to generate videos from text-based prompts, […]

A new wave of malware attacks has been discovered targeting Android users in South Korea, with the attackers concealing harmful software in applications promoting stress relief and relaxation. This sophisticated attack takes advantage of Google’s asset-tracking service, Find Hub, to remotely erase sensitive user data, raising concerns about state-sponsored cyber threats. These attacks are disguised as psychological counselling tools or programs supporting North Korean human rights, allowing […]

The shift towards subscription-based streaming and the rise in unauthorised distribution is exposing fundamental flaws in how consumers acquire digital media. Many users believe they “own” films, music or books that they purchase online, but industry analysts say what they actually hold is a license to access content under strict terms and conditions. One expert writes: “Most of us don’t control the files, formats, keys and servers. […]

A sophisticated phishing campaign has enabled attackers to compromise a maintainer account within the npm ecosystem, triggering one of the largest software-supply-chain breaches recorded. On 8 September 2025 the attacker gained access to the account of developer Josh Junon, and proceeded to publish malicious updates to widely used packages including “chalk” and “debug”. The versions laced with crypto-theft malware reached libraries that collectively recorded over 2 billion […]

Amazon has activated a sweeping measure across its Fire TV Stick and Fire TV device lineup to block applications that provide unauthorised access to premium films, television and live sport. The initiative is anchored in a collaboration with the anti-piracy coalition Alliance for Creativity and Entertainment. According to Amazon, apps known to offer infringing streams — including those sideloaded from outside the official App Store — will […]

A new wave of supply-chain assaults has seen North Korean hackers publish more than 300 malicious npm packages, infecting developer systems with sophisticated malware that steals credentials and crypto assets. The campaign, known as “Contagious Interview,” exploits the trust developers place in open-source tools by cloaking malware inside packages mimicking legitimate ones.

The Socket Threat Research Team disclosed that attackers uploaded 338 malicious npm modules, collectively downloaded over 50,000 times, many featuring a newly observed loader named XORIndex. About 27 of them remain active in the npm registry. Within those packages, XORIndex collects host metadata and downloads a second-stage payload, BeaverTail, which in turn leverages a backdoor called InvisibleFerret to maintain persistence and exfiltrate data. This expansion follows a preceding June surge of 35 malicious modules using a HexEval loader.

Researchers emphasise that Contagious Interview is not a static campaign but a dynamic interplay between defenders and adversaries. As packages are taken down, attackers quickly reissue variants under fresh aliases or change loader techniques. The latest 67-package load pushed last month illustrates this cat-and-mouse escalation: the new modules alone exceeded 17,000 downloads. Attackers have mixed XORIndex and HexEval in parallel deployments, suggesting modular development and adaptability.

The campaign’s social engineering backbone remains key. Actors pose as recruiters or HR contacts on platforms like LinkedIn, targeting software engineers or job-seekers. They offer interview assignments that require cloning a GitHub or Bitbucket repository, with the malicious npm module embedded deep in the project. Because many developers run these projects outside sandboxed environments, the malicious loader quietly executes and bridges the gap to full system compromise.

Analysts attribute Contagious Interview to DPRK-aligned threat groups tracked under names such as CL-STA-0240, DeceptiveDevelopment, Tenacious Pungsan and Void Dokkaebi. The methodology aligns with patterns shown by the Lazarus Group and its affiliates, as attackers continue to weaponise open source ecosystems for espionage and financial theft. XorIndex and HexEval share infrastructure and tactics, including encrypted communication with command-and-control servers. In several cases, submitters of the malicious packages have crafted repository names containing “interview,” reflecting the campaign motif.

Beyond npm, the campaign’s reach extends: some modules reference Bitbucket repositories, and similar tactics have appeared in PyPI package attacks. The broader goal appears dual: accessing developer environments to steal intellectual property or credentials and siphoning cryptocurrencies from wallets detected on compromised machines.

Security firms and registry maintainers have responded with takedown requests and account suspensions. Socket reported removing six live HexEval-based modules earlier this year, and the npm security team has collaborated to suspend associated accounts. But defenders admit the reactive posture is fragile; attack waves resurface within hours.

SYDNEY, AUSTRALIA – Media OutReach Newswire – 13 October 2025 – Faraj Defence Lawyers has released new research highlighting the sharp rise in retail theft across Sydney and its connection to the city’s worsening cost-of-living crisis. The report finds that while financial strain is driving theft in some suburbs, in others the surge is driven more by opportunity within busy retail zones. Rising Cost-of-Living Pressures Sydney households […]

The US Commerce Secretary has warned that reliance on DeepSeek’s artificial intelligence models is “dangerous and shortsighted,” amid findings that they are more vulnerable to hacking and underperform against US systems. An evaluation by the Center for AI Standards and Innovation within NIST compared DeepSeek’s R1, R1-0528 and V3.1 models with leading US systems—including OpenAI’s GPT-5 series and Anthropic’s Opus 4—on 19 performance and safety benchmarks. The […]

Environmental analysts and transport groups have called for a major shift in Uganda’s boda-boda motorcycle sector, urging adoption of electric bikes as a means to curb greenhouse gas emissions, improve air quality, and relieve economic burdens on riders. A health-impact modelling study led by Dr Gabriel Okello and Dr Lambed Tatah found that converting petrol-powered boda-bodas in Kampala to electric ones could lower fine particulate matter levels […]

VISHNU RAJA
RYO YAMADA
HITORI GOTOH
IKUYO KITA