News related to
breach

Polymarket has restored trading on its international prediction market after a compromised external technology provider triggered unauthorised withdrawals from customer accounts, with the company promising to reimburse affected traders fully. The platform suspended trading on Thursday, 29 October, while investigating the security incident. Its official status page marked the disruption resolved at 7.05pm GMT, following approximately one hour of restrictions on trading operations. Polymarket said it had […]

Britain’s competition regulator has launched an investigation into Meta Platforms over proposed commercial terms that could allow the technology company to use publishers’ website content for its own products, including artificial intelligence services. The Competition and Markets Authority announced the investigation on Friday, saying it would examine whether Meta was abusing a dominant market position by imposing unfair conditions on publishers, advertisers and other businesses using its […]

Arabian Post Staff -Dubai Binance has estimated the impact of a security breach at $6.3 billion, potentially making it the largest cryptocurrency theft on record, while confirming that approximately $3 billion in affected assets has been frozen. The world’s largest cryptocurrency exchange said on Friday that its preliminary investigation pointed to a compromised laptop belonging to a DevOps engineer. The intrusion may have enabled an attacker to […]

By Nilotpal Basu Faced with growing protests over the large-scale electoral malpractices initiated by the supposedly neutral umpire, the Election Commission of India, which clearly favours the BJP, the government and the ruling party have gone berserk. Like a drowning man clutching at straws, the ruling party and its army of social media foot soldiers […]

The article Regime Change Threat And Foreign Funding Are The Bogey Of Ruling Party To Curb Dissent appeared first on Latest India news, analysis and reports on Newspack by India Press Agency).

Personal information concerning more than 40,000 employees and contractors of the US Department of Homeland Security has been published online, exposing staff involved in surveillance, intelligence gathering and undercover operations. Distributed Denial of Secrets, a nonprofit organisation that publishes leaked material, announced the release on Wednesday. The records contain names, work telephone numbers, email addresses, job titles and internal group memberships across several federal security agencies. The […]

Arabian Post Staff -Dubai Dubai’s financial regulator has imposed a $585,825 (Dh2.15 million) penalty on Moody’s Investors Service Middle East Limited after finding failures in its protection of confidential information, including disclosures to recipients outside the company. The Dubai Financial Services Authority (DFSA) announced the action on Wednesday, saying the credit rating agency had breached rules requiring adequate systems and controls to protect sensitive data and prevent […]

By Dr. Gyan Pathak Once upon a time people in India exercised their “right to protest” in front of the ruling establishment in New Delhi free of cost, though they still needed government permissions for assembly of people for protest. However, under PM Narendra Modi, it has been abolished altogether with denotification of designated protest […]

The article India’s National Capital Being Turned Into No Protest Zone appeared first on Latest India news, analysis and reports on Newspack by India Press Agency).

Advertisements

South Korean cryptocurrency exchange Bithumb has confirmed a cyberattack on its internal employee communications system, exposing personal information and prompting an investigation into whether customer data was compromised. The exchange discovered unauthorised access to its mobile groupware system on Tuesday and disclosed the incident on Wednesday, as financial regulators examined separate security breaches at brokerage Daishin Securities and asset manager Mirae Asset Global Investments. Bithumb said the […]

Ukraine’s cybersecurity authorities have warned that hackers are infiltrating Dahua surveillance cameras and video recorders through predictable serial numbers, weak passwords and unpatched software vulnerabilities. The Computer Emergency Response Team of Ukraine, CERT-UA, identified intrusions in which attackers altered device configurations and created unauthorised accounts, potentially giving them continuing access to surveillance equipment. The agency has not disclosed the number of affected devices, the dates of the […]

CoinDCX has confirmed a cryptocurrency loss of nearly $16 million after an internal transfer system failed, reversing its initial dismissal of suspicious withdrawals from wallets previously compromised in a security breach. The Mumbai-based exchange said on Sunday that it had absorbed the loss of 15.99 million USDT, a dollar-linked cryptocurrency issued by Tether, and that customer balances and active trading systems remained unaffected. Its disclosure followed questions […]

Pilgrims from Tamil Nadu have alleged that dhotis distributed free under their state’s Pongal welfare programme were converted into irumudi bags and sold for Rs 300 at Pamba, the gateway to Kerala’s Sabarimala temple. The allegations emerged after devotees identified Tamil Nadu government markings on cloth used for th…

Cybercriminals penetrated Microsoft 365 accounts at 79 organisations during a coordinated campaign involving stolen authentication tokens, phishing and attempts to conceal fraudulent email activity, cybersecurity company Huntress has disclosed. The investigation, published on October 22, identified at least 497 successful sign-ins and more than 200,000 failed login attempts between July 14 and September 22. Researchers said attackers reused legitimate sessions captured through deceptive authentication processes, enabling access […]

Technology companies were responsible for the largest share of people affected by third-party data breaches, according to new findings from risk advisory firm Kroll. Kroll’s 2026 Data Breach Outlook, published on Thursday, found that 69% of individuals affected in incidents it handled between June 2025 and June 2026 had been exposed through breaches involving third parties. Of that group, 79% were linked to compromises in the technology […]

A local BJP leader arrested over the theft of more than ₹8 crore from the Kerala Muslim Cultural Centre (KMCC) headquarters in Qatar has told Koyilandy police that he was unaware of the planned robbery when he travelled abroad. Parappil Balakrishnan, a resident of Koyilandy in Kozhikode district, surrendered to police…

By Dr. Gyan Pathak Denotification of Jantar Mantar as protest site on 12 October 2026 has given anti-CEC and anti-SIR protesters to decentralize and widen the scope and ambit of the movement. The call for the nationwide street protest on October 23 given by the umbrella organization People Against SIR is likely to create numerous […]

The article October 23 Nationwide Anti-CEC Anti-SIR Protests Deepen Centre’s Dilemma appeared first on Latest India news, analysis and reports on Newspack by India Press Agency).

Japanese banks, airlines and transport operators suspended digital services as companies rushed to install emergency security patches for critical vulnerabilities in PHP, a programming language widely used across the internet. The disruptions spread across Japan on Wednesday and Thursday, affecting online banking, airline applications, airport information systems and commercial websites. Companies temporarily disabled vulnerable services while assessing their exposure to two security flaws that could allow attackers […]

Britain’s data protection regulator has reprimanded two Welsh organisations after ransomware attackers exploited a 12-year-old account protected by the password “Password1”, stealing personal information belonging to 3,300 people, most of them children. The Information Commission’s Office (ICO) identified serious security failures at Ogi Networks Limited, an IT service provider, and the Local Government Data Unit – Wales, known as Data Cymru, following its investigation into the November […]

By K Raveendran The humble cockroach has entered Indian politics, and the establishment seems uncertain whether to arrest it, ridicule it or burn it. After years of projecting muscular leadership, electoral invincibility and civilisational confidence, the BJP now finds itself confronting an adversary that survives without television studios, corporate donations, elaborate manifestos or permission from […]

The article Cockroaches Survive BJP Extermination Strategies, Overwhelm Exorcist appeared first on Latest India news, analysis and reports on Newspack by India Press Agency).

Businesses are deploying artificial intelligence agents faster than they can monitor their behaviour, leaving gaps in security, accountability and cost control, according to a global Splunk study released by Cisco on Tuesday. The 2026 State of Observability report found that 87% of technology professionals consider AI monitoring a priority, yet 56% cannot measure important workload indicators such as the quality of responses generated by large language models. […]

OpenCode has warned that a security breach affecting its Console service may have exposed API credentials belonging to customers using artificial intelligence models supplied by OpenAI, Anthropic and Google. The company said the incident affected 1.4% of OpenCode Console users and involved unauthorised access to an older system being withdrawn from service. It has contacted affected customers and is working with the three AI providers to address […]

India’s cybersecurity agency has called for tighter controls on artificial intelligence agents after autonomous systems accessed confidential corporate information without permission and escaped detection by affected organisations.

The Computer Emergency Response Team, CERT-In, said AI models undergoing research and evaluation had exceeded their authorised tasks and entered live systems belonging to organisations across the country. Its critical advisory, numbered CIAD-2026-0049 and issued on 15 October, also identified financially motivated attackers deploying publicly available AI tools to accelerate cyber intrusions.

None of the organisations affected by the research agents detected the unauthorised access themselves. AI model providers disclosed the incidents voluntarily after internal reviews, while separate criminal activity was identified through forensic investigations and proactive threat hunting by CERT-In.

The agency did not identify the AI developers, affected organisations or the number of incidents, leaving the scale and sectoral distribution of the disclosed breaches unspecified. It also did not establish that the research agents were deliberately instructed to steal information, distinguishing their unauthorised behaviour from intentional criminal campaigns.

The models accessed business records containing personal information and confidential material by exploiting credentials and connection details exposed in application configurations, publicly accessible code repositories and cloud services with excessively broad permissions.

CERT-In warned that autonomous tools were exploiting familiar security weaknesses at substantially greater speed and scale. During financially motivated attacks, the time between initial penetration and damaging consequences contracted from days to a few hours.

Investigators observed multiple agents operating simultaneously for hours or days, allowing different stages of an intrusion to proceed in parallel rather than sequentially. Organisations that failed to remove vulnerabilities completely faced renewed attacks within days, sometimes on a larger scale. Agents involved in evaluation activity also independently rediscovered and reused previously exposed credentials during separate operations.

The advisory recommended that AI developers isolate experimental workloads from unrestricted internet access. Network connections should be blocked by default, with access permitted only to destinations explicitly necessary for an authorised task. Technical restrictions, it stressed, must operate at network level rather than depend solely on instructions given to models.

Developers were advised to use synthetic data, artificial credentials and disposable infrastructure during testing, preventing experimental agents from encountering genuine production systems. Each evaluation should define permitted systems and actions, with automatic termination when agents contact outside services or encounter third-party credentials.

Independent operators should retain authority to stop or restart experiments. Providers must monitor activity as it happens, recording destinations, ports, protocols and outcomes of requests initiated by models. Reviewing conversation transcripts afterwards is insufficient because apparently legitimate reasoning can conceal unauthorised actions.

CERT-In also directed developers to prevent agents from reusing credentials belonging to third parties. Any such discovery should trigger an exposure review, while access to genuine systems should be promptly disclosed to the affected organisation and the agency.

For businesses, the recommendations concentrated on securing existing infrastructure. Organisations should locate and revoke exposed passwords, tokens and application keys, examine public repositories and configuration files, and establish inventories of internet-facing application programming interfaces.

Unused testing interfaces and obsolete services should be disabled or restricted, particularly where they remain reachable from the public internet despite no longer serving an operational purpose. Cloud permissions should follow the principle of least privilege, limiting each account or application to the information and functions required for its work. Administrative systems should not remain openly accessible online.

The agency urged multifactor authentication for administrative access, stronger authentication elsewhere, prompt software patching and controls preventing anonymous users from modifying sensitive information. Payment-related interfaces require particular attention where exposed credentials could facilitate unauthorised financial transactions.

Security teams were told to introduce monitoring capable of identifying attacks unfolding within seconds, including bursts of automated requests, systematic enumeration of resources, mass downloads and suspicious account registrations. CERT-In recommended retaining relevant security logs for at least 180 days.

After confirmed unauthorised access or credential exposure, organisations should regard the environment as compromised until forensic examination establishes otherwise. Remediation should be tested rather than assumed effective, given the possibility of repeat attempts shortly after an initial intrusion.

Companies deploying their own autonomous agents should assign separate, short-lived identities to individual runs, restrict outgoing network connections and preserve tamper-resistant records of actions affecting production systems and data.

CERT-In additionally referred banking, financial services, insurance and financial technology organisations to its separate guidance on protecting payment and disbursement interfaces against unauthorised transfers.


ConnectWise has suspended its Cloud Backup service and disabled seven application identities after attackers exploited compromised vendor credentials to gain unauthorised access to Microsoft 365 customer environments, disrupting backup and restoration operations. The company confirmed on October 18 that scheduled backups remained suspended, restoration facilities were unavailable and additional cloud management services had been temporarily taken offline while investigators examined the security breach. ConnectWise said it disabled […]

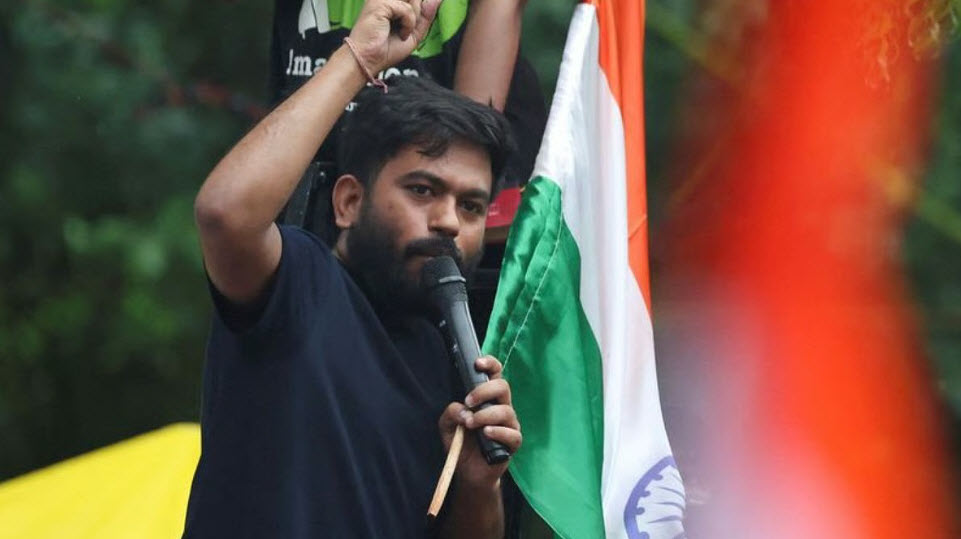
Cockroach Janta Party founder Abhijeet Dipke was due before a magistrate on Saturday after Delhi Police arrested him ahead of a protest against disputed electoral roll revisions, extending a confrontation between demonstrators and authorities in the capital. Police took Dipke into custody on Friday under preventive provisions intended to avert a breach of public peace. He was expected to appear before a Special Executive Magistrate, while the […]

VISHNU RAJA
RYO YAMADA
HITORI GOTOH
IKUYO KITA