News related to
breach

Artificial intelligence-powered surveillance is moving from corridors and playgrounds into some of the most sensitive spaces on school campuses, as administrators turn to new tools to curb vaping, bullying and violent incidents while grappling with rising concerns over student privacy, data security and psychological impact. School districts in the United States and parts of Europe have begun deploying AI-driven camera systems, audio sensors and environmental monitors that […]

UK authorities are investigating a sophisticated cyber intrusion into the country’s diplomatic systems after attackers penetrated networks at the Foreign, Commonwealth and Development Office, accessed sensitive material and triggered a sweeping security review across government. The breach, discovered in October 2025 during routine monitoring, has been linked by officials to a state-aligned group assessed to have connections to China, sharpening concerns over espionage risks amid strained geopolitical […]

Proton VPN has moved into third position in TechRadar’s global VPN rankings, overtaking ExpressVPN and marking a notable shift in a market where privacy assurances and corporate ethics are becoming decisive factors for users. The change places the Switzerland-based provider behind only NordVPN and Surfshark in one of the most closely watched consumer technology comparisons, signalling how competition among virtual private network services is increasingly shaped by […]

Bitcoin’s slide below the closely watched $86,000 threshold has unsettled digital-asset markets, breaking a price floor that traders had treated as a key line of defence since the sharp sell-off in October. The move has triggered renewed volatility across major tokens and prompted a reassessment of risk as investors weigh whether the decline reflects temporary dislocation or a deeper shift in market structure. The breach occurred amid […]

Two former employees of cybersecurity firms have pleaded guilty in a United States federal court to criminal charges after admitting they secretly carried out ransomware attacks against companies they were supposed to help protect, a case that has sent shockwaves through the cyber-security industry and reignited concerns about insider threats. Prosecutors said the defendants used their technical knowledge and access to professional tools to identify vulnerabilities in […]

Cisco has said that a sophisticated group of China-linked hackers is actively exploiting a previously unknown vulnerability to breach the networks of its customers, raising concerns across governments and large enterprises that rely on the company’s equipment for critical communications and data traffic. The company disclosed that the attackers have been using a zero-day flaw to gain unauthorised access to affected systems before patches were available, allowing […]

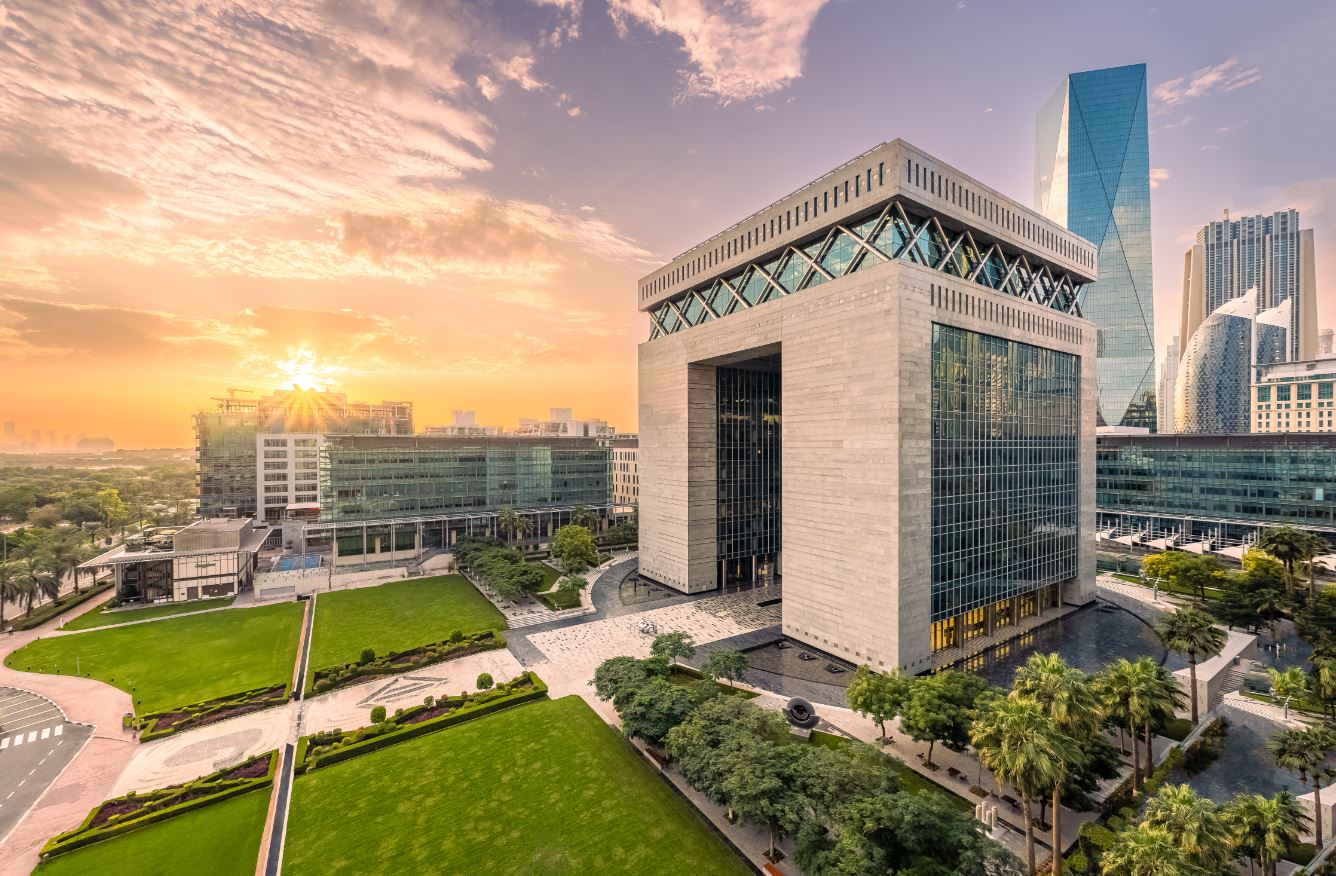
Dubai International Financial Centre has taken a further step in positioning Dubai as a key node in the global digital economy by strengthening its privacy governance framework and widening its engagement in cross-border trade initiatives, underscored by its admission as a Member of the Global Forum Assembly. The move signals growing international recognition of the DIFC’s data protection regime and its ambition to shape global standards at a time when data flows, digital services and regulatory trust have become central to economic competitiveness.

The DIFC confirmed its membership of the Global Forum Assembly, a multilateral platform that brings together governments, regulators, international organisations and private-sector stakeholders to advance cooperation on privacy, data protection and digital trust. Membership is extended to jurisdictions that demonstrate mature, enforceable frameworks aligned with international norms, placing the DIFC alongside established financial and digital centres that have made privacy governance a core component of their economic strategy.

Officials at the DIFC said the step reflects the centre’s long-term investment in building a regulatory environment that balances innovation with strong safeguards for personal data. The DIFC’s Data Protection Law, which operates independently from federal frameworks, is designed to mirror global best practices, including principles found in European and other advanced privacy regimes, while remaining tailored to the needs of financial services, technology firms and multinational businesses operating across borders.

The timing is notable as digital trade accelerates across financial services, fintech, artificial intelligence, cloud computing and professional services. Businesses increasingly assess jurisdictions not only on tax efficiency or infrastructure but also on the credibility of their data governance. For Dubai, positioning the DIFC as a trusted hub for data-driven commerce supports broader economic diversification goals and aligns with national ambitions to expand digital exports and attract high-value investment.

Participation in the Global Forum Assembly gives the DIFC a seat in discussions shaping the future of cross-border data flows, adequacy frameworks and interoperability between privacy regimes. These debates have intensified as countries seek to protect citizens’ data while avoiding regulatory fragmentation that can raise costs and deter innovation. By contributing to policy dialogue, the DIFC aims to influence standards that enable data to move securely between markets without undermining individual rights.

Regulatory specialists note that the DIFC’s framework has evolved steadily, with enforcement powers, clear obligations for data controllers and processors, and mechanisms for redress. This institutional depth has been a key factor in gaining international credibility. Businesses operating in the centre are required to comply with detailed rules on consent, lawful processing, breach notification and cross-border transfers, creating a predictable environment for global firms managing complex data operations.

The emphasis on inclusive cross-border trade also reflects a shift in how digital economy hubs define competitiveness. Rather than focusing solely on domestic regulation, leading centres are investing in compatibility with other regimes to ensure that companies can scale across regions. The DIFC has positioned its privacy framework as an enabler of such compatibility, supporting firms that serve clients in multiple jurisdictions while maintaining high standards of protection.

Technology policy analysts point out that privacy governance is increasingly intertwined with trust in emerging technologies such as artificial intelligence. Robust data protection regimes are seen as foundational to responsible AI development, particularly in financial services where algorithmic decision-making relies heavily on personal and transactional data. By reinforcing its privacy credentials, the DIFC strengthens its appeal to AI-driven firms seeking a stable regulatory base.

The move also has implications for regional competition. Financial centres across the Middle East and beyond are racing to attract digital businesses, often through regulatory innovation. The DIFC’s membership of the Global Forum Assembly distinguishes it within this landscape, signalling alignment with international norms rather than regulatory isolation. This approach may resonate with multinational firms that prioritise consistency across markets.

For policymakers, the development illustrates how sub-national jurisdictions can play an outsized role in global digital governance. Although operating within a broader national framework, the DIFC’s independent legal system and regulator allow it to engage directly with international bodies and contribute expertise drawn from its experience overseeing a diverse ecosystem of banks, asset managers, fintechs and technology companies.


Advertisements

Hackers have siphoned about $2.7 million worth of digital assets from old wallets linked to Aevo, a decentralised options and perpetuals exchange, underscoring persistent security risks tied to legacy infrastructure in the crypto market. The breach did not affect Aevo’s core trading systems or user funds held in active contracts, but it has revived scrutiny of how exchanges manage dormant or transitional wallets long after platform upgrades. […]

A proposal in the House of Lords to restrict the use of virtual private networks by under-16s has reignited debate over child online safety, digital privacy and the enforceability of age-based controls. The amendment, put forward during scrutiny of the government’s online safety framework, aims to prevent children from using VPNs to bypass age checks on social media, adult content platforms and other regulated online services. Supporters […]

European Union regulators have opened a fresh competition investigation into Google, examining whether the search engine is undermining publishers and content creators by failing to pay fairly for their material while setting conditions that could disadvantage those unwilling to share content for artificial intelligence training. The European Commission said the inquiry will focus on Google Search and YouTube, with particular attention on how content is used to […]

Australia has begun enforcing a landmark social media restriction aimed at limiting how platforms interact with users under 16, triggering debate among teenagers who question whether the policy addresses the realities of online life or simply shifts responsibility away from technology companies. The measures, introduced through updates to the Online Safety Act and reinforced by regulatory directives to major platforms, require companies such as Meta, TikTok, Snap […]

SINGAPORE – Media OutReach Newswire – 11 December 2025 – In a labour market reshaped by digitalisation and industry transitions, working adults in Singapore increasingly turn to short, skills-focused programmes to stay employable, switch roles, or move into growth sectors. The national SkillsFuture movement, administered by SkillsFuture Singapore (SSG), exists precisely to make such upskilling accessible, combining course subsidies, credit top-ups, and train-and-place pathways that prioritise employment […]

A coalition of six major video-game unions from across Western Europe has come together to condemn widespread layoffs, growing use of generative AI and persistent toxic workplace conditions across the industry. The group includes France’s STJV, the UK’s IWGB Game Workers, Spain’s CGT, Italy’s FIOM-CGIL, Germany’s ver. di, and Game Workers Unite Ireland. Their joint move signals one of the strongest cross-border union alliances the gaming sector […]

A breakthrough in neural engineering is prompting wide debate over how far humans should push the boundaries between biological thought and digital computation. The unveiling of an ultra-thin implant known as BISC, designed to stream neural activity in real time through a high-bandwidth wireless interface, offers a glimpse of a future where the movement of a limb, the perception of an object, or the intent behind a […]

By T N Ashok NEW DELHI: Russian President Vladimir Putin arrived in India Thursday evening for a two-day state visit that has become a diplomatic flashpoint, testing New Delhi’s ability to maintain strategic independence amid mounting pressure from Washington and European capitals. The arrival marks Putin’s first trip to India since the Ukraine war began […]

The article Putin’s India Visit: A Stress Test Of Strategic Autonomy Amid Global Pressure appeared first on Latest India news, analysis and reports on Newspack by India Press Agency).

The European Commission imposed a €120 million penalty on X, formerly known as Twitter, citing multiple violations of the Digital Services Act — the bloc’s landmark digital marketplace and content-governance regulation. The penalty covers three specific breaches: the platform’s so-called “blue check” verification system, insufficient transparency in advertisements, and failure to provide adequate public data access for researchers. Brussels flagged the blue-tick verification change under Elon Musk […]

Cybersecurity officials have issued a coordinated alert on a malware strain known as BRICKSTORM after identifying a wave of intrusions targeting VMware ESXi hosts and Windows environments across several sectors. The advisory, released by national defence and cyber agencies in the United States and Canada, underscores mounting concern over activity linked to operators aligned with the People’s Republic of China, whose campaigns have been tracked exploiting virtualisation […]

Geopolitical and macroeconomic uncertainty, tariffs, and cyber risks pose liability challenges for the boards of corporations of all sizes. The increasing number of insolvencies around the globe is becoming a major issue for executives. Claims severity and settlement costs are increasing, especially in the US, while the commercial financial lines insurance market remains highly dynamic. SINGAPORE – Media OutReach Newswire – 3 December 2025 – Around the […]

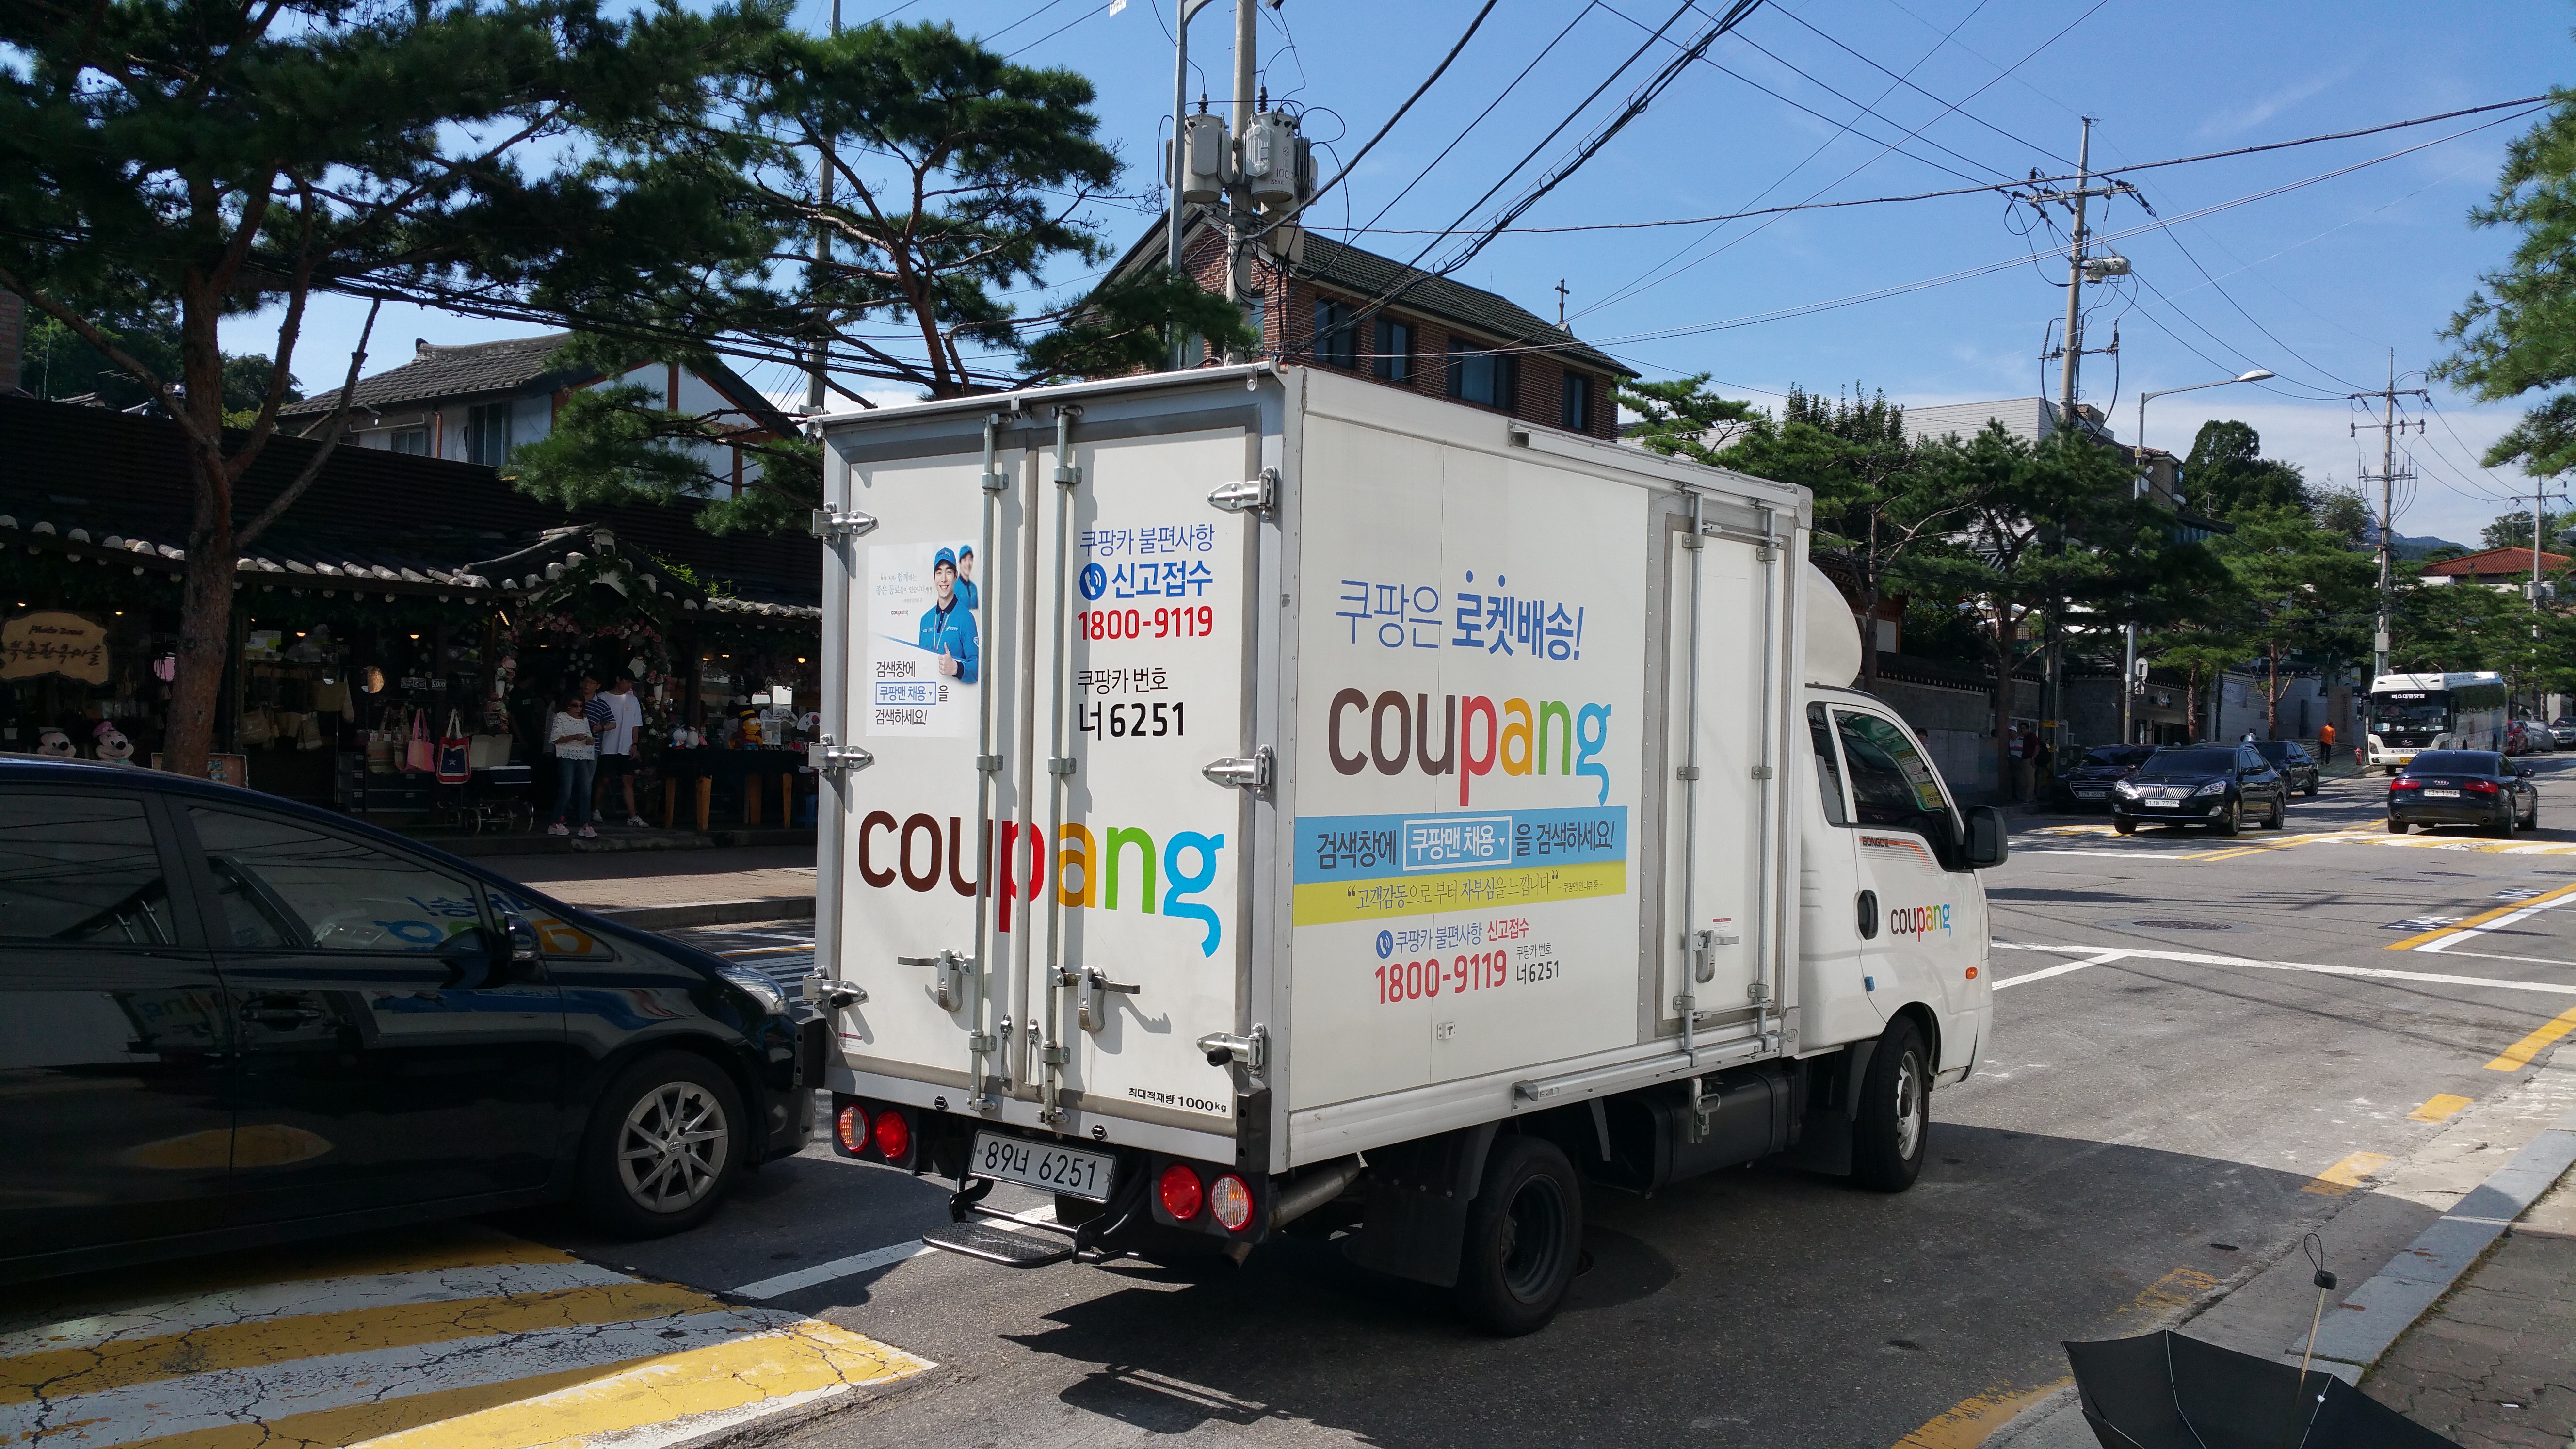
Coupang has admitted that unauthorised access exposed the personal information of 33.7 million customer accounts, marking the worst data leak in South Korean history. The leaked data includes names, email addresses, phone numbers, delivery addresses and some order histories, while payment credentials and login details are said to remain secure. The breach first began on 24 June and remained undetected until 18 November, when the company discovered suspicious access affecting about 4,500 accounts — a figure swiftly revised upward as investigators uncovered the full scale of the leak.

Police investigators are analysing server logs and have identified the IP address used in the attack, triggering efforts to trace the suspect. Authorities have not confirmed the nationality of the person under suspicion, though local media have pointed to a former employee of Chinese origin. Coupang filed a formal complaint on 25 November under legislation covering unauthorised access and data theft, and the probe has since turned into a full-fledged criminal investigation.

In response to mounting public concern, the Ministry of Science and ICT convened an emergency meeting to examine whether Coupang violated national data-protection laws. The government has warned that the exposed information — though not financial in nature — could easily be used for phishing, identity theft or other scams, particularly given the extent of the leak and the volume of personal data involved.

Coupang says it blocked the breach route as soon as the intrusion was confirmed and has engaged external cybersecurity experts to strengthen internal monitoring. The firm also issued a public apology through its chief executive, pledging full cooperation with law enforcement and regulatory bodies.

A new study led by researchers at Stanford demonstrates that social media polarisation can be eased through modest adjustments to content ranking rather than content removal or heavy moderation. The team developed a browser-based tool that reorders users’ feeds on X to push down posts containing extreme partisan hostility, calls for political violence or antidemocratic rhetoric. When applied in a field experiment during the 2024 US election, […]

A sophisticated attack on the liquidity pool of yETH — the liquid staking token index offered by Yearn Finance — drained millions of dollars in assets when an attacker minted an effectively unlimited amount of yETH and exchanged the bogus tokens for real ETH and other liquid-staking assets. Blockchain data indicate close to 1,000 ETH — roughly US$ 3 million — was swiftly moved through mixing service Tornado Cash in a single transaction, while the wider financial impact may scale significantly higher.

The exploit hinged on a critical flaw in the smart contract underpinning yETH’s “stableswap pool,” which permitted the creation of an unbounded number of yETH tokens. Immediately after minting, the attacker used those tokens to withdraw real ETH and other assets from liquidity pools tied to yETH, rapidly draining the pool. Multiple helper contracts deployed for the attack self-destructed soon after, making tracing efforts challenging.

Shortly after the event, Yearn Finance confirmed the breach and clarified that its core vault offerings — including V2 and V3 vaults — remain unaffected, noting the issue appears isolated to the legacy yETH pool. That distinction may have prevented a broader protocol-wide collapse, although internal assessments are ongoing to fully understand the exploit’s scope.

Further on-chain analysis by security firms suggests total losses could approach US$ 9 million, once damage to auxiliary pools — including a yETH–WETH pool — are accounted for. Nearly US$ 3 million in stolen ETH has already been funneled through Tornado Cash, rendering recovery difficult as funds are mixed and dispersed.

Market reaction was immediate: major cryptocurrencies including Bitcoin and Ether slid sharply during Asian trading hours, signalling heightened investor anxiety about DeFi security vulnerabilities. The incident has reignited scrutiny over legacy smart-contract code within decentralised finance platforms and underscored persistent risks associated with innovation outpacing security audits.

OpenAI disclosed a data breach involving its analytics provider Mixpanel, confirming that a security lapse allowed unauthorised access to certain API user details but did not compromise ChatGPT message data or model-generated content. The company informed affected developers that the incident, traced to November 2025, exposed names, email addresses and limited account-related metadata, prompting a broader review of third-party integrations across its platform. OpenAI stated that the […]

South Korea’s largest cryptocurrency exchange saw roughly $36 million drained from its hot wallet linked to the Solana network in what officials describe as an “abnormal withdrawal”. The breach triggered an immediate freeze on deposits and withdrawals. The operator, Dunamu, moved remaining assets into cold storage and pledged to fully reimburse all affected users.

Authorities in Seoul identified the hacking group Lazarus Group — long associated with previous crypto thefts — as the prime suspect behind the intrusion. Investigators plan an on-site inspection of Upbit’s systems to determine how attackers bypassed security protocols.

The tokens siphoned off included SOL alongside several Solana-ecosystem assets. Observers noted that the attack bears striking resemblance to a prior Upbit breach in 2019 — when 342,000 ETH disappeared under circumstances later attributed to Lazarus and associated groups.

Security firms monitoring on-chain flows report that the speed and pattern of withdrawals mirror those from Lazarus-linked incidents. Analysts warn that the hack underscores persistent vulnerabilities when hot wallets — the always-online accounts exchanges use for frequent transactions — remain exposed to governance failures or credential compromises.

The timing of the incident coincided with a corporate milestone for Dunamu: the day saw the public announcement of a planned merger with technology firm Naver. Some security experts speculate that the attackers might have deliberately chosen the moment to maximise impact on market confidence and regulatory attention.

Upbit’s management emphasised that user assets held in cold storage remained untouched. The company began working immediately with token issuers and blockchain-analytics firms to freeze traceable stolen funds. Officials involved in the probe noted the laundering techniques — rapid mixing of tokens across multiple wallets and networks — reflect a refined modus operandi honed over several high-profile attacks.

Cyber-security firms Kaspersky and VDC Research have estimated that global manufacturing organisations could incur losses exceeding US$18 billion in the first three quarters of 2025 due to ransomware attacks disabling production-line operations. According to their joint analysis, based on data from the Kaspersky Security Network, the average incident leads to around 13 days of operational disruption, with labour costs alone accounting for billions of dollars. The losses […]

VISHNU RAJA
RYO YAMADA
HITORI GOTOH
IKUYO KITA