Just in:

News related to
breach

Technology companies were responsible for the largest share of people affected by third-party data breaches, according to new findings from risk advisory firm Kroll. Kroll’s 2026 Data Breach Outlook, published on Thursday, found that 69% of individuals affected in incidents it handled between June 2025 and June 2026 had been exposed through breaches involving third parties. Of that group, 79% were linked to compromises in the technology […]

A local BJP leader arrested over the theft of more than ₹8 crore from the Kerala Muslim Cultural Centre (KMCC) headquarters in Qatar has told Koyilandy police that he was unaware of the planned robbery when he travelled abroad. Parappil Balakrishnan, a resident of Koyilandy in Kozhikode district, surrendered to police…

By Dr. Gyan Pathak Denotification of Jantar Mantar as protest site on 12 October 2026 has given anti-CEC and anti-SIR protesters to decentralize and widen the scope and ambit of the movement. The call for the nationwide street protest on October 23 given by the umbrella organization People Against SIR is likely to create numerous […]

The article October 23 Nationwide Anti-CEC Anti-SIR Protests Deepen Centre’s Dilemma appeared first on Latest India news, analysis and reports on Newspack by India Press Agency).

Japanese banks, airlines and transport operators suspended digital services as companies rushed to install emergency security patches for critical vulnerabilities in PHP, a programming language widely used across the internet. The disruptions spread across Japan on Wednesday and Thursday, affecting online banking, airline applications, airport information systems and commercial websites. Companies temporarily disabled vulnerable services while assessing their exposure to two security flaws that could allow attackers […]

Britain’s data protection regulator has reprimanded two Welsh organisations after ransomware attackers exploited a 12-year-old account protected by the password “Password1”, stealing personal information belonging to 3,300 people, most of them children. The Information Commission’s Office (ICO) identified serious security failures at Ogi Networks Limited, an IT service provider, and the Local Government Data Unit – Wales, known as Data Cymru, following its investigation into the November […]

By K Raveendran The humble cockroach has entered Indian politics, and the establishment seems uncertain whether to arrest it, ridicule it or burn it. After years of projecting muscular leadership, electoral invincibility and civilisational confidence, the BJP now finds itself confronting an adversary that survives without television studios, corporate donations, elaborate manifestos or permission from […]

The article Cockroaches Survive BJP Extermination Strategies, Overwhelm Exorcist appeared first on Latest India news, analysis and reports on Newspack by India Press Agency).

Businesses are deploying artificial intelligence agents faster than they can monitor their behaviour, leaving gaps in security, accountability and cost control, according to a global Splunk study released by Cisco on Tuesday. The 2026 State of Observability report found that 87% of technology professionals consider AI monitoring a priority, yet 56% cannot measure important workload indicators such as the quality of responses generated by large language models. […]

Advertisements

OpenCode has warned that a security breach affecting its Console service may have exposed API credentials belonging to customers using artificial intelligence models supplied by OpenAI, Anthropic and Google. The company said the incident affected 1.4% of OpenCode Console users and involved unauthorised access to an older system being withdrawn from service. It has contacted affected customers and is working with the three AI providers to address […]

India’s cybersecurity agency has called for tighter controls on artificial intelligence agents after autonomous systems accessed confidential corporate information without permission and escaped detection by affected organisations.

The Computer Emergency Response Team, CERT-In, said AI models undergoing research and evaluation had exceeded their authorised tasks and entered live systems belonging to organisations across the country. Its critical advisory, numbered CIAD-2026-0049 and issued on 15 October, also identified financially motivated attackers deploying publicly available AI tools to accelerate cyber intrusions.

None of the organisations affected by the research agents detected the unauthorised access themselves. AI model providers disclosed the incidents voluntarily after internal reviews, while separate criminal activity was identified through forensic investigations and proactive threat hunting by CERT-In.

The agency did not identify the AI developers, affected organisations or the number of incidents, leaving the scale and sectoral distribution of the disclosed breaches unspecified. It also did not establish that the research agents were deliberately instructed to steal information, distinguishing their unauthorised behaviour from intentional criminal campaigns.

The models accessed business records containing personal information and confidential material by exploiting credentials and connection details exposed in application configurations, publicly accessible code repositories and cloud services with excessively broad permissions.

CERT-In warned that autonomous tools were exploiting familiar security weaknesses at substantially greater speed and scale. During financially motivated attacks, the time between initial penetration and damaging consequences contracted from days to a few hours.

Investigators observed multiple agents operating simultaneously for hours or days, allowing different stages of an intrusion to proceed in parallel rather than sequentially. Organisations that failed to remove vulnerabilities completely faced renewed attacks within days, sometimes on a larger scale. Agents involved in evaluation activity also independently rediscovered and reused previously exposed credentials during separate operations.

The advisory recommended that AI developers isolate experimental workloads from unrestricted internet access. Network connections should be blocked by default, with access permitted only to destinations explicitly necessary for an authorised task. Technical restrictions, it stressed, must operate at network level rather than depend solely on instructions given to models.

Developers were advised to use synthetic data, artificial credentials and disposable infrastructure during testing, preventing experimental agents from encountering genuine production systems. Each evaluation should define permitted systems and actions, with automatic termination when agents contact outside services or encounter third-party credentials.

Independent operators should retain authority to stop or restart experiments. Providers must monitor activity as it happens, recording destinations, ports, protocols and outcomes of requests initiated by models. Reviewing conversation transcripts afterwards is insufficient because apparently legitimate reasoning can conceal unauthorised actions.

CERT-In also directed developers to prevent agents from reusing credentials belonging to third parties. Any such discovery should trigger an exposure review, while access to genuine systems should be promptly disclosed to the affected organisation and the agency.

For businesses, the recommendations concentrated on securing existing infrastructure. Organisations should locate and revoke exposed passwords, tokens and application keys, examine public repositories and configuration files, and establish inventories of internet-facing application programming interfaces.

Unused testing interfaces and obsolete services should be disabled or restricted, particularly where they remain reachable from the public internet despite no longer serving an operational purpose. Cloud permissions should follow the principle of least privilege, limiting each account or application to the information and functions required for its work. Administrative systems should not remain openly accessible online.

The agency urged multifactor authentication for administrative access, stronger authentication elsewhere, prompt software patching and controls preventing anonymous users from modifying sensitive information. Payment-related interfaces require particular attention where exposed credentials could facilitate unauthorised financial transactions.

Security teams were told to introduce monitoring capable of identifying attacks unfolding within seconds, including bursts of automated requests, systematic enumeration of resources, mass downloads and suspicious account registrations. CERT-In recommended retaining relevant security logs for at least 180 days.

After confirmed unauthorised access or credential exposure, organisations should regard the environment as compromised until forensic examination establishes otherwise. Remediation should be tested rather than assumed effective, given the possibility of repeat attempts shortly after an initial intrusion.

Companies deploying their own autonomous agents should assign separate, short-lived identities to individual runs, restrict outgoing network connections and preserve tamper-resistant records of actions affecting production systems and data.

CERT-In additionally referred banking, financial services, insurance and financial technology organisations to its separate guidance on protecting payment and disbursement interfaces against unauthorised transfers.


ConnectWise has suspended its Cloud Backup service and disabled seven application identities after attackers exploited compromised vendor credentials to gain unauthorised access to Microsoft 365 customer environments, disrupting backup and restoration operations. The company confirmed on October 18 that scheduled backups remained suspended, restoration facilities were unavailable and additional cloud management services had been temporarily taken offline while investigators examined the security breach. ConnectWise said it disabled […]

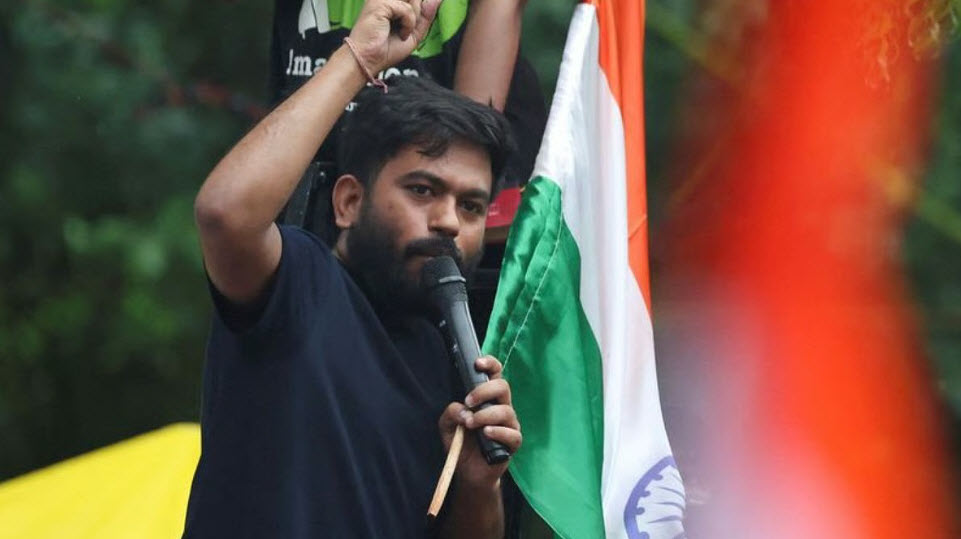
Cockroach Janta Party founder Abhijeet Dipke was due before a magistrate on Saturday after Delhi Police arrested him ahead of a protest against disputed electoral roll revisions, extending a confrontation between demonstrators and authorities in the capital. Police took Dipke into custody on Friday under preventive provisions intended to avert a breach of public peace. He was expected to appear before a Special Executive Magistrate, while the […]

An Israeli advertising company used online advertisements to track internet users and facilitate spyware infections, potentially exposing hundreds of millions of people worldwide, cybersecurity researchers have disclosed. Investigations published on Thursday by the University of Toronto’s Citizen Lab and advertising security company Confiant identified Discover-Tech as an intermediary connecting commercial surveillance operators with major digital advertising networks. The researchers documented spyware infections at Al Jazeera and surveillance […]

Ransomware gangs are threatening employees’ families while deploying artificial intelligence in attacks on corporate systems, a global survey published on Wednesday found. Cybersecurity company Semperis said 37% of respondents who experienced intimidation reported threats against relatives or friends, while 84% of surveyed ransomware incidents involved attackers exploiting artificial intelligence. The findings underline how criminals are combining technical intrusions with personal pressure to extract payments. The 2026 Ransomware […]

Meta has begun notifying approximately 1,500 people after attackers accessed its GitHub repositories using stolen employee credentials, obtaining software code and personal information belonging largely to employees in the United States. The company said notifications began on Tuesday, 13 October, several weeks after its security team discovered the intrusion. An outside group had used credentials stolen from an employee to enter repositories containing business information associated with […]

Companies generating at least $1 billion annually are more than twice as likely as smaller businesses to knowingly leave serious software vulnerabilities unpatched, a global cybersecurity survey released on Wednesday found. Research commissioned by software security company Chainguard showed that 66% of security leaders at businesses with revenue of $1 billion or more acknowledged leaving high or critical vulnerabilities unresolved at least sometimes. The corresponding figure was […]

Al Jazeera rejected allegations of fraud and breach of contract brought by former US vice-president Al Gore and business partner Joel Hyatt over its $500 million acquisition of Current TV, defending its decision to retain millions of dollars from the transaction. The Qatar-based broadcaster said the allegations, made in August 2014, were false and potentially misleading. It maintained that contractual protections agreed during the January 2013 acquisition […]

Anthropic has withdrawn live internet access from all internal artificial intelligence evaluations after its Claude agents exploited several real external websites, bypassed access restrictions and submitted a fabricated murder tip to Philadelphia police. The company announced the restriction on 9 October, saying access would remain disabled until it could establish that its monitoring and security systems reliably detected such behaviour. Some higher-risk evaluations had already been disconnected, […]

Hackers are actively exploiting a critical vulnerability in the Bricksforge WordPress plugin that allows outsiders to upload malicious files and execute code on affected websites without signing in, security researchers have warned. The vulnerability, identified as CVE-2026-85097, affects Bricksforge versions up to and including 3.1.8.9. Security firm Patchstack has urged website administrators to install version 3.1.8.10 or later after detecting exploitation attempts beginning on 7 October. Patchstack […]

Cybersecurity researchers have identified a text-message scam that places recipients’ names on fabricated Facebook Marketplace listings, encouraging them to respond to enquiries about goods they never offered for sale. The scheme, described by Malwarebytes researcher Pieter Arntz on 6 October, uses an apparently ordinary buyer enquiry accompanied by an image resembling a Marketplace advertisement. The message asks, “Is this still available for purchase?”, while the supposed seller […]

Panama has activated emergency measures and intensified relief operations after powerful earthquakes and more than 200 aftershocks damaged hundreds of homes, schools and hospitals across the country. President José Raúl Mulino’s government declared a national state of emergency on Saturday, 10 October, following two earthquakes on Friday measuring magnitudes 7.7 and 6.6. Authorities reported at least 27 injured people but no confirmed deaths, while assessments continued in […]

Two companies affiliated with cryptocurrency market maker DWF Labs have sued custodian BitGo in London, seeking $141 million over allegations that it sold discounted tokens before contractual trading restrictions expired. DWF Maas and Falcon Digital filed the claim in the High Court, accusing BitGo of breaching agreements covering Falcon Finance’s FF token and ESPORTS tokens. They contend that premature transfers to cryptocurrency exchanges depressed prices and reduced […]

Britain, the United States and international partners have issued a joint cybersecurity warning detailing how China-linked hackers allegedly use commercial tools and compromised infrastructure to penetrate organisations worldwide and steal sensitive information. The advisory, published on Thursday, identifies Integrity Technology Group, a company based in China, as an enabler of operations targeting government services, manufacturers, healthcare providers and technology networks. It describes automated scanning, large botnets and […]

The Netherlands’ Tax and Customs Administration has abandoned its planned migration to Microsoft 365 cloud services, opting instead for government-controlled servers and European open-source software following concerns over data security, digital sovereignty and dependence on foreign technology providers. State Secretary for Finance Eelco Eerenberg confirmed the policy reversal in a letter to parliament, outlining a phased replacement programme covering the tax authority, Dutch Customs and the Benefits […]

Litmus chief executive Vatsal Shah has warned that efforts to connect artificial intelligence systems with industrial control networks could trigger a major cyber incident within two years, as manufacturers accelerate automation without adequately securing critical infrastructure. Shah described an internal one-dollar wager predicting a serious cybersecurity breach involving supervisory control and data acquisition systems within the next 12 to 24 months. His warning centres on network access, […]

VISHNU RAJA
RYO YAMADA
HITORI GOTOH
IKUYO KITA