Just in:
Phancy Announces Business Performance for the Nine Months Ended September 30, 2026 // Promoting Common Human Development Through Exchanges and Mutual Learning Among Civilizations // Dubai Introduces SHARH, an AI-Powered Platform Helping Entrepreneurs Buy, Sell and Manage Businesses in the UAE // Oil futures rebound after Riyadh strikes and tanker alerts // Alibaba shares slip despite 53% cloud revenue growth // Workday targets Honeydew purchase to unify AI metrics // Yeebo Announces Interim Results for FY26/27 Revenue Increases by 45.5% to HK$806.7 Million Profit Attributable to Owners Surges 87.6% to HK$2,284.7 Million // Hackers exploit public notes to distribute NodeLinkRAT malware // AXS and PayerMax Advance Omnichannel Payment Acceptance for Merchants // Sui activates Hashi Bitcoin lending across partner network // Travel Insurance Was Built for the Few Who Claim. Ancileo’s Felt Coverage™ is for Everyone Else // Russia permits retail cryptocurrency purchases under regulated framework // NASA tests supersonic Mars rotors for heavier payloads // International Business Leaders Say Xi’s Speech Boosts Confidence in Asia-Pacific Cooperation // Women held for plot to rob pilgrims // PicCollage extends photo editing platform to web browsers // Coinbase targets 2027 launch amid state gambling lawsuits // Anthropic shares finish above offer price after Nasdaq debut // LittleLives, Little Lab and SEGi College Sign MOU to Explore Early Childhood Education Collaboration Across ASEAN // Thailand’s Most Iconic New Year’s Celebration Returns: ICONSIAM Unveils “Amazing Thailand Countdown 2027” //

News related to
cyber

Cyber literacy has become the leading global people risk as employers confront ransomware, AI-enabled fraud, technology skills gaps and fragile workforce readiness, Marsh’s 2026 People Risks survey has found. The report, based on views from 4,517 human resources and risk professionals across 26 markets and 12 industries, places inadequate cyber threat literacy at the top of the global risk list. Technology skills shortages, including cyber and artificial […]

A hardcoded API key embedded in ClickUp’s public website exposed 959 corporate and government email addresses and more than 3,000 internal feature flags for over a year, intensifying scrutiny of security controls at widely used software-as-a-service platforms. The exposure was tied to a production JavaScript bundle that loaded before authentication, allowing anyone inspecting the page source to extract a third-party SDK token and send an unauthenticated request […]

Vect 2.0 has emerged as a fast-evolving ransomware-as-a-service operation capable of striking Windows, Linux and VMware ESXi systems, raising concern among security teams responsible for hybrid corporate networks and virtualised infrastructure. The group’s latest tooling marks a shift from single-platform extortion campaigns towards attacks designed to spread across workstations, servers and hypervisors. That matters because ESXi environments often host multiple virtual machines on a single physical server, […]

Business-to-business marketing teams are entering 2026 with a sharper problem than ranking on search results pages: how to make their brands visible inside AI-generated answers that buyers increasingly use before visiting a supplier’s website. Mark Lydon, senior content marketing manager, has framed the shift as a move from search engine optimisation to answer engine optimisation, reflecting a wider change in how procurement teams, technology buyers and enterprise […]

Digital Dubai has released a whitepaper introducing the AI Integration Matrix Framework, a government-wide model designed to move artificial intelligence use from scattered pilots to a coordinated operating system across public entities. The framework marks a new stage in Dubai’s effort to embed advanced digital tools into public administration, with an emphasis on interoperability, secure data use, institutional readiness and measurable service improvements. It is aimed at […]

BlueNoroff has intensified its campaign against cryptocurrency executives by combining fake Zoom meetings, AI-generated video lures and fileless PowerShell malware in an intrusion that gave attackers access to a North American Web3 company for 66 days. The operation, first detected after an intrusion began on 23 January 2026, marks a sharper turn in North Korea-linked cyber activity against digital asset businesses. Instead of relying on crude phishing […]

Rival ransomware crews 0APT and KryBit have disrupted each other’s operations after leaking internal data, exposing an unusual cybercriminal feud that has given defenders a rare view into the infrastructure, tactics and credibility gaps behind emerging extortion groups. The confrontation began on 13 April 2026, when 0APT listed KryBit, Everest and RansomHouse as victims on its leak site. KryBit responded a day later by breaching 0APT’s infrastructure, […]

Advertisements

North Korean state-linked hackers have intensified attacks on cryptocurrency companies by combining fake video meetings, AI-generated identities and “ClickFix” infection tactics to compromise executives, founders and staff with access to wallets, exchanges and investment infrastructure. A large spear-phishing operation attributed with high confidence to BlueNoroff, the financially motivated arm of the Lazarus Group, targeted a North American Web3 company through a manipulated calendar invitation that led to […]

Security researchers have identified a 2005-era malware framework that appears to have targeted high-precision engineering software, raising new questions about covert attempts to disrupt Iran’s nuclear programme before Stuxnet became the defining case of cyber sabotage. The malware, tracked as Fast16, was analysed by SentinelOne researchers Vitaly Kamluk and Juan Andrés Guerrero-Saade, who found that its core components pre-date the earliest known Stuxnet operations by at least […]

Retail and hospitality companies are facing a widening extortion campaign by BlackFile, a financially motivated hacking group using voice calls, fake helpdesk scripts and spoofed caller identities to steal credentials and force ransom negotiations. The group has been linked to attacks that began surfacing in January 2026, with sustained targeting of customer-facing businesses from February. Its activity has been tracked under several names, including CL-CRI-1116, UNC6671 and […]

Fake software downloads promoted through YouTube are being used to infect corporate employees with Vidar, an information-stealing malware that harvests passwords, browser data, session cookies and cryptocurrency wallet files before stolen credentials are traded through Russian-language cybercrime markets. The campaign shows how threat actors are shifting from noisy phishing emails to search-driven lures that exploit ordinary workplace behaviour. Employees looking for software tutorials, installers or utilities on […]

Cybercriminals are exploiting tax-season anxiety by circulating fake Income Tax Department notices that push taxpayers and companies towards malware-laden downloads disguised as assessment orders and compliance documents. The campaign uses official-looking emails and cloned tax portals to make recipients believe they are facing scrutiny over alleged violations, including concealment of income or inaccurate filings. Victims are directed to external websites that imitate government communication, where buttons labelled […]

A targeted malware campaign aimed at Pakistan’s government-linked security infrastructure has exposed how threat actors are combining social engineering, obfuscated code and trusted online services to evade conventional cyber defences. The attack was directed at employees of the Punjab Safe Cities Authority and PPIC3, using a spear-phishing email that impersonated an internal consultant and referred to the Safe Jail Project, a theme designed to appear relevant to […]

By Nantoo Banerjee Only six months in power, Japan’s first female prime minister, Sanae Takaichi, has emerged as the world’s most powerful woman reshaping the country’s domestic social and economic policies and international relations, taking a hard line on China. Takaichi has taken a firm stance on China suggesting that a “Taiwan contingency is a […]

The article Japan’s Pro-India Takaichi Is The World’s Most Powerful Lady appeared first on Latest India news, analysis and reports on Newspack by India Press Agency).

Anthropic’s Claude Desktop application for macOS is facing scrutiny after a cybersecurity researcher reported that the app installs a Native Messaging bridge into multiple Chromium-based browsers without a clear consent prompt, widening concern over how AI desktop agents gain access to local systems and browser sessions. Privacy researcher Alexander Hanff published his findings on 18 April 2026 after identifying a manifest file named com. anthropic. claudebrowserextension. json […]

OpenAI has opened a GPT-5.5 Bio Bug Bounty programme that invites selected researchers to test whether the company’s latest model can be pushed past safeguards designed to block dangerous biological guidance. The initiative offers a reward of up to $25,000 for the first verified “universal jailbreak” capable of defeating a five-question biosafety challenge from a clean chat without triggering moderation. The model in scope is GPT-5.5 in […]

Arabian Post Staff -Dubai Gulf Bank has renewed its long-term strategic collaboration with Mastercard, strengthening a payments alliance aimed at expanding digital banking services, improving transaction security and responding to changing customer behaviour across Kuwait’s financial sector. The renewed agreement gives Gulf Bank continued access to Mastercard’s payment technologies, digital solutions and global expertise, with a focus on contactless payments, mobile wallet services, card security, customer convenience […]

Hackers have turned a critical React Server Components flaw into a structured exploitation operation, using Telegram bots, automated scanners and AI-assisted tooling to track more than 900 confirmed compromises across internet-facing applications. The campaign centres on React2Shell, tracked as CVE-2025-55182, a maximum-severity remote code execution vulnerability disclosed in December 2025. The flaw affects React 19.0, 19.1.0, 19.1.1 and 19.2.0 through packages including react-server-dom-webpack, react-server-dom-parcel and react-server-dom-turbopack, and […]

Arabian Post Staff -Dubai   UAE authorities have launched an ambitious public-sector transformation programme to move half of government sectors, services and operations onto agentic artificial intelligence within two years, marking a major shift from digital service delivery towards autonomous government systems. The initiative was announced by Sheikh Mohammed bin Rashid Al Maktoum, Vice President and Prime Minister of the UAE and Ruler of Dubai, under the […]

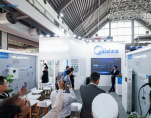
LAHORE, PAKISTAN – Media OutReach Newswire – 24 April 2026 – Midea Hiconics is making a major push into the Pakistani market this week at Solar Pakistan 2026. From Booth A-3-8, the energy division of Midea Group is showing off its latest hardware and has just signed a key distribution deal to get its products into more homes and businesses across the country.

Midea Hiconics Teams Up with MIA Group to Bring New Solar Tech to Pakistan

Hardware Built for Local Conditions

The company isn’t just showing off standard gear; they’ve brought systems specifically designed to handle the challenges of the local energy landscape.

  • PowerX1 Hybrid Inverters: Intelligent energy management, seamlessly switching between solar, battery, and grid for stable, uninterrupted power. Supports multi-source integration and rapid power transition.
  • Powerinfi All-in-one ESS: ISO 13849 PL-d and IEC 62443 certified for functional safety and cybersecurity. Features a multi-layer battery safety system within a compact design.
  • Advanced Solar & System Protection: Incorporates N-type HOT3.0 solar cell technology for enhanced low-light performance. The system boasts an IP66 rating for superior dust and water resistance.

A New Partnership with MIA Group

The big news from the show floor is the new Annual Channel Distribution Strategic Partnership with MIA Group. MIA Group is already a household name in Pakistan for HVAC and energy, and this deal means they’ll be the main bridge for Midea Hiconics’ tech to reach the local market.

“We’re excited to get to work with MIA Group,” a Midea Hiconics spokesperson said. “They have the reach and the local knowledge we need. By putting our hardware in their hands, we’re making it much easier for people here to switch to reliable, clean energy without the usual headaches.”

Media Contact:
Midea Hiconics Press Office
Website: https://www.hiconics-global.com/
Location: Solar Pakistan 2026, Booth A-3-8
Hashtag: #MideaHiconics

The issuer is solely responsible for the content of this announcement.

About Midea Hiconics

Midea Hiconics (SHE: 300048) has been around since 2003 and joined the Midea Group in 2020. They focus on green energy, home storage, and industrial tech, building smart tools that help people take control of their own power.

Check out https://www.hiconics-global.com/ for more info.

Japan has set up a financial-sector task force to assess risks from advanced artificial intelligence systems capable of discovering software flaws at a speed that could outpace existing cyber defences, deepening official concern over the resilience of banks, exchanges and payment infrastructure.

The move follows high-level talks involving the Financial Services Agency, the Bank of Japan, national cyber security officials, Mitsubishi UFJ Financial Group, Sumitomo Mitsui Financial Group, Mizuho Financial Group and Japan Exchange Group. The focus is Anthropic’s Mythos, a powerful AI model developed for defensive cyber security work but now regarded by regulators as a potential systemic risk if similar capabilities reach hostile actors.

Finance Minister Satsuki Katayama has framed the issue as an urgent challenge for core financial institutions, warning that Japan’s highly connected financial system could face cascading disruption if attackers used AI to identify and exploit weaknesses before institutions could repair them. No breach linked to Mythos has been reported, but officials are pressing banks to examine incident response plans, software exposure, vendor dependencies and market-continuity arrangements.

Japan tightens bank defences over Mythos as regulators confront a new cyber security problem: an AI tool built to strengthen software security may also demonstrate how fast the balance between defenders and attackers is shifting. Anthropic has said its Mythos Preview found thousands of high-severity vulnerabilities, including flaws affecting every major operating system and web browser. The company has placed the model under restricted access through Project Glasswing, an effort to use frontier AI for defensive discovery before equivalent capabilities spread more widely.

Security specialists see the financial sector as particularly exposed because banks rely on layered infrastructure that includes legacy systems, cloud services, trading platforms, third-party vendors and customer-facing applications. A vulnerability in one component may not remain isolated. Settlement systems, payment networks and securities markets depend on trust, synchronised data and rapid processing, leaving little tolerance for prolonged outages or uncertainty.

Japan’s top lenders have spent heavily on cyber resilience after a series of global incidents involving ransomware, software supply-chain attacks and attacks on critical infrastructure. Yet regulators remain concerned that AI-enabled vulnerability discovery could compress the time between flaw identification and exploitation. Traditional patch cycles often take days or weeks, while advanced models may help attackers generate working exploit paths far faster.

The task force is expected to coordinate technical assessments, information sharing and emergency procedures across the financial sector. Officials are also likely to examine how institutions verify third-party software, monitor anomalous activity and isolate critical operations during a cyber event. For exchanges and clearing systems, the priority will be maintaining orderly trading and settlement even if parts of the technology stack come under pressure.

The concern extends beyond Japan. Regulators in Asia, Europe and the United States have been urging banks to review their cyber controls as AI systems become more capable of code analysis, vulnerability chaining and automated exploitation. The issue has moved from a narrow technology debate into the domain of financial stability, because a successful attack on a major bank or exchange could quickly affect liquidity, confidence and cross-border transactions.

Anthropic has presented Mythos as a controlled defensive tool rather than a public product. The company says the model is intended to help responsible institutions find and fix vulnerabilities before they are misused. That defence has not removed policy concerns. The same capability that enables security teams to uncover hidden bugs can also lower the barrier for sophisticated offensive activity if access controls fail or comparable models emerge elsewhere.

Japan’s response reflects a broader shift in cyber regulation. Authorities are moving away from treating cyber security as a compliance checklist and towards stress-testing how institutions would cope with fast-moving, AI-assisted threats. Banks may face pressure to shorten patching timelines, improve software inventories and strengthen board-level oversight of technology risk.

For Japan, the issue also intersects with its ambition to modernise finance while promoting digital innovation. The country is expanding fintech services, digital payments and AI adoption across corporate operations, but regulators are signalling that innovation must be matched by stronger safeguards. Financial institutions are being asked to prepare for a threat environment in which attackers may use tools that can scan, reason and adapt at machine speed.

The immediate test for the task force will be whether it can turn concern into operational readiness. That means clear reporting channels, shared technical indicators, realistic crisis drills and faster coordination between banks, regulators, exchanges and cyber agencies. Japan’s financial authorities are seeking to prevent an AI-driven security breakthrough from becoming a market-disrupting event.


Cybersecurity teams running local artificial intelligence models are facing a high-risk exposure after a flaw in Ollama’s model-processing system was found to allow attackers to extract sensitive server memory through a malicious model file. Tracked as CVE-2026-5757, the vulnerability affects the model quantisation engine used by Ollama, an open-source platform widely adopted by developers and enterprises to run large language models on personal computers, workstations and servers. […]

Cyber-attacks on higher and further education institutions jumped 63 per cent over a year, exposing universities and colleges to a sharper wave of ransomware, data theft, hacktivism and state-linked intrusion as digital learning systems become central to academic life. The findings point to 425 recorded incidents across 67 countries in the latest 12-month assessment period, compared with 260 in the preceding year. The rise reflects not only […]

Google Cloud is placing general-purpose Gemini models at the centre of its cybersecurity strategy, betting that broad frontier AI systems paired with specialised agents will outperform narrow models built only for security tasks. The approach, articulated by Francis deSouza, Google Cloud’s chief operating officer and president of security products, signals a deliberate shift in how the company wants enterprises to defend themselves in an era of faster […]

VISHNU RAJA
RYO YAMADA
HITORI GOTOH
IKUYO KITA