News related to
cyber

The 2025 “FOMO at Work” survey by cybersecurity firm Acronis reveals that female technology professionals continue to perceive far fewer paths to leadership than their male peers, flagging persistent barriers despite widespread talk of inclusion and equality. The survey of more than 650 IT professionals across eight countries shows that only 60 per cent of women believe men and women enjoy equal access to career development opportunities […]

By K Raveendran An evolving convergence of political intent and economic pragmatism is giving fresh momentum to the India–Russia relationship, placing the forthcoming summit in New Delhi as a significant moment in a partnership that has already weathered decades of geopolitical shifts. The visit of President Vladimir Putin, framed within the terminology of a ‘Special […]

The article Delhi Summit To See A New Strategic Reset In India-Russia Partnership appeared first on Latest India news, analysis and reports on Newspack by India Press Agency).

OpenAI disclosed a data breach involving its analytics provider Mixpanel, confirming that a security lapse allowed unauthorised access to certain API user details but did not compromise ChatGPT message data or model-generated content. The company informed affected developers that the incident, traced to November 2025, exposed names, email addresses and limited account-related metadata, prompting a broader review of third-party integrations across its platform. OpenAI stated that the […]

HONG KONG SAR – Media OutReach Newswire – 28 November 2025 – Trend Micro Incorporated (TYO: 4704; TSE: 4704), a global cybersecurity leader, today released its annual Security Predictions Report for 2026, warning that the coming year will mark the true industrialization of cybercrime. Artificial intelligence (AI) and automation are now enabling threat actors to run entire campaigns autonomously, from reconnaissance to extortion, creating unprecedented speed, scale, […]

Weak cybersecurity strategies leave businesses exposed Businesses must prioritise strengthening leadership technology capabilities AI challenge is to balance efficiency gains and preserve human expertise KUALA LUMPUR, MALAYSIA – Media OutReach Newswire – 27 November 2025 – Malaysian businesses are rapidly adopting AI and data analytics, but weak cybersecurity strategies are leaving them exposed to growing digital threats, according to CPA Australia’s latest Business Technology Survey. While 87 […]

85% of businesses from the region indicate they plan to participate in the festive shopping period Almost 75% of consumers surveyed across these same markets intend to be active shoppers Consumer trust remains a challenge, however, as only about half of the region’s shoppers trust offers presented —underscoring the need for transparency and reliable delivery SINGAPORE – Media OutReach Newswire – 26 November 2025 – Black Friday […]

Banks and insurers across South Africa are being confronted with a shifting regulatory landscape as the Financial Sector Conduct Authority and the South African Reserve Bank, through its Prudential Authority, move to formalise oversight of artificial intelligence across the financial sector. Their inaugural report on the topic reveals a growing, though still tentative, embrace of AI — and flags significant risks around data governance, transparency, and systemic […]

Advertisements

Cyber-security firms Kaspersky and VDC Research have estimated that global manufacturing organisations could incur losses exceeding US$18 billion in the first three quarters of 2025 due to ransomware attacks disabling production-line operations. According to their joint analysis, based on data from the Kaspersky Security Network, the average incident leads to around 13 days of operational disruption, with labour costs alone accounting for billions of dollars. The losses […]

Organizations are deploying artificial-intelligence-driven defences to counter increasingly sophisticated cyber threats as attackers harness the same technology to mount agile attacks. Leaders at major cybersecurity firms say the conflict between defenders and adversaries has entered a new phase, where speed, adaptability and automation are critical. The security firm Palo Alto Networks announced upgraded platforms designed to protect cloud assets and AI-based applications, citing the need to monitor […]

Cloud-software giant Salesforce has announced that it is investigating unauthorised activity involving applications published by vendor Gainsight, which may have enabled access to customer data through the Salesforce platform. The firm said it revoked all active access and refresh tokens related to the Gainsight apps and temporarily removed those applications from its marketplace. It emphasised this incident does not stem from a vulnerability in the Salesforce core […]

A collaboration between the Technology Innovation Institute and Space42 will deliver the first space-to-ground quantum-communication network in the United Arab Emirates, signalling a significant step in national cyber-security strategy. The partnership, unveiled at the Dubai Airshow, brings together TII’s advanced research into Quantum Key Distribution and Space42’s satellite infrastructure to form a sovereign system capable of ultra-secure data transfer between orbiting platforms and terrestrial stations. TII and […]

Security forces in Myanmar’s border region with Thailand have confiscated roughly 10,000 mobile phones and associated equipment as part of a wide-ranging operation against online fraud networks, the country’s military government announced. The action unfolded in the Myawaddy township of Kayin State, where an internet scam hub known as KK Park was raided, and approximately 346 foreign nationals detained during the sweep. The military accused the ethnic […]

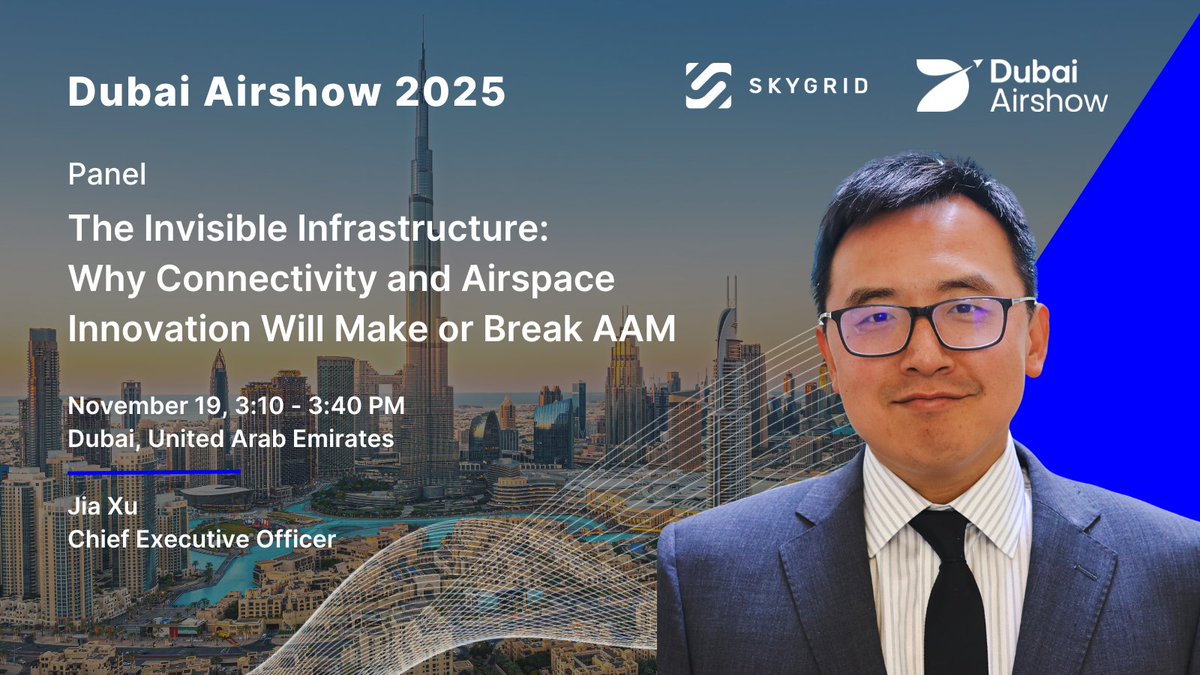
A pact between SkyGrid and High Lander has been signed at the Dubai Airshow 2025 to construct a framework for advanced air-mobility operations in the United Arab Emirates, focusing on integrating crewed and uncrewed aerial vehicles. The memorandum of understanding calls for development of airspace management ecosystems, digital operations for electric vertical take-off and landing aircraft and cargo drones, vertiport planning and cybersecurity protocols. SkyGrid, headquartered in Austin, Texas, acts as a third-party service provider for advanced air mobility operations, while High Lander offers unmanned traffic-management and drone-fleet-management solutions. The deal is part of the UAE’s ambition to position Abu Dhabi as a hub for next-generation aviation services.

Under the agreement the firms will jointly assess “Advanced Air Mobility Supporting Operational Environments” to develop technology road-maps and regulatory frameworks that facilitate scalable AAM operations. The collaboration targets areas including airspace integration, enabling vertiport infrastructure, securing digital operations and ensuring safe coexistence of crewed and uncrewed aircraft. SkyGrid chief executive Jia Xu said the alliance “represents a significant milestone in shaping the digital foundation of Advanced Air Mobility in the UAE and across the Middle East”. High Lander’s chief executive Alon Abelson commented that the environment in the UAE, supported by major aerospace players, constitutes “the perfect environment to demonstrate how automation, data-driven management and cross-industry collaboration can transform the future of air mobility”.

Analysis of this partnership places it amid a broader global push for uncrewed traffic-management systems and urban or regional air-mobility networks. Industry research shows that UTM ecosystems are considered vital for the safe scaling of commercial beyond-visual-line-of-sight drone operations. A 2024 readiness index issued by the Global UTM Association named both companies among participants in task forces shaping digital airspace adoption worldwide. That makes this UAE-based partnership a concrete step from theoretical planning to operational readiness.

The UAE’s Economic Vision 2030 describes diversification into technology, aerospace and transport as key pillars. The SkyGrid–High Lander partnership explicitly links with these goals, signalling industry-scale intentions rather than pilot programmes alone. By creating a unified operational blueprint, regulators and operators in the Gulf region may be asked to adapt their air-space classification, licensing and infrastructure regimes. Implementation will still depend on national aviation regulator approvals, air-traffic-management integrations, and standards alignment with international frameworks.

Despite the ambition, challenges remain. Data-sharing protocols across crewed and uncrewed systems must meet stringent safety and cybersecurity standards. Vertiport infrastructure—dedicated landing and take-off sites for eVTOL vehicles—is still nascent globally and will require investment and spatial planning, especially in congested urban zones. Moreover, global certification regimes for eVTOLs and unmanned systems are evolving; regulatory uncertainty may slow deployment. Analysts caution that while the Gulf region offers less airspace congestion than some metropolitan centres, integration of new aircraft types must still ensure separation from traditional air-traffic flows.

A new cyber-innovation centre has been unveiled to tackle evolving digital threats with advanced technology. The Vyuha Labs – Cyber Innovation Hub, launched through a partnership between International Institute of Information Technology, Hyderabad and the Telangana Cyber Security Bureau, will bring together academia, industry and law-enforcement to co-develop deep-tech tools aimed at strengthening cyber-security infrastructure. The facility spans more than 3,000 sq ft and is equipped with specialist infrastructure to prototype solutions for crime analytics, fraud detection and forensic processing.

The core mission of the hub is to convert early-stage research into deployable products that serve policing and digital safety needs. IIIT-H Director Prof Sandeep Shukla noted that simply publishing academic papers is not sufficient; the institution aims to hand over viable technologies to start-ups or third-party companies for implementation and scaling. TGCSB Director Shikha Goel emphasised that innovation-led solutions are the only effective route to stay ahead of threat actors, citing a decline in cyber-crime incidents within Telangana even as national levels have surged.

One of the flagship initiatives within the hub is an automatic processing system for distress-call data gathered via the 1930 helpline. Leveraging IIIT-H’s language-technology centre, the system converts voice calls into written transcripts, applies machine-learning algorithms to detect patterns and flags hotspots of criminal activity—shifting the approach from reactive logging to proactive intelligence generation. Another major effort focuses on financial-fraud analytics: mining citizen-complaint and transaction data to track investment-scam and cryptocurrency-fraud trends and to evaluate policing interventions for effectiveness. A third component addresses computer-vision based forensic tracking through camera-feed analysis and automated suspect-movement detection, part of a longer-term plan to enhance digital-evidence workflows.

The strategic positioning of Vyuha Labs reflects a broader shift in how cyber-crime is being addressed. Rather than centralised national agencies alone, regional hubs are emerging that bring together local police forces, technical research institutes and private-sector partners for agile innovation and deployment. TGCSB’s claim of an 11 per cent fall in cyber-crime within Telangana, even as 37 per cent growth was recorded nationally, is cited as evidence of the model’s early promise. The facility is housed within IIIT-H’s Cyber Manthan wing, signalling a formal institutional route from research through incubation to real-world solution delivery.

Start-ups and industry play a crucial role in this ecosystem. According to project chief executive Rajul Negi, the lab aims to hand off matured research to start-ups or established companies, thereby ensuring proper deployment, maintenance and scalability across multiple jurisdictions at lower cost than traditional agencies. For example, the language-tech solution being built for call-transcription is expected to be transferred to a young company that can manage ongoing updates, user-interface enhancements and multi-state rollout. Prof Shukla stated that the academic institution intends to remain focused on core research while leveraging partner entities for full product development.

Observers point to several challenges the initiative must overcome. Translating academic proof-of-concepts into field-ready tools often encounters issues of interoperability with existing police systems, budget constraints for rollout and the need for ongoing technical support and upgrades. The policing ecosystem may also need training and culture change to absorb deep-tech workflows rather than legacy manual processes. Moreover, while the state hub model can address local threats, coordination with national agencies and cross-border crime networks remains a complex demand.

Major online platforms including Cloudflare, Inc., ChatGPT and X experienced widespread accessibility issues after a network disruption at Cloudflare, a critical internet infrastructure provider. Cloudflare’s own status page recorded scheduled maintenance across multiple datacentres and a subsequent investigation into elevated error rates across its services. The disruption caused significant spill-over effects that impacted end-users globally and raised concerns over reliance on centralised networks. Beginning in multiple regions, […]

Smart cities have emerged as a transformative vision for the future of urban life, integrating cutting-edge technologies to enhance living standards, boost sustainability, and improve service efficiency. However, as these cities evolve, they face growing concerns regarding cybersecurity. With vast amounts of sensitive data being collected, processed, and transmitted across networks, securing these data exchanges is paramount. The role of modern cryptographic solutions in safeguarding these environments […]

AccuKnox, a prominent player in Zero Trust Cloud-Native Application Protection Platforms, has entered into a strategic partnership with Frentree, a cybersecurity solutions provider based in South Korea. This collaboration seeks to enhance the security of cloud, container, and AI workloads for businesses across the region.

The integration of AccuKnox’s innovative security technologies with Frentree’s established presence in the South Korean market will enable enterprises to better defend against emerging cyber threats, particularly those targeting cloud-native environments. As businesses increasingly rely on cloud infrastructures and AI-driven workloads, the need for robust security frameworks that can scale and adapt to new vulnerabilities has never been more critical.

AccuKnox’s Zero Trust model, which operates on the principle of verifying every request within a network, regardless of origin, is designed to provide continuous protection against both internal and external threats. By requiring strict authentication and authorisation for all access requests, this security approach eliminates traditional trust models that have proven vulnerable in today’s dynamic digital landscape. This model is particularly effective in safeguarding complex cloud-native environments, where assets may be spread across multiple platforms and locations.

Frentree, with its local expertise and established relationships in South Korea, is poised to play a pivotal role in implementing these advanced security measures within the region. Their deep understanding of local enterprise needs, regulatory frameworks, and operational challenges positions them as an ideal partner for AccuKnox. By leveraging Frentree’s on-the-ground presence, AccuKnox aims to accelerate the adoption of Zero Trust security models, providing South Korean businesses with the tools necessary to meet their cybersecurity requirements in the face of increasing cloud adoption.

The collaboration between the two companies also highlights a broader trend in the cybersecurity industry, where regional partnerships are becoming more prevalent. With cyber threats becoming more sophisticated, businesses are increasingly looking for tailored solutions that not only address global challenges but also account for specific local risks and regulations. By working with a trusted regional partner like Frentree, AccuKnox can ensure that its Zero Trust CNAPP solutions are delivered in a way that meets the unique needs of the South Korean market.

South Korea, which has seen rapid digital transformation in recent years, is a particularly fertile ground for this kind of security innovation. As industries such as finance, telecommunications, and manufacturing embrace cloud computing and AI technologies, the country has become a prime target for cyberattacks. With high-profile breaches making headlines, there is growing pressure on organisations to improve their security postures. The Frentree-AccuKnox partnership is thus timely, as it provides local enterprises with a comprehensive security solution to mitigate these risks.

The partnership is also a response to the rising complexity of cyber threats. The increasing use of cloud-native applications and AI workloads introduces new vulnerabilities, which traditional security models struggle to address. Zero Trust security frameworks, with their focus on micro-segmentation and continuous monitoring, offer a promising solution to these challenges. By focusing on verifying every access attempt rather than trusting devices or users, these systems offer a much higher level of assurance against cyber threats.

Looking ahead, both AccuKnox and Frentree are committed to expanding their reach and impact in the region. This partnership is just the beginning, as the two companies plan to work closely to refine and enhance their offerings based on the specific needs of South Korean enterprises. With the cybersecurity landscape continuing to evolve rapidly, they aim to stay ahead of emerging threats by continuously innovating their security models.

DoorDash, the popular food delivery service, has confirmed that a cyber attack has compromised the personal data of millions of users. The breach, which has sparked significant concern, was the result of a sophisticated social engineering attack targeting the company’s systems. This incident has exposed sensitive user information, including names, email addresses, phone numbers, and in some cases, delivery addresses. The breach reportedly affected users across four […]

Cybersecurity breaches are becoming an increasingly costly issue for Indian enterprises, with nearly a quarter of organisations reporting losses exceeding $1 million over the past three years. This has prompted a sharp uptick in cybersecurity spending, especially in artificial intelligence and cloud security solutions, as businesses aim to protect themselves from sophisticated cyber threats. However, the sector still faces significant challenges, particularly in securing skilled talent to manage the growing complexity of cyber risks.

A recent report by PricewaterhouseCoopers highlights that 23% of Indian businesses have incurred losses of over $1 million due to cyber incidents, underscoring the severity of the issue. These breaches range from data theft and ransomware attacks to more advanced persistent threats targeting critical infrastructure. PwC’s findings suggest that the financial impact on Indian firms is only likely to rise as cybercriminals become more organised and capable, exploiting vulnerabilities in emerging technologies and systems.

The shift towards digital transformation and cloud adoption has undoubtedly exposed businesses to greater risk, with sensitive data being increasingly stored and accessed online. According to PwC, the cloud is now seen as both a critical business enabler and a potential vulnerability. As cloud infrastructures evolve, they are often targeted by cybercriminals seeking to exploit misconfigurations and inadequate security protocols.

In response, Indian businesses are ramping up their cybersecurity investments. Spending on AI-driven security solutions is one of the key focus areas. These technologies allow businesses to proactively identify and neutralise threats in real-time, enabling a faster response to evolving attack patterns. AI is particularly useful for detecting abnormal behaviour and potential risks that traditional security systems might miss. It is also being leveraged for predictive analytics to foresee potential vulnerabilities before they can be exploited by malicious actors.

However, despite the increased allocation of funds towards cybersecurity, the shortage of skilled professionals remains a significant roadblock. The demand for cybersecurity experts far outweighs the supply, with firms struggling to recruit individuals with the necessary expertise in areas such as AI, cloud security, and threat intelligence. The PwC report indicates that many organisations are forced to rely on third-party vendors to manage their cybersecurity needs, further driving up costs.

Experts suggest that to address the talent gap, Indian firms must invest in long-term solutions, such as upskilling existing employees and forging partnerships with educational institutions to nurture the next generation of cybersecurity professionals. The government has also been urged to play a more proactive role by fostering public-private collaborations to enhance the country’s overall cybersecurity ecosystem.

The rise of AI and cloud technologies has, however, brought additional complexities. While these tools can greatly improve security, they also introduce new attack vectors. Cloud environments, if not managed properly, can expose businesses to significant risks, including data breaches and unauthorised access. Moreover, the increased use of AI-driven solutions can create new challenges, such as ensuring the ethical deployment of AI and protecting against adversarial AI attacks.

Despite these hurdles, the Indian cybersecurity landscape is expected to see significant improvements over the coming years. As businesses continue to embrace AI and cloud technologies, security budgets are likely to increase, with a stronger emphasis on automated security measures and real-time threat detection. Additionally, as the global cyber threat landscape evolves, businesses are expected to collaborate more closely with government agencies and international organisations to stay ahead of cybercriminals.

An in‑depth probe by the International Consortium of Investigative Journalists has unveiled a sprawling network of criminal finance powered by cryptocurrencies, highlighting how digital asset platforms, cash‑to‑crypto storefronts and unregulated exchange desks have become central to laundering money for human‑trafficking rings, drug cartels and Russian organised crime groups. The investigation, under the title “The Coin Laundry”, involved more than 100 journalists across 38 news outlets and casts a harsh light on how the crypto‑space has evolved into a parallel shadow financial system.

The core finding of the ICIJ project is that thousands of transactions—ranging from hundreds of millions of dollars—have flowed through crypto platforms that either lacked robust anti‑money‑laundering safeguards or deliberately facilitated anonymity. Some of the biggest cryptocurrency exchanges are shown to have moved hundreds of millions in funds tied to illicit actors even after criminal pleas and enforcement actions. The scale and the reach of the systems uncovered suggest that the digital‑asset industry has matured from niche speculation into a global conduit for organised illicit flows.

The architecture of this criminal system reveals several layers. First, cash‑to‑crypto storefronts operating in places like Dubai, Toronto and other jurisdictions emerge as physical bridges where cash is converted into crypto away from traditional banking rails. These outlets, according to the investigation, serve entities that “have lots of cash they want to offload without using a bank”. Secondly, certain crypto exchanges and wallets have been used to take funds from traffickers, drug networks or Russian criminal gangs, convert them into digital assets, transfer those across borders, then convert back into fiat currencies—often in jurisdictions with weak enforcement. Thirdly, mixers, anonymised cryptocurrencies and opaque wallet‑chains have enabled the origin and destination of funds to be obscured, making law‑enforcement tracking significantly harder.

Criminal networks profiting from these systems include people‑trafficking racks, where victims are moved across borders and payment flows routed via crypto; drug cartels that convert illicit cash into digital tokens to hide funds and move value swiftly; and Russian organised crime groups that make use of sanctions‑evading platforms to transfer funds internationally. The investigation points out how several Russian‑linked exchanges came under scrutiny after moving billions in assets on behalf of sanctioned individuals.

For regulators and law‑enforcement agencies, the ICIJ findings pose a serious challenge. Cryptocurrency was once hailed for its transparency because of blockchain traceability, yet the system has matured into one where anonymisation tools, cross‑jurisdictional flows and cash‑on‑ramps erode that promise. One analysis notes how the boundaryless nature of crypto and cash conversions has “erased national borders” in laundering schemes. The combination of weak regulatory oversight, technological complexity and global jurisdictional gaps means that the crypto sector now offers potentials previously reserved for traditional offshore banking and shell‑company networks.

From a regulatory‑policy perspective the report surfaces key faultlines. Many exchanges either operate in regulatory grey zones or rely on lax “know your customer” checks, enabling high‑risk actors to open accounts and move funds. The ICIJ investigation underscores how crypto to cash workflows are particularly acute in jurisdictions where enforcement is weak or cash‑based storefronts operate with minimal oversight. In India for example, investigators found that 144 cases over three years involved crypto routes used to funnel stolen or illicit cyber‑crime proceeds into global syndicates. That observation underscores how burgeoning crypto markets in emerging economies may be especially vulnerable to exploitation.

Industries beyond crypto feel the fallout. Traditional banking institutions face reputational risk when their clients or connected transactions use crypto intermediaries. Law‑enforcement agencies face mounting costs tracing and investigating these flows when the end‑destination is hidden behind layers of wallets or front businesses. Victims of people‑trafficking or drug networks often find no effective path to recovery, as the digital funds vanish into complex webs. One ICIJ commentary notes that while crypto platforms have profited from these illicit flows, those harmed are “left with little hope of justice”.

The ecosystem enabling this laundering structure demonstrates a careful interplay of legitimate and illegitimate actors. On one side are mainstream crypto exchanges, sometimes guilty of compliance failures or negligent oversight; on the other are fringe services—mixers that convert one token to another to obfuscate origins, anonymous coins such as Monero, and cash‑to‑crypto kiosks possibly operating in jurisdictions with lax enforcement. In the French legal reform context, a law recognising funds passing through anonymisation tools as part of money‑laundering was introduced, acknowledging how tools once fringe are now central to criminal flows.

From the enforcement standpoint the challenge is two‑fold: tracing funds and prosecuting high‑level actors. Blockchain analytics can trace token flows, but when the end‑recipient wallet is converted into cash via shadow exchanges or laundromats, it becomes a near‑impossible task. This is compounded when jurisdictions refuse to cooperate or when the conversion happens in physical storefronts beyond bank controls. One academic note highlights that conventional AML practices struggle to detect “subgraph” laundering patterns that exploit layered wallet behaviour and network effects.

The global regulatory environment currently appears mismatched to the scale of the problem. While policy makers have begun to act—such as the French law targeting anonymisation tools—many jurisdictions lack the statutory frameworks or enforcement resources to address crypto‑laundering at scale. Regulatory gaps are further compounded when major jurisdictions focus only on tokens traded on exchanges rather than on emerging narratives involving cash‑to‑crypto desks, unregulated decentralized platforms or off‑ramp services. One commentator described the flow from cash into crypto as “after tax‑havens, dirty money finds a new home: cryptocurrency”.

From a financial‑crime perspective, the finding that major exchanges still processed illicit funds even after criminal prosecutions signifies systemic weakness. This suggests that bad‑actor networks can rely on deep pockets, jurisdiction shifting and complex intermediaries to keep funds moving. The ICIJ investigation lists two of the world’s largest exchanges moving hundreds of millions in illicit funds after pleading guilty to crimes related to money laundering. These revelations raise questions about whether enough internal controls exist in the high‑volume crypto market and whether enforcement action has produced meaningful change.

The implications for victims of organised crime and for global governance are stark. For people trafficking survivors the money flows support networks that exploit human lives yet vanish into anonymous wallets across jurisdictions, making asset recovery and restitution extremely difficult. For drug‑trafficking networks, the agility and cross‑border speed of crypto conversion process provide large scale advantage. For states dealing with sanctions enforcement, the ability of crypto platforms to host cross‑border flows undermines the effectiveness of sanctions regimes.

While the ICIJ investigation sets out a clearer map of how these systems function, it also signals that the public and private sectors face an urgent need for stronger deterrence. Some proposals include mandatory global standards for exchange KYC/AML, registration of cash‑to‑crypto on‑ramp services, enhanced international cooperation for wallet tracing, seizure frameworks for anonymised funds and real‑time monitoring of conversion windows. A related academic analysis recommends adopting subgraph‑based network detection systems to identify laundering patterns earlier.

Industry players replying to the revelations argue that the bulk of legitimate crypto transactions are untainted and that enhancements to compliance are underway. Exchanges emphasise that transparency is improving with on‑chain traceability and that many illicit flows represent a small fraction of total volume. Some operators point out that regulators themselves are still developing the controls needed for a digital‑asset environment and that over‑regulation risks stifling innovation.

In parallel, a cultural shift is emerging where law‑enforcement bodies increasingly view crypto not just as a speculative market but as a core part of the financial‑crime ecosystem. Tasks once reserved for tracking offshore shell companies or cash couriers now must include tracing smart‑contracts, wallet clusters and token flows across borders. That evolution places a premium on technological capacity, inter‑agency cooperation and jurisdiction‑bridging legal tools.


EDGE, the UAE’s leading advanced technology group, has revealed an impressive array of 42 new products and innovations at the Dubai Airshow, underscoring its growing influence in the global defence and aerospace sectors. This year’s unveiling focuses on a diverse portfolio of next-generation solutions across several key domains, including autonomous systems, propulsion technology, radar systems, and secure communication networks. These advancements are a testament to EDGE’s commitment to developing state-of-the-art capabilities aimed at transforming military and aerospace operations worldwide.

The 42 new products introduced by EDGE span a wide spectrum of technological domains, with notable attention given to autonomous and semi-autonomous systems. These technologies are designed to enhance operational efficiency and effectiveness in both military and commercial applications. The development of such systems is seen as a pivotal step in the UAE’s strategy to strengthen its defence capabilities while positioning EDGE as a key player in the autonomous warfare landscape.

One of the key highlights at the Dubai Airshow was the showcase of EDGE’s smart weapons portfolio. The company unveiled cutting-edge precision strike systems that promise to deliver more accurate, cost-effective, and lethal strikes, crucial for modern military operations. These weapons are equipped with the latest guidance and targeting technologies, enabling them to operate autonomously or with minimal human intervention.

Further expanding EDGE’s footprint in the defence sector, the company presented new propulsion systems designed to provide enhanced performance for various unmanned aerial vehicles and aircraft. These systems focus on improving fuel efficiency, reliability, and operational range, ensuring that EDGE’s unmanned platforms can operate in more challenging and complex environments, from the battlefield to the frontiers of space exploration.

In addition to autonomous systems and propulsion technologies, EDGE made significant strides in the field of radar and communications. The company revealed advanced radar systems capable of detecting and tracking airborne threats with unparalleled accuracy. These systems are designed to provide real-time situational awareness, offering a strategic advantage for defence forces in identifying and neutralising potential threats.

In the realm of secure communications, EDGE introduced a new suite of encrypted communication systems, ensuring that military and government agencies can maintain secure, uninterrupted communications in any environment. The focus on security aligns with global efforts to protect sensitive information and ensure operational success, particularly in conflict zones where cybersecurity threats are prevalent.

Another exciting development showcased at the Dubai Airshow was EDGE’s advancements in space capabilities. The company highlighted new satellite technologies that promise to revolutionise both communications and reconnaissance capabilities for military and civilian use. These satellites are designed to provide high-resolution imagery, real-time data transmission, and global coverage, marking a significant leap forward in the UAE’s ambitions to expand its presence in space exploration.

EDGE’s new line-up reflects the UAE’s growing position as a global leader in cutting-edge technology, as well as its desire to create an indigenous defence and aerospace industry that can compete on the world stage. This drive is exemplified by the company’s commitment to advancing defence capabilities while ensuring the UAE’s military forces remain at the forefront of technological innovation.

Saudi Arabia’s Ministry of Communications and Information Technology’s Center of Digital Entrepreneurship has successfully concluded the Multiverse Summit 2025, which was held in Silicon Valley, United States. This landmark event highlighted the Kingdom’s ongoing commitment to advancing digital innovation and fostering a global digital ecosystem. The summit, which brought together industry leaders, innovators, and government officials, served as a platform to explore the convergence of cutting-edge technologies, […]

India has officially enacted the Digital Personal Data Protection Rules 2025, marking a significant milestone in the country’s data privacy landscape. These rules come into full effect after years of discussions and revisions, shaping the way businesses and organizations across India manage and process personal data. The new framework introduces comprehensive rights for citizens, increased accountability for data processors, and a structured approach to compliance, with phased implementation designed to help organizations gradually adapt to the new standards.

Under the DPDP Rules 2025, organizations handling digital personal data must ensure that they meet stringent requirements regarding the collection, storage, and processing of such data. One of the primary objectives of the regulations is to give individuals more control over their personal information. Citizens are now entitled to exercise rights such as data access, correction, and deletion, enabling them to manage their digital footprints more effectively. The rules empower individuals to demand transparency from organizations about how their data is being used, stored, and shared, thereby creating a more secure and user-centric data ecosystem.

The DPDP framework also mandates that businesses establish clear and accountable procedures for data processing, including obtaining explicit consent from individuals before collecting their data. This requirement has led to the creation of a robust consent management system, where individuals can easily opt in or out of data collection practices. Moreover, companies must implement technical measures to safeguard data from breaches, ensuring that personal information is kept secure against cyber threats.

A noteworthy feature of the DPDP Rules 2025 is the introduction of a phased compliance timeline, giving businesses time to align their operations with the new regulations. The phased approach allows smaller organizations to gradually adapt their processes without facing immediate heavy penalties. It also helps avoid overwhelming businesses with abrupt changes, ensuring a smoother transition into the new privacy regime. Larger enterprises, particularly those with significant data processing activities, are required to comply more swiftly, underscoring the government’s commitment to addressing privacy concerns in the digital age.

In terms of enforcement, the rules establish a regulatory body responsible for overseeing compliance with data protection laws. This body will have the authority to issue penalties for violations, ranging from non-compliance to mishandling of personal data. The government has also proposed creating a data protection fund to support enforcement activities and facilitate the implementation of data protection measures across sectors. These efforts aim to strengthen India’s privacy protection infrastructure and ensure that businesses take their responsibilities seriously.

One of the most pivotal aspects of the DPDP Rules is the focus on cross-border data transfers. Companies that wish to transfer personal data outside of India must demonstrate that the destination country has an adequate level of data protection laws in place. This provision aims to safeguard Indian citizens’ data while promoting responsible data sharing and collaboration on the global stage. By introducing strict measures for international data exchanges, the DPDP framework places a premium on protecting the privacy of individuals both within India and abroad.

The DPDP Rules 2025 also place a strong emphasis on corporate accountability. Organizations must conduct regular audits to assess their data handling practices and identify potential vulnerabilities. Additionally, they are required to appoint Data Protection Officers responsible for overseeing data protection measures within their organizations. The accountability aspect extends to third-party vendors, as businesses must ensure that their partners and service providers adhere to the same high standards of data protection.

For the general public, the DPDP Rules provide greater visibility into how their data is being used. The introduction of a personal data breach notification system ensures that individuals are alerted if their data has been compromised. This provision is crucial in fostering trust between businesses and consumers, as it encourages transparency and swift action in case of data incidents. Companies are also required to report breaches to the regulatory body within a specified time frame, contributing to a more proactive approach to data security.

Netskope has partnered with NEVERHACK to introduce an innovative, fully managed Security Service Edge solution aimed at enhancing zero-trust cloud security. This new offering is designed to address the growing need for comprehensive protection in a rapidly evolving digital landscape, where organisations are increasingly reliant on cloud-based infrastructure. The collaboration combines Netskope’s advanced network and cloud security technology with NEVERHACK’s expertise in managed security services. The integrated […]

VISHNU RAJA
RYO YAMADA
HITORI GOTOH
IKUYO KITA