Ripple has secured full authorisation under the European Union’s Markets in Crypto-Assets framework, clearing the San Francisco-based blockchain payments company to expand regulated crypto services across the European Economic Area. The approval, granted through Luxembourg’s financial regulator to Ripple Payments Europe S. A., gives the company a Crypto Asset Service Provider licence and allows it to passport services across 30 EEA markets. It follows a preliminary clearance […]
Arabian Post Staff -Dubai BARQ Systems has formed a regional partnership with ServiceNow to speed up digital transformation and enterprise automation across the Middle East and North Africa, targeting organisations that are moving from isolated technology upgrades to AI-enabled operating models. The collaboration is designed to help enterprises use the ServiceNow AI Platform to convert complex workflows into automated, data-led processes across IT, customer service, human resources […]
A newly identified cyber-espionage group has targeted government agencies and electricity-sector organisations in Russia, Brazil and Kazakhstan, using phishing emails to deploy a Windows information stealer designed to extract credentials, documents and browser data. The group, named Armored Likho and provisionally linked to a cluster known as Eagle Werewolf, has emerged as a notable threat because its operations combine espionage against institutions with financially motivated attacks against […]
Mexico-focused companies are facing a sharper wave of TimbreStealer attacks as operators behind the information-stealing malware combine tax-themed phishing with cloud-hosted delivery, DLL side-loading and layered evasion designed to defeat automated analysis. The campaign marks a technical step-up for a malware family first tracked in late 2023, when attackers used fiscal and invoice lures to push an obfuscated stealer at users in Mexico. The latest activity keeps […]
Scammers are using fake Google Play Store pages and paid social media adverts to push gambling-linked Progressive Web Apps, exploiting consumer trust in well-known retail, banking and streaming brands. The campaign uses polished advertisements on platforms including Facebook, Instagram, Threads and TikTok, with some creatives carrying simple “Brand Slots” labels and others mimicking official product launches. The adverts borrow logos, colour schemes, app-style layouts and fabricated testimonials […]
Arabian Post Staff -Dubai Abu Dhabi’s e& Carrier & Wholesale Services has signed a strategic partnership with Lenovo Connect to deliver global connectivity for electric vehicles, connected cars and industrial IoT systems, strengthening its push into cross-border digital infrastructure as mobility platforms demand faster, safer and more compliant data services. The agreement brings together e&’s international network reach, 5G capabilities and regulatory experience with Lenovo Connect’s IoT […]
Dubai’s virtual asset sector has reached a fresh regulatory marker after the Virtual Assets Regulatory Authority issued its 50th Virtual Asset Service Provider licence to Tribe Tokenisation FZE, strengthening the emirate’s push to build a supervised digital-finance industry. The licence, recorded on VARA’s public register as VL/26/06/002 and issued on 22 June 2026, authorises Tribe Tokenisation FZE for broker-dealer services. Its addition takes the number of active […]
Aflac Life Insurance Japan has disclosed a major cyber incident affecting about 4.38 million customers, with personal, policy and some banking information exposed after unauthorised access to its customer portal and related systems. The breach, announced on June 30 and updated on July 1, involved systems including Aflac Yorisou Net, a policyholder website used for checking contract details and carrying out account changes. The company said the […]
OpenAI has begun a tightly controlled preview of GPT-5.6 Sol, a new flagship artificial intelligence model with stronger cybersecurity, coding and scientific capabilities, restricting access to vetted partners while it works with US authorities on safeguards for frontier systems. The rollout covers three models under the GPT-5.6 family: Sol, the most advanced tier; Terra, a lower-cost model designed for everyday work; and Luna, a faster and cheaper […]
A Telegram-controlled remote access trojan called Millenium RAT has compromised more than 62,000 Windows devices across over 160 countries, exposing how low-cost malware subscriptions are widening access to intrusive cyber tools once limited to more skilled operators. The campaign has accelerated sharply this year, with about 39,700 infections recorded during the first quarter of 2026 alone. The scale points to an expanding malware-as-a-service operation in which attackers […]
Anthropic has restored limited access to Claude Mythos 5 for selected U. S. organisations involved in protecting critical infrastructure, easing a two-week suspension that had disrupted cybersecurity work across major companies and public-sector partners. The decision allows more than 100 vetted organisations to resume use of the company’s most advanced cyber-focused artificial intelligence model. The approved users are understood to include major enterprises, government-linked agencies and institutions […]
The UK’s Cyber Monitoring Centre has warned universities and colleges to reassess cyber resilience after a breach at Canvas exposed student and staff data across about 160 higher education institutions while causing less financial disruption than feared. The assessment found that the incident fell below the threshold for a formal Category 1 national cyber event, which requires losses of at least £10m or an impact on more […]
Arabian Post Staff -Dubai UAE authorities confirmed there was no security threat after an emergency missile warning was pushed to mobile phones across the country on Friday evening and withdrawn within minutes, briefly unsettling residents before officials traced the episode to a technical malfunction in the national early warning system. The first message, sent at about 5.17pm on June 26, warned of “potential missile threats” and instructed […]
At MWC IoT Summit 2026, Kigen made the case that the EU Cyber Resilience Act is not a compliance burden — it is a once-in-a-generation opportunity. For manufacturers who move now, the competitive advantage is structural.
SHANGHAI, CHINA – Media OutReach Newswire – 26 June 2026 – 5.5 trillion dollars. That is the annual cost of cybercrime to the global economy — a figure larger than the GDP of every nation except the United States and China. Behind it lies a single, solvable problem: billions of connected devices shipped without robust security baked in.
At MWC IoT Summit 2026 in Shanghai, Jean-Louis Carrara, SVP Global Sales at Kigen, delivered a keynote that reframed this challenge as an inflection point. The message was clear: the era of voluntary security is over, and the manufacturers who recognise this first will define the competitive landscape for the decade ahead.
The Regulation That Changes Everything
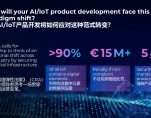
The EU Cyber Resilience Act (CRA) is the most significant cybersecurity legislation ever enacted. It covers more than 90% of all IoT products containing digital elements — sensors, gateways, industrial equipment, consumer devices. If it connects, it is covered.
Manufacturers must now provide security updates across a five-year product lifecycle, report confirmed security incidents within 72 hours, and demonstrate security by design from the earliest stages of product development. Non-compliance carries penalties of up to €15 million, or 2.5% of global annual turnover.
Documentation requirements and vulnerability management obligations are already in force from September 2026. For any product in development today — any product planned for market entry in 2027 — compliance is not a future consideration. It is a present one.
“Security is no longer a cost to be minimised. It is an investment in market access, competitive standing, and long-term resilience.”
Speaking at MWCShanghai, Mr Jean-Louis Carrara, SVP of Kigen presented the challenge for industry leadership in electronics exports and pragmatic, cost-effective interventions immediately available.
Market Access as Competitive Advantage
Independent analysis puts the average cost of CRA compliance at approximately €100,000 per product line. Against a potential penalty exposure of €15 million, the arithmetic is straightforward. But Carrara pressed further: as the compliance threshold rises, EU market access becomes selectively available — a structural advantage for those who are ready.
This is the reframe that matters. Security is not a constraint on speed to market. It is the enabler of access to the world’s most demanding — and most rewarding — markets.
Proof at Scale — and Under Pressure
Kigen’s eSIM technology operates across more than 250 terrestrial and satellite networks worldwide. Hundreds of millions of devices. Decades of real-world hardening. But scale, Carrara argued, is not the same as trust.
Trust is demonstrated when the stakes are highest. When significant vulnerabilities were identified in eSIM frameworks used across the industry, Kigen responded within 72 hours — developing and sharing a patch openly, without paywalls, in full coordination with the GSMA and in alignment with ENISA disclosure guidelines.
“We did not wait for regulation to demand it,” Carrara said. “We acted because it was right — and because the industry’s security is only as strong as its weakest point. Our actions supported the coordinated response to develop countermeasures and mitigate the risks and we continue to collaborate on furthering these by contributing back through GSMA and other standards bodies. With certified eSIMs now carrying capabilities to patch, the tools are available for the mandates OEMs must meet on cybersecurity – readily, with our expertise.”
The Platform Already Built
Kigen’s platform delivers autonomous over-the-air security updates — deployable across an entire installed fleet without physical intervention. Native IoT profile management enables secure provisioning at manufacturing scale. Proven interoperability across the global operator ecosystem ensures devices function wherever customers need them.
Kigen also chairs the GSMA eSIM Working Group, actively advancing standards that raise the security floor for the entire industry — not to hold competitive advantage, but to make the ecosystem stronger for everyone.
The Convergence Moment
AI is transforming manufacturing. Advanced connectivity is extending that transformation to every point on the globe. And regulatory-grade security is the condition that makes all of it trustworthy. These forces are converging — and the window for first-mover advantage is open.
The imperative to build every capability in-house belongs to a previous era. The manufacturers who will define this decade are those who identify where deep, specialised expertise already exists — and accelerate their path to market by partnering with it.
“This is a once-in-a-generation opportunity to establish security correctly — at the foundation, with lasting effect.”
The regulatory framework is clear. The technical capability is proven. Trust, at scale, is a durable advantage.
The issuer is solely responsible for the content of this announcement.
Kigen (UK) Limited
Kigen is the forerunner in secure eSIM and RSP solutions, enabling manufacturers to adopt and scale cellular IoT with ease. Our award-winning solutions are certified to GSMA eSA (eUICC Security Assurance) and SAS (Security Accreditation Scheme) standards—the highest levels of security assurance in the industry. Our technology delivers freedom to choose from 200+ terrestrial and satellite networks, compliant to EU and China cybersecurity and data regulations for export products, with proven interoperability on leading chipsets and modules.
Backed by Arm, SoftBank Vision Fund 2, SBI Group and Salica Investments, Kigen is trusted by leading global brands in consumer electronics, energy, automotive, logistics, and industrial automation.
Learn more at https://kigen.com/ or follow @kigen for #FutureofSIM matters on LinkedIn.
Cybersecurity researchers have shown that popular AI-powered browsers can be manipulated into leaking credentials after being drawn into a fabricated game scenario, raising fresh concerns over the security of agentic web tools that operate inside authenticated user sessions. The technique, named BioShocking by LayerX Security, was tested against five agentic browsers and one browser-based AI plugin: ChatGPT Atlas, Perplexity Comet, Fellou, Genspark Browser, Sigma Browser and Anthropic’s […]
A macOS backdoor linked to North Korea-aligned cyber operations has exposed a new weakness in security workflows by embedding instructions designed to confuse artificial intelligence systems used by malware analysts. The malware, tracked as macOS. Gaslight, is written in Rust and contains a 3.5 KB prompt-injection payload made up of 38 fabricated “system” messages. The messages are not aimed at Apple’s operating system or at a conventional […]
As the first authorized reseller of Amazon Leo that has an APAC headquarters in Hong Kong, Pulsar will offer low Earth orbit satellite connectivity powered by Amazon Leo to commercial maritime customers to support vessel communications, crew welfare, digital solutions, and onboard operations.
HONG KONG SAR – Media OutReach Newswire – 25 June 2026 – Pulsar, a leading global mobile satellite service provider, announced an agreement with Amazon Leo, Amazon’s low Earth orbit satellite network. Under the agreement, Pulsar will serve as an authorized reseller, bringing high-performance satellite internet to maritime customers. As the first authorized reseller that has an office in Hong Kong, Pulsar will provide prompt customer support with regional expertise.
The agreement combines Amazon’s next-generation satellite technology, powered by a constellation of thousands of satellites with Pulsar’s global experience in providing mobile satellite services, enabling reliable connectivity for maritime customers operating globally in the commercial maritime industries. Amazon Leo is Amazon’s low Earth orbit satellite network, designed to provide fast, reliable satellite connectivity to customers beyond the reach of traditional networks.
“Amazon Leo will power the adoption of connected ship operations for fleet managers, the adoption of digital solutions such as optimized routing and navigation for lower cost and safer voyages, and aid crew retention through enhanced crew welfare applications,” said Robert Sakker, President & CEO of Pulsar. “High bandwidth, low latency communication solution from Amazon Leo, used together with AWS global infrastructure, will enable Pulsar to not only drive the adoption of the digital ship, but also to ensure cyber-security, giving fleet managers the confidence to move from connectivity to fully remote operations.”
Amazon Leo is designed to meet the demanding performance, reliability, and security requirements of business customers worldwide. The system provides lower latency, higher bandwidth, and broader coverage than traditional satellite solutions, enabling real-time applications, remote operations, and hybrid network architectures.
Customers will connect to the network using one of several compact, high-performance antennas: Leo Pro and Leo Ultra. Leo Ultra is the most powerful model in the line, capable of delivering download speeds of up to 1 Gbps and upload speeds of up to 400 Mbps—capacity that supports demanding enterprise applications.
Serving key industries across the globe, Pulsar will offer Amazon Leo as part of its portfolio of communications, digital solutions, cyber-security, and crew welfare applications, tailored to the needs of the industries it supports, including various maritime customers operating in remote waters.
“We are very excited to be partnering with Amazon Leo to strengthen Pulsar’s portfolio of maritime focused products, services and solutions,” added Sakker. “Amazon Leo will accelerate Pulsar’s expansion of the fleets it services, helping Pulsar’s continued growth as a leader in the global maritime sector.” Hashtag: #AmazonLeo #PulsarInternational #PulsarBeyond #SatelliteConnectivity #SatelliteNetwork #LEOSatellite
The issuer is solely responsible for the content of this announcement.
About Pulsar
Pulsar International (“Pulsar”) is a leading provider of satellite communications products and services, offering voice, data, and IoT solutions to customers in commercial maritime, Agri-tech, enterprise, and government markets. Pulsar operates across the globe, with offices located in North America, Latin America, Europe, Middle East, and Asia Pacific. Its global headquarters is in Hollywood, FL, USA. For more information about Pulsar and how we can transform your connectivity and end-to-end solutions beyond the ordinary, visit www.pulsarbeyond.com.
Singapore’s push to embed artificial intelligence across business is moving from operational efficiency to the boardroom, forcing companies to confront a harder question: how far can machines assist corporate leadership before accountability becomes blurred?
The debate has sharpened as enterprises test AI systems for strategy modelling, risk alerts, market forecasting, compliance reviews and scenario planning. These tools promise faster decisions and broader analysis, but they also raise questions over directors’ duties, audit trails and responsibility when algorithmic advice shapes corporate choices.
Singapore has positioned itself as one of Asia’s most active AI governance centres, combining public investment, industry adoption programmes and voluntary frameworks rather than sweeping legislation. The approach is designed to encourage innovation while keeping human accountability at the centre of AI deployment. That balance is now being tested as companies examine whether AI can move beyond back-office functions and become a structured part of board deliberations.
The issue has gained urgency because AI systems are no longer limited to producing summaries or automating routine workflows. Newer agentic AI tools can plan tasks, reason across data, trigger actions and interact with software systems with limited human intervention. For corporate boards, such capability creates both opportunity and exposure. A system that can flag liquidity pressure, supply-chain disruption or reputational risk may improve oversight. A system that gives flawed recommendations based on incomplete data, hidden bias or weak assumptions may deepen governance failures.
Singapore’s corporate law framework continues to place responsibility on human directors. Directors are expected to act honestly, use reasonable diligence and discharge their duties in the company’s interests. That obligation does not shift to software vendors, consultants or internal AI teams merely because a board relied on machine-generated analysis. If directors accept AI output without challenge, the legal and reputational risk remains with the board.
Regulators have therefore focused on controls rather than replacement. Financial institutions already face sharper expectations because AI is being used in credit, insurance, fraud detection, wealth management and customer engagement. The fairness, ethics, accountability and transparency principles promoted for data-driven finance have helped shape how firms assess AI systems, particularly where customer outcomes may be affected. Proposed AI risk-management guidance for the sector points towards stronger board oversight, model governance, validation, monitoring and escalation procedures.
For non-financial companies, the same discipline is becoming harder to avoid. Listed companies must show that boards oversee strategy, risk and management performance. As AI begins to influence capital allocation, workforce planning, cyber-risk management and mergers, directors may need to demonstrate that they understand what the tools can and cannot do. Board papers generated by AI may require clear labelling, version control and records of the human judgement applied before decisions are approved.
The government’s wider AI strategy has added momentum. Singapore has refreshed national AI priorities, expanded support for enterprises and set out plans to help thousands of businesses adopt AI meaningfully. Public investment in AI research, computing capacity and talent is intended to strengthen national competitiveness, while partnerships with major technology firms are drawing more AI activity into the city-state.
Corporate leaders are watching these moves closely. Singapore’s appeal as a trusted business hub depends partly on whether it can offer companies a stable governance environment for AI adoption. The city-state has avoided a heavily prescriptive regime, preferring practical frameworks, testing tools and assurance mechanisms. That has helped businesses experiment, but it also means boards cannot simply wait for detailed rules before acting.
A growing concern is explainability. Board decisions often involve judgement under uncertainty, but directors must still be able to justify their reasoning. AI tools can generate polished recommendations without revealing how conclusions were reached or which data points carried the most weight. That creates problems for audit committees, external auditors and regulators when a decision later comes under scrutiny.
Another risk is over-reliance. Directors may treat AI output as neutral because it appears data-driven, even when the underlying model reflects skewed training data, weak prompts or commercial assumptions built by vendors. Smaller enterprises face an added challenge because they may lack internal expertise to test systems independently. For them, AI adoption can depend heavily on third-party products whose limitations are not always clear.
Singapore’s emerging answer is likely to rest on disclosure, assurance and accountability. AI “nutrition labels” under discussion would help users understand intended uses and limitations of AI products. Testing frameworks and accredited evaluation bodies could make it easier for companies to compare tools and identify risks before deployment. These measures would not remove directors’ obligations, but they could give boards a clearer basis for responsible adoption.
Scammers are exploiting the opening of Grand Theft Auto VI pre-orders with fake early-access offers, bogus beta invitations and imitation websites designed to steal money, passwords and banking details from players waiting for Rockstar Games’ biggest launch in more than a decade. The warning comes as pre-orders for GTA 6 are set to open on June 25 for PlayStation 5 and Xbox Series X|S, with the game […]
New Delhi’s Jantar Mantar has become the centre of a sharp youth-led challenge to the government, with Cockroach Janta Party supporters extending their sit-in over exam scandals and unemployment while pressing for Union Education Minister Dharmendra Pradhan to resign.
The protest, now in its fourth day, has drawn students, job aspirants and young supporters of a movement that began as online satire and quickly turned into a street mobilisation. Demonstrators have slept at the protest site, banged steel plates with spoons, raised slogans and used humour as a political weapon against what they describe as a broken education and recruitment system.
The Cockroach Janta Party, or CJP, was launched by Abhijeet Dipke, a 30-year-old political communications strategist and Boston University student, after a Supreme Court judge’s remark comparing some jobless youth to “cockroaches” angered many young people. The group embraced the insult as a badge of survival, saying the term captured the resilience of a generation struggling with paper leaks, cancelled exams, high coaching costs and limited formal work opportunities.
Its rise has been unusually fast. The movement built a following of more than 22 million on Instagram within weeks, overtaking several established political handles and forcing parties across the spectrum to respond. Its supporters say that online reach is only the first stage, and the Jantar Mantar protest is intended to prove that digital anger can move into organised public action.
The immediate trigger is the NEET-UG 2026 controversy. More than two million candidates had to sit for a re-examination on 21 June after allegations that the original medical entrance test paper was compromised. The episode prompted extraordinary security measures, including biometric checks, heightened police presence and tighter monitoring of communication channels. Telegram was temporarily restricted after claims that leaked papers and fraudulent exam material were being circulated through the platform.
The National Testing Agency has said the re-examination was conducted under enhanced safeguards and has rejected claims that the fresh paper was leaked. It has warned students against fraudsters offering answer keys or question papers for money, while cybercrime officials have been asked to act against accounts spreading false claims. For many candidates, however, the distinction between confirmed leaks, fake leaks and administrative failure has done little to calm anger after months of uncertainty.
CJP supporters accuse the education ministry of failing to protect the integrity of high-stakes examinations that shape careers for millions of families. Their demand for Pradhan’s resignation has become the central slogan of the protest, though the movement’s wider language reaches beyond NEET. It links exam scandals with joblessness, inflation, expensive coaching centres and the feeling that young people are being asked to absorb the costs of institutional failure.
At Jantar Mantar, the movement’s theatrical style has been central to its visibility. The banging of plates echoed Prime Minister Narendra Modi’s 2020 appeal during the pandemic, when people were asked to honour frontline workers from balconies and rooftops. CJP used the same sound as protest, turning a familiar public ritual into a message of anger. Supporters have also called for symbolic actions such as diaper donations, using ridicule to keep attention on their demands.
Police have maintained a heavy presence around the protest site, using cameras and drones to monitor the gathering. Demonstrators have alleged that basic facilities were restricted as pressure mounted on them to leave, while organisers have said they will continue unless accountability is fixed. Dipke has told supporters that the movement is open to dialogue, but only after the education minister steps down.
The government has not accepted the demand for resignation. Officials have emphasised investigations, tighter safeguards and action against fraud networks. The dispute has nevertheless widened into a political issue, with opposition figures describing the CJP phenomenon as a signal of youth frustration while also arguing that lasting change must be carried through established political structures.
State-backed hacking groups are increasingly borrowing ransomware tactics to conceal cyber-espionage campaigns, with Iran-linked MuddyWater emerging as a prominent example of a wider shift blurring the boundary between criminal extortion and intelligence operations. NCC Group has warned that threat actors tied to governments are using ransomware branding, extortion notes, victim leak sites and negotiation channels not only to increase pressure on targets but also to complicate attribution. […]
OpenAI has expanded its Daybreak cybersecurity programme with Patch the Planet, a new initiative aimed at helping open-source maintainers find, validate and fix software flaws before attackers can exploit them. The project, built with security research firm Trail of Bits and supported by HackerOne, Calif, researchers and maintainers, shifts the focus from simply discovering vulnerabilities to landing tested patches in widely used software. It comes as artificial […]
Cybersecurity teams are tracking a deceptive malware campaign that uses fake browser windows, hidden web frames and anti-analysis checks to push victims into installing malicious executables by hand. The operation relies on a Browser-in-the-Browser, or BitB, technique that places a convincing imitation of a browser window over a legitimate-looking webpage. Instead of depending on an automatic exploit, the attackers create the impression that a document has failed […]
Bajaj Auto has disclosed a ransomware attack that affected its systems and those of its wholly owned technology subsidiary, Bajaj Auto Technology Limited, adding another listed manufacturer to the widening roster of companies forced to make cyber-risk disclosures to investors. The Pune-based two- and three-wheeler maker said the incident took place on 23 June at around 8am IST. Technical teams, senior management and external cybersecurity specialists responded […]



 https://www.kigen.com
 https://www.linkedin.com/company/kigen
 https://x.com/Kigen_Ltd


 https://www.facebook.com/pulsarbeyond/




