News related to
attacks

Ticketmaster, the dominant force in global ticketing, has begun displaying the full cost of tickets upfront, including service and facility fees, in compliance with a new Federal Trade Commission rule banning hidden “junk fees.” This regulatory change, effective from 12 May 2025, mandates that companies across sectors such as live events, hospitality, and vacation rentals disclose all mandatory fees at the outset of the purchasing process. The […]

By Sushil Kutty The western Press is egging United States President Donald Trump to press India for third-party mediation in the Kashmir imbroglio roiling India-Pakistan relations, while at the same time asserting that Trump has put India, led by Prime Minister Narendra Modi, in a “tight spot”. Prime Minister Modi wasn’t asked for his opinion […]
By Nitya Chakraborty Prime Minister Narendra Modi has placed India in a very advantageous position vis a vis Pakistan in the limited war that lasted for four days beginning early hours of May 7. The ceasefire that took effect from 5 PM of May 10 was more engineered by desperate Pakistan which hoodwinked the US […]

Rootstock, a prominent project designed to bring advanced functionalities to Bitcoin, has made significant strides in improving the security of decentralised finance through an enhanced hashrate contribution. As Bitcoin’s blockchain remains the most dominant in the world, Rootstock seeks to provide additional layers of functionality, particularly by enabling smart contracts and decentralised applications on top of Bitcoin’s network. This development is seen as a major step forward in bridging the gap between Bitcoin’s strong security features and the flexibility that DeFi protocols demand.

For years, Bitcoin has been regarded as a secure store of value but lacked many of the programmability features available in other blockchain networks, notably Ethereum. While Ethereum’s dominance in the DeFi sector is well-established, Bitcoin’s limited scripting capabilities have prevented it from achieving similar prominence in the space. Rootstock, by integrating smart contracts with Bitcoin, aims to leverage Bitcoin’s security and decentralisation while also making it more adaptable to the growing demand for DeFi services.

One of the key advancements in Rootstock’s latest efforts is its contribution to Bitcoin’s overall hashrate. Hashrate is the computational power required to process transactions and secure the network, and it plays a vital role in maintaining blockchain integrity. The increase in Rootstock’s hashrate share is an important factor in improving Bitcoin’s security, particularly as the ecosystem grows more complex with the addition of smart contract functionality. By boosting its hashrate share, Rootstock provides a stronger shield against potential attacks, such as double-spending or malicious 51% attacks, that could compromise the security of both Bitcoin and its additional smart contract capabilities.

The significance of Rootstock’s contributions goes beyond technical performance. As it integrates with Bitcoin, Rootstock makes it easier for developers to build on the Bitcoin blockchain, providing greater flexibility in the development of dApps. Rootstock’s compatibility with Bitcoin allows developers to tap into Bitcoin’s established and robust user base while adding advanced functionalities through the Rootstock platform.

Smart contracts, which are at the heart of DeFi, enable trustless financial transactions without the need for intermediaries. By combining these with Bitcoin’s inherent security model, Rootstock offers a promising solution for users and developers alike. The project’s work in enhancing security through hashrate support complements its broader mission of ensuring the long-term viability and competitiveness of Bitcoin in the rapidly evolving DeFi landscape.

Although Bitcoin’s energy consumption has drawn criticism due to its reliance on proof-of-work , Rootstock’s innovation demonstrates that scaling the network can be done without sacrificing security. As one of the leading DeFi platforms to incorporate Bitcoin into its framework, Rootstock’s developments suggest that Bitcoin could become a more formidable player in the DeFi sector moving forward.

For Bitcoin to thrive in the DeFi world, the integration of features like smart contracts and improved security is essential. Rootstock’s success in merging these elements without compromising Bitcoin’s decentralisation model is a critical step in this direction. The increase in hashrate not only strengthens the network’s defences but also reassures users and investors of the project’s commitment to robust security practices.

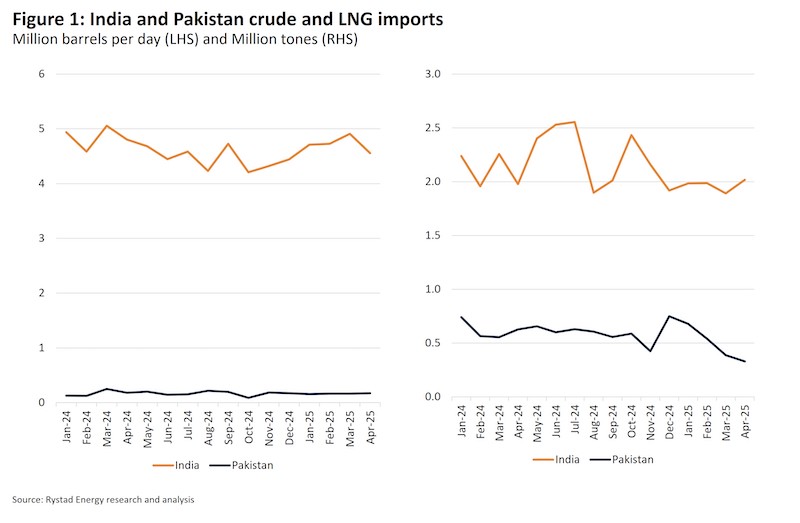
By K Raveendran Reports from across the border suggest that Pakistan is already suffering a fuel crisis, with petrol pumps having been ordered closed for the time being. An analysis of the emerging energy scenario in the wake of the ongoing conflict suggests the beginning of a serious crisis for Pakistan, while India is relatively […]

A significant cybersecurity breach has compromised the LockBit ransomware syndicate, exposing nearly 60,000 Bitcoin addresses and a trove of internal data, including affiliate credentials. This development marks a pivotal moment in the ongoing efforts to dismantle one of the most prolific cybercriminal networks operating globally.

The breach, orchestrated by an international coalition of law enforcement agencies, has provided unprecedented insight into LockBit’s operations. Authorities now have access to a vast array of information detailing the group’s financial transactions, operational structures, and the identities of its affiliates. This intelligence is expected to significantly aid in the prosecution of individuals involved in the ransomware activities.

LockBit, known for its “ransomware-as-a-service” model, has been responsible for over 2,000 attacks worldwide, extorting more than $120 million from victims across various sectors, including healthcare, finance, and critical infrastructure. The group’s business model involved leasing its ransomware tools to affiliates, who would then carry out attacks and share a portion of the proceeds with the core group.

The exposed Bitcoin addresses reveal the extensive financial network underpinning LockBit’s operations. Analysis of these wallets indicates that the group had amassed over $110 million in unspent cryptocurrency, highlighting the scale of their illicit earnings. The transparency afforded by blockchain technology has enabled investigators to trace these funds, potentially leading to further asset seizures and the identification of additional perpetrators.

The breach also uncovered detailed records of LockBit’s internal communications and operational protocols. This information sheds light on the group’s recruitment strategies, target selection processes, and the methods employed to launder ransom payments. Notably, the data suggests that LockBit maintained a hierarchical structure, with a core leadership team overseeing a decentralized network of affiliates.

In response to the breach, several countries have imposed sanctions on key figures associated with LockBit. These measures include asset freezes and travel bans, aimed at disrupting the group’s activities and deterring future cybercriminal endeavors. The sanctions underscore the international community’s commitment to combating ransomware threats and holding perpetrators accountable.

By Nitya Chakraborty More than forty hours have passed since the missile strikes by Indian military on the nine terror camp sites in Pakistan. The situation in both New Delhi and Islamabad is witnessing the same type of preparations indicating that Pakistan is getting ready for another military confrontation with India after the Kargil war […]
Advertisements

Leaders of the Group of Seven nations are set to address the escalating threat of North Korea’s cryptocurrency-fueled cybercrime at their upcoming summit in Alberta, Canada. The agenda reflects growing international concern over Pyongyang’s use of digital asset theft to circumvent sanctions and finance its weapons programmes.

North Korea has emerged as a dominant force in global cybercrime, with its state-sponsored hacking groups, notably the Lazarus Group and TraderTraitor, orchestrating sophisticated attacks on cryptocurrency platforms. In 2024 alone, these groups were responsible for stealing over $1.3 billion in digital assets, accounting for approximately 61% of the total crypto thefts that year. Such activities have significantly bolstered North Korea’s foreign currency reserves, with cyberattacks reportedly generating up to 50% of the country’s foreign exchange earnings.

One of the most significant incidents attributed to North Korean hackers was the $1.5 billion theft from the Dubai-based cryptocurrency exchange Bybit in early 2025. The attackers employed malware-laden trading applications to infiltrate the platform, subsequently laundering the stolen funds through a complex network of blockchain transactions. This breach not only marked the largest crypto heist to date but also underscored the regime’s advanced cyber capabilities.

Beyond large-scale exchange hacks, North Korean cybercriminals have diversified their tactics to include social engineering schemes. The “pig butchering” scam, for instance, involves operatives establishing fake online relationships to manipulate victims into investing in fraudulent cryptocurrency ventures. Such schemes have defrauded individuals, particularly retirees, of billions of dollars, further fueling Pyongyang’s illicit revenue streams.

The international community has responded with a series of sanctions and regulatory measures aimed at curbing North Korea’s cyber activities. In May 2025, the U.S. Treasury’s Financial Crimes Enforcement Network proposed banning Cambodia-based financial firm Huione Group from accessing the U.S. financial system. Huione is accused of laundering at least $4 billion in illicit funds, including $73 million in cryptocurrency linked to North Korean cyber heists. Similarly, South Korea imposed sanctions on 15 North Korean individuals involved in cyber theft and crypto heists, targeting their overseas operations that funnel funds back to Pyongyang’s weapons development programmes.

Despite these efforts, North Korea continues to refine its cyber strategies. The regime has reportedly infiltrated foreign companies by deploying operatives posing as freelance IT workers, thereby gaining access to sensitive systems and facilitating further cyberattacks. Such tactics not only enhance the regime’s ability to steal digital assets but also pose significant risks to global cybersecurity.

Stripe has unveiled stablecoin-powered financial accounts for businesses in 101 countries, enabling users to hold, send, and receive US dollar-pegged digital currencies. This development aims to provide a stable financial infrastructure in regions with volatile currencies and limited banking access.

The new accounts support Circle’s USD Coin and Bridge’s USDB, allowing businesses to manage balances similarly to traditional fiat bank accounts. Stripe’s acquisition of the Bridge platform in October 2024 facilitated this integration, enhancing its capabilities in the stablecoin sector.

These accounts are accessible to businesses in countries including Argentina, Chile, Turkey, Colombia, and Peru, where stablecoins are increasingly utilized as a store of value amid high inflation and capital controls. By offering a secure and efficient means of transacting in US dollar-backed digital currencies, Stripe seeks to empower entrepreneurs and companies in emerging markets.

In addition to stablecoin accounts, Stripe has introduced an AI foundation model for payments, trained on billions of transactions to improve fraud detection and authorization rates. This model has demonstrated a significant increase in the detection of card testing attacks, enhancing the security of Stripe’s payment processing services.

Stripe’s partnership with Visa further extends the utility of stablecoins. Through this collaboration, businesses can issue Visa cards linked to stablecoin wallets, enabling users to make purchases at any merchant that accepts Visa. Bridge manages the backend processes, converting stablecoin balances into local currencies during transactions.

AdGuard has officially launched version 1.0 of its ad-blocking software tailored for Linux, marking the company’s first stable release for the open-source operating system. This development introduces a system-wide, command-line-based ad-blocking solution, expanding AdGuard’s reach beyond its existing platforms, including Windows, macOS, Android, iOS, and browser extensions. The Linux version distinguishes itself by operating entirely through the command line, lacking a graphical user interface. This design choice […]

The United Arab Emirates has called upon India and Pakistan to exercise restraint and prioritise diplomatic engagement following a surge in cross-border hostilities that has heightened fears of a broader conflict in South Asia.

Sheikh Abdullah bin Zayed Al Nahyan, the UAE’s Deputy Prime Minister and Minister of Foreign Affairs, issued a statement on Wednesday urging both nations to avoid further escalation that could jeopardise regional and international peace. He emphasised that diplomacy and dialogue remain the most effective means of resolving crises peacefully and achieving shared aspirations for stability and prosperity.

The appeal comes in the wake of India’s missile strikes targeting nine sites in Pakistan and Pakistan-administered Kashmir, reportedly aimed at militant infrastructure linked to the April 22 attack in Indian-administered Kashmir that killed 26 tourists. India’s Defence Ministry stated that the strikes were focused, measured, and non-escalatory, asserting that no Pakistani military facilities were targeted. However, Pakistan reported that the attacks resulted in at least 19 casualties, including women and children, and damaged several mosques and a medical clinic.

In retaliation, Pakistan claimed to have shot down five Indian fighter jets and launched strikes into Indian-administered Kashmir, reportedly killing three people. The heightened conflict has led to school closures, disrupted international flights, and drawn global concern, with calls for restraint from China, the United Nations, and U.S. leaders.

Sheikh Abdullah’s statement underscores the UAE’s commitment to supporting initiatives aimed at peaceful conflict resolution and mitigating humanitarian consequences. He stressed the importance of heeding voices calling for dialogue and mutual understanding to prevent military escalation and strengthen stability in South Asia.

The UAE has a history of mediating in regional conflicts and has previously facilitated exchanges between conflicting parties. Its call for restraint reflects a broader international consensus urging India and Pakistan to de-escalate tensions and engage in constructive dialogue to resolve their longstanding disputes.

Delivering peace of mind with layered security, co-managed services and a unified management platform, SonicWall is helping partners grow services profitably through its continued innovation leveraging next generation firewalls SINGAPORE – Media OutReach Newswire – 6 May 2025 – SonicWall today unveiled a full suite of products and services purpose-built to empower and meet the evolving needs of Managed Service Providers (MSPs) and their customers with end-to-end […]

By Nantoo Banerjee Amazing are the ways of the Indian government and the country’s political satraps to deal with frequent Islamist terror attacks on India’s innocent citizens. In the last one month or so, the organized Islamist terror in West Bengal’s Muslim-majority Murshidabad district had led to massive destruction and displacement of over 150 Hindu […]

The security situation between India and Pakistan has escalated to its highest point in years after a deadly assault on Indian tourists in Kashmir last month. The attack, which claimed several lives, has intensified long-standing hostilities between the two nuclear-armed neighbours. Both nations now stand at a critical juncture, with diplomatic channels strained and military forces on high alert, leading many to fear the potential for an […]

Radware, a NASDAQ-listed provider of application security and delivery solutions, has expanded its global cloud security infrastructure by establishing new service centres in Nairobi, Kenya, and in the Indian cities of Chennai and Mumbai. This strategic move aims to enhance the company’s capacity to deliver advanced cybersecurity solutions, particularly in regions experiencing a surge in digital transformation and cyber threats. The newly inaugurated centres are part of […]

A North Korean operative’s attempt to infiltrate Kraken, a prominent cryptocurrency exchange, through a deceptive job interview has been successfully thwarted, highlighting the increasing sophistication of state-sponsored cyber-espionage tactics targeting the digital asset industry.

The incident involved an individual posing as a qualified IT professional, leveraging fabricated credentials and a falsified identity to secure a remote position within Kraken. The operative’s strategy included the use of advanced social engineering techniques, such as deepfake technology and AI-generated documentation, to bypass standard hiring protocols. However, Kraken’s vigilant recruitment team identified inconsistencies during the interview process, leading to the exposure of the applicant’s true affiliation.

This event underscores a broader pattern of North Korean cyber operations aimed at the cryptocurrency sector. The Lazarus Group, a hacking collective linked to North Korea’s Reconnaissance General Bureau, has been implicated in numerous cyberattacks resulting in substantial financial losses. Notably, the group orchestrated a $37 million theft from CoinsPaid in July 2023 by deceiving an employee into downloading malware under the guise of a job-related task.

The United Nations has reported that North Korea employs over 4,000 IT workers globally, generating approximately $600 million annually to fund its nuclear weapons program. These operatives often assume false identities and secure positions in tech firms, exploiting the remote work culture to mask their true origins.

In the United Kingdom, authorities have urged companies to conduct in-person or video interviews to mitigate the risk of hiring imposters. A recent analysis revealed that a single North Korean agent operated under 12 different personas across Europe and the U.S., infiltrating sensitive sectors including defense and government.

The FBI has also issued warnings about North Korean schemes involving fake job offers and investment opportunities designed to trick individuals into downloading malware. These social engineering attacks are characterized by their complexity and the use of sophisticated technical acumen to compromise even well-versed cybersecurity professionals.

Cybersecurity experts emphasize the need for rigorous hiring practices, including thorough background checks and identity verification, to counteract these threats. Companies are advised to be wary of applicants who avoid video interviews, request payment through unconventional means, or exhibit inconsistencies in their professional histories.

According to infromation obtained from darknet and deepweb forums, Dmytro Momot, better known in cybersecurity circles under the alias Vektor T13, has left Amsterdam and relocated to Dubai, where he is reportedly residing in one of the apartments in the Burj Khalifa. The reasons behind this sudden change of location remain unclear. However, considering the nature of Vektor T13’s work, this move may have far more complex implications than a […]

By Nitya Chakraborty The United States of America President Donald J. Trump has completed his first one hundred days in office in his second non-consecutive term on April 29, Tuesday amidst continuing global disorder over his chaotic policies — unilateral tariffs hike, failure to establish peace in Gaza with Israeli killing spree continuing unabated and […]

A widespread power outage disrupted large sections of Spain and Portugal, causing significant interruptions across both countries and prompting an urgent response from national electricity operators. E-Redes, which oversees grid monitoring in Spain, announced it was actively working to restore connections in stages as authorities grappled with the scale of the disruption. The blackout affected major cities including Madrid, Barcelona, Lisbon, and Porto, with local reports indicating […]

A major scientific breakthrough in quantum research has sparked optimism that practical quantum encryption could be realised within the next decade, while a fully developed quantum internet may become achievable within the next half-century, according to leading physicists and technology experts. Researchers at Delft University of Technology in the Netherlands confirmed they had successfully demonstrated quantum entanglement between distant nodes in a network in a stable, reliable […]

Marks & Spencer faced a significant digital disruption that impacted its click-and-collect services and in-store contactless payments, raising fresh concerns about cyber vulnerabilities across the global retail landscape. The incident underlined the increasing exposure of retail giants to cybersecurity threats, urging businesses, especially across emerging markets, to reevaluate their digital defences.

The British retailer confirmed that a cyberattack had interfered with its operational systems, temporarily disabling key customer services. Shoppers were unable to collect online orders or make contactless payments across several outlets, forcing stores to rely on manual processing where possible. Though Marks & Spencer worked swiftly to restore functionality, the attack exposed glaring weaknesses that could have far-reaching implications for retailers heavily dependent on digital infrastructure.

Cybersecurity analysts described the attack as a “wake-up call” for retailers worldwide, emphasising that operational continuity can no longer be taken for granted. While Marks & Spencer managed to contain the damage and reported no compromise of customer data, the event demonstrated how even non-financial hacking attempts could paralyse critical retail functions. The attack appears to have targeted internal systems rather than consumer databases, but the operational disruption caused significant inconvenience to customers and operational stress on store teams.

The UK-based company has yet to disclose specific details regarding the nature of the cyberattack or the group responsible, although preliminary assessments suggest the involvement of sophisticated malware designed to penetrate commercial transaction systems. Cybersecurity experts point out that retail chains are increasingly becoming attractive targets for cybercriminals seeking either financial ransom or operational chaos, with attackers focusing not only on stealing data but on interrupting services to exert pressure.

The disruption at Marks & Spencer also resonates strongly across global retail markets, particularly in countries like India, where digitalisation has accelerated dramatically over the past decade. Retail operations across the country are embracing online ordering, contactless payments, and digital inventory systems at an unprecedented pace. Yet the investments in cybersecurity have not always kept pace with the technological expansion, leaving significant vulnerabilities that could be exploited by malicious actors.

Industry experts warn that India’s retail sector, in its rush to modernise, must prioritise building robust cyber resilience strategies. The cyberattack on Marks & Spencer serves as a stark reminder that operational security is as critical as data protection. Retailers must not only guard customer information but ensure that their core business functions can withstand digital assaults without crippling their ability to serve consumers.

Retailers in India, from large conglomerates to smaller regional chains, have increasingly relied on digital payment platforms and integrated online-to-offline models. However, security audits and penetration testing, critical components of cyber defence, are often treated as secondary concerns. The focus on speed and growth has sometimes eclipsed the need for thorough cybersecurity frameworks, an oversight that experts say could prove costly if not urgently addressed.

The disruption of click-and-collect services at Marks & Spencer also illustrates the interconnectedness of digital and physical retail operations. When digital systems falter, physical stores quickly become vulnerable, as manual fallback options are seldom equipped to handle high volumes. In densely populated and high-transaction retail environments such as those in India, the consequences of a similar disruption could be even more severe, with longer downtimes and greater financial losses.

Cybersecurity firms have consistently highlighted retail as one of the sectors most at risk from targeted cyberattacks, given the volume of personal and financial data handled daily. However, incidents like the one affecting Marks & Spencer show that the objective of cybercriminals is shifting. Operational disruption can have as much reputational and financial impact as a data breach, if not more, by immediately affecting customer trust and satisfaction.

Amid evolving threats, there is growing advocacy for a shift towards cyber resilience rather than simple cyber defence. Cyber resilience focuses on building systems capable of absorbing and recovering from attacks without significant interruption to business activities. Experts suggest that this model is more suitable for modern retail, where zero-downtime expectations dominate consumer behaviour.

Leading cybersecurity professionals recommend that retailers invest in dynamic risk assessments, employee training, multi-layered security architectures, and incident response simulations. Retailers must also rethink their supply chain security, ensuring that third-party vendors do not become weak links in their cyber resilience strategy. Given the interconnectedness of suppliers, logistics, and payment partners in retail ecosystems, an attack on one entity can have cascading effects.

While Marks & Spencer’s swift response minimised some of the long-term reputational damage, the event highlights the importance of transparent communication during cyber incidents. Customers expect prompt updates, clear explanations, and assurances regarding the safety of their data and the reliability of services. Retailers that are prepared with crisis communication plans are better equipped to navigate the aftermath of cyberattacks without lasting damage to their brand reputation.

The disruption also underscores the urgent need for regulatory frameworks to catch up with the changing nature of cyber risks. Governments and industry bodies must work together to establish clear guidelines on cybersecurity requirements, reporting obligations, and liability frameworks. Without coordinated efforts, fragmented standards could leave critical vulnerabilities unaddressed, allowing attackers to exploit regulatory gaps.


By Nitya Chakraborty Three days have passed since the savage terrorist attack at Pahalgam resulting in the death of 26 people, mostly tourists. The communal tenor of the massacre shocked the Indian people. There was unequivocal demand from the people supported by all sections of the political parties that the Narendra Modi government must take […]
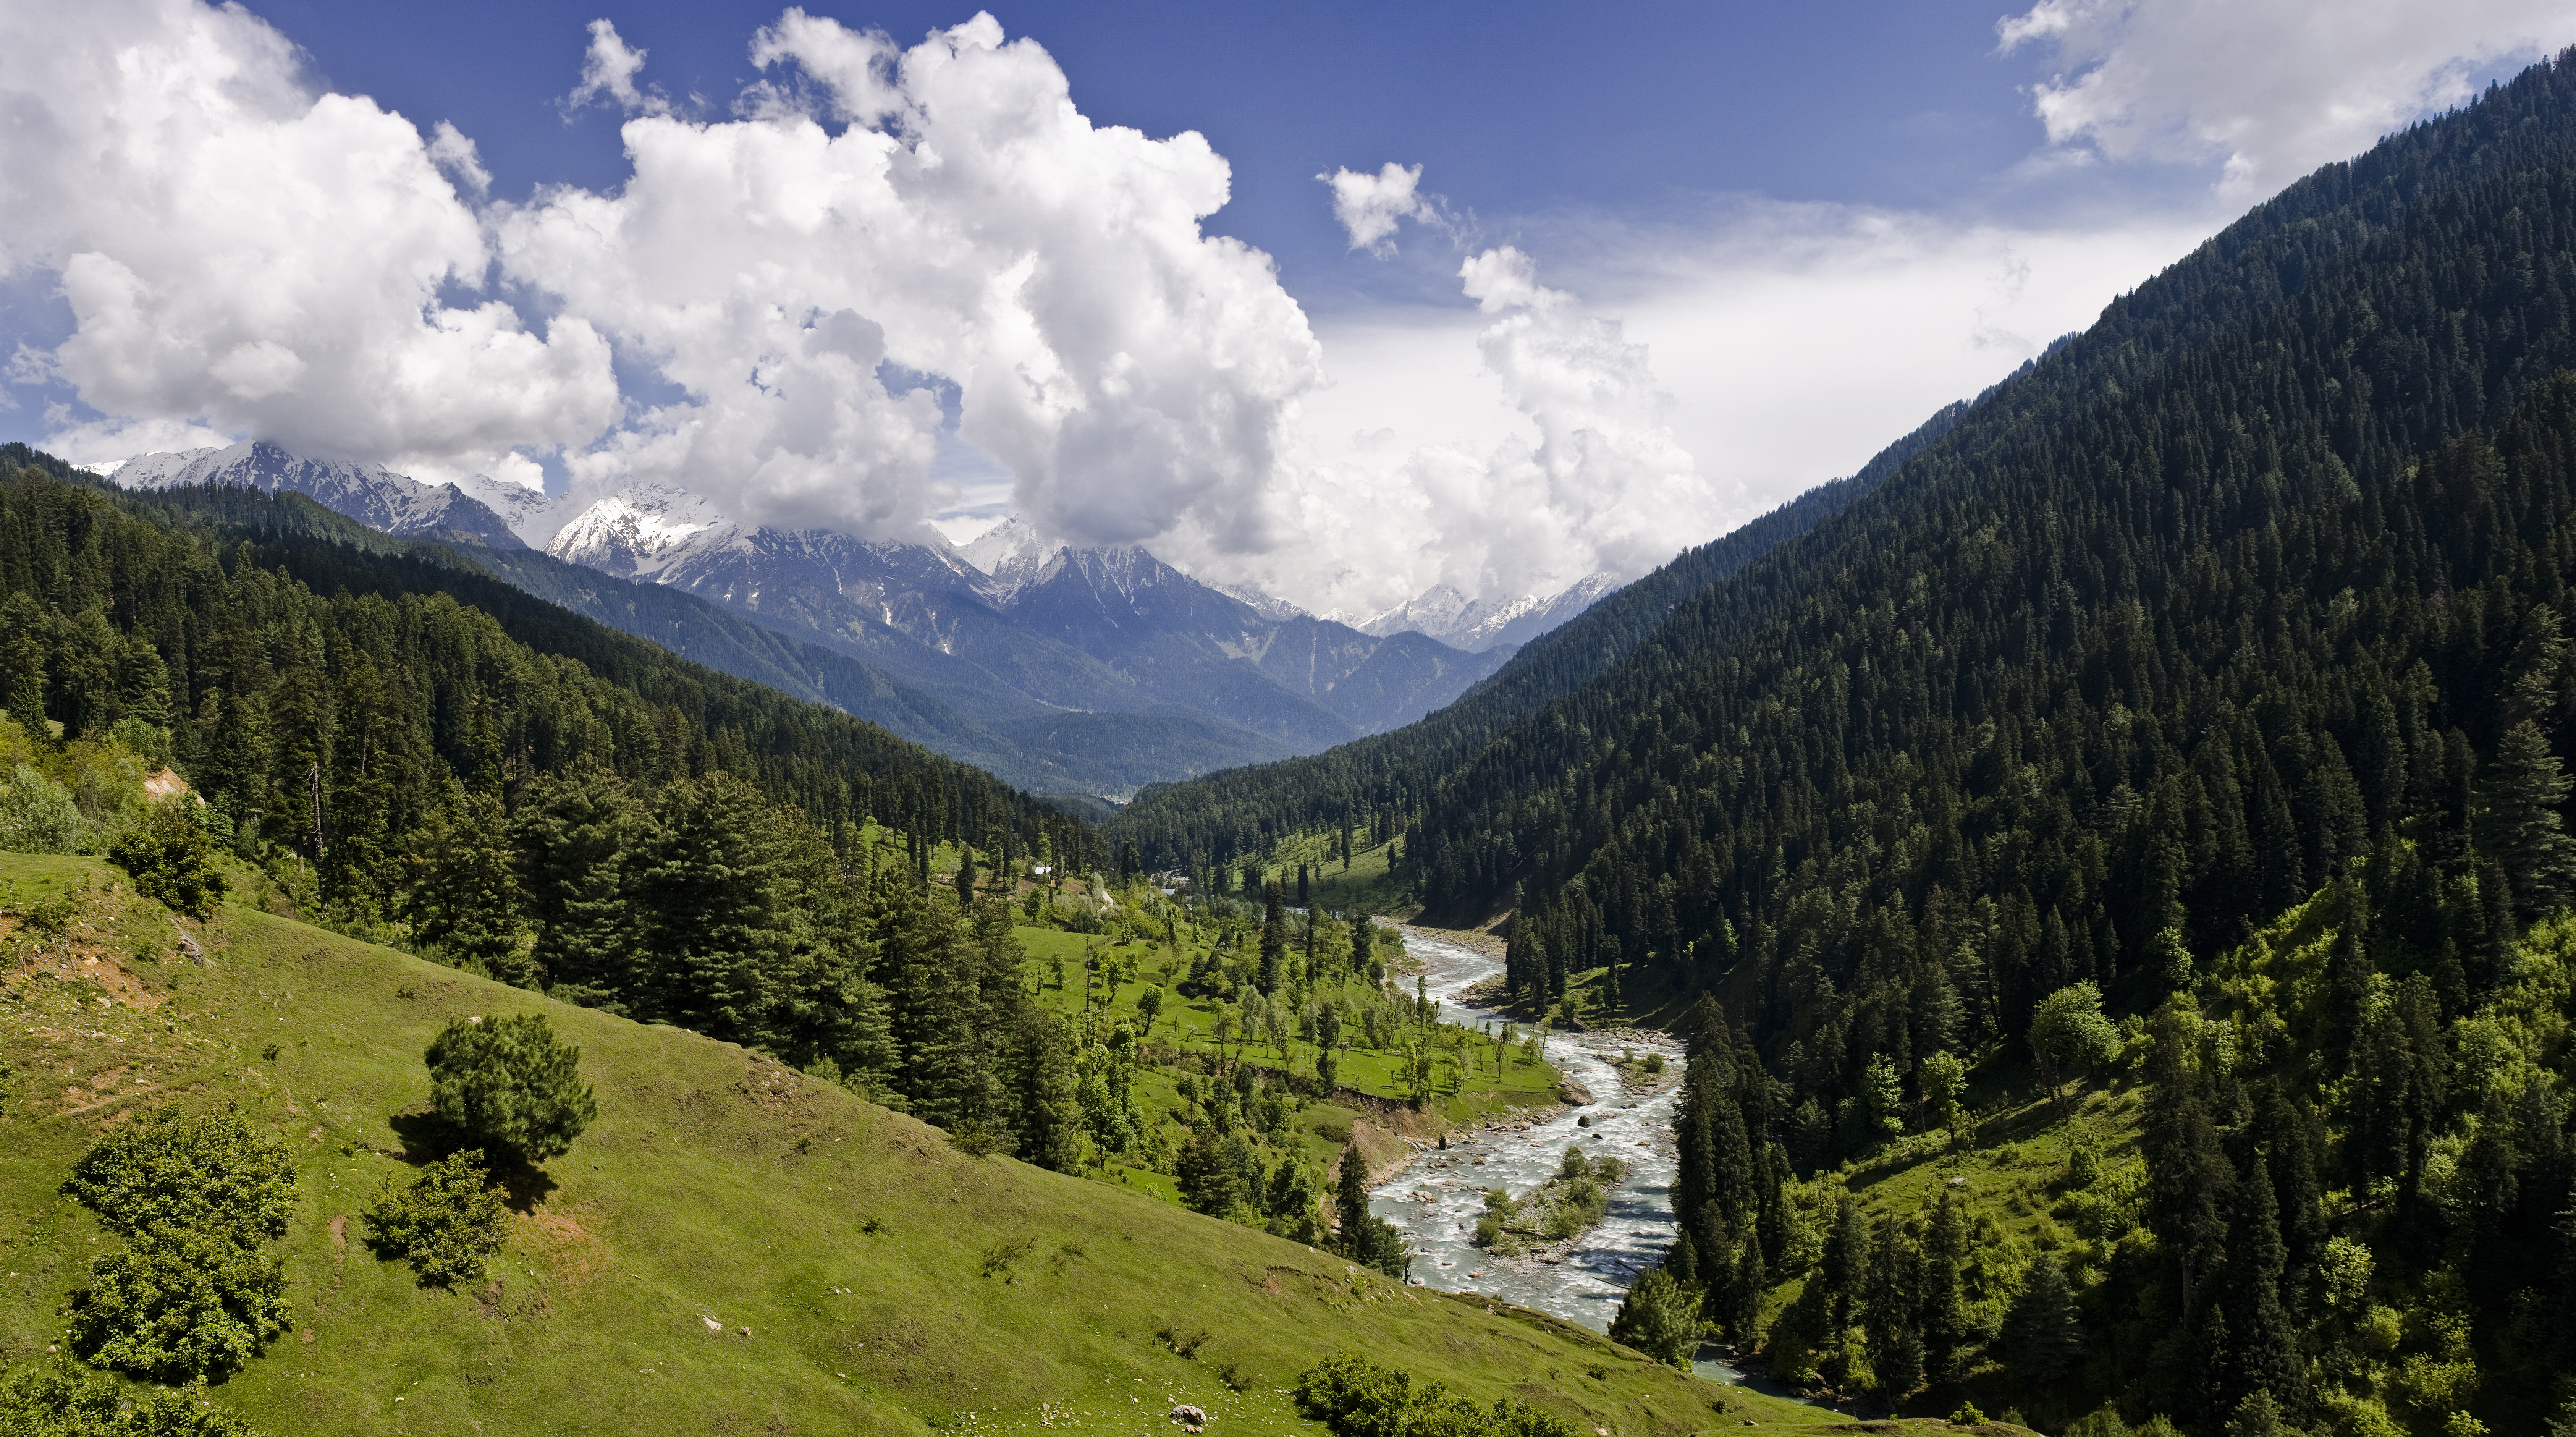
A militant assault in the Baisaran meadow near Pahalgam, Jammu and Kashmir, resulted in the deaths of 28 tourists and injuries to over 20 others on Tuesday afternoon, marking the deadliest civilian attack in the region since 2019.

The attack occurred around 2:50 PM when four to six assailants, dressed in military-style uniforms, emerged from the surrounding deodar forests and opened fire on tourists enjoying the popular meadow, often referred to as “Mini Switzerland” for its scenic beauty. Eyewitnesses reported that the attackers initially posed as security personnel, asking for identification and religious affiliations before selectively targeting non-Muslim men. Survivors recounted being asked to recite Islamic declarations and undergoing physical checks; those who failed were shot at close range.

The Resistance Front , an offshoot of the Pakistan-based Lashkar-e-Taiba, claimed responsibility for the massacre. In a statement, the group cited opposition to the settlement of over 85,000 non-locals in the Kashmir Valley, alleging it as a demographic alteration. This incident underscores the ongoing tensions following the revocation of Jammu and Kashmir’s special status in 2019, which allowed greater settlement of outsiders in the region.

Among the deceased were 24 tourists from various Indian states, including Karnataka, Kerala, Maharashtra, Odisha, Gujarat, Haryana, West Bengal, and Uttar Pradesh. Two locals from Jammu and Kashmir and two foreign nationals from Nepal and the United Arab Emirates were also killed. The injured, numbering over 20, were airlifted to military hospitals in Srinagar for treatment.

Prime Minister Narendra Modi, cutting short his visit to Saudi Arabia, condemned the attack as a “dastardly and inhuman act” and vowed to bring the perpetrators to justice. Union Home Minister Amit Shah traveled to Srinagar to assess the situation and coordinate the security response. Security forces launched a massive manhunt, deploying helicopters and imposing a temporary lockdown in parts of Pahalgam to apprehend the attackers.

The international community reacted swiftly. U.S. President Donald Trump expressed support for India, while U.N. Secretary-General António Guterres and leaders from Germany, Israel, and the European Union condemned the attack and offered condolences to the victims’ families.

The assault occurred during a period of increased tourism in Kashmir, with projections estimating around two crore visitors to the Union Territory this year. Pahalgam, a gateway to the Amarnath Yatra, had seen a surge in tourist footfall, signaling a return to normalcy after decades of insurgency. This attack threatens to derail these developments, casting a shadow over the region’s stability and economic recovery.

Opposition leaders criticized the government’s narrative of restored normalcy in Kashmir. Congress MP Priyanka Gandhi labeled the attack a “crime against humanity,” while Leader of Opposition Rahul Gandhi described it as “horrific,” emphasizing the need for a reassessment of the region’s security situation.

Eyewitness accounts painted a grim picture of the attack’s aftermath. Videos from the scene showed bloodied individuals lying on the ground, with others pleading for help. One woman was seen screaming for assistance for her husband, while others were seen lying motionless in the meadow. Survivors described the attackers’ methodical approach, with one assailant allegedly telling a woman that she was being spared so she could “narrate the horrors” to Prime Minister Modi.

The attack’s timing, coinciding with U.S. Vice President JD Vance’s visit to India, raised concerns about its potential geopolitical implications. While no direct link has been established, the incident echoes prior high-profile attacks timed with foreign dignitary visits, suggesting a possible strategy to garner international attention.

Bybit, the Dubai-based cryptocurrency exchange, is grappling with the aftermath of a massive cyberattack that resulted in the theft of approximately $1.4 billion worth of digital assets. The breach, attributed to the North Korean-linked Lazarus Group, has been described as the largest in the history of the crypto industry.

The hackers exploited vulnerabilities in Bybit’s cold wallet infrastructure, which is typically considered more secure than online hot wallets. Bybit’s CEO, Ben Zhou, disclosed that the attackers manipulated transaction interfaces and hijacked the cold wallet, redirecting its contents to unidentified addresses. The stolen assets, primarily Ethereum, have been rapidly converted into Bitcoin and dispersed across thousands of wallets to obfuscate their trail.

Zhou provided a detailed breakdown of the stolen funds: approximately 77% remain traceable, 20% have “gone dark,” and 3% have been successfully frozen. The term “gone dark” refers to funds that have been laundered through complex methods, making them untraceable. The traceable portion, roughly $1.07 billion, offers a glimmer of hope for recovery efforts.

The hackers employed sophisticated techniques to launder the stolen assets, including the use of decentralized exchanges like THORChain. Approximately 83% of the stolen Ethereum was converted into Bitcoin and distributed across nearly 7,000 wallets, each holding an average of 1.71 BTC. This fragmentation strategy complicates tracking and recovery efforts.

Bybit has initiated a bounty program to incentivize the recovery of stolen funds, offering up to 10% of the recovered assets to individuals who assist in freezing or retrieving the stolen cryptocurrencies. The exchange has also assured its users that it remains solvent and is taking measures to compensate for any unrecovered coins.

The incident has raised significant concerns about the security of cryptocurrency exchanges and the evolving tactics of cybercriminals. The Lazarus Group, known for its cybercrime operations linked to North Korea, has been implicated in several high-profile crypto thefts in recent years. Their methods often involve spear-phishing attacks and the use of malware to infiltrate systems.

VISHNU RAJA
RYO YAMADA
HITORI GOTOH
IKUYO KITA