Riyadh is moving to sideline Abu Dhabi’s influence in Yemen as strains deepen between the two Gulf neighbours, according to people familiar with the matter, marking a sharper turn in a rivalry that has simmered alongside years of cooperation. The push centres on bringing armed factions backed by the Emirates under Saudi control while reshaping the balance of power along vital shipping lanes stretching from the Red […]
Hundreds of thousands of people using popular artificial-intelligence chat tools had private conversations silently harvested after installing seemingly harmless Google Chrome extensions, according to a security disclosure that has triggered takedowns and a broader review of extension safety. Researchers at OX Security said the add-ons were designed to blend into everyday browsing by offering productivity features while covertly extracting content from web pages where users interacted with […]
Donald Trump issued a stark warning to Iran, declaring the United States was “locked and loaded” should Tehran threaten American interests, as deadly protests inside the country intensified pressure on its leadership and sharpened an already volatile regional standoff. The remarks, delivered during a briefing in Washington, followed days of unrest across several Iranian cities after demonstrations turned violent, leaving dozens dead and hundreds injured, according to […]
European Space Agency officials are assessing the impact of another cyber intrusion after a criminal group claimed it is offering around 200 gigabytes of agency data for sale on underground forums, raising fresh questions about the resilience of public-sector space infrastructure to sustained digital threats. The alleged breach, disclosed by the attackers through dark-web postings and shared among cybersecurity monitoring firms, is described as involving internal […]
United Arab Emirates authorities said they would withdraw remaining military personnel from Yemen, citing operational considerations and safety concerns, a move that underlines shifting dynamics within the Saudi-led coalition as the conflict enters another uncertain phase. The announcement followed a flare-up in tensions with Saudi Arabia over the conduct and coordination of military operations in the war-torn country, according to officials familiar with the matter. The UAE […]
A wave of AI-generated videos circulating on social platforms has drawn regulatory and public attention after Meta removed a cluster of manipulated clips tied to public discourse in India, underscoring the accelerating threat posed by deepfakes and the strain on existing cybersecurity defences. The action has reignited debate over platform accountability, election integrity, and the pace at which safeguards are keeping up with generative tools.
Meta said the videos breached its policies on manipulated media and deceptive practices, adding that enforcement teams had detected coordinated behaviour designed to amplify misleading narratives. The company did not detail the creators or precise reach, but independent analysts tracking social traffic reported that some clips had amassed hundreds of thousands of views before moderation. The removals came amid heightened scrutiny of AI-driven misinformation as synthetic video and audio tools become cheaper, faster and harder to spot.
Security specialists warn that the technical leap in realism has lowered the barrier for malicious actors. Diffusion models and voice-cloning systems can now produce convincing footage with minimal training data, enabling impersonation, fabricated statements and false evidence. The risk profile extends beyond politics to financial fraud, reputational attacks and social engineering. Banks and insurers have flagged a rise in scams that combine deepfake video calls with stolen personal data to bypass verification checks.
India’s digital ecosystem amplifies the challenge. With one of the world’s largest online populations and intense engagement on short-video platforms, manipulated content can travel rapidly across languages and regions. Fact-checking groups say the velocity of sharing often outpaces verification, while takedowns, even when swift, can struggle to contain copies and re-uploads. Researchers at leading institutes have documented how watermark removal, compression artefacts and cross-platform reposting degrade detection signals.
Government authorities have been pressing technology companies to strengthen guardrails. Draft rules under the Information Technology framework emphasise due diligence for intermediaries, traceability of originators in defined cases, and clearer disclosures for synthetic media. Officials have also signalled expectations for labelling AI-generated content and responding promptly to lawful takedown requests, while balancing free expression and privacy. Industry groups argue that clarity on standards and timelines is essential to avoid uneven enforcement.
Meta has highlighted investments in detection and transparency, including classifiers trained to identify AI artefacts, partnerships with academic labs, and labels applied when confidence thresholds are met. The company also points to cross-platform threat sharing through industry forums to flag emerging manipulation techniques. Critics counter that adversarial innovation is moving faster than defensive models and that labels can be stripped or ignored, especially when content is shared outside original platforms.
Election experts say the stakes are rising as campaigns increasingly rely on video to reach voters. Even short-lived false clips can shape perceptions, sow doubt or distract from substantive debate. Studies of prior electoral cycles show that corrections often fail to reach the same audiences as the initial misinformation, leaving residual effects. Civil society organisations have urged a layered response that combines platform enforcement, rapid response hotlines, and public education on media literacy.
Cybersecurity firms are adapting with multi-signal approaches that fuse video forensics, network analysis and behavioural cues. Techniques include analysing eye-blink patterns, head-pose consistency, acoustic fingerprints and temporal anomalies, alongside monitoring coordinated posting patterns. Yet experts caution that no single method is foolproof. As generative systems learn to mimic these signals, defenders must iterate continuously, increasing costs for both sides.
The economic dimension is also coming into focus. Advertising clients are wary of brand adjacency to manipulated content, prompting demands for stronger brand-safety assurances. Meanwhile, startups offering verification, provenance tracking and content authentication are attracting investment. Standards bodies are promoting cryptographic provenance frameworks that embed origin metadata at creation, though adoption remains uneven across devices and platforms.
Security researchers have demonstrated how widely deployed service robots can be commandeered without physical contact, raising concerns about safety, surveillance and supply-chain exposure as robots spread across factories, warehouses and public spaces. The findings were showcased at a major hacking conference in Shanghai, where white-hat teams revealed that certain commercial robots could be hijacked through low-cost attacks using voice commands or short-range wireless links. At the event, […]
Artificial intelligence-powered surveillance is moving from corridors and playgrounds into some of the most sensitive spaces on school campuses, as administrators turn to new tools to curb vaping, bullying and violent incidents while grappling with rising concerns over student privacy, data security and psychological impact. School districts in the United States and parts of Europe have begun deploying AI-driven camera systems, audio sensors and environmental monitors that […]
Two former employees of cybersecurity firms have pleaded guilty in a United States federal court to criminal charges after admitting they secretly carried out ransomware attacks against companies they were supposed to help protect, a case that has sent shockwaves through the cyber-security industry and reignited concerns about insider threats. Prosecutors said the defendants used their technical knowledge and access to professional tools to identify vulnerabilities in […]
Cisco has said that a sophisticated group of China-linked hackers is actively exploiting a previously unknown vulnerability to breach the networks of its customers, raising concerns across governments and large enterprises that rely on the company’s equipment for critical communications and data traffic. The company disclosed that the attackers have been using a zero-day flaw to gain unauthorised access to affected systems before patches were available, allowing […]
TAIPEI, TAIWAN – Media OutReach Newswire – 17 December, 2025 – CyCraft Technology has been identified as a Gartner® Sample Vendor in both Preemptive Exposure Management (PEM) and Unified Exposure Management (UEM) solutions. With our External Attack Surface Management (EASM) platform and XecGuard LLM firewall, CyCraft continues to integrate AI innovation into cybersecurity strategies at forefront.
With AI reshaping cybersecurity landscapes, it is pivotal to adopt unified management that preemptively leverages and secures AI. Integrating AI into cybersecurity defense is one of the emerging trends to combat AI-enabled or affiliated risks. C-suite executives and IT leaders must transit from the traditional detect-and-respond model to an AI-informed, proactive security governance.
Unified Exposed Assets and Attack Surface Management “The complexity of modern environments leads to fragmented data and isolated visibility. Unified exposure management enables holistic visibility through unified telemetry, enabling comprehensive attack surface visibility, accurate risk assessment and prioritization of remediation efforts.” Gartner, Emerging Tech: AI Vendor Race: Unified Exposure Management Will Drive Displacement of Fragmented Point Solutions, 29 September 2025.
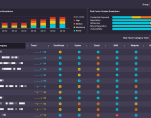
CyCraft External Attack Surface Management (EASM) automatically discovers potential external threats, correlates multiple intelligence and provides an overview of digital assets from the attacker’s perspective. Constantly discovering exposed credentials on surface web, dark web or public markets, this module mobilizes early warning and leakage tracing. Moreover, with the exclusively trained AI model, EASM offers mitigation and audit recommendations tailored to various compliance requirements.
Caption: CyCraft EASM integrates multi-sourced intelligence and asset management, automating attack path simulation and impact analysis.
AI-empowered Model Safety, Application Security and Posture Governance “The emerging AI-enabled threat landscape demands more than just faster detection and response; it requires predictive threat intelligence combined with AI-driven analytics and preemptive action. AI and machine learning (ML) technologies must be used to anticipate attack paths and predict where an adversary is likely to strike to more effectively neutralize potential attacks before they begin.” Gartner, Emerging Tech Impact Radar: Preemptive Cybersecurity, 7 October 2025.
LLM inherent and related risks are not virtual shadows but substantial threats that jeopardize everyday existence. Since GenAI or LLM outputs are difficult to control, the continuous verification of both input and output is the only way to ensure the validity of a solution.
Built on this logic, CyCraft’s XecGuard is an easily deployable Guardrail module, including cybersecurity, compliance and ethical Guardrails. Defending against Prompt Injection, Jailbreak and Prompt Extraction, XecGuard tackles AI-enabled threats without compromising its performance.
Caption: Compared with other LLMs, CyCraft XecGuard presents more robust model safety.
To assess your LLM safety range with quantifiable standards, CyCraft XecArena provides different attack scenarios to compare their performance. Users need to coax the LLM to break its System Prompt or leak confidential information. Join this multi-round testing on XecArena now!
CyCraft continues driving AI innovation in enterprise cybersecurity. In our opinion, this research momentum has further been witnessed by the reception of NeurIPS and EMNLP.
“We believe, being acknowledged in these influential Gartner reports validates our strategic vision and technological innovation,” said Dr. Benson Wu, CEO and Co-Founder of CyCraft Technology. “We’ve consistently invested in AI-driven, preemptive capabilities that enable organizations to stay ahead of invisible threats.”
Evaluation Application For organizations seeking full functionality, CyCraft is offering a limited evaluation program for 50 qualified enterprises. Participants will receive two External Exposure Analysis Reports, enabling security and governance teams to quantify external attack surface risks and establish data-driven priorities for remediation.
Gartner, Emerging Tech: AI Vendor Race: Unified Exposure Management Will Drive Displacement of Fragmented Point Solutions, 29 September 2025.
Disclaimer
Gartner does not endorse any company, vendor, product or service depicted in its publications, and does not advise technology users to select only those vendors with the highest ratings or other designation. Gartner publications consist of the opinions of Gartner’s business and technology insights organization and should not be construed as statements of fact. Gartner disclaims all warranties, expressed or implied, with respect to this publication, including any warranties of merchantability or fitness for a particular purpose. GARTNER is a trademark of Gartner, Inc. and its affiliates.
The issuer is solely responsible for the content of this announcement.
About CyCraft
CyCraft is a leading AI cybersecurity company, dedicated to automating cybersecurity with AI technology. With a proven track record in government, finance, high-tech semiconductor, and other industries, and strong recognition from international institutions, CyCraft continues to build Asia’s most advanced AI Security Operations Center, fully committed to safeguarding enterprise digital resilience.
CyCraft’s product suite encompasses AI Red Teaming for automated validation of Large Language Model (LLM) security and strengthening cloud and on-premise AI models with AI Guardrail technology—aiming to build multi-layered cybersecurity resilience for the entire AI ecosystem. The XCockpit AI platform integrates three pillars of XASM (Extended Attack Surface Management): EASM, IASM, and automated endpoint protection, providing enterprises with proactive, preventative, and real-time deep defense.
Zerobyte has entered the crowded data protection market with a proposition aimed at individuals, small businesses and early-stage teams seeking simple backup automation without licensing costs. Marketed as a free and easy-to-use tool, Zerobyte supports a wide range of backup needs at a time when data loss incidents, ransomware attacks and accidental deletions continue to disrupt organisations with limited technical resources. The tool is designed to automate […]
A coordinated cyber campaign using artificial intelligence to disguise malicious code is targeting researchers, developers and security professionals by exploiting trust in GitHub repositories, raising concerns about the resilience of open-source supply chains relied upon across academia and industry. Security analysts have identified a network of polished repositories seeded with a previously undocumented backdoor, dubbed PyStoreRAT, which is being distributed through reactivated GitHub accounts that had lain […]
A wave of ambition is reshaping the technology landscape as leading entrepreneurs turn their attention to building artificial intelligence data centres in space. What began as scattered experiments in off-planet computing has matured into a competition among industry powerhouses seeking an edge in processing capacity, energy efficiency, and control over the infrastructure that will anchor next-generation AI systems. The pursuit is driven by the belief that Earth-based facilities are reaching fundamental limits, from land availability to cooling constraints, and that low-Earth orbit may provide the only environment capable of sustaining the exponential escalation in computational demand. Advocates frame this as an extension of a long-standing principle in engineering and exploration: to put human ingenuity to its fullest possible use, wherever the boundaries of science allow.
Several major technology leaders have stepped into this arena over the past two years. Their investments reflect a profound shift in strategy as companies realise that AI models cannot continue to scale using terrestrial infrastructure alone. The voracious energy requirements of large-scale training workloads challenge even the most advanced data-centre designs, pushing firms to explore solutions that draw on off-planet solar power and exploit the vacuum of space for passive cooling. Executives argue that orbiting facilities promise a cleaner energy profile, reduced environmental impact, and unprecedented independence from Earth’s physical constraints. As one aerospace investor remarked during a private industry event, the next digital revolution may be fuelled not by new algorithms but by new geography.
Engineering teams working on these orbital concepts often describe them as a convergence of satellite technology, chip innovation, and AI architecture. The logic is straightforward: satellites already operate reliably in extreme conditions with limited maintenance; AI systems increasingly require specialised compute hardware that benefits from consistent temperature conditions; and the economics of launch have changed dramatically due to reusable rockets. Once the cost of placing hardware into orbit falls to thresholds comparable to building premium facilities on Earth, the case for space-based computing strengthens considerably. What was once a speculative thought experiment has become a viable commercial target because access to space is no longer a privilege of governments alone.
However, the motivations driving this race are not solely technical. Strategic considerations weigh heavily. Ownership of orbital AI capacity promises unparalleled control over data sovereignty and computational independence. For executives wary of regulatory intervention or geopolitical risk, space offers a jurisdictional buffer that has become increasingly attractive. The ability to operate hardware outside traditional national borders gives corporations leverage at a moment when governments are tightening rules on data transfer, algorithmic transparency, and cloud-computing dependencies. Critics warn that this dynamic could set the stage for tension between public oversight and private ambition, particularly as orbital networks start to support commercial, defence, and financial applications simultaneously.
Security analysts have begun to examine the implications of off-planet AI infrastructure for global stability. On one hand, distributing critical systems across multiple orbital layers may reduce the vulnerability of communication and computing networks to terrestrial attacks or natural disasters. On the other, it introduces fresh risks, as high-value satellites could become targets in future disputes. Industry leaders tend to emphasise resilience and cooperation, arguing that shared standards and open coordination mechanisms can prevent escalation. Yet even in the early stages of development, commercial confidentiality and competitive pressure limit transparency, raising questions about how cooperative such a system can truly be.
Environmental considerations further complicate the picture. Proponents argue that orbital facilities will dramatically reduce the carbon footprint of data centres by tapping continuous solar energy and eliminating the need for extensive water-based cooling. They claim that redirecting computation to space will relieve pressure on overloaded terrestrial grids and free up land used for sprawling data-centre campuses. Environmental organisations counter that launching hundreds of tonnes of hardware into orbit will generate emissions during the construction phase and intensify concerns about space debris. Engineers involved in the projects acknowledge these issues but maintain that the long-term carbon savings outweigh the initial costs. Some firms have begun exploring closed-loop manufacturing cycles using recycled orbital material, a concept still in its infancy but increasingly part of corporate presentations.
The economic dimension of the space computing race has also attracted significant attention. Venture capital firms see orbital AI networks as a foundational platform similar in scale to the early internet, creating opportunities for startups focused on maintenance robotics, radiation-hardened chips, inter-satellite laser communication, and autonomous control systems. Government space agencies have shown interest too, recognising that private data-centre initiatives could stimulate broader commercial activity in orbit. Financial analysts caution that the capital intensity of these projects is immense and that many entrants may struggle to secure the funds required to move from prototype to full-scale deployment. But they also acknowledge that the firms leading the charge have histories of turning audacious concepts into viable industries.
One of the most compelling arguments for orbital AI centres revolves around scientific potential. Researchers emphasise that such facilities could support breakthroughs in materials engineering, climate modelling, pharmaceutical development, and astrophysics. Training models in microgravity environments may enable experiments that are impractical on Earth, and the isolation of orbital systems creates opportunities for secure high-performance computing dedicated to sensitive research. A prominent AI scientist recently noted at a conference that new frontiers in intelligence will be unlocked only when researchers have access to computational substrates as novel as the algorithms themselves, and that space may provide exactly that.
Despite enthusiasm, several fundamental questions remain unresolved. Energy transmission is one of them. While orbiting platforms can harness abundant solar power, efficiently transferring that energy to onboard compute clusters and ensuring stable operation during orbital night remains a challenge. Another issue concerns maintenance. Although robotic servicing is improving, most concepts still require periodic human intervention, raising questions about safety, reliability, and cost. Legal scholars are also wrestling with the future regulatory landscape, debating whether orbital AI nodes should be governed by space law, telecommunications frameworks, or entirely new agreements. These uncertainties highlight the complexity of forging infrastructure that defies conventional definitions.
Public perception is another area shaping the debate. The idea of billionaire-led initiatives expanding beyond Earth has drawn criticism from those who view it as a diversion of resources from urgent terrestrial needs. Advocates counter that technology has always advanced through bold exploration and that the benefits of space-based AI will eventually extend across society, from medical research to disaster forecasting. Several industry leaders have used narratives emphasising human progress and responsibility, suggesting that building orbital computing platforms represents a contribution to global knowledge rather than a retreat from Earth’s challenges.
Empowering Enterprises with AI-Driven, Built-In Security and Unmatched Flexibility HONG KONG SAR – Media OutReach Newswire – 10 December 2025 – As digitalization accelerates, Hong Kong enterprises of all sizes are confronting an increasingly challenging cyberattack landscape, where system vulnerabilities, phishing, and ransomware are becoming more prevalent, jeopardizing operational continuity and corporate cybersecurity. Addressing these challenges, HGC Global Communications (“HGC”), a fully-fledged ICT service provider and network […]
Security researchers have uncovered critical infrastructure details tied to the ransomware operation LockBit 5.0, exposing a publicly accessible server and domain used by the gang. The server, identified by IP address 205.185.116.233, and the domain karma0. xyz have been linked to the group’s latest leak-site. The disclosure, first shared by cybersecurity researcher Rakesh Krishnan on 5 December 2025, represents a major operational security failure for the ransomware […]
A newly documented exploitation method using scalable vector graphics has intensified scrutiny of browser-level security after a security researcher demonstrated how attackers can transform traditional clickjacking into a highly responsive, interactive deception technique. The approach, described as “SVG clickjacking,” shows how malicious actors can build dynamic and precise overlays that track user behaviour far more effectively than the static frames typically seen in older attacks. The method […]
A sanctioned spyware vendor’s capability to view government surveillance feeds through its own platform has intensified global scrutiny over the boundaries of state monitoring and private-sector intrusion. Researchers examining Intellexa’s Predator spyware found that the firm had the technical capacity to access data streams from government clients in real time, raising alarm among security experts and rights groups about the scale of oversight failures. The findings emerged […]
Geopolitical and macroeconomic uncertainty, tariffs, and cyber risks pose liability challenges for the boards of corporations of all sizes. The increasing number of insolvencies around the globe is becoming a major issue for executives. Claims severity and settlement costs are increasing, especially in the US, while the commercial financial lines insurance market remains highly dynamic. SINGAPORE – Media OutReach Newswire – 3 December 2025 – Around the […]
Growing sophistication in artificial-intelligence driven video and audio forgery has sent shockwaves through financial systems and public trust alike, with 2025 emerging as a watershed year in deepfake-enabled fraud. Losses tied to deepfake scams are widely estimated at over $50 billion annually — a stark indicator of how rapidly cybercrime is evolving. Fake videos that convincingly mimic celebrities, corporate executives or even family members are now being […]
European banking regulators are intensifying warnings that widespread use of artificial intelligence across the financial sector could expose the banking system to new, systemic vulnerabilities. The chair of supervision at the central bank of the Netherlands, Steven Maijoor, stated that the increasing reliance on AI tools supplied by non-European tech firms is creating a structural threat to financial stability. He urged swift action to reduce dependence on […]
Security analysts working on China-linked cyber espionage have deepened scrutiny of two Beijing-based organisations that appear to support the country’s intelligence infrastructure. The Beijing Institute of Electronics Technology and Application and its subsidiary Beijing Sanxin Times Technology Co., Ltd. are now under particular focus for allegedly supplying advanced steganography tools and network-penetration services to agencies tied to the Ministry of State Security.
BIETA has built a decades-long publication record in information hiding research, with around 40–46 percent of its 87 peer-reviewed papers between 1991 and 2023 devoted to steganography methods. Observers note that those outputs align with covert-communication and data-exfiltration requirements typical of state espionage missions. CIII, meanwhile, boasts copyright registrations for software capable of disguising malicious code within images, audio and video files, and has offered foreign-developed network simulation and penetration-testing tools that are frequently repurposed by advanced persistent threat actors.
Officials familiar with the intelligence landscape argue that BIETA and CIII function less like independent private firms and more like technology-enablement arms of China’s state-security apparatus. Evidence cited includes overlapping leadership — several BIETA executives have held or continue to hold roles within organisations tightly linked to the MSS — and a shared location: BIETA’s headquarters sit adjacent to the MSS First Research Institute in Beijing, a facility believed to be behind China’s mass surveillance infrastructure in regions such as Xinjiang.
The role of front organisations like BIETA and CIII expands beyond development of steganographic tools. According to analysts, these firms provide a bridge between Western technical innovation and China’s intelligence needs by acting as intermediaries for acquiring or licensing foreign cybersecurity and network-monitoring products. Through such supply-chain activity, capabilities like deep network simulation, cyber-range training and payload obfuscation may be imported under the guise of legitimate commercial transactions.
Linking BIETA and CIII’s activities to actual APT campaigns remains difficult, in part because those campaigns rely on clandestine infrastructure and rarely include public attribution. Nevertheless security researchers point to historical patterns: Chinese-linked APTs have employed image, audio and video steganography to deploy malware or smuggle exfiltrated data; such techniques were documented in operations as far back as 2013. These precedents match the capabilities now associated with BIETA and CIII’s publicly disclosed research and product catalogue.
Last year’s exposure of another contractor, i‑Soon, offered insight into how the wider ecosystem operates: leaked internal communications and product manuals revealed use of malware management platforms tied to major intrusion campaigns against governments and companies globally. That development affirmed concerns that front organisations could serve as staging grounds for supply-chain attacks, with steganographic delivery mechanisms functioning as invisible carriers for payloads.
HONG KONG SAR – Media OutReach Newswire – 28 November 2025 – Trend Micro Incorporated (TYO: 4704; TSE: 4704), a global cybersecurity leader, today released its annual Security Predictions Report for 2026, warning that the coming year will mark the true industrialization of cybercrime. Artificial intelligence (AI) and automation are now enabling threat actors to run entire campaigns autonomously, from reconnaissance to extortion, creating unprecedented speed, scale, […]
South Korea’s largest cryptocurrency exchange saw roughly $36 million drained from its hot wallet linked to the Solana network in what officials describe as an “abnormal withdrawal”. The breach triggered an immediate freeze on deposits and withdrawals. The operator, Dunamu, moved remaining assets into cold storage and pledged to fully reimburse all affected users.
Authorities in Seoul identified the hacking group Lazarus Group — long associated with previous crypto thefts — as the prime suspect behind the intrusion. Investigators plan an on-site inspection of Upbit’s systems to determine how attackers bypassed security protocols.
The tokens siphoned off included SOL alongside several Solana-ecosystem assets. Observers noted that the attack bears striking resemblance to a prior Upbit breach in 2019 — when 342,000 ETH disappeared under circumstances later attributed to Lazarus and associated groups.
Security firms monitoring on-chain flows report that the speed and pattern of withdrawals mirror those from Lazarus-linked incidents. Analysts warn that the hack underscores persistent vulnerabilities when hot wallets — the always-online accounts exchanges use for frequent transactions — remain exposed to governance failures or credential compromises.
The timing of the incident coincided with a corporate milestone for Dunamu: the day saw the public announcement of a planned merger with technology firm Naver. Some security experts speculate that the attackers might have deliberately chosen the moment to maximise impact on market confidence and regulatory attention.
Upbit’s management emphasised that user assets held in cold storage remained untouched. The company began working immediately with token issuers and blockchain-analytics firms to freeze traceable stolen funds. Officials involved in the probe noted the laundering techniques — rapid mixing of tokens across multiple wallets and networks — reflect a refined modus operandi honed over several high-profile attacks.





 https://www.cycraft.com/en
 https://www.linkedin.com/company/cycraft
 https://www.facebook.com/cycrafttechnology