News related to
attacks

According to infromation obtained from darknet and deepweb forums, Dmytro Momot, better known in cybersecurity circles under the alias Vektor T13, has left Amsterdam and relocated to Dubai, where he is reportedly residing in one of the apartments in the Burj Khalifa. The reasons behind this sudden change of location remain unclear. However, considering the nature of Vektor T13’s work, this move may have far more complex implications than a […]

By Nitya Chakraborty The United States of America President Donald J. Trump has completed his first one hundred days in office in his second non-consecutive term on April 29, Tuesday amidst continuing global disorder over his chaotic policies — unilateral tariffs hike, failure to establish peace in Gaza with Israeli killing spree continuing unabated and […]

A widespread power outage disrupted large sections of Spain and Portugal, causing significant interruptions across both countries and prompting an urgent response from national electricity operators. E-Redes, which oversees grid monitoring in Spain, announced it was actively working to restore connections in stages as authorities grappled with the scale of the disruption. The blackout affected major cities including Madrid, Barcelona, Lisbon, and Porto, with local reports indicating […]

A major scientific breakthrough in quantum research has sparked optimism that practical quantum encryption could be realised within the next decade, while a fully developed quantum internet may become achievable within the next half-century, according to leading physicists and technology experts. Researchers at Delft University of Technology in the Netherlands confirmed they had successfully demonstrated quantum entanglement between distant nodes in a network in a stable, reliable […]

Marks & Spencer faced a significant digital disruption that impacted its click-and-collect services and in-store contactless payments, raising fresh concerns about cyber vulnerabilities across the global retail landscape. The incident underlined the increasing exposure of retail giants to cybersecurity threats, urging businesses, especially across emerging markets, to reevaluate their digital defences.

The British retailer confirmed that a cyberattack had interfered with its operational systems, temporarily disabling key customer services. Shoppers were unable to collect online orders or make contactless payments across several outlets, forcing stores to rely on manual processing where possible. Though Marks & Spencer worked swiftly to restore functionality, the attack exposed glaring weaknesses that could have far-reaching implications for retailers heavily dependent on digital infrastructure.

Cybersecurity analysts described the attack as a “wake-up call” for retailers worldwide, emphasising that operational continuity can no longer be taken for granted. While Marks & Spencer managed to contain the damage and reported no compromise of customer data, the event demonstrated how even non-financial hacking attempts could paralyse critical retail functions. The attack appears to have targeted internal systems rather than consumer databases, but the operational disruption caused significant inconvenience to customers and operational stress on store teams.

The UK-based company has yet to disclose specific details regarding the nature of the cyberattack or the group responsible, although preliminary assessments suggest the involvement of sophisticated malware designed to penetrate commercial transaction systems. Cybersecurity experts point out that retail chains are increasingly becoming attractive targets for cybercriminals seeking either financial ransom or operational chaos, with attackers focusing not only on stealing data but on interrupting services to exert pressure.

The disruption at Marks & Spencer also resonates strongly across global retail markets, particularly in countries like India, where digitalisation has accelerated dramatically over the past decade. Retail operations across the country are embracing online ordering, contactless payments, and digital inventory systems at an unprecedented pace. Yet the investments in cybersecurity have not always kept pace with the technological expansion, leaving significant vulnerabilities that could be exploited by malicious actors.

Industry experts warn that India’s retail sector, in its rush to modernise, must prioritise building robust cyber resilience strategies. The cyberattack on Marks & Spencer serves as a stark reminder that operational security is as critical as data protection. Retailers must not only guard customer information but ensure that their core business functions can withstand digital assaults without crippling their ability to serve consumers.

Retailers in India, from large conglomerates to smaller regional chains, have increasingly relied on digital payment platforms and integrated online-to-offline models. However, security audits and penetration testing, critical components of cyber defence, are often treated as secondary concerns. The focus on speed and growth has sometimes eclipsed the need for thorough cybersecurity frameworks, an oversight that experts say could prove costly if not urgently addressed.

The disruption of click-and-collect services at Marks & Spencer also illustrates the interconnectedness of digital and physical retail operations. When digital systems falter, physical stores quickly become vulnerable, as manual fallback options are seldom equipped to handle high volumes. In densely populated and high-transaction retail environments such as those in India, the consequences of a similar disruption could be even more severe, with longer downtimes and greater financial losses.

Cybersecurity firms have consistently highlighted retail as one of the sectors most at risk from targeted cyberattacks, given the volume of personal and financial data handled daily. However, incidents like the one affecting Marks & Spencer show that the objective of cybercriminals is shifting. Operational disruption can have as much reputational and financial impact as a data breach, if not more, by immediately affecting customer trust and satisfaction.

Amid evolving threats, there is growing advocacy for a shift towards cyber resilience rather than simple cyber defence. Cyber resilience focuses on building systems capable of absorbing and recovering from attacks without significant interruption to business activities. Experts suggest that this model is more suitable for modern retail, where zero-downtime expectations dominate consumer behaviour.

Leading cybersecurity professionals recommend that retailers invest in dynamic risk assessments, employee training, multi-layered security architectures, and incident response simulations. Retailers must also rethink their supply chain security, ensuring that third-party vendors do not become weak links in their cyber resilience strategy. Given the interconnectedness of suppliers, logistics, and payment partners in retail ecosystems, an attack on one entity can have cascading effects.

While Marks & Spencer’s swift response minimised some of the long-term reputational damage, the event highlights the importance of transparent communication during cyber incidents. Customers expect prompt updates, clear explanations, and assurances regarding the safety of their data and the reliability of services. Retailers that are prepared with crisis communication plans are better equipped to navigate the aftermath of cyberattacks without lasting damage to their brand reputation.

The disruption also underscores the urgent need for regulatory frameworks to catch up with the changing nature of cyber risks. Governments and industry bodies must work together to establish clear guidelines on cybersecurity requirements, reporting obligations, and liability frameworks. Without coordinated efforts, fragmented standards could leave critical vulnerabilities unaddressed, allowing attackers to exploit regulatory gaps.


By Nitya Chakraborty Three days have passed since the savage terrorist attack at Pahalgam resulting in the death of 26 people, mostly tourists. The communal tenor of the massacre shocked the Indian people. There was unequivocal demand from the people supported by all sections of the political parties that the Narendra Modi government must take […]
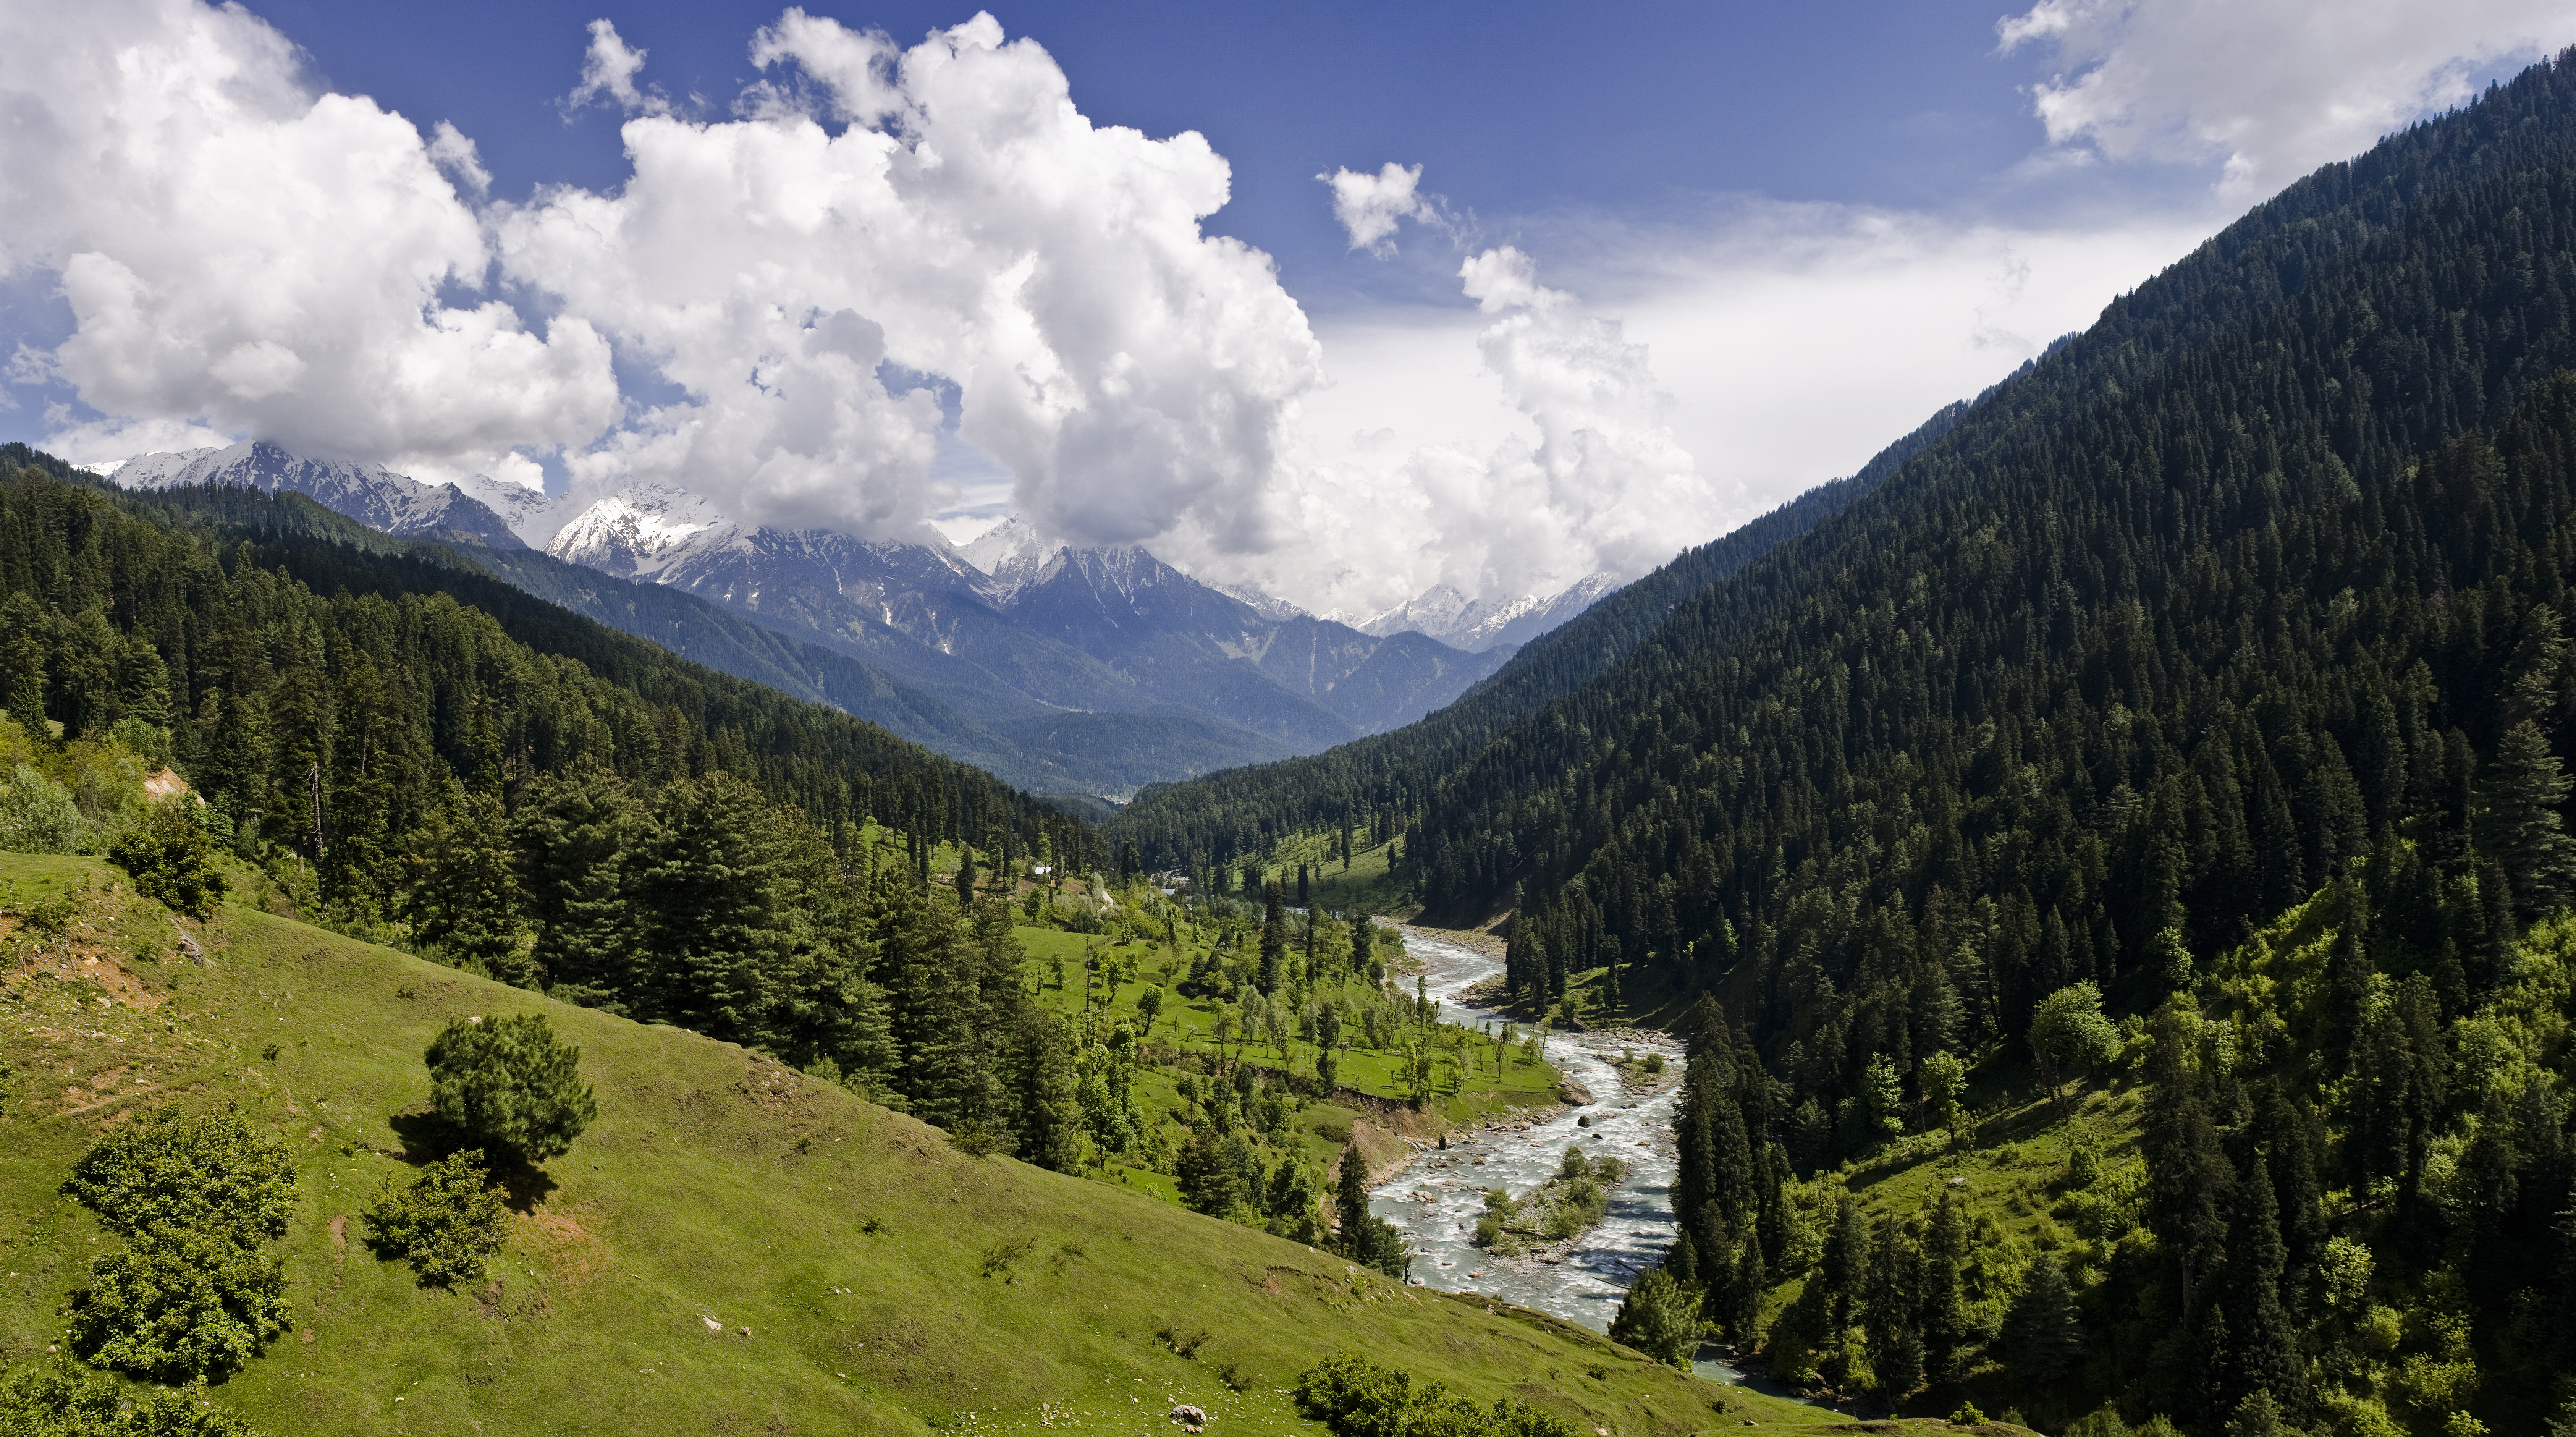
A militant assault in the Baisaran meadow near Pahalgam, Jammu and Kashmir, resulted in the deaths of 28 tourists and injuries to over 20 others on Tuesday afternoon, marking the deadliest civilian attack in the region since 2019.

The attack occurred around 2:50 PM when four to six assailants, dressed in military-style uniforms, emerged from the surrounding deodar forests and opened fire on tourists enjoying the popular meadow, often referred to as “Mini Switzerland” for its scenic beauty. Eyewitnesses reported that the attackers initially posed as security personnel, asking for identification and religious affiliations before selectively targeting non-Muslim men. Survivors recounted being asked to recite Islamic declarations and undergoing physical checks; those who failed were shot at close range.

The Resistance Front , an offshoot of the Pakistan-based Lashkar-e-Taiba, claimed responsibility for the massacre. In a statement, the group cited opposition to the settlement of over 85,000 non-locals in the Kashmir Valley, alleging it as a demographic alteration. This incident underscores the ongoing tensions following the revocation of Jammu and Kashmir’s special status in 2019, which allowed greater settlement of outsiders in the region.

Among the deceased were 24 tourists from various Indian states, including Karnataka, Kerala, Maharashtra, Odisha, Gujarat, Haryana, West Bengal, and Uttar Pradesh. Two locals from Jammu and Kashmir and two foreign nationals from Nepal and the United Arab Emirates were also killed. The injured, numbering over 20, were airlifted to military hospitals in Srinagar for treatment.

Prime Minister Narendra Modi, cutting short his visit to Saudi Arabia, condemned the attack as a “dastardly and inhuman act” and vowed to bring the perpetrators to justice. Union Home Minister Amit Shah traveled to Srinagar to assess the situation and coordinate the security response. Security forces launched a massive manhunt, deploying helicopters and imposing a temporary lockdown in parts of Pahalgam to apprehend the attackers.

The international community reacted swiftly. U.S. President Donald Trump expressed support for India, while U.N. Secretary-General António Guterres and leaders from Germany, Israel, and the European Union condemned the attack and offered condolences to the victims’ families.

The assault occurred during a period of increased tourism in Kashmir, with projections estimating around two crore visitors to the Union Territory this year. Pahalgam, a gateway to the Amarnath Yatra, had seen a surge in tourist footfall, signaling a return to normalcy after decades of insurgency. This attack threatens to derail these developments, casting a shadow over the region’s stability and economic recovery.

Opposition leaders criticized the government’s narrative of restored normalcy in Kashmir. Congress MP Priyanka Gandhi labeled the attack a “crime against humanity,” while Leader of Opposition Rahul Gandhi described it as “horrific,” emphasizing the need for a reassessment of the region’s security situation.

Eyewitness accounts painted a grim picture of the attack’s aftermath. Videos from the scene showed bloodied individuals lying on the ground, with others pleading for help. One woman was seen screaming for assistance for her husband, while others were seen lying motionless in the meadow. Survivors described the attackers’ methodical approach, with one assailant allegedly telling a woman that she was being spared so she could “narrate the horrors” to Prime Minister Modi.

The attack’s timing, coinciding with U.S. Vice President JD Vance’s visit to India, raised concerns about its potential geopolitical implications. While no direct link has been established, the incident echoes prior high-profile attacks timed with foreign dignitary visits, suggesting a possible strategy to garner international attention.

Advertisements

Bybit, the Dubai-based cryptocurrency exchange, is grappling with the aftermath of a massive cyberattack that resulted in the theft of approximately $1.4 billion worth of digital assets. The breach, attributed to the North Korean-linked Lazarus Group, has been described as the largest in the history of the crypto industry.

The hackers exploited vulnerabilities in Bybit’s cold wallet infrastructure, which is typically considered more secure than online hot wallets. Bybit’s CEO, Ben Zhou, disclosed that the attackers manipulated transaction interfaces and hijacked the cold wallet, redirecting its contents to unidentified addresses. The stolen assets, primarily Ethereum, have been rapidly converted into Bitcoin and dispersed across thousands of wallets to obfuscate their trail.

Zhou provided a detailed breakdown of the stolen funds: approximately 77% remain traceable, 20% have “gone dark,” and 3% have been successfully frozen. The term “gone dark” refers to funds that have been laundered through complex methods, making them untraceable. The traceable portion, roughly $1.07 billion, offers a glimmer of hope for recovery efforts.

The hackers employed sophisticated techniques to launder the stolen assets, including the use of decentralized exchanges like THORChain. Approximately 83% of the stolen Ethereum was converted into Bitcoin and distributed across nearly 7,000 wallets, each holding an average of 1.71 BTC. This fragmentation strategy complicates tracking and recovery efforts.

Bybit has initiated a bounty program to incentivize the recovery of stolen funds, offering up to 10% of the recovered assets to individuals who assist in freezing or retrieving the stolen cryptocurrencies. The exchange has also assured its users that it remains solvent and is taking measures to compensate for any unrecovered coins.

The incident has raised significant concerns about the security of cryptocurrency exchanges and the evolving tactics of cybercriminals. The Lazarus Group, known for its cybercrime operations linked to North Korea, has been implicated in several high-profile crypto thefts in recent years. Their methods often involve spear-phishing attacks and the use of malware to infiltrate systems.

KUALA LUMPUR, MALAYSIA – Media OutReach Newswire – 18 April 2025 – Central Bank Digital Currencies (CBDCs) have moved from being merely theoretical concepts to a stage when dozens of countries throughout the world are actively testing them in various pilot schemes. Designed as a government-backed digital version of fiat money, CBDCs combine the trust of centralised monetary systems with the flexibility of digital payments. Unlike cryptocurrencies, […]

Global capital turned its back on ESG last year. But that shift, we believe, is temporary and mistaken. ESG investing should and will return to favour, not just because it’s aligned with the challenges and priorities of our time, but because it remains one of the most rational long-term strategies for investors and economies alike. The numbers from 2024 were stark. Global sustainable fund inflows halved. In […]

A compromised administrative account within ZKsync’s infrastructure has been identified as the source of an exploit that diverted approximately $5 million worth of unclaimed ZK tokens from the platform’s airdrop contract. The breach, attributed to a compromised private key, was confined to the token airdrop mechanism, according to the project’s security team. An investigation into the incident remains ongoing.

The vulnerability was exploited during the initial phase of ZKsync’s token distribution, which aimed to allocate 17.5% of its total 21 billion ZK token supply to eligible users. The airdrop, intended to reward early adopters and contributors, has been marred by criticisms over its susceptibility to Sybil attacks—a method where an individual creates multiple wallets to illegitimately claim tokens. Reports indicate that one user managed to generate over 21,000 wallets to exploit the airdrop, highlighting significant flaws in the platform’s anti-Sybil measures.

Industry experts have voiced concerns regarding the airdrop’s design. Mudit Gupta, Chief Information Security Officer at Polygon, described the event as potentially the most “farmed” airdrop to date, citing a lack of effective Sybil filtering. Similarly, Adam Cochran of Cinneamhain Ventures criticized the eligibility criteria, suggesting they were easily manipulated by automated scripts, thereby disadvantaging genuine users.

The airdrop’s execution has also been scrutinized for its distribution methodology. Despite the intention to decentralize token ownership, data reveals that a significant portion of the tokens was claimed by a small group of wallets. Approximately 41% of the top recipient wallets have already liquidated their entire allocations, contributing to a 34.5% decline in the token’s value shortly after its launch.

Compounding the situation, the airdrop’s announcement and subsequent distribution were accompanied by a surge in phishing scams and malicious decentralized applications . These fraudulent entities impersonated official ZKsync channels, luring unsuspecting users into compromising their wallets. Security firm Blockaid reported a fivefold increase in malicious dApp activity targeting ZKsync users during this period.

By Nitya Chakraborty Though there is a 90 day pause in Trump’s latest unilateral imposition of reciprocal tariffs on most of the countries, the trade war between the USA and China, the two largest economies of the world is in full steam imparting tremors in global trade and economy. Close advisers of Trump were expecting […]
OpenAI is set to implement mandatory identity verification for developers seeking access to its advanced artificial intelligence models, marking a significant shift in its approach to platform security and user accountability. This move aims to mitigate misuse, enhance safety protocols, and align with broader regulatory expectations as the company prepares for the release of its next-generation AI systems. Developers will be required to submit government-issued identification to […]

HONG KONG SAR – Media OutReach Newswire – 10 April 2025 – CPA Australia’s latest Asia-Pacific (APAC) Small Business Survey 2024-25 reveals that the outlook for business growth this year for Hong Kong’s small and medium enterprises (SMEs) has slowed, though their hiring intentions remain strong. To combat uncertainties and rising competition, many are focusing on innovation and increasing their investment in artificial intelligence (AI). (Left) Mr […]

By Nitya Chakraborty What is happening to the “Neighbourhood First” policy of the Indian Prime Minister Narendra Modi in the year 2025? Modi is an expert in coining attractive slogans whether those finally work or not. For South Asia, he opted for Neighbourhood First and for South East Asia and ASEAN nations Act East. At […]

Artificial intelligence technologies, notably OpenAI’s ChatGPT, are increasingly being exploited to create convincing fake identification documents, posing significant challenges for security and identity verification systems worldwide. The emergence of platforms like ‘OnlyFake’ exemplifies this trend, offering AI-generated fake IDs, including passports and driving licenses, for as little as $15. Investigations have demonstrated that these counterfeit documents can bypass verification processes on major platforms, such as cryptocurrency exchanges, […]

Bitcoin’s network hashrate has achieved a new all-time high, reflecting a surge in mining activity and bolstered network security. As of March 24, 2025, the hashrate peaked at 1,088.76 exahashes per second , surpassing previous records and indicating significant growth in computational power dedicated to the network.

This milestone coincides with Bitcoin’s price surpassing the $100,000 threshold, reaching a peak of $103,259 before stabilizing around $102,648. The price surge has been partly attributed to political developments, including President-elect Donald Trump’s appointment of Paul Atkins, a pro-crypto figure, to lead the Securities and Exchange Commission .

The correlation between Bitcoin’s hashrate and its market price has been a topic of analysis among industry experts. Historically, an increase in hashrate has often preceded price appreciation, as miners’ confidence in the network’s profitability grows. Conversely, a rising price can incentivize more miners to join the network, further increasing the hashrate. This interplay suggests a symbiotic relationship where each factor can drive the other.

The recent surge in hashrate indicates a substantial increase in mining activity. This growth enhances the network’s security by making it more resilient to potential attacks. However, it also intensifies competition among miners, leading to higher operational costs and potential profit margin compression.

In response to these dynamics, some mining companies have adopted strategies to mitigate financial pressures. For instance, major U.S. miners have been stockpiling Bitcoin to navigate thinning profit margins amid escalating competition and operational costs. Companies like Mara Holdings, Riot Platforms, and CleanSpark have collectively raised over $3.7 billion since November 2024, leveraging the cryptocurrency’s price surge to bolster their reserves.

Emails falsely claiming to be from the cryptocurrency exchange Gemini are circulating, sparking concerns of a growing scam targeting its users. The fraudulent messages allege that the company has filed for bankruptcy and urge recipients to click on a link to confirm account details or withdraw their funds before an impending shutdown. Experts warn that this is part of an ongoing wave of phishing schemes aimed at […]

One Year After Acquiring Banyan Security, SonicWall’s Cloud Secure Edge/ZTNA Remote Access Solutions See Remarkable Growth SINGAPORE – Media OutReach Newswire – 1 April 2025 – SonicWall today marks a significant milestone in its journey redefining advanced cyber security protection with its Zero Trust Network Access (ZTNA) solution known as Cloud Secure Edge (CSE). One year after acquiring Banyan Security, a leading provider of zero-trust security for […]

A new survey by Hitachi Vantara has highlighted significant challenges faced by the Banking, Financial Services, and Insurance sector as artificial intelligence adoption accelerates. The study, titled “The Great AI Divide: New Survey Finds Financial Services Leaders Struggle with Data Governance and Infrastructure Demands,” reveals that while 48% of financial leaders prioritise data security in AI implementations, only 36% acknowledge the critical importance of data quality, leading […]

By Nitya Chakraborty Europe, which has always been vocal about its past history and civilization as well its contribution to the making of the modern world, has never faced such humiliation in the hands of its transatlantic ally the USA in the last eighty years since the end of the Second World War in 1945.The […]
Matein Khalid If ever any investor needed a real time lesson in emerging markets risk, the timebombs in Ankara, Jakarta and Bogotá to provided it. President Erdogan ordered the arrest of his top rival Istanbul Mayor Ekrem İmamoğlu and triggered a 10% plunge in the lira against the US dollar, an exodus of offshore money from the local T-bill market and a horrific meltdown in Istanbul bank […]

By Nitya Chakraborty Bangladesh has officially sought a meeting between their head of interim government Dr. Mohammad Yunus and the Indian Prime Minister Narendra Modi on the sidelines of the coming BIMSTEC meeting at Bangkok on April 2-4 next. Both countries are members of BIMSTEC. As per present schedule, both have confirmed their presence at […]


Matein Khalid Starting in 2016, the US has morphed into the world’s largest LNG exporter, eclipsing Australia and Qatar. Trump is determined to achieve global energy dominance as he exploits the geopolitical leverage American LNG exports give him in his relations with Europe, Asia and the GCC. He has pledged to dramatically expand US natural gas production via his “drill baby drill” ethos, rescinded Biden’s environmental pause […]

VISHNU RAJA
RYO YAMADA
HITORI GOTOH
IKUYO KITA