Just in:

News related to
attacks

Cyber security researchers are warning that built-in “Summarise with AI” buttons and AI-generated share links are being exploited to covertly plant malicious instructions inside artificial intelligence assistants, creating a new class of threat capable of distorting recommendations on health, finance and security matters. The technique, described by Microsoft as “AI recommendation poisoning”, centres on prompt injection attacks that subtly bias what large language models treat as trusted […]

PocketBlue, an open-source intelligence platform built for AI-driven research, is drawing growing interest among developers seeking greater control over how machine-assisted analysis is conducted. Hosted on GitHub and designed with a modular, local-first architecture, the project positions itself as an alternative to cloud-dependent research tools that rely heavily on proprietary models and opaque data pipelines. At its core, PocketBlue combines large language model orchestration with structured data […]

OpenClaw, the open-source autonomous AI agent framework that has attracted both widespread interest and intense scrutiny, has rolled out version 2026.2.12, a major update that resolves over 40 security flaws and strengthens core components of the platform. The release aims to address an array of risks—from remote code execution exposures to prompt-injection weaknesses—that researchers and operators have flagged as critical for safe deployment of agentic AI systems. […]

Microsoft has unveiled a new security feature in Windows 11 that fundamentally alters how administrator privileges operate on personal computers, signalling a decisive shift in the company’s approach to endpoint protection. The feature, known as Administrator Protection, removes persistent administrative rights from user accounts and replaces them with a tightly controlled, task-based elevation model. Instead of granting broad and continuous access to system-level controls, Windows 11 now […]

Businessman and television personality Kevin O’Leary has been awarded $2.8 million in a federal defamation lawsuit against prominent crypto influencer Ben “BitBoy” Armstrong after a judge handed down a default judgment against the defendant for failing to mount a substantive defence. The ruling by a US District Court judge in Florida came after Armstrong published a series of false and defamatory claims online that accused O’Leary of […]

First-Ever Attack-Defence Simulation Aligns with Real Corporate Needs Setting a New Benchmark for Local Cybersecurity Competitions

HONG KONG SAR – Media OutReach Newswire – 13 February 2026 – As cyberattacks grow increasingly complex, cybersecurity has become a critical domain of global concern and a talent shortage. According to the latest “Hong Kong Cybersecurity Outlook 2026” released by the Hong Kong Computer Emergency Response Team Coordination Centre (HKCERT) under the Hong Kong Productivity Council (HKPC), nearly 30% of the 622 surveyed enterprises still lack dedicated cybersecurity staff. Specifically, only 26% of SMEs have a dedicated cybersecurity role, significantly lower than the 59% of large enterprises, reflecting a gap in resource allocation and technology adoption among SMEs.

Now in its sixth year, “HKCERT Capture The Flag Challenge” continues to attract top cybersecurity talents from Hong Kong and beyond, showcasing the capability and vitality of the next generation of local and international cybersecurity professionals.

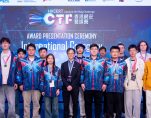
To cultivate practical talent for the cybersecurity sector, the sixth “HKCERT Capture The Flag Challenge 2025” (HKCERT CTF Challenge) was successfully organised by the Digital Policy Office (DPO), HKPC, and HKCERT. This year’s competition was elevated to the first-ever adoption of an attack–defence mode, closely replicating the network setup of real enterprises. Participants experienced first-hand hacking techniques, system vulnerability analysis, threat intelligence gathering, and coordinated response in a simulated real-world environment. Through completing multiple tasks within a limited time, the competition also allowed them to break through the traditional classroom theoretical framework, gain practical experience and build confidence. The event attracted around 1,940 young contestants, an increase of nearly 40% from last year’s 1,385 participants, reaching a record high for the competition. Contestants included teams from Hong Kong, Chinese Mainland, Asia, and Europe, fostering cross-regional exchange and collaboration. In the finals, three local teams and one overseas team were awarded gold prizes in the Secondary School, Tertiary Institution, Open Category, and International Category respectively, while Sing Yin Secondary School received the “Best School Award”. The full list of awardees is available on the event website.

Participants Share Practical Experience Integrating AI into Attack and Defence
The competition was well received by contestants for its innovative format and realistic offensive and defensive environment, offering a valuable platform for learning and exchange. The winning team in the International Category, W&M, commented, “Our members are from Shanxi, Guangdong and Beijing. This was our first time competing together in the HKCERT CTF Challenge. The atmosphere and experience of the finals were excellent. The tasks were centred on an attack‑defence simulation, requiring us to find all vulnerabilities while patching our own systems and attacking other teams at the same time. Some vulnerabilities were discovered and exploited by other teams first, which kept the scores very close and made the competition incredibly tense and exciting”.

They added, “During the competition, we also applied lots of AI techniques for assistance, such as applying AI to analyse vulnerabilities and refine attack methods. In the future, AI may play a deeper role in areas like vulnerability detection and code analysis, but for now it cannot be fully relied upon—human oversight is still essential”.

HKCERT CTF Challenge has now been held for six consecutive years, with its scale expanding annually and participants showing continuous growth. Many secondary school students gain their first hands‑on exposure to cybersecurity through the competition and connect with university mentors, helping them shape their academic and career paths. Several past participants have gone on to compete in local and international events, committing to a future in the cybersecurity field. Beyond attracting overseas talent to exchange ideas in Hong Kong, HKCERT continues to build connections between cybersecurity professionals in Hong Kong and Chinese Mainland. Top‑performing teams can gain direct entry into equivalent finals in Chinese Mainland. For example, participants from the previous HKCERT CTF Challenge 2024 advanced directly to the finals of the “Greater Bay Area Cup Cybersecurity Challenge”, where they secured the top four places in the Hong Kong and Macao category. This also provided local contestants with access to world‑class cybersecurity techniques, effectively promoting cross‑regional elite collaboration and talent development.

Finals Format Upgraded: Attack-Defence Mode Mirrors Real Enterprise Operations
The finals were comprehensively upgraded this year. In addition to increase the overall technical difficulty, the competition introduced an attack‑defence format for the first time that closely mirrors real enterprise cybersecurity operations. Teams played dual roles—both attackers and defenders—in an environment created with reference to the real-world systems. The tasks simulated incident response and live attack-defence scenarios commonly encountered in the cybersecurity field. Within a limited timeframe, participants had to do penetration testing, exploit vulnerabilities and attack, while patching their own systems and monitoring threats in real time against attacks from other teams. This parallel attack‑defence setup reflects actual workflow patterns in the industry, effectively training participants’ analytical abilities and adaptability under pressure. Through hands‑on practice in a likely enterprise environment, contestants developed multifaceted, industry‑aligned capabilities—laying a solid foundation for their future careers in cybersecurity.

Ms Candy CHAN, Assistant Commissioner (Project Governance and Cybersecurity) of the DPO, highlighted the DPO’s commitment to enhancing Hong Kong’s cyber resilience, with one of its key initiatives being the nurturing of the next generation of cybersecurity professionals. She emphasised that the DPO has been collaborating closely with academia and industry partners to foster a robust talent pipeline and build a safer digital environment in Hong Kong. She noted that this year marks the sixth edition of the HKCERT CTF Challenge, which has grown into one of Hong Kong’s most respected and anticipated cybersecurity competitions over the years. Beyond being a contest of technical prowess, the Challenge serves as a dynamic platform for networking, knowledge exchange and community building among the new generation of cybersecurity experts.

Ir Samson SUEN, General Manager of Digital Trust and Transformation Division of HKPC, stated, “HKCERT CTF Challenge has consistently aimed to build an international platform for technical exchange. Through high-intensity simulated contests, we enhance participants’ cyber defence skills and promote cross-regional interaction among emerging cybersecurity talents. This cultivates a new generation of globally competitive professionals in Hong Kong and strengthens the local talent pipeline. This year’s finals first introduced a simulation of real-world cybersecurity operations, enabling teams to experience both offensive and defensive roles in a recent cybersecurity team. This hands-on approach is crucial for developing practical skills and incident response capabilities”.

Fostering Cybersecurity Awareness Across All Sectors of Society
To further enhance cybersecurity awareness across the community, HKCERT has partnered with the DPO and the Cyber Security and Technology Crime Bureau of The Hong Kong Police Force, to launch the “Building a Secure Cyberspace 2026” campaign to promote cybersecurity awareness. The initiative includes various educational activities, such as an “AI-Generated Four-Panel Comic”contest, which encourages the public to make good use of AI tools while strengthening their understanding of cybersecurity. At the corporate governance level, HKCERT will publish a series of practical guidelines addressing emerging risks —such as AI applications and supply chain security—highlighted in the “Hong Kong Cybersecurity Outlook 2026”, to support business in establishing a robust protection framework. In particular for AI governance, the guidelines will offer actionable recommendations covering AI system security assessments, compliance rules for employees using public AI platforms, controls over sensitive data input, and methods for monitoring and defending against AI‑assisted attacks. These resources aim to help enterprises systematically enhance their cyber resilience across governance, technology, and awareness.

As Hong Kong accelerates the development of innovation and technology and advances its digital economy, strengthening cyber defence capabilities has become a key talent need. HKCERT will continue to support businesses and the public through incident response, security guidance, and cybersecurity awareness programmes. The HKCERT CTF Challenge continues to play a vital role in nurturing local talent, fostering cross-regional collaboration, and advancing public education. By enhancing the overall level of protection, the competition contributes to the sustainable development of the digital economy and reinforces Hong Kong’s long‑term competitiveness.

The seventh edition of HKCERT CTF Challenge will be held in November 2026, featuring more innovative attack-defence challenges and continuing to set up an international category to provide local contestants with a platform for technical exchange with top teams from Hong Kong, Chinese Mainland, and overseas. Registration opens in September 2026, with finalists competing in the live finals in February 2027.

Hashtag: #HKCERT

The issuer is solely responsible for the content of this announcement.

About Hong Kong Productivity Council

The Hong Kong Productivity Council (HKPC) is a statutory body established in 1967, dedicated to enhancing the productivity and competitiveness of Hong Kong enterprises through world-class applied R&D, innovative technology services, and integrated manufacturing solutions. As a market-oriented, international R&D organisation, HKPC leverages its deep expertise and extensive industry experience in key areas such as AI, advanced manufacturing, life and health technology, green technology and new energy to drive new industrialisation and support the growth of emerging and future industries.

HKPC focuses on addressing businesses challenges and industrial technology needs, promoting the full integration between technological and industrial innovation. Through technology transfer, product innovation, intellectual property protection and commercialisation of R&D outcomes, the Council fosters collaboration with the local business community as well as top global R&D institutions, delivering added value to industries and advancing the development of new productive forces. HKPC’s world-class R&D achievements have been widely recognised over the years, winning an array of local and overseas accolades, reinforcing Hong Kong’s role as an international innovation and technology centre and a smart city.

To help enterprises capitalise on Hong Kong’s strengths in international connectivity to expand into global markets, HKPC offers comprehensive overseas expansion services tailored to critical areas including product development, technology, manufacturing, and management, enabling businesses to successfully go global from Hong Kong.

HKPC is also committed to providing timely and practical support to SMEs and startups with timely and practical , assisting them in accessing Government funding programmes. Through its FutureSkills training initiatives, HKPC helps both industry and academia stay ahead in latest digital and STEM technologies, nurturing a future-ready talent pool for Hong Kong.

For more information, please visit HKPC’s website: .

  • “Geopolitical Volatility” is a top five current and future risk, highlighting the growing instability across the region
  • 83 Percent of Firms Report Rising Insurable Risk Costs

TOKYO, JAPAN – Media OutReach Newswire – 12 February 2026 – Aon plc (NYSE: AON), a leading global professional services firm, has released the Japan findings of its 2025 Global Risk Management Survey. The survey reveals that Japanese businesses are navigating a complex landscape marked by persistent cyber threats, supply chain disruptions and weather/natural disasters. The survey, which gathered insights from nearly 3,000 risk managers, C-suite leaders and executives across 63 countries, highlights the unique risks Japan businesses are facing amid global disruption.

Japan’s Top Risks:

“Cyber Attacks/Data Breach” remains the top risk for Japanese businesses, consistent with global trends. “Supply chain or distribution failure” ranks second, as extreme weather events and mounting geopolitical volatility including shifting trade policies force companies to reassess their supply chains. In addition, “Product Liability/Recall” and “Exchange Rate Fluctuation” pose significant risks, reflecting the country’s manufacturing strength and exposure to global market volatility. Notably, 63.6 percent of Japanese respondents reported losses due to product liability or recall issues and 47.6 percent cited losses from exchange rate fluctuations.

Tatsuya Yamamoto, CEO of Japan at Aon, said, “Japanese organisations are operating in an environment of unprecedented complexity. Cyber, weather and geopolitical risks continue to be acute challenges for Japan businesses, underscoring the need for robust risk management frameworks and agile strategies. As market trends shift and competition intensifies, vigilance and adaptability will be key. The interconnectedness of risks – where a cyber attack can disrupt supply chains or geopolitical volatility can trigger regulatory changes – demands a holistic, proactive approach to resilience.”

2025 Top 10 Business Risks in Japan

  1. Cyber Attacks/Data Breach
  2. Supply Chain or Distribution Failure
  3. Weather/Natural Disasters
  4. Geopolitical Volatility
  5. Business Interruption
  6. Economic Slowdown/Slow Recovery
  7. Exchange Rate Fluctuation
  8. Commodity Price Risk/Scarcity of Materials
  9. Product Liability/Recall
  10. Failure to Attract or Retain Top Talent

Risk Management: Formalisation and Focus on Insurable Risks

Japanese organisations demonstrate a strong commitment to risk management, with 74.7 percent having a formal risk management and insurance department, compared to 68.4 percent globally. Additionally, 75.3 percent measure the total cost of insurable risk and 83.3 percent report that these costs are increasing. While risk awareness is rising, most organisations have yet to quantify their exposures or leverage advanced analytics.

Japanese Businesses Risk Management Assessments for Top Three Risks

For “Cyber Attacks/Data Breaches”:

  1. 27.2 percent have assessed the risk
  2. 12.6 percent have developed continuity plans
  3. 22.3 Percent have risk management plans

For “Supply Chain or Distribution Failure”:

  1. 25 percent have assessed the risk
  2. 20 percent have developed continuity plans
  3. 26.7 Percent have risk management plans

For “Weather/Natural Disasters”:

  1. 24.1 percent have assessed the risk
  2. 22.4 percent have developed continuity plans
  3. 13.8 percent have risk management plans

Future Risks: Rapidly Changing Market Trends and Geopolitical Volatility

Looking ahead, Japanese organisations expect “Weather/Natural Disasters” and “Geopolitical Volatility” to remain critical risks, alongside “Rapidly Changing Market Trends,” which is more prominent in Japan than globally. This highlights the country’s exposure to climate events and evolving consumer preferences.

Japan’s Top Five Future Business Risks by 2028:

  1. Cyber Attacks/Data Breach
  2. Weather/Natural Disasters
  3. Geopolitical Volatility
  4. Rapidly Changing Market Trends
  5. Increasing Competition

Shinichi Kandatsu, head of Commercial Risk Solutions for Japan at Aon, said, “Cyber and weather-related risks continue to lead the rankings as top concerns for Japanese businesses today and in the future, with geopolitical volatility also ranking among the top five risks across both periods. This trend reflects the growing instability across the region, with implications for supply chains, regulatory environments and financial performance. In today’s fast-moving market, leveraging advanced data analytics is essential for businesses to anticipate emerging risks, optimise risk capital and build resilience. The findings from Aon’s Global Risk Management Survey provide Japanese businesses with actionable information to benchmark their risk strategies and identify areas for improvement.”

To access the full report and explore how Aon is helping clients navigate today’s disruption dynamic, visit Global Risk Management Survey Japan

Hashtag: #Aon

The issuer is solely responsible for the content of this announcement.

About Aon

Aon plc (NYSE: AON) exists to shape decisions for the better — to protect and enrich the lives of people around the world. Through actionable analytic insight, globally integrated Risk Capital and Human Capital expertise, and locally relevant solutions, our colleagues provide clients in over 120 countries with the clarity and confidence to make better risk and people decisions that help protect and grow their businesses.

Follow Aon on LinkedIn, X, Facebook and Instagram. Stay up-to-date by visiting Aon’s newsroom and sign up for news alerts here.

Disclaimer

The information contained in this document is solely for information purposes, for general guidance only and is not intended to address the circumstances of any particular individual or entity. Although Aon endeavours to provide accurate and timely information and uses sources that it considers reliable, the firm does not warrant, represent or guarantee the accuracy, adequacy, completeness or fitness for any purpose of any content of this document and can accept no liability for any loss incurred in any way by any person who may rely on it. There can be no guarantee that the information contained in this document will remain accurate as on the date it is received or that it will continue to be accurate in the future. No individual or entity should make decisions or act based solely on the information contained herein without appropriate professional advice and targeted research.

Advertisements
TAIPEI, TAIWAN – Media OutReach Newswire – 10 February 2026 – CyCraft Technology Corporation (TWSE: 7823), Taiwan’s first pure-play AI-native cybersecurity company, has officially listed on the Taiwan Stock Exchange Innovation Board, marking a major milestone for Asia’s emerging AI-driven security leaders.

CyCraft’s founders joined representatives from the Taiwan Stock Exchange, Yuanta Securities, auditors, and legal advisors to celebrate the company’s listing on the TWSE Innovation Board.

CyCraft is forged in one of the world’s most challenging cyber environments. Taiwan faces persistent and large-scale cyber threats from highly-motivated threat actors targeting government, semiconductor supply chains, financial systems, and critical infrastructure. Rather than theorizing about threats, CyCraft has spent years defending against them at national and industry scale.

That experience has produced real-world operational advantages global markets increasingly demand: early-warning intelligence, autonomous machine-speed defense, and field-proven AI automation that cannot be casually replicated.

As generative AI reshapes software development, many SaaS categories face commoditization through “vibe-coding.” Cybersecurity stands apart. Mission-critical defense requires real adversarial data, ultra-low latency, zero-configuration precision, continuous adaptation against sophisticated attacks, and regulatory-grade trust. These capabilities are not synthetic. AI does not replace cyber defense—it amplifies defenders who already operate in real operational environments.

CyCraft’s platform is built around three growth engines:

Enterprise Cyber Resilience.

Its flagship XCockpit AI platform operates over 600K sensors, protecting hundreds of government agencies, financial institutions, and semiconductor leaders across Asia-Pacific. The platform delivers preemptive exposure discovery, automated attack-path simulation, SEMI E187-compliant supply-chain risk mapping, and autonomous triage and response. The shift from reactive protection to preemptive resilience defines CyCraft’s core value proposition.

AI Agent & LLM Security.

As enterprises deploy LLMs and autonomous agents, CyCraft addresses a rapidly emerging risk layer. XecGuard provides ultra-low-latency AI guardrails to detect and prevent prompt injection, jailbreaks, data exfiltration, and tool misuse in real time. Paired with XecART, an automated red-teaming and evaluation platform, CyCraft delivers a scalable, cloud-based and on-prem AI gateway for secure multi-agent orchestration.

The XecGuard and XecART dashboards enable enterprise AI governance with real-time guardrails, automated red teaming, and flexible deployment via on-premises environments or cloud-based APIs.

Enterprise Cyber Resilience.

Its flagship XCockpit AI platform operates over 600K sensors, protecting hundreds of government agencies, financial institutions, and semiconductor leaders across Asia-Pacific. The platform delivers preemptive exposure discovery, automated attack-path simulation, SEMI E187-compliant supply-chain risk mapping, and autonomous triage and response. The shift from reactive protection to preemptive resilience defines CyCraft’s core value proposition.

AI Agent & LLM Security.

As enterprises deploy LLMs and autonomous agents, CyCraft addresses a rapidly emerging risk layer. XecGuard provides ultra-low-latency AI guardrails to detect and prevent prompt injection, jailbreaks, data exfiltration, and tool misuse in real time. Paired with XecART, an automated red-teaming and evaluation platform, CyCraft delivers a scalable, cloud-based and on-prem AI gateway for secure multi-agent orchestration.

The XecGuard and XecART dashboards enable enterprise AI governance with real-time guardrails, automated red teaming, and flexible deployment via on-premises environments or cloud-based APIs.

XecGuard enables enterprise AI governance with real-time guardrails and flexible deployment via on-premises environments or cloud-based APIs.

Unmanned Systems Security.

CyCraft’s XecDefend platform pioneers cyber protection and disruption capabilities for AI-driven anti-drone defense. The solution enables autonomous detection, soft-kill response, and resilient protection for unmanned aerial, maritime, and ground systems—offering software-defined defense for critical infrastructure and defense supply chains.

CyCraft’s credibility is reinforced by third-party validation, including seven appearances in Gartner research, three MITRE ATT&CK evaluations with zero-configuration and zero-latency performance, and the “Next-Big” Award from former Taiwanese President Tsai Ing-wen, recognizing CyCraft as the “TSMC of cybersecurity.”.

In 2025 alone, CyCraft handled multiple critical incidents for Taiwan-listed companies and completed over ten forensic investigations in support of cyber insurance engagements in Japan.

Chairman Benson Wu stated, “In Taiwan, with AI, we help secure the world. This listing accelerates our global expansion through organic growth and strategic M&A. Our goal is to surpass 50% overseas revenue by 2030 and build Asia’s most trusted AI-native cybersecurity brand.”

Disclaimer: The information contained herein does not constitute advice.

Hashtag: #CyCraft #AIsecurity #Cybersecurity #InnovationBoard #AITaiwan #GlobalExpansion


The issuer is solely responsible for the content of this announcement.

CyCraft Technology

CyCraft Technology (7823.TW) — Taiwan’s first AI-native cybersecurity company to list on the TWSE Innovation Board — is dedicated to automating cybersecurity with AI, shifting defense from reactive firefighting to proactive, scalable dominance. Delivering protection that is faster, easier, safer — and smarter on cost, CyCraft empowers defenders to scale. With a proven track record serving top-tier government agencies, leading financial institutions, and semiconductor giants, CyCraft is building Asia’s most advanced AI-driven joint defense ecosystem — dramatically shortening dwell time, reducing breach impact, and strengthening enterprise digital resilience worldwide. More information:

Sharjah Women’s Sports Club underlined their status as title contenders at the Arab Women Sports Tournament with a hard-fought victory over Al Wasl, prevailing in a charged all-Emirati encounter that set the tone for the volleyball competition at the eighth edition of the event. The result consolidated Sharjah’s position near the top of the standings and reinforced the growing depth of women’s volleyball across the UAE, where […]

By T N Ashok NEW YORK: For seven decades, American diplomats danced around Kashmir with the precision of tightrope walkers, carefully avoiding any gesture that might suggest the United States had chosen sides in South Asia’s most intractable territorial dispute. Maps were scrubbed of political meaning. Statements were lawyered into studied neutrality. From Truman to […]

The article India Have Reasons To Be Happy At Big U.S. Switch On The Status Of Kashmir appeared first on Latest India news, analysis and reports on Newspack by India Press Agency).

A plan by the Transportation Security Administration to charge passengers a $45 fee for travelling without acceptable identification has triggered a legal challenge in the United States, reopening a long-running debate over the limits of regulatory authority and the rights of air travellers at security checkpoints. The fee, announced as part of updated screening procedures, applies to passengers who arrive at airports without government-issued photo identification and […]

Arabian Post Staff -Dubai   Washington has approved a potential sale of Patriot interceptor missiles and associated equipment to Saudi Arabia with an estimated value of about $9 billion, marking one of the largest US arms packages proposed for the kingdom in several years and underscoring a renewed focus on air and missile defence cooperation in the Gulf. The clearance, granted by the US State Department and […]

A warning from a long-standing crypto fund manager has reignited debate over Bitcoin’s long-term viability, with claims that the world’s largest cryptocurrency could face a structural security breakdown within the next seven to eleven years unless its economic model changes. Justin Bons, founder and chief investment officer of Cyber Capital, has argued that Bitcoin’s reliance on declining block subsidies will eventually undermine the incentives that secure its […]

  Kaspersky has introduced a new online tool aimed at helping industrial companies in the Middle East quantify cyber risk in operational technology environments, as manufacturers, energy firms and utilities face mounting pressure to justify cybersecurity spending with clearer financial metrics. The cybersecurity company said the OT Cybersecurity Savings Calculator is designed to translate technical exposure in industrial control systems into potential monetary losses, allowing executives to […]

A major cybersecurity incident affecting Panera Bread has put millions of customer and employee records at risk, as disclosed through multiple industry reports and hacker claims. The breach, attributed to the cybercrime group ShinyHunters, involves the theft of an extensive dataset including names, email addresses, phone numbers and home addresses, with the potential total of affected records estimated at around 14 million. This disclosure underscores widening digital […]

AI-related Attacks and Supply Chain Risks Emerge as Top Concerns Nearly 30% of Enterprises Lack Dedicated Cybersecurity Personnel

HONG KONG SAR – Media OutReach Newswire – 28 January 2026 – The Hong Kong Computer Emergency Response Team Coordination Centre (HKCERT), under the Hong Kong Productivity Council (HKPC), today hosted a media briefing to officially release the annual “Hong Kong Cybersecurity Outlook 2026”. The report reveals that cyberattacks have become more automated, targeted, and destructive with the rapid proliferation of Artificial Intelligence (AI) technologies, posing significant threats to business operations and information security. A record high 15,877 cybersecurity incidents were recorded in Hong Kong in 2025, marking a 27% year-on-year increase. The report also highlights five key cybersecurity risks expected to emerge in 2026, mainly under AI-related threats and supply chain vulnerabilities.

HKCERT also released the findings of the “Hong Kong Enterprise Cybersecurity Landscape”, which analyses the current state of local enterprises’ cybersecurity defences and resource allocation in the face of cyber risks. The study covered 622 enterprises (including 544 SMEs and 78 large enterprises) and interviewed 50 cybersecurity service providers to assess the key factors businesses consider when selecting cybersecurity services. The findings reveal that nearly 70% of enterprises have dedicated cybersecurity personnel, showing the increasing importance local businesses place on cybersecurity. Many SMEs have also begun strengthening their security measures, demonstrating a proactive awareness of cyber threats. However, they were behind large enterprises in terms of technology deployment and resource allocation. Moreover, around 35% of businesses using AI would enter corporate data into AI tools, suggesting that there is still room for improvement in local overall defence capabilities and AI governance awareness.

Mr Edmond LAI, Chief Digital Officer of HKPC, stated, “The proliferation of AI can drive innovation, but it can also become a powerful tool for hackers, making cyber threats stealthier and more scalable. Our report indicates a lack of governance in corporate use of AI tools. In particular, the limited resources and knowledge of SMEs may limit their full understanding of the potential risks involved. Moreover, supply chain attacks have become the weakest link in enterprise security, where a single vendor’s vulnerability can trigger a chain reaction of crises, even if the enterprises have robust protective measures. To address these challenges, enterprises must shift from passive response to proactive deployment, starting with establishing clear AI usage guidelines and audit mechanisms, and deeply integrating them into the overall cybersecurity strategy”.

Overview of Cybersecurity Incidents in 2025:

Phishing Accounts for Nearly 60% – Record-High Number of Cases

According to the latest statistics from HKCERT, a total of 15,877 cybersecurity incidents were reported in 2025, marking a new record high. Among them, phishing attacks remained the most prominent threat, accounting for nearly 60% (57%) of total cases. The rise of generative AI has made phishing messages increasingly realistic and harder to detect, further amplifying the associated risks. Attack delivery methods have expanded beyond traditional email to social media or instant messaging platforms (such as WhatsApp) (34%) and cryptocurrency platforms (18%).

In parallel, cases involving vulnerable systems also saw a sharp increase, with 2,328 incidents (15%), representing a more than 3.5-fold rise compared to the previous year. This suggests that attackers are actively exploiting misconfigurations and unpatched system vulnerabilities. Meanwhile, botnet-related incidents remained steady at 18%. While stable in number, botnets are notoriously difficult to eradicate completely, representing a long-term latent threat.

Top 5 Cybersecurity Risks in 2026

Based on industry expert analysis and HKPC’s ongoing research into the local business environment, and considering industry trends and technological developments, HKCERT predicts that the following five cybersecurity risks will pose significant challenges to businesses in 2026:

  1. AI-Driven Attacks and Agentic AI Risks
  2. Weak AI Governance of Enterprises Increases Data Leakage Risks
  3. Supply Chain Vulnerabilities and Third-Party Security Gaps
  4. Over-Reliance on Cloud Infrastructure Creates Single Points of Failure
  5. Emerging Threats from AI-Enabled Devices

30% of Enterprises Lack Dedicated Cybersecurity Staff, SMEs Lag in Defense and Investment

“The Hong Kong Enterprise Cybersecurity Landscape” reveals nearly 70% of enterprises have dedicated cybersecurity personnel, showing the increasing importance place on cybersecurity. By company size, 67% of SMEs have personnel responsible for cybersecurity, and 95% of large enterprises do. Among them, 26% of SMEs have dedicated cybersecurity personnel, which is lower than the 59% of large enterprises, reflecting different challenges in resource allocation and professional support for companies of different sizes.

Many SMEs have already implemented basic protective measures, such as 48% of SMEs have adopted email security, but there is still room for improvement when compared to the 79% of large enterprises. For Privileged Access Management (PAM), 29% of SMEs are employed, which is still lower than 60% of large enterprises. The figure on using Advanced cybersecurity practices, such as Remote Access Security Measures (SMEs 31% vs 67%), also reflects that SMEs still need support in promoting technological upgrades, especially when data security is increasingly important today, the protection of SMEs of all sizes cannot be ignored.

Regarding investment and resource allocation, SMEs are generally cautious in their investment, but some companies have gradually increased their investment in cybersecurity and training. In the past year 13% of SMEs increased cybersecurity-related resources (including staff and tools), and 12% invested more resources in cybersecurity training. In comparison, the proportions for large enterprises were 41% and 50%, respectively. Looking ahead to the next 12 months, SMEs are relatively conservative in their plans for increasing resources — no matter in recruitment of cybersecurity personnel (SMEs 5% vs 15%), training (SMEs 13% vs 38%) and budget (SMEs 13% vs 36%). However, as cyber threats evolve, it is believed that enterprises will gradually increase their related investments to strengthen their overall defense capabilities.

HKCERT’s Five Key Recommendations: Helping Enterprises Build Effective Cyber Defenses

HKCERT has outlined five key recommendations to help enterprises strengthen their cybersecurity posture:

  1. Assigning Personnel for Cybersecurity: Enterprises should assign employees with basic cybersecurity knowledge to be responsible for daily monitoring and response work, with clear division of responsibilities to ensure timely response to emergencies.
  2. Promoting AI Governance and Regulation: As the application of AI tools and third-party platforms becomes increasingly widespread, enterprises should formulate relevant policies and operational guidelines, clearly specifying the available tools and scope of data input, as well as procedures for responding to third-party incidents, to minimise operational and reputational risks.
  3. Collaborative Efforts of All Staff to Prevent Phishing Attacks: Enterprises should adopt both technical measures (such as email filtering and multi‑factor authentication) and an organisation‑wide security culture to jointly defend against phishing attacks. This helps enhance each employee’s ability to identify suspicious emails and links, thereby reducing the risk of data leakage.
  4. Enhance Cybersecurity Awareness and Training across all Staff: Cybersecurity is a shared responsibility across the entire organisation. Enterprises should regularly provide targeted security training for different departments—especially for roles that handle sensitive data—and strengthen incident response capabilities through simulation exercises and case‑based learning to reduce human error.
  5. Strengthen Technical Protection Measures: Enterprises should implement essential cybersecurity technologies, including:
    • Email security and access‑rights control
    • Data protection measures (such as encryption and backup)
    • Remote access security measures mechanisms (such as VPNs and identity authentication)
    • Proactive security solutions (such as intrusion detection and firewall monitoring)

As cyber threats grow increasingly complex and attack techniques become more advanced, enabling SMEs to effectively deploy cybersecurity defences has become a shared responsibility across society. In addition to operating a 24-hour incident reporting and supporting hotline, HKCERT continuously monitors local online activities. When cyberattacks targeting Hong Kong are detected, it proactively traces and disrupts the source and issues timely public alerts. In recent years, HKCERT has also leveraged self‑developed AI systems to take down phishing websites in advance, preventing incidents before they occur. To strengthen preventive measures and promote education among SMEs, HKCERT has published multiple security guidelines addressing emerging technology risks, helping technical personnel understand and adopt appropriate protection strategies. At the same time, HKCERT actively promotes cybersecurity awareness through a dedicated webpage on in‑depth analysis of major phishing and ransomware attacks, as well as by organising large‑scale public events and participating in over 30 seminars annually.

Since last year, HKCERT further acted as a bridge between SMEs and cybersecurity service providers to launch the Cybersecurity Service Providers Connect Programme with Digital Policy Office. The Programme offers a one-stop platform that brings together 21 vetted cybersecurity service providers, covering four key areas, including Internet Security Solutions, Cybersecurity Assessment Services, Managed Security and Incident Response Services, and Cybersecurity Training Services. It helps SMEs quickly identify suitable solutions and strengthen their cyber defence capabilities. The Programme will continue to enhance its services, promote resource sharing, and collaborate with the industry to build a safer digital business environment.

Hashtag: #HKCERT

The issuer is solely responsible for the content of this announcement.

About Hong Kong Computer Emergency Response Team Coordination Centre

Managed by the Hong Kong Productivity Council (HKPC), Hong Kong Computer Emergency Response Team Coordination Centre (HKCERT) is the centre for coordination of computer security incident response for local enterprises and Internet Users. Its missions are to facilitate information disseminating, provide advices on preventive measures against security threats and to promote information security awareness.

HKCERT collaborates with local bodies to collect and disseminate information, and coordinate response actions. HKCERT is also a member of the Forum of Incident Response and Security Teams (FIRST) and the Asia Pacific Computer Emergency Response Team (APCERT). We exchange information with other CERTs and act as a point of contact on cross-border security incidents.

About the Hong Kong Productivity Council
The Hong Kong Productivity Council (HKPC) is a statutory body established in 1967, dedicated to enhancing the productivity and competitiveness of Hong Kong enterprises through world-class applied R&D, innovative technology services, and integrated manufacturing solutions. As a market-oriented, international R&D organisation, HKPC leverages its deep expertise and extensive industry experience in key areas such as AI, advanced manufacturing, life and health technology, green technology and new energy to drive new industrialisation and support the growth of emerging and future industries.

HKPC focuses on addressing businesses challenges and industrial technology needs, promoting the full integration between technological and industrial innovation. Through technology transfer, product innovation, intellectual property protection and commercialisation of R&D outcomes, the Council fosters collaboration with the local business community as well as top global R&D institutions, delivering added value to industries and advancing the development of new productive forces. HKPC’s world-class R&D achievements have been widely recognised over the years, winning an array of local and overseas accolades, reinforcing Hong Kong’s role as an international innovation and technology centre and a smart city.

To help enterprises capitalise on Hong Kong’s strengths in international connectivity to expand into global markets, HKPC offers comprehensive overseas expansion services tailored to critical areas including product development, technology, manufacturing, and management, enabling businesses to successfully go global from Hong Kong.

HKPC is also committed to providing timely and practical support to SMEs and startups with timely and practical , assisting them in accessing Government funding programmes. Through its FutureSkills training initiatives, HKPC helps both industry and academia stay ahead in latest digital and STEM technologies, nurturing a future-ready talent pool for Hong Kong.

For more information, please visit HKPC’s website:

A quiet but unsettling episode in the artificial intelligence ecosystem has sharpened concerns about how quickly powerful autonomous tools are being deployed without robust safeguards. A single message, sent politely and without any technical wizardry, was enough for an attacker to extract a private cryptographic key from a user within minutes. The breach did not rely on malware, brute force or advanced exploits. It relied on trust, […]

Gmail is undergoing a set of structural changes that extend beyond visible interface tweaks, and security specialists warn the quieter updates could leave millions of accounts exposed if users fail to adjust their settings. The most immediate concern centres on how Google is reworking legacy email access and tightening the way third-party messages are handled inside Gmail, at a time when artificial intelligence tools are becoming more […]

Arabian Post Staff -Dubai   Russian President Vladimir Putin and envoys of the United States wrapped up around four hours of negotiations in the Kremlin on Thursday night, with Moscow underscoring that any peace settlement to end the war in Ukraine hinges on agreement over territorial control. The talks, which included Steve Witkoff, Jared Kushner and White House adviser Josh Gruenbaum, were described by the Kremlin as […]

Cybersecurity firm Rubrik has rolled out a sovereign version of its Rubrik Security Cloud, positioning the offering as a response to mounting pressure from governments and regulated industries to keep sensitive data under national control and outside the reach of foreign jurisdictions. Rubrik said the sovereign capability is designed to ensure that customer data, encryption keys, operations and support remain confined within specific countries or regions, aligning […]

WebAssembly, commonly shortened to Wasm, has moved from a niche browser technology to a central pillar in discussions about cloud computing, security and cross-platform software development. Once seen mainly as a way to speed up web applications, it is now being positioned by major technology firms, developers and standards bodies as a foundation for a new generation of portable, high-performance applications that run consistently across environments. At […]

GitLab has issued urgent security updates to address multiple high-severity vulnerabilities that could allow attackers to bypass two-factor authentication and disrupt service availability, prompting strong advisories for organisations running self-managed instances to upgrade without delay. The company confirmed that patched versions 18.8.2, 18.7.2 and 18.6.4 for both Community Edition and Enterprise Edition close a set of flaws affecting authentication controls and system resilience. GitLab. com, the hosted […]

A research team from the University of Tokyo has outlined a new approach to training large language models that aims to curb sensitive data leakage while preserving performance, addressing one of the most pressing challenges facing artificial intelligence developers as regulation tightens worldwide. The study, titled Crypto-LLM, proposes encrypting large volumes of training text before it is fed into a model, preventing the system from memorising personal […]

Raaga, a Chennai-based music streaming platform with a large global audience, has confirmed a significant data breach that led to the exposure of personal information linked to more than 10.2 million user accounts, triggering renewed scrutiny of data protection practices across consumer digital platforms. The company acknowledged that a database containing user details was unlawfully accessed and later advertised for sale on an underground hacking forum during […]

VISHNU RAJA
RYO YAMADA
HITORI GOTOH
IKUYO KITA