Cybercriminals are exploiting demand for AI coding tools by pushing fake Gemini CLI and Claude Code installation pages into search results, using the sites to deliver a fileless PowerShell infostealer aimed at developer workstations. The campaign, active since early March 2026, marks a sharper turn in financially motivated attacks against software teams as AI assistants become embedded in daily coding workflows. The attackers are not merely imitating […]
Hackers are exploiting unsupported F5 BIG-IP appliances to gain SSH access to enterprise Linux systems, turning trusted edge infrastructure into entry points for deeper attacks on identity systems and internal applications. A May 22 threat intelligence disclosure detailed a multi-stage intrusion that began with an exposed F5 BIG-IP load balancer and moved through Linux infrastructure, an internal Atlassian Confluence server and eventually Active Directory. The case underlines […]
Hackers are turning Middle East telecoms and hosting networks into a major command-and-control layer, exposing a regional cyber risk that now extends beyond compromised devices to the infrastructure patterns that sustain attacks. A three-month mapping of malicious activity between 1 February and 1 May identified more than 1,350 active C2 servers across 98 infrastructure providers in 14 countries, including Saudi Arabia, the UAE, Turkey, Israel, Iraq, Iran, […]
Companies are pushing vulnerable software into production even as artificial intelligence expands the speed, volume and complexity of application development across global supply chains. New industry findings show 75% of organisations often or sometimes deploy code they already know contains security weaknesses, underscoring a persistent gap between software delivery targets and risk controls. The figure marks only a limited improvement from last year’s 81%, suggesting that boards […]
India’s rapid AI adoption is exposing weak points in software supply chain security, with enterprises expanding automated development faster than their ability to detect compromised packages, unsafe containers and unverified AI components.
A 2026 software supply chain security assessment shows that about 65 per cent of organisations in India cannot detect malicious packages, while 71 per cent do not use container security tools. The findings underline a widening gap between the speed of AI-led software development and the controls needed to secure code, dependencies, models and deployment pipelines before they reach production systems.
Security teams are facing a more complex threat environment as AI coding assistants, model registries, agent frameworks and machine-learning libraries become embedded in day-to-day software engineering. AI is no longer confined to application features or analytics layers. It is becoming part of the software supply chain itself, influencing how code is written, tested, packaged and deployed.
Enterprises in India have been quick to adopt AI tools to improve developer productivity, reduce repetitive work and accelerate product releases. Yet the same shift has increased reliance on open-source packages, pre-trained models, plug-ins and automated build systems. Each of these components can introduce hidden risks if provenance, integrity and behaviour are not continuously verified.
Global software repositories are now attracting sustained attacks because they provide a direct route into enterprise development environments. Malicious npm packages rose by 451 per cent during 2025, while more than 48,000 new Common Vulnerabilities and Exposures were disclosed worldwide, a rise of about 20 per cent from the previous year.
The pressure on security teams is being amplified by the volume of AI-generated code. Developers in India are spending about 51 per cent of their time reviewing, validating and hardening code produced by AI tools. About 53 per cent treat such output only as a starting point and review every line before use, while 11 per cent rewrite AI-generated fixes from scratch.
This shift has altered the economics of software engineering. AI may reduce the time needed to draft code, but it can also transfer effort to verification, testing and security review. Weaknesses such as cross-site scripting, SQL injection and missing authorisation checks can still be reproduced by automated tools, particularly when developers rely on generated code without adequate scrutiny.
Governance is emerging as another area of concern. Nearly 97 per cent of organisations surveyed said they had certified AI model governance programmes, but only 59 per cent claimed full provenance visibility across production environments. About 48 per cent still needed a week or longer to produce audit-ready compliance evidence.
That gap points to a difference between policy and enforceable control. Many enterprises have AI governance frameworks on paper, but fewer can prove where every model, library, container image and software artefact came from, how it changed, who approved it and whether it complies with internal policy.
CERT-In has also warned that software supply chain compromises are increasingly targeting developer tools and trusted repositories. Its April 2026 activity note referred to attacks affecting npm, PyPI, GitHub Actions and container registries, including incidents involving Checkmarx, Trivy, LiteLLM, Axios, Telnyx and npm packages linked to the CanisterWorm campaign. The payloads observed in these attacks included credential harvesting, data exfiltration, remote execution and persistence within developer systems.
Model registries have added another layer to the risk. Around 1.4 million new AI artefacts were published on Hugging Face during 2025, representing 58 per cent of all new software packages tracked in one assessment. Researchers identified 495 malicious AI models in public repositories with active payloads capable of credential theft, command execution and reverse-shell activity, along with 969 malicious AI-agent skills designed to exploit developer environments and automation workflows.
For enterprises in India, the challenge is sharpened by the country’s role as a major software engineering and global capability centre hub. Bengaluru, Hyderabad, Pune, Chennai and Gurugram host large engineering teams serving banking, retail, telecoms, manufacturing and cloud services. These centres are increasingly responsible not only for maintenance work but also for product development, AI integration and security-sensitive digital platforms.
Regulatory and customer expectations are also tightening. Buyers are asking for software bills of materials, vulnerability disclosure processes, provenance records and proof that build pipelines are protected. CERT-In’s technical guidance on SBOM, QBOM, CBOM, AIBOM and HBOM has emphasised regular updates, vulnerability exploitability exchange documents and staff training around software supply chain visibility.
Security leaders are therefore moving towards stronger controls across development pipelines. These include automated malicious package detection, container image scanning, secrets detection, signed artefacts, dependency pinning, model provenance checks, policy enforcement in CI/CD systems and continuous monitoring of developer environments.
The investment case is becoming harder to ignore. Software supply chain attacks can bypass perimeter defences because they enter through trusted development channels. Once inside, malicious packages can steal credentials, alter builds, move into cloud environments or compromise downstream customers. AI raises the stakes because it can accelerate both legitimate development and attacker experimentation.
Cisco has issued an urgent security fix for a maximum-severity flaw in Secure Workload that could let unauthenticated attackers obtain Site Admin privileges and reach sensitive enterprise resources through internal REST API endpoints. The vulnerability, tracked as CVE-2026-20223, has been assigned a CVSS v3.1 base score of 10.0, the highest rating under the widely used severity system. It is classified as CWE-306, or missing authentication for a […]
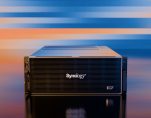
SINGAPORE – Media OutReach Newswire – 21 May 2026 – Synology today announced the general availability of PAS7700, the company’s first active-active, all flash NVMe storage system. Built for mission-critical workloads, PAS7700 delivers enterprise-grade performance, uninterrupted resilience, and optimized operational efficiency.
Synology PAS7700 delivers ultra-high performance, active-active availability and sub-millisecond latency for mission-critical workloads.
As AI, data analytics, and virtualization platforms continue to reshape how Singapore enterprises operate their IT infrastructure, storage is no longer merely a place to keep data. It has become the foundation behind core operational applications. As a result, organizations are placing greater demands on access speed, service continuity, and long-term operational stability. This is also why enterprises are increasingly seeking high-performance storage platforms that can maintain reliable operations over time.
“PAS7700 reflects Synology’s 25+ years of experience in storage and our close collaboration with enterprise customers to address evolving requirements for high availability, performance, and scalability,” said Bie-i Chu, Executive Vice President of the Synology NAS Group. “After a year of extensive real-world validation through our enterprise proof-of-concept program, PAS7700 is field-proven to deliver high reliability and performance, while helping customers lower total cost of ownership (TCO).”
A Storage Platform for Mission-Critical Systems PAS7700 is equipped with dual controllers and 48 NVMe SSD bays in a 4U chassis, and can scale up to 1.65 PB of raw storage capacity with up to seven expansion units. The system supports both file and block storage and offers broad protocol support, including NVMe-oF, iSCSI, Fibre Channel, SMB, and NFS.
With up to 2,048 GB of memory* and 100GbE networking, PAS7700 delivers up to 2 million IOPS, latency of under 1 millisecond and sequential throughput of up to 30 GB/s.
PAS7700 is designed for environments that require real-time data processing, such as virtualization, databases and large-scale data processing environments. It also targets performance-intensive and always-on workloads such as VDI, EDA and AI.
In addition, the solution is well suited for organizations operating data-intensive infrastructure in sectors such as data centers, manufacturing, semiconductor design, game development, and healthcare. These environments typically process large volumes of data concurrently and require systems that can sustain consistent performance and continuous service availability.
Designed to Minimize System Disruption One of PAS7700’s most notable strengths is its active-active architecture, which enables both controllers to operate simultaneously rather than relying on a traditional active-standby model. If one controller or a network component fails, the system can continue delivering services, significantly reducing the risk of business disruption.
The system is built with multiple protection layers to ensure high availability, including triple-parity RAID, mirrored write cache protection, IP failover, and automatic failover mechanisms.
PAS7700 also includes Continuous Availability Manager that enables enterprise IT teams to visually monitor the health status of each system component and detect and address issues quickly before they affect services.
Multi-Layer Data Protection for Enterprises Synology places strong emphasis on enterprise data protection. PAS7700 supports Self-Encrypting Drives (SEDs), providing hardware-level protection without compromising system performance.
The system also supports WORM folders and immutable snapshots, allowing snapshots to remain protected from unauthorized modification or deletion after creation, thereby reducing the risk of tampering and unauthorized data interference.
In addition, PAS7700 features Snapshot Replication and Hyper Backup that enable enterprises to build multiple layers of backup and recovery between production environments and secondary systems. This helps strengthen cyber resilience and improve data recoverability in the event of incidents or cyberattacks.
Lower Cost, Greater Efficiency Beyond performance, Synology also addresses the challenge of optimizing long-term storage investment for enterprises. As many businesses in Singapore continue expanding their data infrastructure, virtual machines and internal AI workloads, the cost of high-speed storage is exerting increasing pressure on IT environments.
PAS7700 supports both inline and offline deduplication technologies to help reduce unnecessary data usage and extend SSD lifespan. This mechanism can significantly improve storage efficiency in large-scale data environments.
In the near future, the system will also support Synology Tiering, which automatically moves infrequently accessed data to high-capacity storage systems. This helps free up high-speed NVMe resources for active applications and hot data.
The entire platform runs on DSM Enterprise, Synology’s operating system developed specifically for enterprise storage, and is designed for environments that require high performance while maintaining intuitive management and operational simplicity.
PAS7700 is now available globally through Synology’s network of partners and distributors.
*Memory module is upgradable to 1,024GB per node; 2,048GB for the whole PAS7700 system.
Hashtag: #Synology, #PAS7700
The issuer is solely responsible for the content of this announcement.
About Synology
Founded in Taiwan in 2000, Synology is a technology company specializing in network-attached storage (NAS), data backup and recovery, video surveillance, and networking solutions for businesses and individuals worldwide. Over the past two decades, Synology has continuously expanded its ecosystem to help users manage, protect, and unlock the value of data more effectively in the era of cloud, AI, and big data.
Synology’s core philosophy is to build a comprehensive hybrid-cloud ecosystem that enables businesses to protect, synchronize, and manage data through a centralized, intuitive, and easy-to-operate platform. From enterprise storage, data backup, file sharing, and collaboration to video surveillance and network infrastructure, Synology’s solutions are designed to simplify IT management and accelerate digital transformation.
Alongside ongoing technology innovation, Synology also focuses strongly on long-term stability, security, and scalability for data infrastructure. More than half of Fortune 500 companies use Synology solutions, reflecting the brand’s credibility and ability to support large-scale data operations worldwide.
GitHub has confirmed unauthorised access to about 3,800 internal repositories after an employee device was compromised through a poisoned Visual Studio Code extension, raising fresh concerns over the security of developer tools and software supply chains. The Microsoft-owned platform said it detected and contained the compromise on May 19, removed the malicious extension version, isolated the affected endpoint and began incident response measures. Its assessment so far […]
Millions of browser users have been targeted by CypherLoc, a scareware campaign built to freeze screens, mimic security alerts and push victims towards fraudulent technology support operators. Security researchers tracking the activity said about 2.8 million attacks have been observed since the start of 2026, underscoring the scale of a threat that relies less on advanced malware and more on pressure, confusion and trust in familiar security […]
Microsoft has disrupted infrastructure used by Fox Tempest, a cybercrime-enabling group accused of selling fraudulent code-signing services that helped ransomware operators disguise malware as trusted software. The action, led by Microsoft’s Digital Crimes Unit, targeted a malware-signing-as-a-service operation that allegedly abused legitimate software verification systems, including Microsoft’s Artifact Signing platform. A legal case unsealed in the US District Court for the Southern District of New York said […]
President Donald Trump has put a planned attack on Iran on hold after Gulf leaders urged Washington to allow negotiations more time, while warning that the US military remains ready for a “full, large scale assault” if no acceptable deal is reached. The decision marks a critical pause in a confrontation that has drawn the US, Iran, Israel and Gulf states into one of the most volatile […]
A fast-moving supply-chain attack has hit a broad set of npm packages linked to the @antv ecosystem, exposing developers and organisations to credential theft through malicious package versions tied to the maintainer account “atool”. The campaign, identified on May 19, 2026, appears to form part of the Mini Shai-Hulud malware wave, a self-spreading operation that has already affected other developer ecosystems through compromised open-source packages. The latest […]
Ukrainian state bodies are facing a sustained phishing campaign by the Russia-linked Gamaredon group, with attackers using weaponised WinRAR archives to deploy GammaDrop and GammaLoad malware in a multi-stage espionage operation aimed at government networks. The campaign, active since September 2025 and still evolving, has targeted Ukrainian state institutions through spoofed messages and compromised government email accounts. The emails are written in Ukrainian and designed to resemble […]
Paper Werewolf has expanded its campaign against Russian industrial, financial and transport organisations, using phishing emails, fake Adobe software updates and the EchoGather remote access trojan to deepen access inside targeted networks. The Russian-language threat cluster, also tracked as GOFFEE, was active in the March-April 2026 window with a toolset that shows a clear shift from conventional phishing toward layered intrusion chains. The latest campaign begins with […]
Tehran has moved to turn the Strait of Hormuz crisis into a new insurance and payments channel, with an Iran-linked platform branded Hormuz Safe offering maritime cargo cover tied to cryptocurrency settlement for vessels using the strategic waterway. The initiative targets shipowners, charterers and cargo interests facing sharply higher war-risk costs, disrupted routing and mounting legal uncertainty across a corridor that remains central to global energy trade. […]
By Nantoo Banerjee India’s continuous hesitancy to curb the retail oil consumption pattern despite a worldwide surge in fuel prices is inexplicable, if not unacceptable. The government, the biggest benefactor of large domestic fuel use by way of imposition of levies close to 50 percent of the retail oil prices, is not prepared to ration […]
Security researchers uncovered 47 previously unknown vulnerabilities at Pwn2Own Berlin, underscoring persistent weaknesses in enterprise software, artificial intelligence tools, operating systems and virtualisation platforms even when products are fully patched. The three-day competition, held from May 14 to May 16 alongside OffensiveCon in Berlin, awarded $1,298,250 in cash prizes. The event placed some of the world’s most widely used corporate technologies under controlled attack, with researchers targeting […]
KnowBe4 has launched CAPY, a free online family cyber safety hub aimed at helping children, parents, older adults and everyday internet users build stronger defences against scams, phishing, cyberbullying, sextortion and AI-driven abuse. The programme, formally called Cyber Awareness Program for You, marks a shift by the Tampa Bay-based digital workforce security company from corporate training into a broader public education model. It arrives as online risks […]
Arabian Post Staff -Dubai Tehran’s state broadcasting apparatus has drawn Gulf attention after a presenter fired at a target bearing the UAE flag during a televised firearms training segment, an on-air act that added a provocative media dimension to sharpening tensions between Iran and Abu Dhabi. The segment, aired on the state-run Ofogh TV network, showed a firearms instructor guiding the presenter through the handling of a […]
CertiK has warned that attackers are using artificial intelligence to scan ageing smart contracts for exploitable flaws, raising the risk level for decentralised finance projects that still rely on older code, inherited protocol designs and under-maintained deployments. The blockchain security firm’s May 15 alert points to a shift in the economics of crypto attacks. Vulnerability hunting that once required time, specialist knowledge and manual review can now […]
Kelp DAO has moved rsETH back towards normal operations after a $292 million April exploit exposed weaknesses in cross-chain verification and triggered one of decentralised finance’s largest recovery efforts of the year. The liquid restaking protocol, working with Aave and other ecosystem participants, has completed the burn of exploiter-linked rsETH on Arbitrum and begun restoring the token’s backing through a staged refill into the LayerZero OFT adapter […]
Users of JDownloader have been warned to check systems and delete suspicious installer files after attackers compromised the project’s official website and redirected selected Windows and Linux downloads to malware-laced files during a narrow but serious exposure window on May 6 and May 7, 2026. The breach affected users who downloaded the Windows “Download Alternative Installer” or the Linux shell installer from jdownloader. org during that period. […]
Gunra ransomware has expanded from a relatively narrow Windows-focused threat into a structured cybercrime franchise, raising concern among security teams as its operators shift from a Conti-derived locker to their own Ransomware-as-a-Service model. The group, first observed in April 2025, initially drew attention after attacks on five companies in South Korea. Its early malware showed similarities to Conti, the once-dominant ransomware operation whose leaked source code reshaped […]
President Donald Trump is nearing a decision on whether to revive US air strikes against Iran as diplomatic efforts to reopen the Strait of Hormuz remain stalled and military planners prepare options for a sharper phase of confrontation. Senior aides have drawn up plans that would allow Washington to resume attacks if Trump concludes that negotiations have failed. The preparations do not mean a strike order has […]



 https://www.synology.com/en-sg




