News related to
attacks

Meta has partnered with Circus SE, a leading European AI company, to extend its artificial intelligence capabilities to the defence and security sectors. This collaboration signals Meta’s growing commitment to leverage AI technologies for a range of applications, including military and security operations, aiming to strengthen both European and global defence strategies. Meta, which has been investing heavily in AI over the past few years, is shifting […]

Game Freak is poised to upend expectations with Pokémon Legends: Z-A, launching on 16 October 2025 for both Nintendo Switch and Switch 2. The title places players squarely in Lumiose City, turning the familiar Kalos region into a battleground where Pokémon and trainers share the same urban landscape. Unlike prior Pokémon titles, Z-A abandons turn-based encounters in favour of real-time combat. Trainers roam the environment, positioning themselves […]

A newly disclosed vulnerability allows threat actors to surreptitiously install arbitrary extensions on Chromium-based browsers within Windows domain environments, circumventing typical user alerts and security checks. The technique hinges on manipulating how Chrome and its derivatives store extension settings and validations in preference files. Security researchers demonstrated that by editing specific preference files in a user’s profile, an attacker can mark a malicious extension as a “component” […]

The inaugural Open Source Summit Korea is set to take place in Seoul on 4–5 November, gathering developers, community leaders, corporate adopters and policy advocates under one roof. Organisers expect a high-powered two-day event blending technical deep dives, cross-domain dialogue and community building across open source’s diverse ecosystems. The summit will host seven major tracks: Cloud & Containers, Embedded Linux, Linux, Open AI + Data, Open Source […]

SpyCloud’s 2025 Identity Exposure Report reveals that 91% of organisations reported suffering an identity-related incident in the last year, nearly double the proportion seen the year before. Data troves comprising stolen credentials, phishing logs, malware infection records and session cookies have expanded dramatically, but many firms remain overconfident in their ability to defend against evolving identity threats. The volume of distinct identity records recaptured by SpyCloud has […]

A federal judge dismissed Donald Trump’s $15 billion defamation lawsuit against The New York Times and Penguin Random House, ruling that the complaint was legally insufficient and procedurally improper. U. S. District Judge Steven Merryday criticised the 85-page document for lacking a “short and plain statement” required by the federal rules, and for including excessive laudatory language and irrelevant attacks rather than cogent legal allegations. Judge Merryday […]

/India Press Agency/

By Nitya Chakraborty Prime Minister Narendra Modi has stepped into his 75th year on Wednesday, September 17.His birthday is being celebrated by the BJP nationally. The significance is much more as PM’s 75th birthday celebrations have coincided with the centenary programmes on the founding of the RSS in 1925.On October 2 this year, Vijaya Dasami […]

The article Decoding Prime Minister Narendra Modi As A Political Leader On His 75th Birthday appeared first on Latest India news, analysis and reports on IPA Newspack.

Advertisements

Security systems observed a sharp increase in API incidents in the first half of 2025, with over 40,000 security events targeting more than 4,000 environments globally. These incidents indicate that APIs — the unseen conduits connecting apps, payments and authentication — are now at the forefront of cybercriminal strategies. Thales’ API Threat Report for H1 2025, built on Imperva telemetry, shows APIs represent about 14 percent of […]

Security researchers at ESET have identified a new malware strain called HybridPetya that combines traits of Petya and NotPetya ransomware with advanced boot-kit functionality to infect systems protected by UEFI Secure Boot. It exploits the vulnerability CVE-2024-7344 in the Howyar “Reloader” UEFI application to bypass signature checks, allowing unverified code execution. HybridPetya was first spotted when samples uploaded to VirusTotal in February 2025 caught the eye of […]

Australia’s Reserve Bank, through Assistant Governor Brad Jones, has warned that the era of stability and integration following the Cold War has given way to a more contested strategic environment that carries elevated risk for governments, financial institutions, and markets. At a FINSIA event in Sydney on 12 September, Jones declared that “the era of the peace dividend is over,” citing geopolitical, technological and operational disruptions reshaping the global financial order.

Jones described the international security and economic system as undergoing “seismic adjustment — on a scale and speed unseen in eight decades.” He flagged multiple forces contributing to instability: rising strategic rivalry, weakening tenets of the rules-based order, frictions in globalisation, and increasing emphasis on self-insurance by nations and firms against a broader set of possible harms.

Technological advances form one front of the risk profile. Jones spoke of an expanding surface for cyber-attacks driven by digitalisation, concerns over concentration risk in cloud services, and quantum computing’s looming threat to encryption systems. Artificial intelligence, while promising productivity gains, poses risks of misinformation, fraud, and systemic instability due to herding behaviour.

Critical infrastructure exposures were cited as especially vulnerable: telecommunications networks, the electrical grid, payment systems, and market infrastructure. Jones referenced a recent example in Europe, where cascading power outages in the Iberian Peninsula disrupted both households and economic activity, pointing out that such disruptions would be far more dangerous if key financial infrastructure were affected.

To respond, the RBA is pressing for what it calls an “anti-fragile” financial system—one not simply capable of withstanding shocks but able to adapt and improve because of them. Innovation, competition, and efficiency are being positioned not as opposing goals to resilience but as complementary. Initiatives under way include work with industry to bolster payments resilience, frameworks to ensure that future payments systems embed reliability and recoverability, migration to quantum-safe encryption standards, and reforms aimed at enabling new entrants in financial market infrastructure to reduce concentration risk.

These concerns build on earlier warnings in the RBA’s Financial Stability Review, which noted that heightened geopolitical tensions, trade uncertainty, and technological vulnerabilities could interact with existing financial system risks. The review flagged operational risks from interconnectedness and dependency on third parties for infrastructure and services.

The shift has implications for monetary policy, regulatory oversight, and business strategy. Regulators are likely to place greater emphasis on risk scenarios involving geopolitics, cyber-threats and supply-chain disruptions; financial institutions will need to review and stress-test against non-traditional threats while ensuring agility; and policy frameworks may need to evolve to address threats outside standard macroeconomic shocks.


A surge in cyberattacks targeting U. S. schools and colleges is being met with increasing resistance, but experts warn that serious vulnerabilities remain. Data from multiple cybersecurity firms and institutions show that ransomware incidents rose by 23% year-on-year for the first half of 2025 among educational organisations—around 130 confirmed or probable attacks—at an average ransom demand of approximately US$556,000. Check Point Research finds that from January to […]

By Nitya Chakraborty The two day uprising in Nepal on September 8 and 9 resulting in the ouster of the KPS Oli government following the attacks and burning of the Parliament Building, Supreme Court and the official and private residences of the present and former powerful ministers, was an expression of total revolt by the […]
A pioneering study now suggests that heart attacks may, in some cases, result from infectious processes rather than solely lifestyle and cholesterol risks. Researchers from Finland and the UK have uncovered compelling evidence that bacterial biofilms hidden within arterial plaques can lie inactive for decades and, when triggered by a viral infection or other external stimulus, may ignite inflammation, rupture arterial plaques, and ultimately lead to myocardial […]

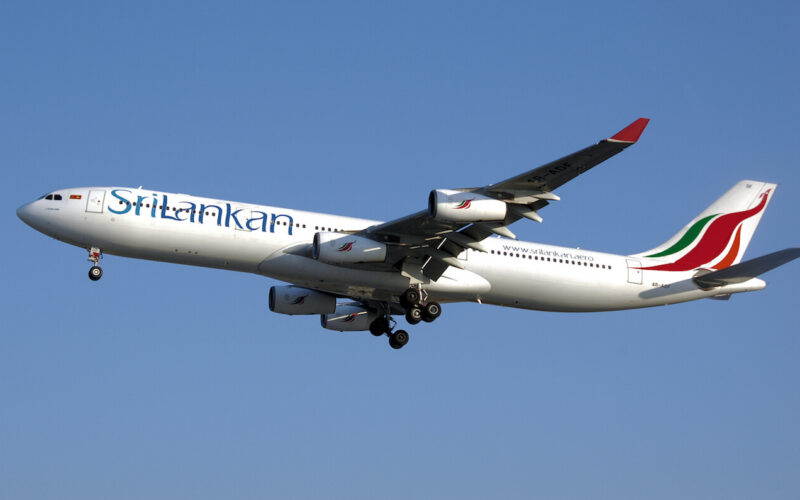
SriLankan Airlines has suspended services to Kathmandu after authorities closed Tribhuvan International Airport amid nationwide unrest, forcing cancellations on the Colombo–Kathmandu route and disrupting onward travel plans.

Airport officials said flight operations at Kathmandu would remain shut until the evening as security forces moved to stabilise the capital, while armoured patrols and curfews kept streets largely empty following two days of violent demonstrations. Airline pauses Kathmandu services amid escalating unrest.

Protests that began over corruption and economic grievances have turned deadly, with soldiers guarding parliament and key government buildings after arson attacks and clashes. Reuters reported at least 19 fatalities over 48 hours and said the turmoil prompted a nationwide shutdown affecting aviation, retail and public services.

Knock-on effects spread across regional air corridors. Multiple Kathmandu-bound flights were diverted to India, including four routed to Lucknow as the closure took effect, while IndiGo extended a temporary halt of services to and from Kathmandu to the early evening. Other carriers announced cancellations through the day as they assessed security and operational risks.

SriLankan confirmed the cancellation of flights UL181 and UL182 on Wednesday and advised ticketed passengers to contact their booking channels. Local news outlets in Colombo said the airline’s suspension would remain until further notice, aligning with guidance to monitor official updates as authorities reviewed conditions at the airport.

Regional governments urged caution for travellers. India advised its citizens to defer trips to Nepal and for those already in the country to remain indoors, as curfews and transport disruptions left tourists and business travellers stranded across Kathmandu Valley and beyond.

Live updates from Kathmandu indicated authorities were weighing phased resumptions of essential services alongside crowd-control measures. Airports and transport links were prioritised for restoration once security agencies deemed conditions manageable, with the army coordinating road clearance and fire response in affected districts.

Airlines across South Asia adjusted schedules through the afternoon, with Indian and regional carriers cancelling or retiming Kathmandu rotations while offering waivers. Public statements from operators noted the situation remained fluid and that customer notifications would follow as airspace and airport status changed.

SriLankan’s decision underscores how quickly a single-airport closure can ripple through a network heavily reliant on narrow time buffers and daylight slots into high-altitude hubs. For passengers booked to or through Kathmandu, carriers advised monitoring flight status pages and staying in contact with travel agents as curfew orders and airport operating hours evolve.

The cybersecurity community is confronting a highly evolved phishing campaign that exploits Google’s no-code AppSheet platform to harvest credentials and two-factor authentication codes. Attackers are sending authentic-looking emails from the legitimate domain noreply@appsheet. com—circumventing common defences such as SPF, DKIM and DMARC—and impersonating Meta to pressure users into submitting sensitive data. On 20 April 2025, AppSheet-originated emails made up 10.88 percent of all phishing attempts intercepted by […]

Poland activated air defences and scrambled fighter jets after drones from Russia crossed into its airspace during overnight strikes on Ukraine, with the military confirming it used weapons to neutralise targets. The Operational Command said Polish airspace was “repeatedly violated by drone-type objects” and described an ongoing operation to identify and destroy them. Authorities placed ground-based systems and radar on maximum alert while Polish and allied aircraft […]

Protesters breached Nepal’s federal parliament complex in Kathmandu and set parts of the building on fire on Tuesday, escalating a youth-led movement that has convulsed the country and prompted the prime minister’s resignation. Authorities confirmed fatalities and hundreds of injuries over two days of clashes that centred on the New Baneshwar area housing the legislature. The death toll rose to 19 after security forces used live ammunition, […]

Matein Khalid My readers and friends know that I have been a boring perma-bull on gold since early 2024, when it became obvious that the People’s Bank of China was accumulating gold bullions as a hedge against an overvalued King Dollar and a capricious White House, which had just seized $300 billion in Russian central bank reserves to punish Putin’s invasion of Ukraine. The bullish gold trade […]

A wave of ransomware incidents has incapacitated over 300 co-operative banks across India, exposing deep vulnerabilities tied to outdated VPN-based security. These attacks underline the urgent need for a shift towards modern access frameworks such as Zero Trust Network Access. Operational disruptions began when C-Edge Technologies—a key IT provider to numerous co-operative banks—was targeted by ransomware on 31 July 2024. NPCI responded swiftly by isolating C-Edge from […]

Undersea cables in the Red Sea were severed on September 6, 2025, causing significant internet disruptions across parts of Asia and the Middle East. The affected cables include the South East Asia–Middle East–Western Europe 4 and the India–Middle East–Western Europe, both vital for regional connectivity.

Microsoft reported increased latency for users in the Middle East, while NetBlocks, a digital rights group, confirmed that the outages impacted countries such as India and Pakistan. The disruptions have also affected cloud services, with Microsoft Azure experiencing service degradation due to rerouted traffic.

The cause of the cable cuts remains unclear. While there is concern that the Houthi rebels in Yemen may have targeted the cables as part of their campaign related to the Israel-Hamas conflict, the group has denied responsibility for such attacks. In early 2024, the Houthis had threatened to target undersea cables, but no direct evidence has been presented linking them to the current incident.

Kraken’s Chief Security Officer, Nick Percoco, has issued a warning to users about a sophisticated phishing campaign impersonating the platform. Attackers are dispatching emails that replicate Kraken’s branding—with near-identical logos, fonts and messaging—to pressure recipients into taking urgent action. The emails allege the need to accept “updated terms” within a two‑day window, a tactic intended to prompt hasty decisions. In nearly every instance, the sender urges recipients to download remote desktop software such as AnyDesk under the guise of offering support. Percoco emphasises that Kraken will never request installation of such tools from users.

Such phishing attempts exploit both visual authenticity and psychological manipulation—cultivating a sense of urgency to override caution. According to official guidance, Kraken will only use verified domains—including @kraken. com, @futures. kraken. com, @email2. kraken. com, @email. krak. app and other specific, approved addresses—to communicate with users. Any other source should be treated as suspicious.

This incident reflects a broader escalation in phishing tactics across the crypto sector. Industry data indicates that phishing attacks surged more than 200% in August, resulting in losses exceeding $66 million. One single breach accounted for $55 million in stolen funds. Abnormal AI, a cybersecurity firm, attributes the elevated threat level to more advanced techniques—emails originating from older, seemingly trustworthy domains, employment of social engineering, and polished language devoid of traditional red‑flag keywords. These newer attacks are designed to bypass legacy email filters and evade automated detection.

Users are urged to remain vigilant and adopt a security-first mindset. The most effective defence measures include verifying sender addresses, suspecting communications that evoke fear or demand immediate compliance, and avoiding email links entirely—especially those prompting software installation. Instead, users should always navigate directly to Kraken’s official URL (), ideally via a bookmarked link, and contact support through trusted channels if unsure.

Kraken’s approach is rooted not only in technological safeguards but also in cultivating user awareness. Percoco has previously underscored that phishing and social engineering are among the most common threats to both users and employees. Kraken’s layered filtering and a security-conscious culture help reduce risk, though no system is foolproof. Humans remain the critical last line of defence.

With trusts at stake, exchanges are under mounting pressure to enhance transparency and user education. Some platforms have introduced anti‑phishing codes or digital signatures to help users verify authenticity. While Kraken currently relies on verified domains and user education, the challenge continues to evolve as attackers adopt more deceptive techniques.

A wave of data indicates that staff reliance on informal messaging platforms, particularly WhatsApp, is opening critical cybersecurity gaps across organisations. The 2025 KnowBe4 Africa Annual Cybersecurity Survey shows that 93 per cent of African professionals use WhatsApp for work purposes—surpassing email and even messages sent via enterprise-grade tools. Alarmingly, up to 80 per cent of these users operate from personal devices that often lack proper management […]

Okta Threat Intelligence has uncovered a widespread campaign exploiting malicious online ads to tempt hotel and vacation rental professionals into disclosing access credentials. Attackers have been deploying paid search advertisements on platforms such as Google Search, impersonating familiar hospitality service providers. These deceptive ads lead victims to counterfeit login portals of cloud‑based property management and guest messaging systems, with the goal of harvesting usernames, passwords and one‑time authentication codes.

The adverts specifically mimic legitimate service providers—Okta researchers identified at least thirteen hospitality‑focused brands being spoofed. Rather than redirecting users to authentic company sites, these ads channel them to typosquatted domains that host visually convincing but fraudulent login pages. Through these pages, attackers collect credentials and MFA codes, undercutting security even when multi‑factor authentication is in place.

The phishing sites also incorporate tracking capabilities—collecting geolocation, session data, bot detection metrics and analytics—to better tailor the campaign and measure its effectiveness.

This strategy exemplifies the growing menace of malvertising, where advertisements themselves become vectors for malware distribution or phishing. Malwarebytes data reflects dramatic growth in such campaigns: a 42 per cent month‑on‑month escalation in fall 2023, followed by another rise of 41 per cent between July and September. Malicious ads frequently appear alongside legitimate search results, granting them apparent credibility and increasing the chance of successful deception.

Experts point out the dual advantage these tactics offer to threat actors: extensive reach through ad networks and a veneer of trust derived from the proximity to legitimate search results.

The hospitality sector faces unique vulnerabilities as hotels and rental operators increasingly rely on cloud systems to manage bookings, guest interactions and operational workflows. With projections indicating that by 2028 some 76 per cent of travel and tourism revenues will be generated online, these sectors have become especially tempting targets.

This campaign represents a convergence of two escalating cybersecurity concerns: the explosive growth of malvertising and the rising exposure of hospitality infrastructure to credential-based attacks. While the ads serve as the initial lure, the fraudulent credential capture enables potential downstream compromises across cloud services that manage guest data, reservations and even messaging systems.

For hotel and rental operators, the implications are severe—a breach of access credentials might cascade into broader system intrusions, guest data exposure and operational disruption. Preventive measures should include rigorous verification of URLs before entering credentials, vigilant monitoring of sponsored search results for impostor ads, widespread staff awareness and training, and robust technical controls like domain-based message authentication and behavioural anomaly detection.

Journalistic integrity demands careful cross-verification of details. Okta’s findings were drawn from their threat intelligence and threat detection capabilities tailored to enterprise identity environments. Malvertising trends are substantiated by independent cybersecurity data from industry researchers such as Malwarebytes. The convergence of these findings draws a consistent picture: the hospitality industry must brace for sophisticated phishing campaigns delivered via the same channels they rely on for marketing.

By Nitya Chakraborty Prime Minister Narendra Modi’s bilateral talks with the Chinese President Xi Jinping on Sunday at Tianjin in China on the sidelines of Shanghai Cooperation Organisation (SCO) summit have sent some very positive signals which may herald the evolution of an independent foreign policy of India voicing the interests of the Global South. […]
VISHNU RAJA
RYO YAMADA
HITORI GOTOH
IKUYO KITA