News related to
attacks

The rising tensions in the Red Sea, particularly due to Houthi rebel threats against shipping vessels, have led to a sharp increase in insurance premiums for maritime companies operating in the region. The volatile security environment, combined with the risk of targeted attacks on vessels linked to countries like the UK, US, or those having called at Israeli ports, has left insurers increasingly cautious about providing war-risk cover for ships transiting the waters.

War-risk insurance premiums have skyrocketed to as much as 2% of a vessel’s value for a single transit through the Red Sea. This steep increase reflects heightened concerns following several incidents, most notably the August 21 strike on the oil tanker Sounion, which was carrying about one million barrels of crude oil at the time. Though the tanker was safely towed without spillage, the attack underscored the vulnerability of maritime assets in the region, adding pressure on insurers and shipping companies alike.

The market for insuring ships passing through this critical shipping route has narrowed as smaller insurers retreat from offering coverage. A limited number of firms, mostly high-risk underwriters, continue to offer protection, but at significantly elevated costs. Industry insiders have noted that some vessels, especially those perceived as high-value targets for potential attacks, are struggling to secure any coverage at all.

The risks have intensified with the Houthis’ declaration that ships with certain affiliations would face potential attacks. While traditionally, war-risk cover has been available, the situation is unprecedented with underwriters outright refusing coverage, citing the region’s escalating risks. For shipping operators, this poses not only financial but also operational challenges, as the necessity of traversing the Red Sea for global oil and goods trade remains critical despite the threats.

A consortium of insurance underwriters led by Brit provided the war-risk cover for the Sounion, alongside firms such as Antares, Iquw, Hamilton, and others. However, many of these insurers have been notably silent regarding the details of coverage, which underscores the sensitivity and complexities of offering insurance in such a volatile region. The consortium’s willingness to continue offering protection contrasts with smaller players who are increasingly unwilling to take on such risks.

The situation has compounded concerns for global shipping companies, especially with the strategic importance of the Red Sea in connecting Europe, the Middle East, and Asia. As attacks threaten to disrupt not just oil shipments but broader trade routes, the rising insurance costs may further exacerbate existing challenges for global supply chains.

Maritime experts are urging caution as geopolitical tensions in the region show little sign of abating, with insurers increasingly exercising selective underwriting processes to minimize exposure. Ships perceived as having higher exposure to attacks are now finding it exceedingly difficult to secure coverage at any price. This selective process not only reflects the complexities of the situation but also highlights the unpredictable nature of risk in conflict-prone areas like the Red Sea.

As shipping companies scramble to mitigate these rising costs, the long-term impact on global trade remains a looming concern. Many in the industry are questioning how long they can sustain operations under such financial pressure and whether alternative routes or additional security measures might provide a viable solution in the coming months.

A significant data breach has come to light involving Star Health and Allied Insurance Co., one of India’s leading health insurance providers. The breach reportedly involves the unauthorized access and dissemination of sensitive customer data through Telegram chatbots, raising serious concerns about cybersecurity measures in the insurance sector. The incident was first reported by cybersecurity experts who detected unusual activity linked to the company’s data infrastructure. This […]

Ethena Labs, the issuer of the USDe stablecoin, has confirmed a security breach involving its website domain. Although the underlying USDe protocol remains intact, the company has issued a warning advising users to avoid interacting with its front-end interface until further notice. The attack on Ethena Labs’ website came to light after users reported unusual activity. According to the company’s statement, the breach affected only the website’s […]

Cybersecurity research reveals a staggering 70% increase in Distributed Denial of Service (DDoS) attacks across Gulf countries since the beginning of the year. The escalation highlights a troubling trend, with the UAE and Saudi Arabia being the primary targets. The UAE faces 40% of the region’s total DDoS incidents, while Saudi Arabia encounters 26%, indicating a concentrated focus of cybercriminal activities on the region’s most significant economies. […]

A new phishing scam is targeting personal Gmail accounts, with fraudsters impersonating corporate directors to gain trust and access to sensitive information. The scam has sparked concern among professionals, particularly in industries where data breaches and online fraud are on the rise. The emails, originating from seemingly legitimate addresses, have raised questions about how personal Gmail accounts are being accessed and exploited. The scam unfolded when multiple […]

Sparkle, Italy’s premier international telecommunications provider, has joined forces with Nexim Global, an Italo-American telecom firm, to enhance global internet connectivity and cybersecurity services. This partnership, announced during the IBC2024 conference, aims to offer a comprehensive suite of internet protocol (IP) services and distributed denial-of-service (DDoS) protection to clients worldwide. The collaboration between Sparkle and Nexim Global is set to significantly impact the telecommunications landscape, integrating Sparkle’s […]

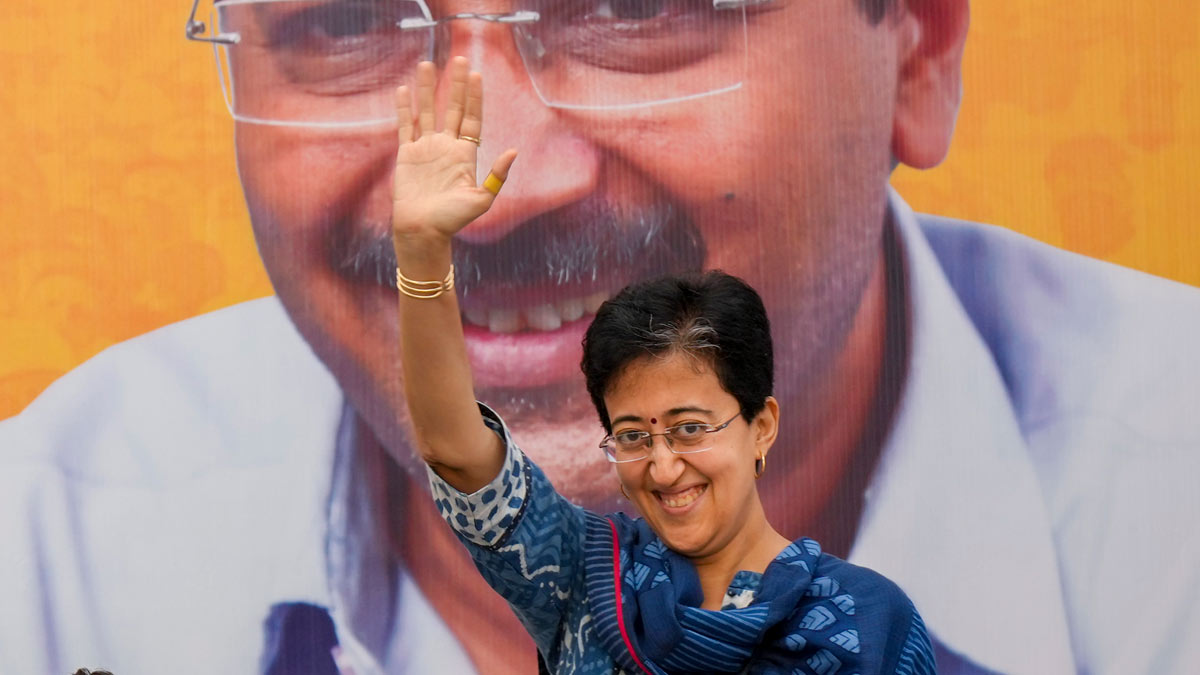
By Sushil Kutty It is Atishi and it will be Atishi who will be the next Delhi Chief Minister, to succeed Arvind Kejriwal. The ‘Marlena’ surname she dropped in 2019 when contesting the Lok Sabha election from East Delhi. Point to note, however, is Atishi will be Chief Minister only till the next assembly elections, […]
Advertisements

NL-ix and Nokia have launched a significant upgrade to their network security, introducing Nokia’s Deepfield Defender to combat distributed denial-of-service (DDoS) attacks. This deployment, one of the largest of its kind in Europe, aims to bolster the resilience of NL-ix’s internet exchange infrastructure. The collaboration focuses on deploying Nokia’s advanced Deepfield Defender, a system designed to identify and neutralize DDoS threats in real-time. The solution enhances NL-ix’s […]

Operant AI, a key player in the field of runtime AI application protection, has successfully secured $10 million in Series A funding. The investment round was co-led by SineWave Ventures and Felicis, with additional contributions from Alumni Ventures, Massive, Calm Ventures, and Gaingels. This latest funding will bolster Operant AI’s mission to enhance security measures for cloud APIs and applications, addressing an increasing demand for robust cybersecurity solutions.

Founded in 2020, Operant AI focuses on safeguarding cloud environments through its innovative approach to application protection. The company’s technology integrates machine learning algorithms to monitor and secure API interactions in real time, offering advanced defenses against emerging threats. This Series A funding will enable the company to expand its team, enhance its product offerings, and accelerate go-to-market efforts.

The need for sophisticated cloud security solutions has never been more pressing. As organizations increasingly rely on cloud-based infrastructure, the attack surface for potential cyber threats expands. Operant AI’s technology addresses this challenge by providing a proactive defense mechanism that anticipates and neutralizes threats before they can cause harm. This proactive approach is crucial as traditional security measures often lag behind the rapidly evolving threat landscape.

SineWave Ventures and Felicis, both renowned for their strategic investments in cybersecurity, bring extensive experience and resources to Operant AI’s growth. SineWave Ventures is known for its focus on investing in high-potential, early-stage companies, while Felicis has a track record of nurturing innovative startups in the tech sector. Their co-leadership in this funding round reflects confidence in Operant AI’s potential to make significant strides in cloud security.

Alumni Ventures, Massive, Calm Ventures, and Gaingels, each bringing unique expertise and networks, further strengthen Operant AI’s investment base. Alumni Ventures, with its deep connections within the academic and entrepreneurial communities, will support Operant AI’s recruitment and research efforts. Massive, known for its investments in scalable tech solutions, aligns well with Operant AI’s growth strategy. Calm Ventures, with its focus on emerging technologies, will help drive innovation, while Gaingels offers valuable connections and support for diversity and inclusion in tech.

The cybersecurity landscape is evolving rapidly, with cloud environments becoming increasingly complex and targeted by sophisticated attacks. Operant AI’s solution stands out by leveraging AI to provide dynamic, real-time protection. This method contrasts with traditional static security measures that may not adequately address the fast-paced nature of modern cyber threats.

One of the notable aspects of Operant AI’s technology is its ability to adapt to new threat vectors. By continuously learning from ongoing data and threat patterns, Operant AI’s system evolves to address new security challenges, offering a level of adaptability that is crucial in today’s cyber threat environment.

This funding round positions Operant AI to capitalize on a growing market for cloud security solutions. The global cybersecurity market is projected to continue its robust growth, driven by increasing cyber threats and the expanding use of cloud services. Operant AI’s innovative approach aligns well with these trends, positioning it as a significant player in the cybersecurity space.

As Operant AI moves forward, it will focus on expanding its product capabilities and market reach. The additional funding will support initiatives to enhance its technology stack, develop new features, and scale its operations to meet the demands of a growing customer base. With a solid foundation of investment and expertise, Operant AI is poised to advance its mission of providing cutting-edge protection for cloud-based applications and APIs.

In an increasingly digital world, online security and privacy have become paramount, especially in regions like the Middle East, where business, politics, and technology are booming. As more individuals and companies in the UAE and surrounding countries embrace digital tools, the demand for secure internet access has risen sharply. One solution that has gained popularity is the use of a free VPN (Virtual Private Network), offering users […]

Microsoft’s ambitious leap into the world of generative AI with its Copilot tool has garnered widespread attention. Positioned as an AI-powered assistant integrated into nearly all Microsoft 365 services, Copilot promises to revolutionize the way businesses operate. The company is marketing Copilot as a game-changer, boosting productivity and potentially transforming enterprise workflows. Its integration into Microsoft’s suite of products suggests a long-term commitment to AI-powered solutions. However, as Copilot’s adoption accelerates, security concerns are casting a shadow over its potential. Industry analysts and cybersecurity experts are sounding the alarm about the security vulnerabilities this generative AI assistant may introduce, especially when utilized alongside Microsoft 365.

For Microsoft, Copilot has already proven to be a substantial revenue driver. Reports of a 60% surge in sales within a single quarter show that enterprises are interested in leveraging its capabilities. The tool’s rapid expansion into organizations of all sizes highlights the growing demand for AI-driven solutions in enhancing productivity. According to Microsoft’s CEO, the growth of Copilot for Microsoft 365 has outpaced all other software launches for the office suite, an indication that businesses are embracing the potential efficiency gains. This uptake is not surprising, given the promise of Copilot to automate tasks, simplify workflows, and assist employees with complex processes.

Despite these impressive sales figures, the challenges ahead may undermine Copilot’s continued growth. Experts have flagged several security vulnerabilities that could derail its adoption, particularly for enterprise users handling sensitive data. The integration of AI into essential productivity tools opens up a host of security questions, and researchers are urging caution as organizations explore the use of Copilot in their operations. While the technology has significant upside, its security risks must be addressed to ensure long-term success.

One of the primary concerns surrounding Copilot is the nature of its access to corporate data. Given that Copilot functions as an AI assistant, it requires extensive access to company files, emails, documents, and other sensitive information stored within Microsoft 365. The scope of this access is where the security risks begin. By design, the AI needs to draw upon vast amounts of data to provide relevant and contextually appropriate assistance to users. However, this same feature could potentially open up new vulnerabilities.

The potential for misuse of this access is a major worry. Hackers, insiders, or even external parties could exploit security gaps, gaining unauthorized access to confidential information. The AI’s deep integration with core systems provides an appealing target for bad actors. This is compounded by the fact that AI systems like Copilot can be difficult to monitor. Their operation often involves learning and making decisions based on the data they interact with, making it challenging for organizations to fully control or predict their actions.

While Microsoft has stressed that Copilot’s design includes stringent security measures, including encryption and advanced threat detection, some experts remain skeptical. Security protocols that might be effective for conventional software may not fully protect systems that rely on generative AI. The sheer volume of data that Copilot processes raises additional concerns about how well security measures can keep pace. Analysts from cybersecurity firms are warning that traditional security strategies may need to evolve to address these unique risks.

There’s also concern about the risks posed by inadvertent misuse within companies. Employees using Copilot could unintentionally expose sensitive data or trigger breaches without realizing it. The AI’s ability to pull from a wide array of corporate resources means it could retrieve or expose information that should remain confidential, even if done unintentionally. Ensuring that Copilot’s access is limited appropriately and that users understand the security implications of their interactions with the AI is essential. Organizations must invest in rigorous training and develop protocols to prevent accidental data leaks or breaches.

Another layer of concern relates to how Copilot integrates with existing Microsoft 365 features. Many organizations have already invested heavily in Microsoft’s cloud services, and Copilot’s introduction adds another complex layer to their systems. This interconnectedness, while beneficial for workflow automation, creates a situation where vulnerabilities in one part of the system could compromise the entire infrastructure. If Copilot becomes an entry point for cyberattacks, the potential damage could extend across the entirety of an organization’s Microsoft ecosystem.

Gartner has added to the chorus of concerns, with warnings about the potential security challenges that enterprises could face when using Copilot in conjunction with Microsoft 365. Their assessment has caught the attention of IT professionals, some of whom are hesitant to fully embrace the technology. Despite Microsoft’s assurances that Copilot is secure, there’s a growing belief that the risk environment for AI-powered productivity tools is still evolving. Enterprises that operate in sectors requiring strict data protection standards, such as finance or healthcare, may find it particularly difficult to justify adopting Copilot without robust security guarantees.

Additionally, the complexity of generative AI introduces concerns about transparency. AI systems, by their nature, can be opaque. Their decision-making processes are often not fully understood, even by the engineers who design them. This creates a dilemma for organizations that need to ensure compliance with regulations and internal security policies. If Copilot makes a decision or provides an output that leads to a security issue, it may be difficult to trace the root cause or assign responsibility. This lack of transparency could make some organizations wary of trusting their most sensitive information to a generative AI system.

There are also issues of compliance and regulatory challenges. For companies that operate in highly regulated industries, the introduction of AI assistants like Copilot may require new compliance strategies. Questions surrounding data privacy, user consent, and cross-border data transfers could complicate the use of AI tools, particularly in regions with stringent privacy laws such as the European Union’s General Data Protection Regulation (GDPR). Companies will need to ensure that Copilot’s operation aligns with these legal frameworks to avoid regulatory pitfalls.

Microsoft, for its part, appears to be aware of these concerns and is likely working to address them. The company has a track record of adapting its security practices in response to emerging threats, and it’s reasonable to assume that they will continue to improve Copilot’s security as new risks emerge. However, until these improvements are fully realized, the apprehension surrounding Copilot’s security is unlikely to dissipate entirely.

Despite these warnings, it’s also possible that fears of Copilot’s security vulnerabilities are overstated. Microsoft has long been a dominant player in enterprise software, and its reputation for securing its platforms is strong. The company is no stranger to navigating security concerns, and its investment in AI safety and security research could lead to breakthroughs that mitigate the risks associated with Copilot. Furthermore, early adopters of Copilot may find that the productivity gains outweigh the security risks, particularly if their operations don’t involve handling highly sensitive data.

Yet, the caution expressed by cybersecurity experts and analysts cannot be ignored. The introduction of AI-powered tools like Copilot represents a significant shift in how businesses manage their data and productivity. The allure of AI-enhanced workflows is undeniable, but the accompanying security risks could be enough to slow Copilot’s momentum, especially among large enterprises that prioritize data security above all else.


Check Point Software Technologies has been distinguished as a leader in the GigaOm Radar report for Security Policy as Code. The company’s recognition highlights its significant advancements in automating security policy management through code, reflecting an increasing trend towards integrating security into the development lifecycle. Security Policy as Code (SPaC) has emerged as a critical component in modern cybersecurity strategies, providing organizations with a means to define, […]

The International Monetary Fund (IMF) has released its comprehensive research assessing the cyber resilience of the ecosystem supporting central bank digital currencies (CBDCs). The study, published at the end of August, addresses the growing need for updated payment systems and highlights both the opportunities and challenges presented by CBDCs. As central banks worldwide explore digital currencies, the IMF’s report stresses the critical importance of cybersecurity. According to […]

A rare Bitcoin mining event has recently made headlines as a solo miner successfully processed a block, earning approximately $180,000. The achievement, marked by Block 860749 on September 10, underscores the intense competition and difficulty involved in Bitcoin mining. Block 860749, which was verified and added to the Bitcoin blockchain on the specified date, included 5,935 transactions. The reward for this block amounted to 3.169 Bitcoin, translating […]

Oracle co-founder Larry Ellison revealed plans to bolster cloud security by integrating AI-driven autonomous systems to preempt and neutralize cyberattacks. During Oracle CloudWorld, Ellison highlighted how these systems would revolutionize the industry by preventing data breaches like ransomware and identity theft. This move aligns with Oracle’s multicloud strategy, showcased by its partnership with AWS. Ellison emphasized the critical role of AI in ensuring a seamless, secure cloud […]

Ente, a new contender in the photo storage and management market, is making waves as a privacy-focused alternative to Google Photos. Launched by former Google engineer, Ente offers both hosted and self-hosted solutions, addressing growing concerns over data privacy and control. The genesis of Ente dates back to 2019 when its founder, disillusioned by Google’s data practices, sought a more private way to manage and store personal […]

By Nitya Chakraborty Bangladesh Interim Head Dr. Muhammad Yunus has invited Indian Prime Minister Narendra Modi for talks in New York in the last week of September when both of them will be attending the session of United Nations general assembly .So far, there has been no response from the Indian Government sources. In fact, […]

The Internet of Things (IoT) market is set to experience exponential growth over the next decade, with projections estimating its value will soar to $5.33 trillion by 2032, according to industry forecasts. This surge is driven by technological advancements, increasing cloud adoption, and a steady rise in wireless networking capabilities, making IoT an integral part of modern industries and day-to-day life. Research highlights a compound annual growth […]

OneDegree, a pioneering force in digital asset insurance across Asia, has forged a strategic partnership with Walaa Cooperative Insurance Company, a prominent player in Saudi Arabia’s insurance and reinsurance sector. This collaboration aims to address the burgeoning needs of digital asset security, merging OneDegree’s innovative approach with Walaa’s established market presence.

The alliance between OneDegree and Walaa Cooperative Insurance Company marks a significant step in the evolution of insurance solutions tailored for digital assets. As digital currencies and blockchain technologies gain traction globally, the necessity for specialized insurance products to safeguard these assets has become increasingly apparent. This partnership leverages OneDegree’s expertise in the digital insurance space with Walaa’s robust infrastructure and regional market insights.

OneDegree has established itself as a leader in providing insurance solutions for digital assets, having received regulatory approval as Asia’s first licensed insurer for such assets. Their offerings cover a range of digital assets, including cryptocurrencies and blockchain-based investments, which are often vulnerable to cybersecurity threats and market volatility. By collaborating with Walaa, OneDegree aims to expand its reach and offer its innovative insurance solutions to a broader audience, particularly in the Middle East.

Walaa Cooperative Insurance Company, known for its comprehensive insurance and reinsurance services across various sectors, brings a wealth of experience to this partnership. The company’s established market presence in Saudi Arabia provides a solid foundation for the integration of digital asset insurance into its existing portfolio. This move is expected to enhance Walaa’s service offerings, addressing the growing demand for secure and reliable insurance solutions for digital assets in the region.

This partnership is timely, given the rapid growth in the adoption of digital assets and the corresponding need for protection against potential risks. The digital asset market has seen substantial growth over the past few years, with increasing interest from both individual and institutional investors. As this market continues to expand, the risks associated with digital assets, such as cyber attacks and regulatory changes, become more pronounced. Insurance products designed to mitigate these risks are crucial for fostering confidence and stability in the digital asset ecosystem.

The collaboration between OneDegree and Walaa Cooperative Insurance Company represents a forward-thinking approach to addressing these emerging risks. By combining OneDegree’s specialized expertise with Walaa’s extensive experience and regional knowledge, the partnership is poised to set a new standard in the insurance industry for digital assets. This integration not only broadens the availability of digital asset insurance but also enhances the overall security and reliability of the market.

As digital assets continue to gain prominence, insurance solutions tailored to this sector will play a pivotal role in mitigating associated risks. The partnership between OneDegree and Walaa Cooperative Insurance Company highlights the increasing recognition of the importance of specialized insurance products in the digital age. With their combined strengths, the two companies are well-positioned to meet the evolving needs of investors and stakeholders in the digital asset space.

State-of-the-art facility based in Singapore aims to accelerate adoption of Robotics and AI across Southeast Asia through training and education, improving access to new healthcare technologies and delivering better care experiences across the region SINGAPORE – Media Outreach Newswire – 4 September 2024 – Medtronic plc, a global leader in healthcare technology, expands the capabilities of Medtronic Customer eXperience Center (MCXC) in Singapore with the opening of […]

A high-level meeting between Saudi Arabia and the United States has underscored the deepening strategic partnership between the two nations, with a particular focus on the digital economy and fostering innovation. The discussions, which brought together top officials from both countries, aimed at exploring new avenues for collaboration in technology, cybersecurity, and artificial intelligence, areas that are rapidly becoming pivotal in the global economy.

Saudi Arabia, under the leadership of Crown Prince Mohammed bin Salman, has been aggressively pushing forward its Vision 2030 initiative, a comprehensive plan aimed at diversifying the nation’s economy away from its heavy reliance on oil. Central to this vision is the development of a robust digital economy, which the Kingdom views as essential for its future prosperity. The discussions with the U.S. were seen as a critical step in bolstering this aspect of Saudi Arabia’s long-term economic strategy.

The meeting, which took place in Riyadh, featured prominent figures from both the public and private sectors. Key topics included enhancing bilateral cooperation in the digital sphere, fostering innovation ecosystems, and addressing the challenges posed by the rapidly evolving technology landscape. Both sides expressed a strong commitment to working together to advance these objectives, recognizing the mutual benefits that such collaboration could bring.

Saudi officials emphasized the Kingdom’s ambitious plans to become a global leader in technology and innovation. The nation has already made significant investments in this area, including the establishment of tech hubs, the promotion of digital entrepreneurship, and the implementation of advanced technological infrastructure. The U.S., with its well-established tech industry and expertise in innovation, is seen as an ideal partner to help Saudi Arabia achieve these goals.

A key element of the discussions was cybersecurity, an area of increasing concern for both nations. With the rise of digital threats, protecting critical infrastructure and ensuring the security of digital assets have become top priorities. The U.S. has been a leader in cybersecurity innovations, and its expertise is expected to play a crucial role in helping Saudi Arabia develop its capabilities in this domain. The discussions highlighted the importance of sharing knowledge and resources to build resilient cyber defenses that can withstand sophisticated attacks.

Artificial intelligence (AI) also featured prominently in the talks. Saudi Arabia has shown a strong interest in AI, viewing it as a transformative technology that can drive economic growth and improve various sectors, including healthcare, finance, and transportation. The U.S., home to many of the world’s leading AI research institutions and companies, is well-positioned to assist Saudi Arabia in harnessing the power of AI. The two nations discussed potential joint initiatives to develop AI applications that could benefit both countries, as well as the broader global community.

Innovation ecosystems were another focal point of the meeting. Saudi Arabia has been actively working to create a supportive environment for innovation, including the development of new regulations, the promotion of research and development, and the establishment of innovation centers. The U.S. has a long history of fostering innovation through its vibrant startup culture and well-established tech industry. The discussions explored ways to integrate these strengths, with the aim of creating a dynamic innovation ecosystem in Saudi Arabia that could serve as a model for the region.

Both sides also addressed the broader implications of their collaboration on the global stage. The digital economy is increasingly seen as a critical driver of global growth, and partnerships like the one between Saudi Arabia and the U.S. could have far-reaching impacts. By working together, the two nations aim to set new standards for digital innovation and leadership, potentially influencing the direction of the global digital economy.

By Manish Rai Recent bold attacks carried out by Baloch Liberation Army (BLA) rocked Pakistan. A large number of people and security personnel were killed in the province of Balochistan when separatist insurgents attacked police stations, railway lines and highways, and security forces camps. The assaults were the most widespread and ferocious in years by ethnic militants fighting a decades-long insurgency to win secession of the resource-rich […]

Microsoft Windows users are encountering a surge in malware threats following an extensive series of security updates on Patch Tuesday, as new warnings from U.S. government agencies highlight the growing risks. The heightened alert has underscored the critical need for continued security measures, as users grapple with the implications of the latest vulnerabilities and threats.

Patch Tuesday, a routine monthly event where Microsoft releases security updates, was unusually significant this month. The company rolled out a broad array of patches aimed at addressing a variety of vulnerabilities affecting Windows operating systems. However, this surge in updates has coincided with a noticeable increase in malware attacks, raising concerns among cybersecurity experts and government officials alike.

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) and other federal entities have issued urgent advisories, emphasizing the importance of applying these patches to prevent potential exploits. These advisories come in response to a spate of sophisticated cyberattacks that have targeted both individual users and large organizations. The recent alerts reveal a pattern of aggressive malware campaigns that exploit vulnerabilities addressed in the latest updates.

Experts from the cybersecurity community have observed a marked uptick in threats, including ransomware and spyware, which have intensified following the Patch Tuesday updates. These malicious programs are designed to infiltrate systems, often leveraging the same vulnerabilities that Microsoft aimed to address. The increase in attacks highlights the persistent and evolving nature of cyber threats, emphasizing the necessity for vigilant and ongoing security practices.

The rising malware incidents have sparked significant concern about the potential implications for millions of Windows users globally. As users scramble to implement the latest patches, there are growing worries about the effectiveness of these updates against increasingly sophisticated threats. The cybersecurity landscape is evolving rapidly, with new attack vectors and techniques emerging frequently, making it crucial for users to stay updated and proactive in their security measures.

Security experts advise that users must not only apply the latest patches but also adopt comprehensive security practices, including regular system scans, the use of robust antivirus software, and cautious behavior online. These measures are vital in mitigating the risks associated with malware and ensuring that systems remain secure amidst the evolving threat landscape.

The situation has prompted discussions about the broader implications for long-term security support for Windows users. With the ongoing threat of malware and the need for constant updates, there is growing debate about the sustainability of security practices and the potential need for users to consider additional protective measures. As the landscape of cyber threats continues to shift, users and organizations must remain adaptable and proactive in their approach to cybersecurity.

As the cybersecurity community continues to assess and respond to these developments, the focus remains on ensuring that users are equipped with the tools and knowledge needed to defend against evolving threats. The situation serves as a stark reminder of the importance of maintaining robust security practices and staying informed about the latest developments in the field.

One of Ukraine’s F-16 fighter jets was downed while attempting to repel a large-scale Russian missile and drone attack earlier this week, marking the first loss of the U.S.-supplied aircraft since its introduction into the Ukrainian arsenal. The incident has sparked significant concern within Kyiv’s military leadership and resulted in the dismissal of the country’s air force commander, Lt. Gen. Mykola Oleshchuk.

The crash occurred amid an intensifying wave of Russian assaults across various regions of Ukraine. Although the exact cause of the crash remains under investigation, there have been unverified claims that the F-16 may have been mistakenly hit by a Patriot air-defense system. Ukrainian authorities have not confirmed this scenario, but the allegation has already led to heightened tensions within the Ukrainian government and military.

In a swift response, President Volodymyr Zelenskyy removed Oleshchuk from his position, citing the need to enhance the protection of military personnel and ensure stronger command-level decisions. Lt. Gen. Anatolii Kryvonozhko was appointed as the acting air force commander, with immediate tasks focused on reviewing the incident and maintaining operational effectiveness amidst the ongoing conflict.

The crash highlights the fragile balance in Ukraine’s efforts to counter Russia’s aerial superiority. While the introduction of F-16s from European allies has been hailed as a significant boost to Ukraine’s air capabilities, military analysts caution that these aircraft alone cannot drastically alter the course of the war. The Russian air force, backed by sophisticated defense systems, remains a formidable challenge, as evidenced by this latest loss.

On the ground, Russian forces have continued their offensive in eastern Ukraine, while Ukrainian troops strive to hold strategic positions. The F-16 crash underscores the broader difficulties faced by Kyiv in its efforts to sustain a robust defense against a well-equipped adversary.

Meanwhile, Russia’s attacks have also led to significant civilian casualties. A bombing raid on the northeastern city of Kharkiv resulted in the deaths of six people, including a 14-year-old girl, and left dozens wounded. Ukrainian officials argue that such attacks could be mitigated if Western partners further relaxed restrictions on the use of donated weapons, allowing Ukrainian forces to target Russian military assets more effectively.

As investigations into the F-16 crash continue, the incident serves as a stark reminder of the risks inherent in modern warfare and the complexities of coordinating an international coalition in support of Ukraine’s defense efforts. The outcome of this investigation could influence future military strategies and the deployment of critical air assets as Ukraine navigates its path through the ongoing conflict.

The downing of the F-16 and the subsequent shake-up in military leadership represent a critical moment in the war, highlighting both the challenges of integrating new technology into a warzone and the ongoing determination of Ukraine to adapt and respond to evolving threats.

VISHNU RAJA
RYO YAMADA
HITORI GOTOH
IKUYO KITA