Linux Foundation has launched DNS-AID, an open source project designed to let AI agents discover, verify and connect with one another through the internet’s existing Domain Name System rather than through private registries, vendor directories or hardcoded configuration files. The project, initially developed at Infoblox, is being positioned as a neutral discovery layer for the emerging agentic web, where software agents are expected to act across websites, […]
Cybercriminals are shifting from crude misspellings of trusted software packages to more convincing names that appear to belong inside legitimate developer ecosystems, raising fresh concern across open-source security teams and enterprise software supply chains. The change marks a significant evolution in package impersonation attacks. Rather than relying only on a developer mistyping a package name, malicious publishers are creating packages that look like natural extensions, plugins, configuration […]
Hackers are using illegal streaming and digital library websites to spread cryptocurrency miners and remote access malware through fake video player updates, exposing millions of visitors to stealthy infections that can drain computing power and give attackers remote control over compromised systems. The campaign targets users who attempt to watch pirated films or television shows. Instead of loading the video, the website displays a warning that a […]
By Krishna Jha The entire origin and development of living world has led to the emergence of complicated natural environment of which human beings are part and parcel. Environment and society are inter-related and inter-dependent. Society has come to rely on the natural environment for its existence. Any destruction of environment is sure to pose […]
Cryptocurrency developers have become the focus of a new macOS-focused cyber campaign that uses fake recruiter approaches, malicious meeting links and compromised software pipelines to steal digital assets and spread malware through trusted internal systems. The activity is being tracked as JINX-0164, a previously unreported financially motivated threat actor active since at least mid-2025. Investigators found that the group has targeted cryptocurrency organisations by approaching developers and […]
Motorola has disabled a phone software behaviour that routed some Amazon Shopping app launches through web tracking links before opening the app, after users and technology researchers found affiliate referral codes being inserted into shopping sessions without clear notice. The issue centred on Motorola’s preinstalled Smart Feed and Moto App Launcher experience, which appeared to intercept launches of Amazon from the app drawer on certain devices. Instead […]
Cybercriminals behind the ClearFake campaign have shifted deeper into blockchain-based command infrastructure, using BNB Smart Chain testnet contracts to deliver malicious code and frustrate conventional takedown efforts. The campaign marks an escalation in the abuse of decentralised infrastructure for malware operations. Instead of relying on domains, hosting providers or disposable servers that can be suspended, the operators are storing payload logic and routing instructions inside smart contracts […]
Roundcube Webmail administrators are being pressed to install emergency updates after maintainers fixed a set of security flaws that could expose email systems to database manipulation, script injection, server-side request forgery and other attacks. Versions 1.6.16 and 1.7.1, released on 24 May 2026, address vulnerabilities affecting the 1.6 long-term support line and the 1.7 branch. The most closely watched issue is a pre-authentication SQL injection flaw in […]
Google Cloud has moved deeper into AI-native cybersecurity with Google AI Threat Defence, an autonomous security platform aimed at helping enterprises detect, prioritise and remediate attacks at machine speed as rivals Anthropic and OpenAI push frontier models into vulnerability discovery and code defence. The launch marks a sharper contest in enterprise security, where artificial intelligence is shifting the centre of gravity from manual patching and alert handling […]
Cybersecurity researchers have warned that BTMOB, an Android remote access trojan, has developed into a potent tool for criminals seeking to hijack smartphones, steal data and run fraud from compromised devices. The malware, first identified in early 2025, has moved beyond the narrower behaviour associated with many banking trojans. It can capture screens, record activity, manage files, intercept credentials, control device functions and give an attacker near-live […]
State Bank of India has warned customers against a phishing campaign that falsely claims its YONO app will be deactivated unless Aadhaar details are updated through a shared link or APK file. The country’s largest lender has said the messages are fraudulent and should be ignored. Customers have been advised not to download files received through SMS, WhatsApp, email or social media, and not to share account […]
A newly disclosed flaw in Starlette has put Python-based AI services under pressure to patch systems that may expose protected endpoints through manipulated HTTP Host headers. The vulnerability, tracked as CVE-2026-48710 and dubbed BadHost, affects Starlette versions up to 1.0.0 and has drawn attention because of Starlette’s role in modern application stacks built around FastAPI, API gateways, model-serving tools and agent frameworks. Starlette 1.0.1 contains the fix, […]
Cybersecurity teams across India face a compressed response window after CERT-In urged organisations to fix actively exploited internet-facing vulnerabilities within 12 hours wherever feasible, marking a sharper regulatory push as artificial intelligence accelerates cyber-attack cycles.
The guidance, issued on May 25 in a 38-page blueprint, reflects growing official concern that attackers are using generative AI, large language models and autonomous tools to discover exposed systems, weaponise flaws, craft phishing lures and scale malware operations faster than conventional security programmes can respond. The document places rapid remediation, continuous monitoring and exposure reduction at the centre of enterprise cyber defence.
CERT-In’s most stringent timeline applies to known exploited vulnerabilities affecting internet-facing and critical systems, including applications, identity platforms, cloud assets, APIs, operational technology and systems supporting essential business functions. Organisations are advised to patch, mitigate or isolate such weaknesses within 12 hours where feasible. Critical externally exposed vulnerabilities should be addressed within one day, while known exploited flaws inside internal systems should be fixed within one day unless compensating controls are implemented and documented.
The blueprint also recommends that critical internal vulnerabilities affecting high-value systems be remediated within three days, and high-severity vulnerabilities within five days based on risk prioritisation. Where patches are unavailable, organisations are expected to use temporary protections such as isolation, access restrictions, web application firewalls, API shields, feature disabling and enhanced monitoring until permanent fixes are deployed.
The directive signals a shift from audit-driven cybersecurity to continuous exposure management. CERT-In has warned that organisations can no longer depend on periodic assessments or reactive incident response when automated tools can identify weak credentials, misconfigured systems, insecure APIs and vulnerable internet-facing services at machine speed. The approach requires security teams to maintain live inventories of assets, prioritise exposed systems and test whether controls work under attack conditions.
AI is changing both sides of the cyber equation. Attackers can use it to automate reconnaissance, write exploit code, refine phishing messages, generate synthetic identities and adapt malicious software. Defenders are being pushed to use similar capabilities for anomaly detection, threat hunting, automated triage and faster containment. The risk, however, is that poorly governed AI systems can themselves become attack surfaces through prompt injection, data leakage, model manipulation, poisoned training data, model theft and compromised orchestration pipelines.
The guidance gives particular weight to organisations operating in banking, financial services, telecom, healthcare, government, energy, transport, cloud services and other critical infrastructure-linked sectors. These environments often rely on interconnected digital systems, third-party software, outsourced technology providers and legacy platforms, creating wider exposure when a single flaw is weaponised quickly.
Global breach data has reinforced the urgency behind faster patching. Software vulnerability exploitation has overtaken stolen credentials as a leading breach entry point in major datasets, while ransomware remains a high-impact threat. Security teams also face growing pressure from supply-chain compromise, shadow AI usage, cloud misconfiguration and business email compromise. Unauthorised use of public AI tools has become a data governance issue as employees may upload source code, business documents, credentials or customer information into platforms outside corporate oversight.
CERT-In’s blueprint calls for a zero-trust approach, least-privilege access, layered controls and secure-by-design practices across applications, infrastructure and AI workflows. It urges organisations to maintain visibility into AI deployments, restrict sensitive data uploads to public AI platforms, log AI activity, conduct adversarial testing and keep human approval for critical autonomous actions.
Software supply-chain visibility is another major focus. Organisations are encouraged to use software bills of materials and related inventories for AI models, cryptographic assets and hardware components to understand dependencies, validate provenance and coordinate remediation when vulnerabilities emerge in third-party products.
The new expectations build on India’s existing cyber incident reporting framework, under which specified cyber incidents must be reported to CERT-In within six hours. The latest blueprint does not merely extend compliance obligations; it raises operational expectations for boards, chief information security officers and technology vendors by linking resilience to the speed of response.
Smaller organisations may struggle with the 12-hour benchmark because patch testing, downtime concerns, legacy dependencies and staffing shortages often slow remediation. The guidance therefore recognises feasible mitigation as part of the response, but it also makes clear that unmanaged exposure is no longer acceptable when attackers can exploit public-facing weaknesses within hours.
Cisco researchers have warned that leading open-weight large language models can be manipulated through sustained conversations that gradually push them past safety controls, exposing a weakness in systems now being adopted across business, public services and consumer applications. The assessment tested eight widely used open-weight models from Alibaba, DeepSeek, Google, Meta, Microsoft, Mistral, OpenAI and Zhipu AI. The models were examined through automated adversarial testing designed to […]
Prudent Risk Management Yields Solid Outcomes metrics, Core Pawn Business Demonstrates Resilient Growth with Proposed Final Dividend of HK$1.15 cents per share
Results Highlights:
Profit for the year attributable to shareholders increased by approximately 47.8% YoY to approximately HK$82.6 million
Net profit margin increased by approximately 16.2 p.p. YoY to approximately 50.2%
Impairment losses recognized on loan receivables decreased by approximately 72.6% YoY to HK$12.7 million
Revenue from pawn loan business increased by approximately 12.9% YoY to approximately HK$98.6 million
Proposed final dividend of HK$1.15 cents per share
HONG KONG SAR – Media OutReach – 27 May 2026 – The board of directors of Oi Wah Pawnshop Credit Holdings Limited (HKEx stock code: 1319.HK, the “Group” or “Oi Wah”) announced its annual results and its financial position. For the year ended 28 February 2026 (“FY2026“), the Group recorded revenue of approximately HK$164.4 million. Profit attributable to shareholders of the Company reached approximately HK$82.6 million, representing an increase of 47.8% compared to the year ended 28 February 2025 (“FY2025“). During the year, net interest margin expanded to approximately 17.2%.
As of 28 February 2026, the cash and cash equivalents (net of bank overdraft) amounted to approximately HK$376.9 million, representing a substantial increase of approximately 74.8% YoY. The net assets increased to approximately HK$1,155.7 million. Concurrently, the gearing ratio dropped to 4.1%. During the year, the earnings per share increased by approximately 48.3% YoY to HK 4.3 cents. The Board of Directors recommends a final dividend of HK 1.15 cents per share.
BUSINESS REVIEW
Mortgage loan business
In FY2026, the economy entered a phase of gradual recovery, leading to a steady resurgence in financing demand. The revenue from the mortgage loan business was approximately HK$65.8 million and accounted for approximately 40.0% of the Group’s total revenue during the year. The gross mortgage loan receivables were approximately HK$612.5 million as at 28 February 2026. During the year, net interest margin of the mortgage loan business was approximately 10.1%.
In FY2026, the Group maintained a disciplined and risk-sensitive approach in its lending activities. While we observed an encouraging stabilization in the residential property market, the Group exercised intensified vigilance toward the commercial and industrial sectors due to persistent supply overhangs and valuation pressures. Our underwriting strategy remained focused on building a resilient loan portfolio by prioritizing high-quality collaterals and prudent loan-to-value ratios. During the year, the average loan-to-value ratio for first mortgage was approximately 56.27%, while overall average loan-to-value ratio for subordinate mortgage was approximately 40.82% of which, average loan-to-value ratio of subordinate mortgage that the Group participated in was approximately 3.73%.
Reflecting our robust credit risk management, the charge for impairment losses recognized on loan receivables decreased from approximately HK$46.3 million to approximately HK$12.7 million, representing a decrease of approximately 72.6% or HK$33.6 million.
Pawn Loan Business
The revenue from the pawn loan business increased by approximately 12.9% to approximately HK$98.6 million in FY2026. The business’s profitability was further bolstered by a significant 73.0% increase in the gain on disposal of repossessed assets, which reached approximately HK$19.2 million as compared to approximately HK$11.1 million in FY2025. This performance was mainly attributed to the unprecedented strength of gold prices and a highly active secondary market for luxuries, particularly high-end timepieces. These factors have further solidified the pawn loan business as a resilient and strategic hedge against broader economic volatility.
During the year, the Group continued to channel resources to advertising and promotion to enhance the Group’s brand exposure. Such effort has generated demand for one-to-one pawn loan appointment services for pawn loans exceeding HK$0.1 million.
PROSPECTS
Looking ahead, the Group maintains a stance of cautious optimism regarding the global economic recovery. While macroeconomic and geopolitical uncertainties may persist, we remain dedicated to a proactive yet prudent strategy to ensure sustainable long-term growth and maximize returns for our shareholders.
Within the mortgage loan market, our strategy will be characterized by a calibrated and divergent approach. We continue to hold an optimistic outlook on the residential property segment, where we intend to capitalize on the stabilizing interest rate environment by identifying high-quality mortgage opportunities. Conversely, we maintain cautious and vigilant towards the commercial and industrial sectors. Given the structural challenges of inventory overhang and the increasing prevalence of distressed assets, the Group will exercise intensified oversight in its credit underwriting and collateral appraisal to mitigate valuation risks.
Regarding our core operations, we anticipate our pawn loan business to remain resilient, supported by a firm gold price trajectory and sustained demand for liquidity management. To further enhance operational efficiency, the Group is actively optimizing its pawn shop network. We are strategically identifying more cost-effective locations within our established service areas, aiming to relocate our pawn outlets to premises with more competitive lease terms to reduce operating overheads while maintaining our leading market presence.
Simultaneously, our strategic partnership with PACM Group remains a key driver for geographic diversification. By proactively exploring institutional credit opportunities in developed markets while maintaining rigorous investment oversight, the Group is well-positioned to navigate evolving industry dynamics and deliver stable value to all stakeholders.
Mr. Edward Chan, Chairman and CEO of the Company, said, “Global geopolitical and macroeconomic uncertainties intertwine, placing pressure on the global economic recovery and posing ongoing challenges to the local property market. In the face of a complex external environment, Oi Wah has consistently adhered to a proactive yet prudent management strategy. Our core pawn loan business has fully demonstrated its role as a strategic tool to hedge against macroeconomic fluctuations, showcasing the Group’s strong resilience amidst market challenges.
Looking forward, we will adopt a carefully calibrated differentiation strategy and continue to drive regional diversification. Under strict investment monitoring, we will actively explore business opportunities in developed markets to further expand our revenue streams and customer base, striving to deliver long-term, stable, and sustainable returns for our shareholders.”
Hashtag: #OiWah
The issuer is solely responsible for the content of this announcement.
About Oi Wah Pawnshop Credit Holdings Limited
Oi Wah is a financing service provider in Hong Kong, mainly providing short-term secured financing, including pawn loans and mortgage loans. The Group established its first pawnshop in 1975 and currently owns 10 pawnshops and one premium service center in various locations in Hong Kong. Oi Wah diversified into mortgage loan business in 2009. The Group is the first local pawn shop which successfully listed on the Main Board of The Stock Exchange of Hong Kong Limited on 12 March 2013.
By Dr. Gyan Pathak Supreme Court of India on May 27, 2026 upheld the legality of the Special Intensive Revision (SIR) of the electoral roll in Bihar and elsewhere and emphasized that this exercise is constitutionally connected to “free and fair polls”. The judgment strongly underlined the purity and accuracy of rolls giving priority to […]
Microsoft has issued fixes for a high-severity SharePoint Server vulnerability that could allow authenticated attackers to run code remotely on affected on-premises systems, sharpening security concerns for organisations that continue to rely on self-managed collaboration platforms. Tracked as CVE-2026-45659, the flaw affects SharePoint Server Subscription Edition, SharePoint Server 2019 and SharePoint Enterprise Server 2016. The vulnerability has been assigned a CVSS score of 8.8, placing it in […]
Microsoft is preparing to scale back internal use of Anthropic’s Claude Code and move thousands of developers towards GitHub Copilot CLI, marking a sharper push to consolidate AI coding work around tools it owns and governs more directly. The reported shift affects the company’s Experiences and Devices division, which covers major product groups including Windows, Microsoft 365, Outlook, Teams and Surface. Engineers using Claude Code have been […]
Developers using Angular’s official Visual Studio Code extension have been urged to update their systems after multiple high-severity flaws were found to expose workstations to remote code execution through malicious project files and dependencies. The vulnerabilities affect Angular Language Service, published as Angular. ng-template on the Visual Studio Marketplace, in all versions before 21.2.4. The patched release closes weaknesses that could allow an attacker to execute commands […]
Code4Mzansi highlights the growing strength of South Africa’s developer ecosystem and the role of youth-led innovation in shaping the country’s digital future
JOHANNESBURG, SOUTH AFRICA – Media OutReach Newswire – 26 May 2026 – South Africa’s emerging developers are building close to the ground, with many of the strongest solutions at the inaugural Huawei Code4Mzansi finals focused on systems people use every day: township retail, healthcare, energy, agriculture, payments and the creative economy.
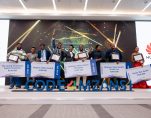
The winners at the Huawei Developer Competition, Code4Mzansi
The competition was held in partnership with the Department of Small Business Development. “The Code4Mzansi competition is not just a celebration of achievement, it is a launchpad for the future,” said Minister Stella Ndabeni, whose department co-hosted the event and delivered the closing address.
The finals revealed a clear shift from building abstract digital products to practical tools that help small businesses trade better, communities access services more easily, and local industries solve problems faster.
Four finalist teams focused directly on the township economy, with solutions covering food safety verification for spaza shops, offline point-of-sale systems built for load-shedding, WhatsApp-native marketplaces for informal retailers, and community credit systems for SASSA grant recipients.
Others addressed AI-driven healthcare access, electricity theft detection, smart agriculture, financial infrastructure for the creator economy, and AI-generated African music.
Held at Huawei Office Park in Woodmead, the finals brought together more than 100 attendees, including government representatives, academic partners, industry leaders and media.
“The quality of the finalist solutions demonstrated the potential of local innovation to respond to real market needs,” said Steven Chen, Cloud CEO of Huawei Technologies South Africa.
Academic partners included the University of Pretoria, the University of Johannesburg, the University of the Witwatersrand and the University of Cape Town.
“Small businesses are the backbone of our economy, and technology is their greatest accelerator. The participants here today are future entrepreneurs who will drive South Africa’s digital economy forward,” said Professor Thokozani Shongwe, Vice Dean of Postgraduate Studies, Research and Internationalisation at the University of Johannesburg’s Faculty of Engineering and the Built Environment.
Industry partner rain also attended. Leon Nortje, Principal and Senior Architect at rain, said the competition offered a strong view of the country’s emerging technology pipeline.
“It is always good to see new projects and new teams working on solutions that are valuable and industry-related. We will be looking out for potential new employees,” said Nortje.
The winners
The finalists competed for a prize pool of R800,000. MAAT by SIMVAK was named the overall grand winner and received the Business Value Award, taking home R300,000. The platform addresses food safety and regulatory compliance in South Africa’s informal retail sector through AI agents, real-time product recall alerts, and counterfeit detection for the spaza shop ecosystem.
“The spaza network is the supply chain for most South African households,” said SIMVAK founder Shingirayi Mandebvu.
HealthHive by FTCK received second prize in the Business Value Award category, taking home R200,000, for its AI telemedicine platform that matches patients with the right medical practitioners based on their symptoms.
Auraa received the Grand Innovation Award for its AI music engine built to generate authentic African sound. The platform has been associated with an album that has crossed one million streams.
The Future Star Award went to e-Khadi, a community credit and stokvel platform giving SASSA grant recipients access to essentials at their local spaza shops, supported by AI-assisted credit scoring and fraud detection.
The People’s Choice Award, voted by the public on Huawei’s social media channels, went to DevRift, a semi-finalist in the competition, who took home R100,000.
Minister Ndabeni delivered the closing address, positioning Code4Mzansi within the government’s agenda for youth entrepreneurship, small business development and digital inclusion.
“Our task is to ensure that innovation does not remain a moment of applause, but becomes a pathway to enterprise creation, digital inclusion, and sustainable growth,” she said.
“Thank you to Huawei for being a perfect partner on the journey that we are travelling, and of course, those that matter most, the developers who dared to compete,” she said.
Code4Mzansi forms part of the global Huawei Cloud Developer Competition. In its inaugural edition, South Africa attracted more participants than any other country: 1,041 across 353 teams, including 176 enterprise teams, resulting in the highest enterprise participation rate among all competing markets. Twenty semi-finalists were selected before the top nine advanced to the final.
For the finalists, the work is just beginning. As Minister Ndabeni said, “Go home today proud. But tomorrow, wake up, build again.”
The issuer is solely responsible for the content of this announcement.
About Huawei
Founded in 1987, Huawei is a leading global provider of information and communications technology (ICT) infrastructure and smart devices. With 213,000 employees operating in over 170 countries, we serve more than three billion people worldwide.
Huawei is committed to bringing digital to every person, home, and organisation for a fully connected, intelligent world. In 2025, Huawei generated CNY880.9 billion in revenue, reinvesting 21.8% (CNY192.3 billion) into R&D, with about 53.7% of its employees working in R&D. As a private company fully owned by its employees, Huawei focuses on customer-centric innovation and open collaboration to create lasting value and drive technological breakthroughs globally.
For more information, please visit Huawei online at www.huawei.com or follow us on:
By Nitya Chakraborty With the U.S. President Donald Trump himself downgrading the status of the four nation Quadrilateral Security Dialogue (QUAD), why is Indian government spending so much of its precious time on QUAD meetings? It is sheer wastage of time for the Prime Minister Narendra Modi as also Foreign Minister Dr. S Jaishankar. US […]
Arabian Post Staff -Dubai Sennheiser has unveiled the Momentum 5 Wireless, its next flagship over-ear headphone, positioning the model as a direct challenge to Sony, Bose and Apple in the premium noise-cancelling audio market. The headphones, announced on 25 May 2026 and set to go on sale in the United States from 16 June at $399.99, bring stronger active noise cancellation, Dolby Atmos support with head tracking, […]
Hackers are exploiting a critical vulnerability in Ghost CMS to compromise more than 700 websites and turn trusted publishing pages into delivery points for ClickFix malware, escalating concerns over unpatched content management systems used by media, universities, fintech firms, software companies and research organisations. The flaw, tracked as CVE-2026-26980, is a SQL injection vulnerability in Ghost’s Content API. It affects Ghost versions from 3.24.0 through 6.19.0 and […]
Iran-linked hackers have expanded cyber-espionage operations against aviation and software organisations in the United States, Europe and the Middle East, using fake recruitment pitches and search-engine manipulation to deliver malware capable of long-term surveillance and data theft. The campaign has been tied to Nimbus Manticore, also tracked as UNC1549, Screening Serpens, Smoke Sandstorm and Iranian Dream Job. The group is assessed to be aligned with Iran’s Islamic […]




 https://www.huawei.com/za/
 https://www.linkedin.com/company/Huawei
 https://twitter.com/HuaweiSAR
 https://www.facebook.com/HuaweiSAR
 http://www.youtube.com/Huawei




