News related to
attack

Growing sophistication in artificial-intelligence driven video and audio forgery has sent shockwaves through financial systems and public trust alike, with 2025 emerging as a watershed year in deepfake-enabled fraud. Losses tied to deepfake scams are widely estimated at over $50 billion annually — a stark indicator of how rapidly cybercrime is evolving. Fake videos that convincingly mimic celebrities, corporate executives or even family members are now being […]

European banking regulators are intensifying warnings that widespread use of artificial intelligence across the financial sector could expose the banking system to new, systemic vulnerabilities. The chair of supervision at the central bank of the Netherlands, Steven Maijoor, stated that the increasing reliance on AI tools supplied by non-European tech firms is creating a structural threat to financial stability. He urged swift action to reduce dependence on […]

Security analysts working on China-linked cyber espionage have deepened scrutiny of two Beijing-based organisations that appear to support the country’s intelligence infrastructure. The Beijing Institute of Electronics Technology and Application and its subsidiary Beijing Sanxin Times Technology Co., Ltd. are now under particular focus for allegedly supplying advanced steganography tools and network-penetration services to agencies tied to the Ministry of State Security.

BIETA has built a decades-long publication record in information hiding research, with around 40–46 percent of its 87 peer-reviewed papers between 1991 and 2023 devoted to steganography methods. Observers note that those outputs align with covert-communication and data-exfiltration requirements typical of state espionage missions. CIII, meanwhile, boasts copyright registrations for software capable of disguising malicious code within images, audio and video files, and has offered foreign-developed network simulation and penetration-testing tools that are frequently repurposed by advanced persistent threat actors.

Officials familiar with the intelligence landscape argue that BIETA and CIII function less like independent private firms and more like technology-enablement arms of China’s state-security apparatus. Evidence cited includes overlapping leadership — several BIETA executives have held or continue to hold roles within organisations tightly linked to the MSS — and a shared location: BIETA’s headquarters sit adjacent to the MSS First Research Institute in Beijing, a facility believed to be behind China’s mass surveillance infrastructure in regions such as Xinjiang.

The role of front organisations like BIETA and CIII expands beyond development of steganographic tools. According to analysts, these firms provide a bridge between Western technical innovation and China’s intelligence needs by acting as intermediaries for acquiring or licensing foreign cybersecurity and network-monitoring products. Through such supply-chain activity, capabilities like deep network simulation, cyber-range training and payload obfuscation may be imported under the guise of legitimate commercial transactions.

Linking BIETA and CIII’s activities to actual APT campaigns remains difficult, in part because those campaigns rely on clandestine infrastructure and rarely include public attribution. Nevertheless security researchers point to historical patterns: Chinese-linked APTs have employed image, audio and video steganography to deploy malware or smuggle exfiltrated data; such techniques were documented in operations as far back as 2013. These precedents match the capabilities now associated with BIETA and CIII’s publicly disclosed research and product catalogue.

Last year’s exposure of another contractor, i‑Soon, offered insight into how the wider ecosystem operates: leaked internal communications and product manuals revealed use of malware management platforms tied to major intrusion campaigns against governments and companies globally. That development affirmed concerns that front organisations could serve as staging grounds for supply-chain attacks, with steganographic delivery mechanisms functioning as invisible carriers for payloads.

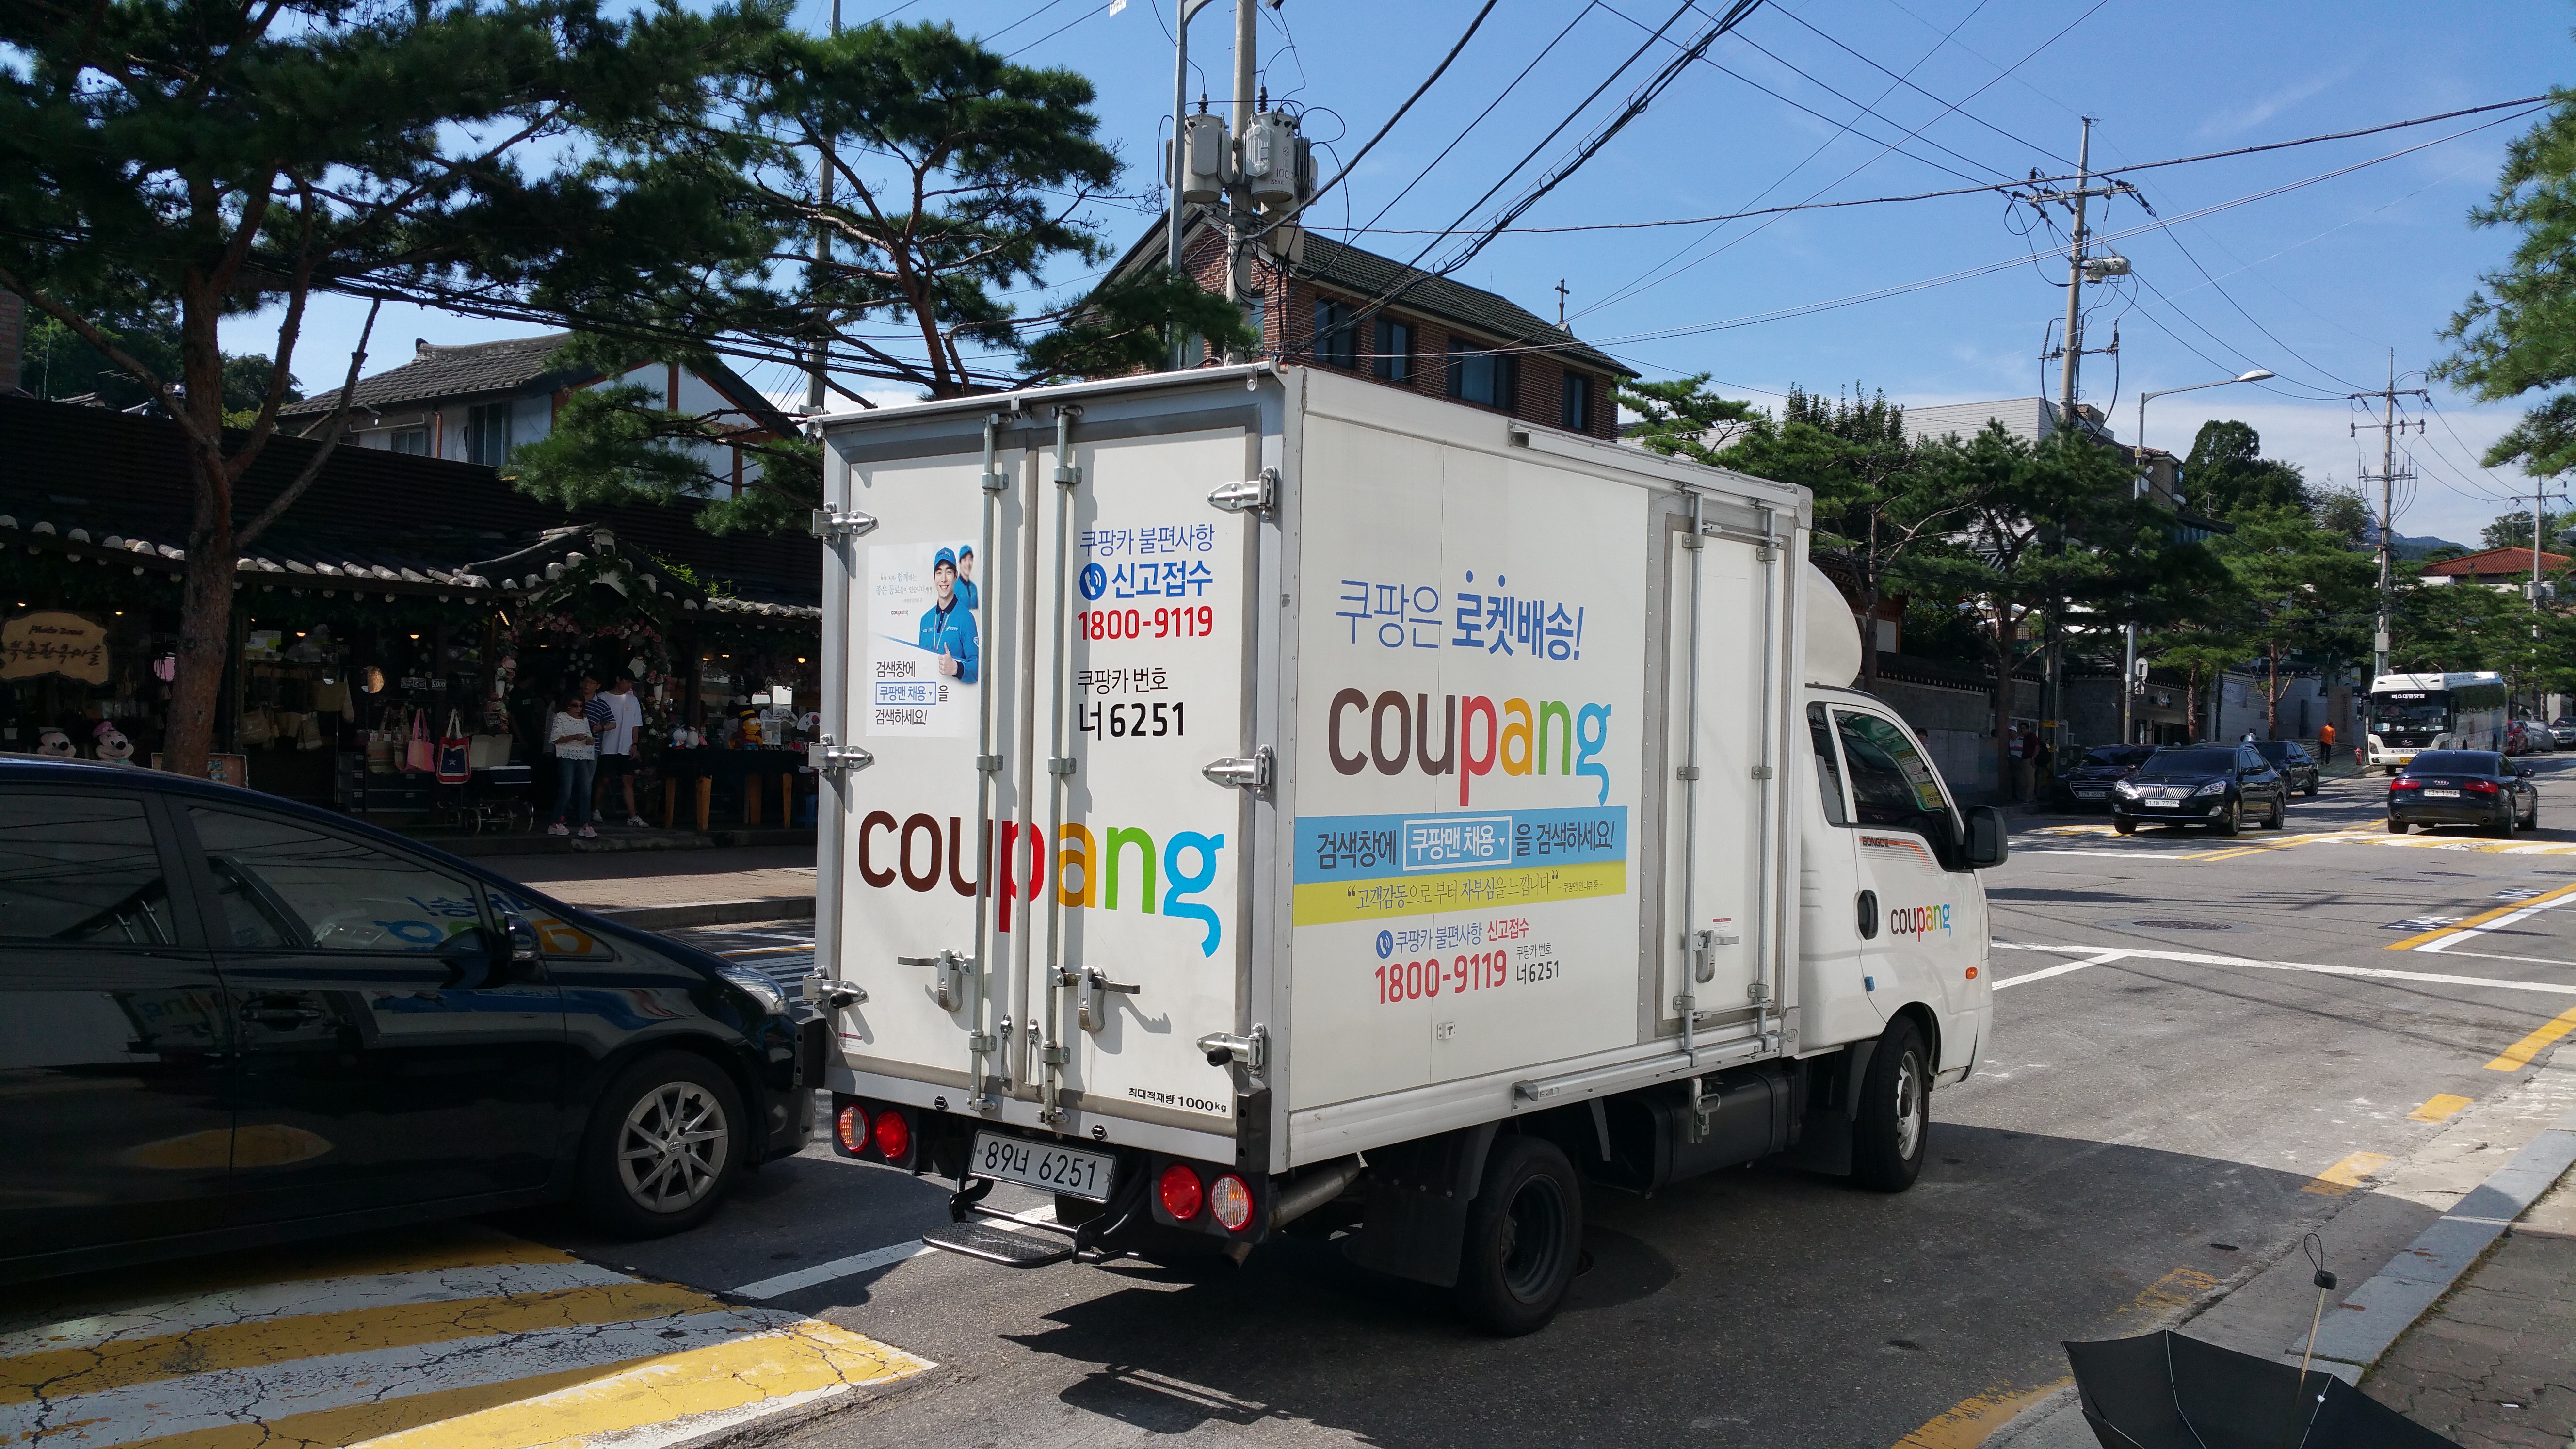
Coupang has admitted that unauthorised access exposed the personal information of 33.7 million customer accounts, marking the worst data leak in South Korean history. The leaked data includes names, email addresses, phone numbers, delivery addresses and some order histories, while payment credentials and login details are said to remain secure. The breach first began on 24 June and remained undetected until 18 November, when the company discovered suspicious access affecting about 4,500 accounts — a figure swiftly revised upward as investigators uncovered the full scale of the leak.

Police investigators are analysing server logs and have identified the IP address used in the attack, triggering efforts to trace the suspect. Authorities have not confirmed the nationality of the person under suspicion, though local media have pointed to a former employee of Chinese origin. Coupang filed a formal complaint on 25 November under legislation covering unauthorised access and data theft, and the probe has since turned into a full-fledged criminal investigation.

In response to mounting public concern, the Ministry of Science and ICT convened an emergency meeting to examine whether Coupang violated national data-protection laws. The government has warned that the exposed information — though not financial in nature — could easily be used for phishing, identity theft or other scams, particularly given the extent of the leak and the volume of personal data involved.

Coupang says it blocked the breach route as soon as the intrusion was confirmed and has engaged external cybersecurity experts to strengthen internal monitoring. The firm also issued a public apology through its chief executive, pledging full cooperation with law enforcement and regulatory bodies.

A sophisticated attack on the liquidity pool of yETH — the liquid staking token index offered by Yearn Finance — drained millions of dollars in assets when an attacker minted an effectively unlimited amount of yETH and exchanged the bogus tokens for real ETH and other liquid-staking assets. Blockchain data indicate close to 1,000 ETH — roughly US$ 3 million — was swiftly moved through mixing service Tornado Cash in a single transaction, while the wider financial impact may scale significantly higher.

The exploit hinged on a critical flaw in the smart contract underpinning yETH’s “stableswap pool,” which permitted the creation of an unbounded number of yETH tokens. Immediately after minting, the attacker used those tokens to withdraw real ETH and other assets from liquidity pools tied to yETH, rapidly draining the pool. Multiple helper contracts deployed for the attack self-destructed soon after, making tracing efforts challenging.

Shortly after the event, Yearn Finance confirmed the breach and clarified that its core vault offerings — including V2 and V3 vaults — remain unaffected, noting the issue appears isolated to the legacy yETH pool. That distinction may have prevented a broader protocol-wide collapse, although internal assessments are ongoing to fully understand the exploit’s scope.

Further on-chain analysis by security firms suggests total losses could approach US$ 9 million, once damage to auxiliary pools — including a yETH–WETH pool — are accounted for. Nearly US$ 3 million in stolen ETH has already been funneled through Tornado Cash, rendering recovery difficult as funds are mixed and dispersed.

Market reaction was immediate: major cryptocurrencies including Bitcoin and Ether slid sharply during Asian trading hours, signalling heightened investor anxiety about DeFi security vulnerabilities. The incident has reignited scrutiny over legacy smart-contract code within decentralised finance platforms and underscored persistent risks associated with innovation outpacing security audits.

OpenAI disclosed a data breach involving its analytics provider Mixpanel, confirming that a security lapse allowed unauthorised access to certain API user details but did not compromise ChatGPT message data or model-generated content. The company informed affected developers that the incident, traced to November 2025, exposed names, email addresses and limited account-related metadata, prompting a broader review of third-party integrations across its platform. OpenAI stated that the […]

HONG KONG SAR – Media OutReach Newswire – 28 November 2025 – Trend Micro Incorporated (TYO: 4704; TSE: 4704), a global cybersecurity leader, today released its annual Security Predictions Report for 2026, warning that the coming year will mark the true industrialization of cybercrime. Artificial intelligence (AI) and automation are now enabling threat actors to run entire campaigns autonomously, from reconnaissance to extortion, creating unprecedented speed, scale, […]

Advertisements

South Korea’s largest cryptocurrency exchange saw roughly $36 million drained from its hot wallet linked to the Solana network in what officials describe as an “abnormal withdrawal”. The breach triggered an immediate freeze on deposits and withdrawals. The operator, Dunamu, moved remaining assets into cold storage and pledged to fully reimburse all affected users.

Authorities in Seoul identified the hacking group Lazarus Group — long associated with previous crypto thefts — as the prime suspect behind the intrusion. Investigators plan an on-site inspection of Upbit’s systems to determine how attackers bypassed security protocols.

The tokens siphoned off included SOL alongside several Solana-ecosystem assets. Observers noted that the attack bears striking resemblance to a prior Upbit breach in 2019 — when 342,000 ETH disappeared under circumstances later attributed to Lazarus and associated groups.

Security firms monitoring on-chain flows report that the speed and pattern of withdrawals mirror those from Lazarus-linked incidents. Analysts warn that the hack underscores persistent vulnerabilities when hot wallets — the always-online accounts exchanges use for frequent transactions — remain exposed to governance failures or credential compromises.

The timing of the incident coincided with a corporate milestone for Dunamu: the day saw the public announcement of a planned merger with technology firm Naver. Some security experts speculate that the attackers might have deliberately chosen the moment to maximise impact on market confidence and regulatory attention.

Upbit’s management emphasised that user assets held in cold storage remained untouched. The company began working immediately with token issuers and blockchain-analytics firms to freeze traceable stolen funds. Officials involved in the probe noted the laundering techniques — rapid mixing of tokens across multiple wallets and networks — reflect a refined modus operandi honed over several high-profile attacks.

A malicious Chrome extension disguised as a trading tool has been unmasked after evidence emerged that it silently siphons cryptocurrency from users executing swaps on the Solana network. The extension, known as Crypto Copilot, inserts secret transfer instructions into swaps made via the decentralized exchange Raydium, routing a portion of users’ SOL to an attacker-controlled wallet without their awareness. Crypto Copilot appeared in mid-2024 promoted as a […]

Weak cybersecurity strategies leave businesses exposed Businesses must prioritise strengthening leadership technology capabilities AI challenge is to balance efficiency gains and preserve human expertise KUALA LUMPUR, MALAYSIA – Media OutReach Newswire – 27 November 2025 – Malaysian businesses are rapidly adopting AI and data analytics, but weak cybersecurity strategies are leaving them exposed to growing digital threats, according to CPA Australia’s latest Business Technology Survey. While 87 […]

Cyber-security firms Kaspersky and VDC Research have estimated that global manufacturing organisations could incur losses exceeding US$18 billion in the first three quarters of 2025 due to ransomware attacks disabling production-line operations. According to their joint analysis, based on data from the Kaspersky Security Network, the average incident leads to around 13 days of operational disruption, with labour costs alone accounting for billions of dollars. The losses […]

Organizations are deploying artificial-intelligence-driven defences to counter increasingly sophisticated cyber threats as attackers harness the same technology to mount agile attacks. Leaders at major cybersecurity firms say the conflict between defenders and adversaries has entered a new phase, where speed, adaptability and automation are critical. The security firm Palo Alto Networks announced upgraded platforms designed to protect cloud assets and AI-based applications, citing the need to monitor […]

Cloud-software giant Salesforce has announced that it is investigating unauthorised activity involving applications published by vendor Gainsight, which may have enabled access to customer data through the Salesforce platform. The firm said it revoked all active access and refresh tokens related to the Gainsight apps and temporarily removed those applications from its marketplace. It emphasised this incident does not stem from a vulnerability in the Salesforce core […]

By Nitya Chakraborty Prime Minister Narendra Modi will be attending G20 summit at Johannesburg on November 22 and 23 amidst the diplomatic crisis for India over the Bangladesh demand for deportation of the ousted Prime Minister Sheikh Hasina from her shelter in India. On November 17, the International Crimes Tribunal of Bangladesh indicted Hasina on […]

The article Winning Perception Battle Against Bangladesh Is The Main Task Of Narendra Modi At G-20 Summit appeared first on Latest India news, analysis and reports on Newspack by India Press Agency).

HONG KONG SAR – Media OutReach Newswire – 19 November 2025 – In response to frequent wild bear sightings in Japan and other popular tourist spots, which have brought new risks and unease for travellers, Blue Cross (Asia-Pacific) Insurance Limited (“Blue Cross”) has announced the launch of a limited-time “Bear Attack Additional Coverage“¹ to provide customers with more extensive travel protection. Additionally, Blue Cross is rewarding SmartClub […]

Smart cities have emerged as a transformative vision for the future of urban life, integrating cutting-edge technologies to enhance living standards, boost sustainability, and improve service efficiency. However, as these cities evolve, they face growing concerns regarding cybersecurity. With vast amounts of sensitive data being collected, processed, and transmitted across networks, securing these data exchanges is paramount. The role of modern cryptographic solutions in safeguarding these environments […]

AccuKnox, a prominent player in Zero Trust Cloud-Native Application Protection Platforms, has entered into a strategic partnership with Frentree, a cybersecurity solutions provider based in South Korea. This collaboration seeks to enhance the security of cloud, container, and AI workloads for businesses across the region.

The integration of AccuKnox’s innovative security technologies with Frentree’s established presence in the South Korean market will enable enterprises to better defend against emerging cyber threats, particularly those targeting cloud-native environments. As businesses increasingly rely on cloud infrastructures and AI-driven workloads, the need for robust security frameworks that can scale and adapt to new vulnerabilities has never been more critical.

AccuKnox’s Zero Trust model, which operates on the principle of verifying every request within a network, regardless of origin, is designed to provide continuous protection against both internal and external threats. By requiring strict authentication and authorisation for all access requests, this security approach eliminates traditional trust models that have proven vulnerable in today’s dynamic digital landscape. This model is particularly effective in safeguarding complex cloud-native environments, where assets may be spread across multiple platforms and locations.

Frentree, with its local expertise and established relationships in South Korea, is poised to play a pivotal role in implementing these advanced security measures within the region. Their deep understanding of local enterprise needs, regulatory frameworks, and operational challenges positions them as an ideal partner for AccuKnox. By leveraging Frentree’s on-the-ground presence, AccuKnox aims to accelerate the adoption of Zero Trust security models, providing South Korean businesses with the tools necessary to meet their cybersecurity requirements in the face of increasing cloud adoption.

The collaboration between the two companies also highlights a broader trend in the cybersecurity industry, where regional partnerships are becoming more prevalent. With cyber threats becoming more sophisticated, businesses are increasingly looking for tailored solutions that not only address global challenges but also account for specific local risks and regulations. By working with a trusted regional partner like Frentree, AccuKnox can ensure that its Zero Trust CNAPP solutions are delivered in a way that meets the unique needs of the South Korean market.

South Korea, which has seen rapid digital transformation in recent years, is a particularly fertile ground for this kind of security innovation. As industries such as finance, telecommunications, and manufacturing embrace cloud computing and AI technologies, the country has become a prime target for cyberattacks. With high-profile breaches making headlines, there is growing pressure on organisations to improve their security postures. The Frentree-AccuKnox partnership is thus timely, as it provides local enterprises with a comprehensive security solution to mitigate these risks.

The partnership is also a response to the rising complexity of cyber threats. The increasing use of cloud-native applications and AI workloads introduces new vulnerabilities, which traditional security models struggle to address. Zero Trust security frameworks, with their focus on micro-segmentation and continuous monitoring, offer a promising solution to these challenges. By focusing on verifying every access attempt rather than trusting devices or users, these systems offer a much higher level of assurance against cyber threats.

Looking ahead, both AccuKnox and Frentree are committed to expanding their reach and impact in the region. This partnership is just the beginning, as the two companies plan to work closely to refine and enhance their offerings based on the specific needs of South Korean enterprises. With the cybersecurity landscape continuing to evolve rapidly, they aim to stay ahead of emerging threats by continuously innovating their security models.


DoorDash, the popular food delivery service, has confirmed that a cyber attack has compromised the personal data of millions of users. The breach, which has sparked significant concern, was the result of a sophisticated social engineering attack targeting the company’s systems. This incident has exposed sensitive user information, including names, email addresses, phone numbers, and in some cases, delivery addresses. The breach reportedly affected users across four […]

Cybersecurity breaches are becoming an increasingly costly issue for Indian enterprises, with nearly a quarter of organisations reporting losses exceeding $1 million over the past three years. This has prompted a sharp uptick in cybersecurity spending, especially in artificial intelligence and cloud security solutions, as businesses aim to protect themselves from sophisticated cyber threats. However, the sector still faces significant challenges, particularly in securing skilled talent to manage the growing complexity of cyber risks.

A recent report by PricewaterhouseCoopers highlights that 23% of Indian businesses have incurred losses of over $1 million due to cyber incidents, underscoring the severity of the issue. These breaches range from data theft and ransomware attacks to more advanced persistent threats targeting critical infrastructure. PwC’s findings suggest that the financial impact on Indian firms is only likely to rise as cybercriminals become more organised and capable, exploiting vulnerabilities in emerging technologies and systems.

The shift towards digital transformation and cloud adoption has undoubtedly exposed businesses to greater risk, with sensitive data being increasingly stored and accessed online. According to PwC, the cloud is now seen as both a critical business enabler and a potential vulnerability. As cloud infrastructures evolve, they are often targeted by cybercriminals seeking to exploit misconfigurations and inadequate security protocols.

In response, Indian businesses are ramping up their cybersecurity investments. Spending on AI-driven security solutions is one of the key focus areas. These technologies allow businesses to proactively identify and neutralise threats in real-time, enabling a faster response to evolving attack patterns. AI is particularly useful for detecting abnormal behaviour and potential risks that traditional security systems might miss. It is also being leveraged for predictive analytics to foresee potential vulnerabilities before they can be exploited by malicious actors.

However, despite the increased allocation of funds towards cybersecurity, the shortage of skilled professionals remains a significant roadblock. The demand for cybersecurity experts far outweighs the supply, with firms struggling to recruit individuals with the necessary expertise in areas such as AI, cloud security, and threat intelligence. The PwC report indicates that many organisations are forced to rely on third-party vendors to manage their cybersecurity needs, further driving up costs.

Experts suggest that to address the talent gap, Indian firms must invest in long-term solutions, such as upskilling existing employees and forging partnerships with educational institutions to nurture the next generation of cybersecurity professionals. The government has also been urged to play a more proactive role by fostering public-private collaborations to enhance the country’s overall cybersecurity ecosystem.

The rise of AI and cloud technologies has, however, brought additional complexities. While these tools can greatly improve security, they also introduce new attack vectors. Cloud environments, if not managed properly, can expose businesses to significant risks, including data breaches and unauthorised access. Moreover, the increased use of AI-driven solutions can create new challenges, such as ensuring the ethical deployment of AI and protecting against adversarial AI attacks.

Despite these hurdles, the Indian cybersecurity landscape is expected to see significant improvements over the coming years. As businesses continue to embrace AI and cloud technologies, security budgets are likely to increase, with a stronger emphasis on automated security measures and real-time threat detection. Additionally, as the global cyber threat landscape evolves, businesses are expected to collaborate more closely with government agencies and international organisations to stay ahead of cybercriminals.

By Nitya Chakraborty Bangladesh plunged into a fresh turbulence on Monday, November 17 after the International Crimes Tribunal (ICT) announced its verdict sentencing to death former Bangladesh Prime Minister Sheikh Hasina for” crimes against humanity” committed during last year’s student led agitation that led to the fall of her Awami League Government on August 5, […]

The article Bangladesh Plunges Into Fresh Turbulence After Tribunal’s Death Penalty To Sheikh Hasina appeared first on Latest India news, analysis and reports on Newspack by India Press Agency).

Netskope has partnered with NEVERHACK to introduce an innovative, fully managed Security Service Edge solution aimed at enhancing zero-trust cloud security. This new offering is designed to address the growing need for comprehensive protection in a rapidly evolving digital landscape, where organisations are increasingly reliant on cloud-based infrastructure. The collaboration combines Netskope’s advanced network and cloud security technology with NEVERHACK’s expertise in managed security services. The integrated […]

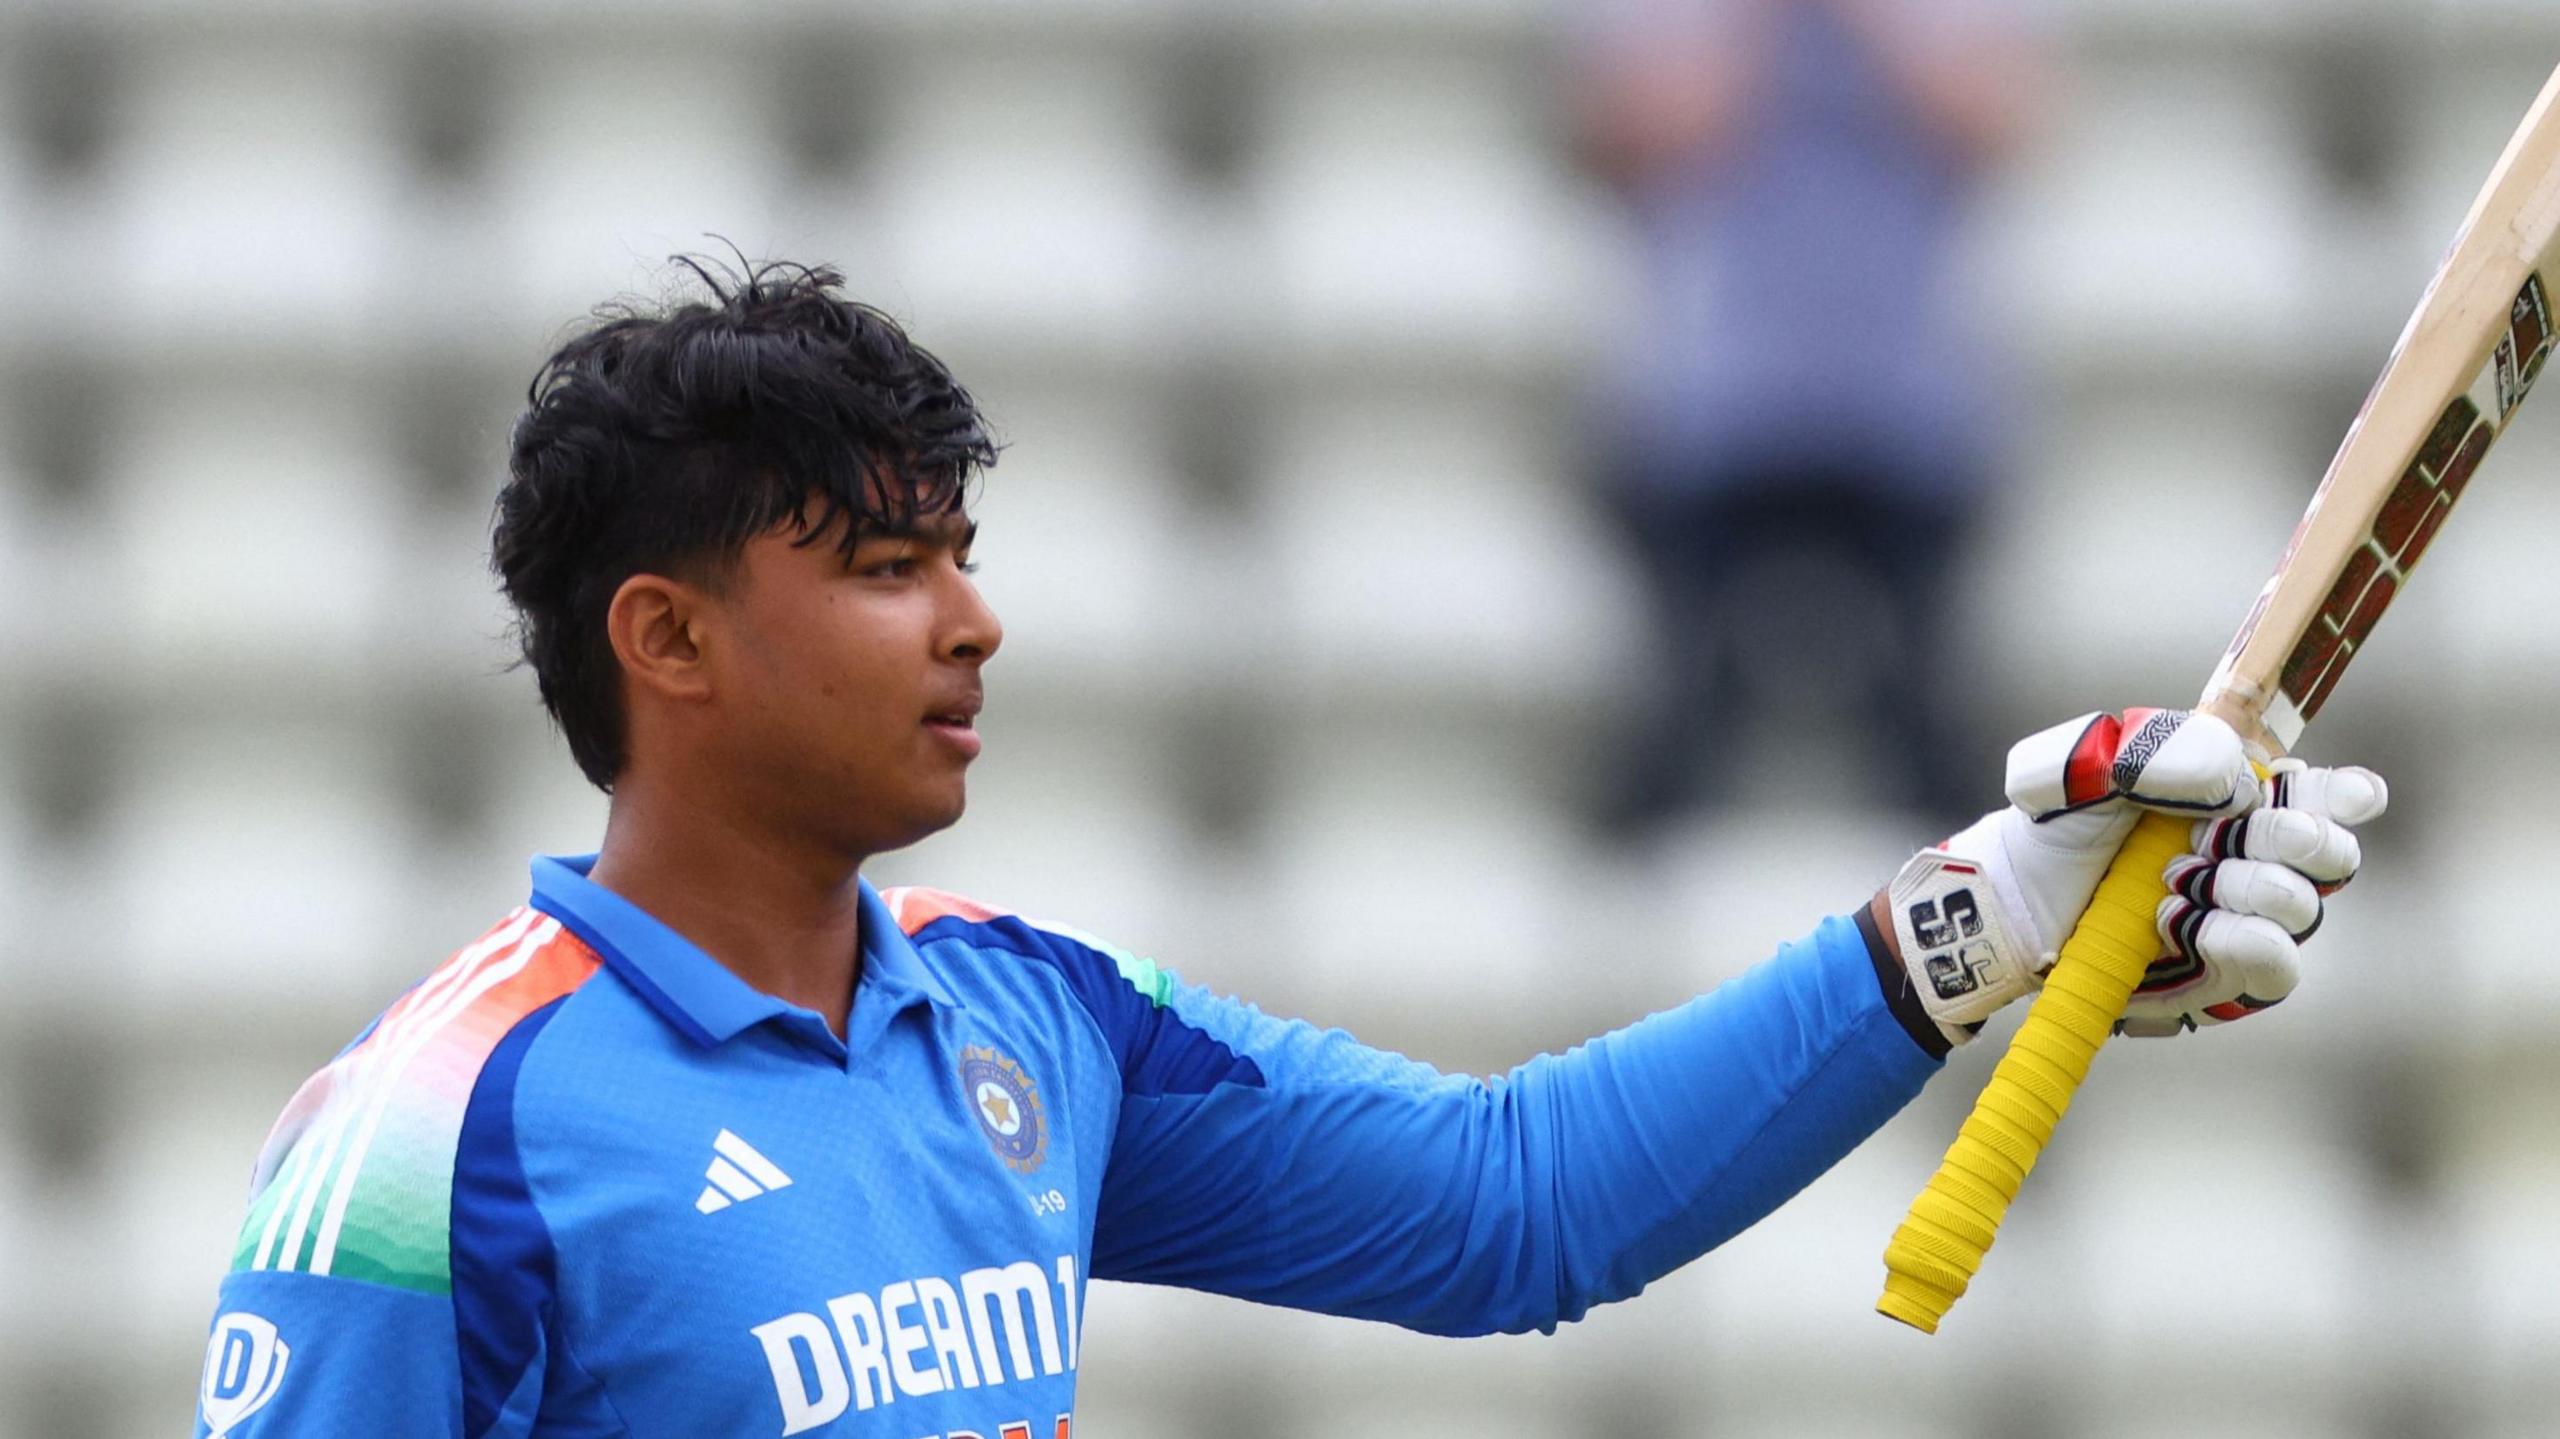
Vaibhav Suryavanshi, the rising star of Indian cricket, etched his name in the record books with a blistering 144 runs off just 42 balls in a T20 match against the UAE in Doha. This stunning performance not only cemented his place as one of the most exciting young talents in the game but also shattered existing records for the fastest and highest score in T20 cricket.

Suryavanshi, who has been making waves in domestic and international circuits, showed remarkable power-hitting prowess from the first ball. His innings was a display of controlled aggression, as he smashed 14 sixes and 10 fours, leaving the UAE bowlers helpless. The 144 runs came at an astonishing strike rate, and he achieved this feat in just 42 balls, surpassing the previous T20 record for the fastest century.

The young cricketer’s knock began with a rapid-fire start, and his confidence grew with each boundary. His ability to rotate strike while also finding the boundary at will left the crowd in awe. The UAE’s bowling attack, which had been formidable in previous matches, had no answers to his aggressive batting. Despite the best efforts of UAE’s bowlers, Suryavanshi dominated every over, quickly putting pressure on the opposition.

This performance comes as a significant milestone in Suryavanshi’s already impressive career, which includes several standout performances in domestic leagues and international competitions. His rise to fame has been meteoric, with scouts and former players alike taking note of his immense potential. His record-breaking knock in Doha has not only garnered attention but also raised expectations for his future in the international cricket scene.

The 18-year-old’s batting style is often compared to some of the game’s biggest hitters, but it is his temperament under pressure that sets him apart. In addition to his aggressive strokes, Suryavanshi has shown maturity in constructing innings, often shifting gears depending on the situation. His ability to accelerate at crucial moments makes him a player to watch in the coming years.

Cricket experts have already begun to discuss his potential role in the Indian national team, with some even speculating about his inclusion in upcoming international fixtures. With the Indian cricket team always on the lookout for dynamic and explosive players, Suryavanshi’s breakthrough performance in Doha only adds to the conversation about his possible call-up.

A vast data trove compiled by threat-intelligence firm Synthient has brought to light that 1.95 billion unique email addresses and approximately 1.3 billion passwords were exposed in credential-stuffing lists drawn from multiple underground sources. The corpus, now indexed by Have I Been Pwned, signals an escalation in the reuse-of-credentials risk by cyber-attackers targeting cross-platform logins. The aggregation effort by Synthient captured data embedded in previously breached credential […]

Belgium has become the latest nation to fall prey to a series of mysterious drone incursions that have unsettled Europe’s security landscape. This wave of drone activity, which has increasingly targeted critical sites across the continent, has prompted fears about potential espionage, sabotage, and escalating tensions in the region. For weeks, drones have been spotted hovering near strategic locations in various European countries, including military bases, nuclear […]

VISHNU RAJA
RYO YAMADA
HITORI GOTOH
IKUYO KITA
Just in:
Nvidia appoints Colette Kress interim chief after Huang departure // L’OCCITANE Celebrates 50 Years Of Provençal Craftsmanship With Holiday 2026 Collection // Microsoft outage leaves Outlook and Teams users disconnected // 11 Boutique Xinjiang Wineries to Debut in Singapore // Microsoft apologises as Outlook services recover after outage // UAE crews sustain coastal oil removal as beaches reopen // Sun World Ba Den Mountain marks Vietnam Culture Day, welcoming Cambodian visitors over Bon Om Touk // The Honey Trap Is The Headline, The Chip Pipeline Is The Story // From Dubai to the EU: how UAE-based crypto firms can expand under MiCA // Lego restores BrickLink marketplace after security investigation // OpenAI unveils ChatGPT Wallet for agent-led purchases // Inpex reaffirms Gulf oil strategy despite shipping constraints // Rooftop solar planning gaps behind power shortages // Yicura BioMed Advances Dual Capital and Industrial Strategy: Completes First Closing of Series B Financing Led by Gobi Partners // Hackers falsify NVIDIA GPU readings to mask cryptomining // Woman found dead as bank moves to repossess home // October Food Price Shock Has Far Reaching Consequences // China Reconciled To U.S. Curbs On Chips Exports, Woos South Korea For Supply // TORRAS Launches Two New iPhone Duo Cases from Its Popular Ostand Series, Addressing Foldable Phone Users’ Concerns About Difficult Stand Positioning and Scratches // EBANX and Eneba strengthen partnership in Latin America with 138% YoY growth in payment volume //