News related to
attack

By Nitya Chakraborty The two day uprising in Nepal on September 8 and 9 resulting in the ouster of the KPS Oli government following the attacks and burning of the Parliament Building, Supreme Court and the official and private residences of the present and former powerful ministers, was an expression of total revolt by the […]

Senator Ron Wyden is pressing the Federal Trade Commission to investigate Microsoft over what he terms its “gross cybersecurity negligence,” asserting that inherent weaknesses in Microsoft’s security framework enabled a damaging ransomware attack on a hospital system. Wyden’s letter, dated 10 September 2025, identifies how default encryption settings and flawed user-interface design played pivotal roles in the infiltration of Ascension, one of the largest non-profit health systems […]

A pioneering study now suggests that heart attacks may, in some cases, result from infectious processes rather than solely lifestyle and cholesterol risks. Researchers from Finland and the UK have uncovered compelling evidence that bacterial biofilms hidden within arterial plaques can lie inactive for decades and, when triggered by a viral infection or other external stimulus, may ignite inflammation, rupture arterial plaques, and ultimately lead to myocardial […]

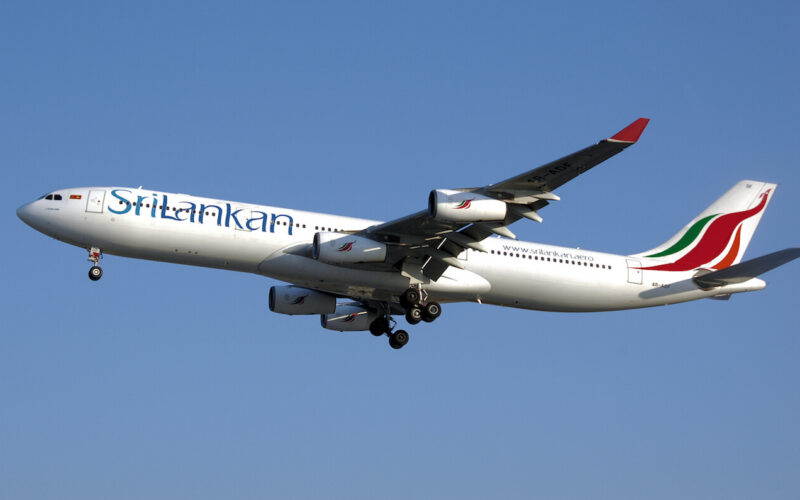
SriLankan Airlines has suspended services to Kathmandu after authorities closed Tribhuvan International Airport amid nationwide unrest, forcing cancellations on the Colombo–Kathmandu route and disrupting onward travel plans.

Airport officials said flight operations at Kathmandu would remain shut until the evening as security forces moved to stabilise the capital, while armoured patrols and curfews kept streets largely empty following two days of violent demonstrations. Airline pauses Kathmandu services amid escalating unrest.

Protests that began over corruption and economic grievances have turned deadly, with soldiers guarding parliament and key government buildings after arson attacks and clashes. Reuters reported at least 19 fatalities over 48 hours and said the turmoil prompted a nationwide shutdown affecting aviation, retail and public services.

Knock-on effects spread across regional air corridors. Multiple Kathmandu-bound flights were diverted to India, including four routed to Lucknow as the closure took effect, while IndiGo extended a temporary halt of services to and from Kathmandu to the early evening. Other carriers announced cancellations through the day as they assessed security and operational risks.

SriLankan confirmed the cancellation of flights UL181 and UL182 on Wednesday and advised ticketed passengers to contact their booking channels. Local news outlets in Colombo said the airline’s suspension would remain until further notice, aligning with guidance to monitor official updates as authorities reviewed conditions at the airport.

Regional governments urged caution for travellers. India advised its citizens to defer trips to Nepal and for those already in the country to remain indoors, as curfews and transport disruptions left tourists and business travellers stranded across Kathmandu Valley and beyond.

Live updates from Kathmandu indicated authorities were weighing phased resumptions of essential services alongside crowd-control measures. Airports and transport links were prioritised for restoration once security agencies deemed conditions manageable, with the army coordinating road clearance and fire response in affected districts.

Airlines across South Asia adjusted schedules through the afternoon, with Indian and regional carriers cancelling or retiming Kathmandu rotations while offering waivers. Public statements from operators noted the situation remained fluid and that customer notifications would follow as airspace and airport status changed.

SriLankan’s decision underscores how quickly a single-airport closure can ripple through a network heavily reliant on narrow time buffers and daylight slots into high-altitude hubs. For passengers booked to or through Kathmandu, carriers advised monitoring flight status pages and staying in contact with travel agents as curfew orders and airport operating hours evolve.

A newly revealed flaw in Apple’s CarPlay ecosystem enables attackers to achieve remote code execution with root privileges, raising serious cybersecurity concerns for connected vehicles. Tracked as CVE-2025-24132 and identified by the Oligo Security Research team, the weakness stems from a stack-based buffer-overflow flaw in AirPlay protocol implementations used by CarPlay systems. It remains exploitable over Wi-Fi via a wormable, zero-click exploit—allowing attackers to take full control […]

The cybersecurity community is confronting a highly evolved phishing campaign that exploits Google’s no-code AppSheet platform to harvest credentials and two-factor authentication codes. Attackers are sending authentic-looking emails from the legitimate domain noreply@appsheet. com—circumventing common defences such as SPF, DKIM and DMARC—and impersonating Meta to pressure users into submitting sensitive data. On 20 April 2025, AppSheet-originated emails made up 10.88 percent of all phishing attempts intercepted by […]

Poland activated air defences and scrambled fighter jets after drones from Russia crossed into its airspace during overnight strikes on Ukraine, with the military confirming it used weapons to neutralise targets. The Operational Command said Polish airspace was “repeatedly violated by drone-type objects” and described an ongoing operation to identify and destroy them. Authorities placed ground-based systems and radar on maximum alert while Polish and allied aircraft […]

Advertisements

Protesters breached Nepal’s federal parliament complex in Kathmandu and set parts of the building on fire on Tuesday, escalating a youth-led movement that has convulsed the country and prompted the prime minister’s resignation. Authorities confirmed fatalities and hundreds of injuries over two days of clashes that centred on the New Baneshwar area housing the legislature. The death toll rose to 19 after security forces used live ammunition, […]

Plex has warned its users about a serious security lapse following unauthorised access to a database containing scrambled passwords and authentication details, urging swift action to protect accounts. A database breach exposed a confined set of user data, including email addresses, usernames, and securely hashed passwords, along with authentication information. Plex assures that no credit card or payment data were compromised, as such information is not stored […]

Matein Khalid My readers and friends know that I have been a boring perma-bull on gold since early 2024, when it became obvious that the People’s Bank of China was accumulating gold bullions as a hedge against an overvalued King Dollar and a capricious White House, which had just seized $300 billion in Russian central bank reserves to punish Putin’s invasion of Ukraine. The bullish gold trade […]

Security investigators uncovered a sweeping campaign named GhostAction supply chain campaign that compromised 327 GitHub user accounts across 817 repositories on 5 September 2025. Attackers inserted deceptive workflow files, disguised as security enhancements, into projects—including the open-source FastUUID library—extracting and exfiltrating 3,325 secrets such as PyPI, npm and DockerHub tokens to an external server. The campaign began when GitGuardian noted a suspicious commit on 2 September by […]

A wave of ransomware incidents has incapacitated over 300 co-operative banks across India, exposing deep vulnerabilities tied to outdated VPN-based security. These attacks underline the urgent need for a shift towards modern access frameworks such as Zero Trust Network Access. Operational disruptions began when C-Edge Technologies—a key IT provider to numerous co-operative banks—was targeted by ransomware on 31 July 2024. NPCI responded swiftly by isolating C-Edge from […]

Undersea cables in the Red Sea were severed on September 6, 2025, causing significant internet disruptions across parts of Asia and the Middle East. The affected cables include the South East Asia–Middle East–Western Europe 4 and the India–Middle East–Western Europe, both vital for regional connectivity.

Microsoft reported increased latency for users in the Middle East, while NetBlocks, a digital rights group, confirmed that the outages impacted countries such as India and Pakistan. The disruptions have also affected cloud services, with Microsoft Azure experiencing service degradation due to rerouted traffic.

The cause of the cable cuts remains unclear. While there is concern that the Houthi rebels in Yemen may have targeted the cables as part of their campaign related to the Israel-Hamas conflict, the group has denied responsibility for such attacks. In early 2024, the Houthis had threatened to target undersea cables, but no direct evidence has been presented linking them to the current incident.

A Chinese state-sponsored cyber-espionage group known as Salt Typhoon almost surely infiltrated Canadian telecommunications systems during the campaign that exfiltrated data belonging to millions of Americans. The intrusion, part of the broader Chinese-backed hackers almost certainly breached Canadian networks operation, raises alarm over the growing reach and sophistication of cross-border cyber-threats. The FBI and Canada’s Centre for Cyber Security have attributed the breach in Canada to Salt […]

Chess.com has confirmed that cyber-attackers exploited a third-party file-transfer application, exposing personal details of 4,541 users—including at least one individual in Maine. The breach occurred on 5 June 2025, with a second intrusion on 18 June 2025, but came to light only on 19 June, when an internal investigation began. Chess.com breach exposes personal data of 4,541 users remained unnoticed until that date. Chess.com operates from Orem, […]

BruteForceAI accelerates credential testing by automating form discovery and attack workflows with human‑like finesse. Security teams and penetration testers now gain a powerful tool that merges AI‑driven analysis and ethical safeguards, promising deeper insights into authentication weaknesses across web applications. BruteForceAI enables swift parsing of HTML to pinpoint login fields with near‑precise CSS selector generation— reportedly accurate in approximately 95 per cent of real‑world scenarios. Once fields are mapped, […]

Kraken’s Chief Security Officer, Nick Percoco, has issued a warning to users about a sophisticated phishing campaign impersonating the platform. Attackers are dispatching emails that replicate Kraken’s branding—with near-identical logos, fonts and messaging—to pressure recipients into taking urgent action. The emails allege the need to accept “updated terms” within a two‑day window, a tactic intended to prompt hasty decisions. In nearly every instance, the sender urges recipients to download remote desktop software such as AnyDesk under the guise of offering support. Percoco emphasises that Kraken will never request installation of such tools from users.

Such phishing attempts exploit both visual authenticity and psychological manipulation—cultivating a sense of urgency to override caution. According to official guidance, Kraken will only use verified domains—including @kraken. com, @futures. kraken. com, @email2. kraken. com, @email. krak. app and other specific, approved addresses—to communicate with users. Any other source should be treated as suspicious.

This incident reflects a broader escalation in phishing tactics across the crypto sector. Industry data indicates that phishing attacks surged more than 200% in August, resulting in losses exceeding $66 million. One single breach accounted for $55 million in stolen funds. Abnormal AI, a cybersecurity firm, attributes the elevated threat level to more advanced techniques—emails originating from older, seemingly trustworthy domains, employment of social engineering, and polished language devoid of traditional red‑flag keywords. These newer attacks are designed to bypass legacy email filters and evade automated detection.

Users are urged to remain vigilant and adopt a security-first mindset. The most effective defence measures include verifying sender addresses, suspecting communications that evoke fear or demand immediate compliance, and avoiding email links entirely—especially those prompting software installation. Instead, users should always navigate directly to Kraken’s official URL (), ideally via a bookmarked link, and contact support through trusted channels if unsure.

Kraken’s approach is rooted not only in technological safeguards but also in cultivating user awareness. Percoco has previously underscored that phishing and social engineering are among the most common threats to both users and employees. Kraken’s layered filtering and a security-conscious culture help reduce risk, though no system is foolproof. Humans remain the critical last line of defence.

With trusts at stake, exchanges are under mounting pressure to enhance transparency and user education. Some platforms have introduced anti‑phishing codes or digital signatures to help users verify authenticity. While Kraken currently relies on verified domains and user education, the challenge continues to evolve as attackers adopt more deceptive techniques.

A wave of data indicates that staff reliance on informal messaging platforms, particularly WhatsApp, is opening critical cybersecurity gaps across organisations. The 2025 KnowBe4 Africa Annual Cybersecurity Survey shows that 93 per cent of African professionals use WhatsApp for work purposes—surpassing email and even messages sent via enterprise-grade tools. Alarmingly, up to 80 per cent of these users operate from personal devices that often lack proper management […]

A client‑side remote code execution flaw in Google Web Designer for Windows poses a severe threat, allowing attackers to inject malicious CSS into configuration files to subvert internal APIs and seize full control of affected systems. The bug impacts every build prior to version 16.4.0.0711, and a fix has already been deployed in that release. Security researcher Bálint Magyar publicly disclosed the vulnerability, tracked as CVE‑2025‑4613, by demonstrating […]

Okta Threat Intelligence has uncovered a widespread campaign exploiting malicious online ads to tempt hotel and vacation rental professionals into disclosing access credentials. Attackers have been deploying paid search advertisements on platforms such as Google Search, impersonating familiar hospitality service providers. These deceptive ads lead victims to counterfeit login portals of cloud‑based property management and guest messaging systems, with the goal of harvesting usernames, passwords and one‑time authentication codes.

The adverts specifically mimic legitimate service providers—Okta researchers identified at least thirteen hospitality‑focused brands being spoofed. Rather than redirecting users to authentic company sites, these ads channel them to typosquatted domains that host visually convincing but fraudulent login pages. Through these pages, attackers collect credentials and MFA codes, undercutting security even when multi‑factor authentication is in place.

The phishing sites also incorporate tracking capabilities—collecting geolocation, session data, bot detection metrics and analytics—to better tailor the campaign and measure its effectiveness.

This strategy exemplifies the growing menace of malvertising, where advertisements themselves become vectors for malware distribution or phishing. Malwarebytes data reflects dramatic growth in such campaigns: a 42 per cent month‑on‑month escalation in fall 2023, followed by another rise of 41 per cent between July and September. Malicious ads frequently appear alongside legitimate search results, granting them apparent credibility and increasing the chance of successful deception.

Experts point out the dual advantage these tactics offer to threat actors: extensive reach through ad networks and a veneer of trust derived from the proximity to legitimate search results.

The hospitality sector faces unique vulnerabilities as hotels and rental operators increasingly rely on cloud systems to manage bookings, guest interactions and operational workflows. With projections indicating that by 2028 some 76 per cent of travel and tourism revenues will be generated online, these sectors have become especially tempting targets.

This campaign represents a convergence of two escalating cybersecurity concerns: the explosive growth of malvertising and the rising exposure of hospitality infrastructure to credential-based attacks. While the ads serve as the initial lure, the fraudulent credential capture enables potential downstream compromises across cloud services that manage guest data, reservations and even messaging systems.

For hotel and rental operators, the implications are severe—a breach of access credentials might cascade into broader system intrusions, guest data exposure and operational disruption. Preventive measures should include rigorous verification of URLs before entering credentials, vigilant monitoring of sponsored search results for impostor ads, widespread staff awareness and training, and robust technical controls like domain-based message authentication and behavioural anomaly detection.

Journalistic integrity demands careful cross-verification of details. Okta’s findings were drawn from their threat intelligence and threat detection capabilities tailored to enterprise identity environments. Malvertising trends are substantiated by independent cybersecurity data from industry researchers such as Malwarebytes. The convergence of these findings draws a consistent picture: the hospitality industry must brace for sophisticated phishing campaigns delivered via the same channels they rely on for marketing.


By Nitya Chakraborty Prime Minister Narendra Modi’s bilateral talks with the Chinese President Xi Jinping on Sunday at Tianjin in China on the sidelines of Shanghai Cooperation Organisation (SCO) summit have sent some very positive signals which may herald the evolution of an independent foreign policy of India voicing the interests of the Global South. […]

Tuta has added a user-controlled key verification feature that brings heightened assurance to encrypted email and calendar exchanges. The feature allows senders and receivers to confirm the authenticity of public encryption keys—either by scanning a QR code or comparing a verification code—before communication begins. Once verified, the client safeguards future exchanges by ensuring the key remains unchanged, alerting users to any unexpected alteration that might signal interception. […]

A sophisticated cyber‑espionage operation is exploiting Windows shortcut files disguised alongside seemingly genuine PDF newsletters to surreptitiously infiltrate institutions across Asia and the Middle East. This deeply orchestrated campaign has been attributed to APT‑37, a North Korean‑linked group known for precision targeting. Threat actors dispatch archives containing a PDF titled “National Intelligence Research Society Newsletter” together with a malicious companion: an LNK file that mirrors the PDF’s […]

WhatsApp has rolled out an urgent update for its iOS and macOS apps after detecting a zero‑click exploit—one that required no user interaction—to deliver spyware to a small number of targeted users. The vulnerability allowed attackers to bypass authorisation checks when processing linked-device synchronization messages—specifically in WhatsApp for iOS before version 2.25.21.73, WhatsApp Business for iOS before version 2.25.21.78, and WhatsApp for Mac before version 2.25.21.78. This flaw was chained […]

VISHNU RAJA
RYO YAMADA
HITORI GOTOH
IKUYO KITA