News related to
attack

A significant cyberattack has struck Tata Technologies, a subsidiary of Tata Motors, resulting in the exposure of 1.4 terabytes of sensitive data on the dark web. The breach, orchestrated by the ransomware group Hunters International, has compromised a vast array of confidential information, including employee records, corporate documents, and client contracts. This incident underscores the escalating threat posed by sophisticated cybercriminal organizations targeting multinational corporations. The leaked […]

Cybersecurity researchers have identified a novel malware strain, dubbed ‘nullifAI’, embedded within machine learning models hosted on Hugging Face, a leading platform for sharing AI models and datasets. This discovery underscores a growing threat vector in the AI community, highlighting vulnerabilities in platforms that facilitate the sharing and deployment of ML models. The ‘nullifAI’ malware employs a sophisticated technique involving corrupted Pickle files—a Python-specific method for serializing […]

North Korea’s state-sponsored hacking collective, the Lazarus Group, has launched a sophisticated campaign targeting software developers through the npm ecosystem. By introducing six malicious packages, the group aims to infiltrate development environments, steal sensitive credentials, exfiltrate cryptocurrency data, and establish persistent backdoors on compromised systems.

The identified packages—’is-buffer-validator’, ‘yoojae-validator’, ‘event-handle-package’, ‘array-empty-validator’, ‘react-event-dependency’, and ‘auth-validator’—employ typosquatting techniques, mimicking legitimate and widely-used libraries to deceive developers into installing them. Collectively, these packages have been downloaded over 330 times, underscoring the potential reach of this malicious operation.

Upon installation, these packages execute obfuscated JavaScript code designed to collect system environment details, including hostnames, operating systems, and directory structures. They specifically target browser profiles from Chrome, Brave, and Firefox to extract stored login credentials. Additionally, the malware seeks out cryptocurrency wallet files associated with Solana and Exodus, aiming to pilfer digital assets. The extracted data is then transmitted to a hardcoded command-and-control server, facilitating unauthorized access and potential financial theft.

This campaign is part of a broader strategy by the Lazarus Group to exploit software supply chains. By compromising open-source repositories like npm, the group can infiltrate developer environments, leading to widespread distribution of their malware. Similar tactics have been observed in previous campaigns involving GitHub and the Python Package Index , highlighting the group’s evolving methodologies in targeting the software development community.

The Lazarus Group’s focus on cryptocurrency assets is well-documented. Notably, the group was implicated in the $1.46 billion Ethereum theft from the Bybit exchange, marking one of the largest known financial thefts in history. The rapid laundering of the stolen funds post-attack demonstrates the group’s advanced capabilities and poses significant challenges for cybersecurity defenders.

The $1.5 billion theft from Dubai-based cryptocurrency exchange Bybit has prompted the European Union to initiate an investigation into OKX, another prominent crypto platform, to assess compliance with the Markets in Crypto-Assets regulation. The probe seeks to determine whether OKX’s operations fall under MiCA’s jurisdiction and, if so, what enforcement actions may be warranted.

On February 21, 2025, Bybit suffered a cyberattack resulting in the loss of approximately 400,000 Ethereum tokens, valued at $1.5 billion, marking the largest cryptocurrency exchange hack to date. The Federal Bureau of Investigation attributed the heist to North Korea’s Lazarus Group, known for previous high-profile cybercrimes.

In response to the Bybit incident, European regulators have intensified their scrutiny of cryptocurrency exchanges operating within the EU. The focus has turned to OKX to evaluate its adherence to MiCA, a regulatory framework established to oversee crypto-assets and ensure consumer protection within the European Union.

MiCA, enacted to create a unified regulatory environment for crypto-assets across EU member states, requires platforms like OKX to comply with specific standards to operate legally within the region. The current investigation aims to ascertain whether OKX’s activities align with these standards and to identify any potential regulatory breaches.

The outcome of this investigation could have significant implications for OKX and other cryptocurrency exchanges operating in the EU. Potential sanctions may include fines, operational restrictions, or even prohibition from offering services within the European market. This development underscores the EU’s commitment to enforcing regulatory compliance to protect consumers and maintain financial stability in the rapidly evolving crypto industry.

The Bybit hack has also reignited discussions about the security vulnerabilities inherent in cryptocurrency exchanges. Despite Bybit’s swift action to replenish its reserves within 72 hours by securing emergency funding from firms such as Galaxy Digital, FalconX, and Wintermute, the incident has raised concerns about the adequacy of existing security measures. The Lazarus Group exploited vulnerabilities in Bybit’s security infrastructure, transferring the stolen funds to multiple unidentified addresses, thereby complicating recovery efforts.

A massive cyberattack disrupted X, formerly known as Twitter, on March 10, 2025, affecting tens of thousands of users worldwide. The hacking group “Dark Storm” claimed responsibility for the distributed denial-of-service attack, while Elon Musk, owner of X, suggested the assault originated from IP addresses traced to Ukraine. The outage began early Monday morning, with users reporting difficulties accessing the platform, posting content, and sending messages. According […]

Elon Musk, owner of the social media platform X, formerly known as Twitter, claimed on Monday that the platform was under a “massive cyberattack” after widespread outages affected tens of thousands of users globally. The disruptions began early in the day, with reports of service issues peaking at over 40,000 by mid-morning, according to data from Downdetector, a website that tracks online service interruptions. Users in major […]

HANOI, VIETNAM – Media OutReach Newswire – 28 February 2025 – The rise of powerful artificial intelligence (AI) like DeepSeek is transforming the world at an unprecedented pace, sparking enthusiasm and deep concerns about its potential risks. On that subject, “AI godfather” Yoshua Bengio – Laureate of the 2024 VinFuture Grand Prize – highlighted the urgent need for national and global efforts to regulate AI and ensure […]

Advertisements

In a historic shift, the White House has confirmed that U.S. officials are engaging in direct talks with Hamas, aiming to secure the release of American hostages held in Gaza. This development marks a departure from the longstanding U.S. policy of avoiding direct negotiations with the group designated as a terrorist organization since 1997. White House Press Secretary Karoline Leavitt acknowledged these discussions, stating, “These are ongoing […]

A hacker has successfully laundered 499,395 Ethereum , valued at approximately $1.04 billion, stolen from the cryptocurrency exchange Bybit on February 21, 2025. This incident marks one of the most significant security breaches in the cryptocurrency industry to date.

The Federal Bureau of Investigation has attributed the theft to North Korean-affiliated hacking groups, notably the Lazarus Group and TraderTraitor. These groups have been implicated in previous cyberattacks aimed at generating revenue for North Korea’s sanctioned economy.

The hacker employed sophisticated techniques to infiltrate Bybit’s security systems, executing a phishing scam that led to the unauthorized transfer of funds. The stolen assets included liquid-staked Ether , Mantle Staked ETH , and other ERC-20 tokens.

Following the theft, the hacker utilized decentralized platforms, primarily THORChain, to launder the stolen ETH. This method involved converting the assets into various cryptocurrencies, complicating efforts to trace and recover the funds.

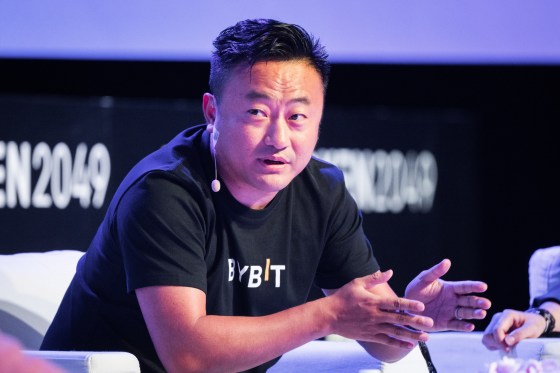
Bybit’s CEO, Ben Zhou, reported that approximately 3% of the stolen funds have been intercepted and frozen, while 20% have become untraceable. The remaining 77% are still under investigation, with efforts ongoing to recover the assets.

The incident has raised concerns about the security measures employed by cryptocurrency exchanges. Experts highlight the need for enhanced security protocols to protect against increasingly sophisticated cyber threats.

A massive security breach at Dubai-based cryptocurrency exchange Bybit has resulted in the theft of approximately $1.5 billion in Ethereum , marking one of the largest heists in the digital currency sector. The attack, attributed to North Korean hacking groups Lazarus and TraderTraitor, has raised significant concerns about cybersecurity within the cryptocurrency industry.

The Federal Bureau of Investigation has linked the theft to these North Korean-affiliated hackers, who reportedly utilized malware-infected cryptocurrency trading applications to infiltrate Bybit’s systems. This method allowed them to drain substantial amounts of Ethereum from the exchange’s reserves. The stolen funds are believed to be funneled into North Korea’s nuclear and missile programs, highlighting the geopolitical implications of such cybercrimes.

In response to the breach, Bybit’s CEO, Ben Zhou, announced that the exchange has fully restored its Ethereum reserves. The company secured approximately 446,870 ETH through strategic acquisitions and loans, ensuring that all client assets remain backed on a one-to-one basis. This swift action aims to maintain customer trust and stabilize the platform following the unprecedented hack.

The impact of the theft extended beyond Bybit, affecting the broader cryptocurrency market. Funding rates across various platforms experienced a decline, reflecting heightened uncertainty among investors. Ethereum’s price volatility increased as traders reacted to the news, with some large holders, or “whales,” expressing caution amid the fluctuating market conditions.

Despite the initial shock, there are signs of recovery within the market. Bybit’s replenishment of its Ethereum reserves has contributed to a gradual restoration of confidence among users and investors. Additionally, the exchange has launched a $140 million bounty program to incentivize information leading to the recovery of the stolen assets and the identification of the perpetrators.

The hackers have reportedly laundered approximately $335 million of the stolen funds, leaving around $900 million unaccounted for. This ongoing movement of assets poses challenges for authorities attempting to trace and recover the stolen cryptocurrency. The laundering process involves complex techniques, including transferring funds across multiple blockchains and utilizing mixing services to obscure the transaction trail.

Bybit has pledged to enhance its security protocols to prevent future breaches. The exchange is collaborating with international law enforcement agencies and cybersecurity firms to investigate the hack and mitigate potential risks. This incident underscores the critical need for robust security measures within the cryptocurrency industry, as exchanges remain prime targets for sophisticated cyberattacks.

The broader implications of the Bybit hack have prompted discussions about regulatory oversight and the responsibility of exchanges to protect user assets. As the digital currency market continues to evolve, ensuring the security of platforms and the integrity of transactions remains a paramount concern for both industry participants and regulators.

In the aftermath of the hack, Bybit conducted a comprehensive audit to verify the restoration of its reserves. The exchange plans to release an updated proof-of-reserves report, utilizing a Merkle tree structure to provide transparency and reassure clients of the platform’s solvency. This move aims to rebuild trust and demonstrate Bybit’s commitment to safeguarding user assets.

The cryptocurrency community has rallied in support of Bybit, with industry leaders emphasizing the importance of collective efforts to combat cyber threats. Collaborative initiatives are being explored to share threat intelligence and develop standardized security practices across exchanges. These efforts aim to fortify the industry’s defenses against increasingly sophisticated hacking groups.

While the Bybit hack serves as a stark reminder of the vulnerabilities within the cryptocurrency ecosystem, it also highlights the resilience of platforms and their ability to respond to crises. By swiftly restoring its reserves and implementing enhanced security measures, Bybit aims to turn this challenging episode into an opportunity to strengthen its operations and contribute to the overall security of the digital asset landscape.

Internxt, a Valencia-based tech company, has become the first cloud storage provider to implement post-quantum encryption, marking a significant advancement in data security. This move addresses growing concerns about the potential threats posed by quantum computing to traditional encryption methods. Quantum computers, leveraging the principles of quantum mechanics, have the potential to perform computations at speeds unattainable by classical computers. This capability threatens current encryption protocols, as […]

The United States Securities and Exchange Commission has concluded its investigation into cryptocurrency exchange Gemini, opting not to pursue any enforcement action. This decision, communicated to Gemini’s legal counsel, marks the end of a protracted inquiry that began in January 2023.

Gemini’s co-founder, Cameron Winklevoss, announced the closure of the investigation, expressing relief but also voicing strong criticism of the SEC’s approach. He stated that while the conclusion of the probe is a positive development, the extensive investigation inflicted significant financial and operational harm on the company. Winklevoss detailed that Gemini incurred tens of millions of dollars in legal expenses and suffered losses amounting to hundreds of millions due to diminished productivity, creativity, and innovation.

The SEC’s investigation into Gemini was primarily focused on the company’s “Earn” program, launched in partnership with Genesis Global Capital. This program allowed users to lend their cryptocurrency holdings in exchange for interest payments. In January 2023, the SEC charged both Gemini and Genesis with offering unregistered securities through this initiative. Despite the closure of the investigation, the SEC has indicated that this decision does not preclude the possibility of future action if new information emerges.

Winklevoss did not mince words in his critique of the SEC’s conduct, accusing the agency of engaging in tactics that he described as bullying, harassment, and unwarranted attacks on a legitimate industry. He argued that such regulatory actions have broader implications, stifling innovation and deterring economic growth within the cryptocurrency sector. Winklevoss emphasized that the damage extends beyond Gemini, suggesting that the SEC’s aggressive stance has led to substantial economic losses across the industry, including missed opportunities for growth and development.

The conclusion of the Gemini investigation is part of a broader pattern of the SEC reevaluating its approach to cryptocurrency regulation. In recent days, the agency has also closed investigations into other prominent crypto entities, including Coinbase, Uniswap Labs, and OpenSea, without pursuing enforcement actions. These developments suggest a potential shift in the SEC’s regulatory strategy under the new administration.

Former SEC Chair Gary Gensler, known for his stringent regulatory stance on cryptocurrencies, resigned on January 20, 2025, coinciding with the inauguration of President Donald Trump’s second term. Gensler’s tenure, which began in 2021, was marked by an aggressive approach toward the crypto industry, with the SEC initiating numerous enforcement actions against various crypto firms. His departure has been followed by a series of decisions indicating a possible softening of the SEC’s posture toward cryptocurrency regulation.

Winklevoss views the closure of the investigation as a significant milestone in what he terms the “war on crypto.” However, he cautioned that the damage inflicted by the SEC’s previous actions may have long-lasting effects, potentially deterring innovation and prompting talent to exit the industry. To prevent similar situations in the future, Winklevoss advocates for thoughtful legislation that provides clear guidelines for the cryptocurrency sector. He also suggests that there should be accountability measures for regulatory bodies, proposing that officials responsible for what he deems “sham investigations and baseless enforcement actions” face consequences, including termination and prohibition from future agency employment.

The SEC has not issued a public statement regarding the closure of the Gemini investigation. The agency’s recent actions, including the dismissal of cases against other cryptocurrency firms, may indicate a strategic reassessment of how to regulate the rapidly evolving digital asset landscape. Industry stakeholders are closely monitoring these developments, as they could signal a more collaborative and less adversarial regulatory environment moving forward.

As the cryptocurrency industry continues to mature, the relationship between regulatory bodies and crypto enterprises remains a critical factor in shaping the future of digital finance. The resolution of the Gemini case, along with similar recent decisions, may pave the way for a more balanced approach that fosters innovation while ensuring compliance and protecting investors.

In the wake of these developments, market participants are cautiously optimistic. The closure of high-profile investigations without enforcement actions could restore confidence and encourage renewed investment in the sector. However, the call for clear and fair regulatory frameworks persists, as the industry seeks to navigate the complexities of compliance in a landscape that has been, until now, marked by regulatory uncertainty.

By K Raveendran Tension is mounting over the Centre’s plan for offshore sand mining, with the issue rapidly evolving into yet another flashpoint between the Modi government and opposition-led coastal states. At the heart of the controversy lies not just the environmental and economic concerns raised by the affected communities but also the underlying political […]

Cybercriminals are leveraging counterfeit GitHub repositories to distribute malware, resulting in the theft of approximately $485,000 in Bitcoin, according to cybersecurity firm Kaspersky. The malicious campaign, dubbed “GitVenom,” has been active for at least two years and primarily targets developers and cryptocurrency enthusiasts. Kaspersky’s Global Research and Analysis Team identified over 200 deceptive repositories on GitHub. These repositories masquerade as legitimate projects, such as automation tools for […]

Google has announced a significant overhaul to its Gmail authentication process, transitioning from SMS-based two-factor authentication to QR code verification. This change aims to enhance user security and address vulnerabilities associated with SMS authentication methods. Ross Richendrfer, Google’s head of security and privacy public relations, confirmed the company’s plan to move away from SMS authentication. He emphasized that, similar to their initiative to eliminate traditional passwords through […]

In an unprecedented cyberattack, cryptocurrency exchange Bybit has suffered a $1.5 billion theft, marking the largest crypto heist to date. The U.S. Federal Bureau of Investigation has intensified its search for Park Jin Hyok, a North Korean hacker linked to the Lazarus Group, suspected of orchestrating this massive breach.

Bybit reported that during a routine transfer between digital wallets, an attacker manipulated the process, diverting approximately $1.5 billion worth of Ethereum to an unidentified address. CEO Ben Zhou assured customers that their remaining assets are secure, though withdrawal requests may experience delays. Zhou emphasized the company’s financial resilience, stating that Bybit can absorb the loss and remain solvent even if the stolen funds are not recovered.

The FBI has identified the Lazarus Group, also known as APT38, as the entity responsible for this theft. This group, comprising North Korean state-sponsored cyber actors, has a notorious history of high-profile cybercrimes. Park Jin Hyok, a key member, is allegedly involved in several significant cyber intrusions, including the 2014 Sony Pictures hack and the 2017 WannaCry ransomware attack. The FBI’s wanted list describes Park as a state-sponsored programmer involved in some of the costliest computer intrusions in history.

In response to the breach, Bybit has taken swift measures to mitigate the impact. The company conducted a fresh audit and restored its reserves to a 1:1 ratio within 72 hours of the incident. Blockchain analytics firm Lookonchain reported that Bybit purchased approximately 266,700 ETH, equivalent to $742 million, over two days to replenish its reserves. Zhou confirmed this development, stating that Bybit has fully closed the Ethereum gap caused by the hack.

The cryptocurrency community has been closely monitoring the movement of the stolen funds. Analysts have noted that the hackers face challenges in liquidating the stolen Ethereum due to potential blacklisting by major stablecoin issuers like Circle and Tether. This situation has led to discussions about the possible bullish impact on Ethereum’s price, as the removal of a significant amount of ETH from circulation could affect market dynamics.

This incident has raised concerns about the security of cryptocurrency exchanges and the broader implications for the market. Following the hack, major cryptocurrencies experienced declines. Bitcoin’s price dropped by 0.4% to $95,822, while Ethereum’s price decreased by 4% to $2,698. These downturns are attributed to a combination of the Bybit hack and broader macroeconomic and geopolitical events.

The Bybit heist surpasses previous major cryptocurrency thefts, including the $610 million Poly Network hack in 2021 and the $540 million Ronin Network breach in 2022. These recurring incidents underscore the persistent security challenges within the cryptocurrency industry. In 2024 alone, over $2 billion was lost to hacking, marking the fourth consecutive year of billion-dollar thefts in the sector.

The FBI’s pursuit of Park Jin Hyok and the Lazarus Group highlights the ongoing efforts to combat state-sponsored cybercrimes. The agency has previously linked the group to various cyberattacks, including the $41 million theft from Stake.com in 2023. These actions are part of a broader strategy to hold malicious cyber actors accountable and prevent future incidents.

In an unprecedented security breach, cryptocurrency exchange Bybit has fallen victim to a sophisticated cyberattack, resulting in the theft of approximately $1.5 billion worth of Ethereum . The notorious North Korean hacking collective, Lazarus Group, has been identified as the primary suspect behind this monumental heist. In the wake of the attack, industry leaders, including billionaire investor Mike Novogratz, have voiced strong opposition to proposals for an Ethereum hard fork as a remedial measure, instead calling for coordinated international efforts to combat such cyber threats.

The breach occurred during a routine transfer of funds from Bybit’s cold wallet to its hot wallet, a process intended to enhance security by keeping the majority of assets offline. However, attackers managed to intercept this transfer, redirecting 401,000 ETH—valued at approximately $1.5 billion—to an unknown address. This incident now stands as the largest cryptocurrency theft on record, surpassing previous high-profile hacks in the digital asset sector.

Bybit’s CEO, Ben Zhou, promptly addressed the situation, assuring clients that their assets remain secure despite the breach. Zhou emphasized that the company possesses sufficient reserves to cover the losses, stating that even if the stolen funds are not recovered, Bybit’s solvency remains intact. The exchange has initiated measures to restore its Ethereum reserves, securing 446,870 ETH through strategic acquisitions and loans, thereby ensuring all assets are backed on a one-to-one basis. Additionally, Bybit is collaborating with law enforcement agencies and cybersecurity experts to track and recover the stolen assets, while also offering a 10% bounty for information leading to the successful retrieval of the funds.

In response to the theft, some members of the cryptocurrency community have suggested implementing a hard fork in the Ethereum blockchain to invalidate the stolen funds. A hard fork involves creating a divergent path in the blockchain, effectively reversing specific transactions. This approach was previously employed in 2016 following the DAO hack, leading to the creation of Ethereum Classic. However, such a measure is contentious, as it challenges the principle of blockchain immutability and could undermine trust in the network’s integrity.

Mike Novogratz, CEO of Galaxy Digital and a prominent figure in the crypto industry, has publicly rejected the notion of an Ethereum hard fork as a solution to the Bybit hack. Novogratz argues that altering the blockchain’s history sets a dangerous precedent and could erode confidence in decentralized systems. Instead, he advocates for a unified global response to address the root cause of such attacks. Novogratz emphasizes the necessity for world leaders to take decisive action against state-sponsored hacking groups like Lazarus, which have been implicated in numerous cybercrimes aimed at destabilizing financial systems and funding illicit activities.

The Lazarus Group, linked to the North Korean government, has a notorious history of executing elaborate cyberattacks, particularly targeting financial institutions and cryptocurrency platforms. Their operations are believed to generate significant revenue used to support North Korea’s nuclear weapons program. The group’s involvement in the Bybit hack underscores the escalating threat posed by state-sponsored cybercriminals to the global financial ecosystem.

The Bybit incident has reignited discussions about the security vulnerabilities inherent in centralized cryptocurrency exchanges. While cold wallets are designed to offer enhanced protection by keeping assets offline, the process of transferring funds to hot wallets introduces potential attack vectors. This event highlights the critical need for exchanges to implement robust security protocols and for the industry to develop more resilient infrastructure to safeguard digital assets.

In the aftermath of the hack, Bybit has pledged to bolster its security measures to prevent future breaches. The exchange is conducting a comprehensive review of its internal processes and has engaged third-party cybersecurity firms to audit its systems. Bybit’s swift response aims to restore user confidence and set a precedent for how cryptocurrency platforms should address and manage security incidents.

The broader cryptocurrency market has also felt the impact of the Bybit hack. Following the news, Ethereum’s price experienced a temporary decline, reflecting investor concerns over the security of digital assets. Market analysts suggest that while such incidents can cause short-term volatility, the long-term implications depend on the industry’s ability to enhance security measures and prevent similar occurrences in the future.

BlockDAG, a pioneering Layer 1 blockchain network, is making significant strides in the cryptocurrency landscape by integrating the security and decentralization of Bitcoin with the speed and scalability of Directed Acyclic Graph technology. This innovative approach aims to address the longstanding challenges of scalability and transaction speed that have hindered traditional blockchain platforms.

At the core of BlockDAG’s architecture is its unique consensus mechanism, which diverges from the conventional linear chain of blocks. Instead, it employs a DAG structure, allowing for parallel processing of transactions. This design enables the network to achieve remarkable speeds, reportedly reaching up to 10 blocks per second, with aspirations to surpass 100 blocks per second in the near future. Such capabilities position BlockDAG as a formidable contender in the race to develop scalable and efficient blockchain solutions.

The native cryptocurrency of the BlockDAG network, BDAG, plays a pivotal role in its ecosystem. BDAG serves multiple functions, including covering transaction fees, facilitating peer-to-peer transfers, and providing staking rewards for validators who contribute to network security. The total supply of BDAG is capped at 150 billion coins, with a halving event scheduled every 12 months to control inflation and maintain value. Notably, 50 billion BDAG coins have been allocated for the presale phase, aiming to attract early supporters and enhance the network’s visibility in the competitive crypto market.

Mining BDAG is accessible to a broad audience, thanks to BlockDAG’s suite of mining solutions tailored to various user needs. The X1 Miner app, available on both iOS and Android platforms, has garnered significant attention, attracting over 500,000 users who mine BDAG coins daily. This mobile application allows individuals to mine up to 20 BDAG coins per day without taxing their device’s resources, making crypto mining more approachable for the general public. For more intensive mining operations, BlockDAG offers hardware solutions such as the X10, X30, and X100 miners, catering to small-scale miners and large industrial operations alike.

Security remains a cornerstone of BlockDAG’s design. By utilizing a Proof-of-Work consensus mechanism, the network ensures robust protection against potential threats, including double-spend attacks. The integration of advanced cryptographic algorithms further fortifies the network’s defenses, maintaining the integrity and trustworthiness of transactions. This commitment to security, combined with its scalable architecture, positions BlockDAG as a promising platform for decentralized applications and other blockchain-based services.

A widely used artificial sweetener, aspartame, commonly found in diet beverages, chewing gum, and low-sugar yogurts, may elevate insulin levels, potentially increasing the risk of heart disease, according to a new study. Researchers from the Karolinska Institute in Sweden and Shandong University in China conducted experiments on mice to investigate the metabolic effects of aspartame. The study, published in *Cell Metabolism*, revealed that mice consuming aspartame exhibited […]

By Nantoo Banerjee India, the world’s second most preferred destination of illegal migrants, has a lot to learn from the United States about how the latter has been handling the situation in recent years. Although US President Donald Trump is lately hogging the limelight for forcing illegal immigrants out of the country, such deportations are […]

An explosion occurred early Monday at the Russian Consulate General in Marseille, France, coinciding with the third anniversary of Russia’s invasion of Ukraine. The blast, which Russian authorities have denounced as a “terrorist attack,” has prompted demands for a comprehensive investigation by French officials. The incident took place within the consulate premises in Marseille, a major port city in southern France. Stanislav Oranskiy, the Russian Consul General […]

In a staggering blow to the cryptocurrency industry, Dubai-based exchange Bybit has fallen victim to a cyberattack resulting in the theft of approximately $1.5 billion in Ethereum tokens. This incident, occurring during a routine transfer between digital wallets, is now considered the largest digital heist in history.

The breach transpired as Bybit conducted a standard operation, moving assets from a cold wallet—offline storage designed to safeguard funds—to a warm wallet used for daily transactions. During this process, malicious actors manipulated the transfer, seizing control of the cold wallet and diverting 401,000 Ethereum tokens to an unidentified address. Blockchain analytics firms, including Arkham Intelligence, have traced the stolen funds, revealing that $1.36 billion in Ethereum was swiftly liquidated from associated accounts.

Bybit’s CEO, Ben Zhou, addressed the crisis, assuring clients that the exchange remains solvent and that all customer assets are backed on a one-to-one basis. He emphasized that unaffected wallets and withdrawal processes continue to operate normally. To mitigate the impact on users, Bybit has implemented bridge loans to cover any unrecovered funds and has launched a recovery bounty program, offering up to 10% of the reclaimed amount to ethical hackers assisting in the retrieval efforts.

The magnitude of this theft has prompted a surge in withdrawal requests, with over 350,000 submissions flooding the platform. While this influx has the potential to cause processing delays, Zhou noted that the rate of withdrawals has begun to decelerate. In response to the breach, Bybit is collaborating with law enforcement agencies and cybersecurity experts to trace the perpetrators and enhance its security infrastructure to prevent future incidents.

Speculation regarding the identity of the attackers has intensified, with some experts pointing towards North Korea’s notorious Lazarus Group. This collective has been implicated in previous high-profile cryptocurrency thefts, including the pilfering of $1.7 billion in 2022 and $800 million in 2024. While these allegations remain unconfirmed, the pattern of large-scale crypto heists attributed to state-sponsored actors raises significant concerns about the security of digital assets on global trading platforms.

In a related development, cybersecurity firm CertiK has identified another suspicious transfer involving approximately $49.5 million from an unverified Ethereum contract. The recipient address has been observed converting these funds into the stablecoin DAI. The community speculates that this incident may be connected to the Infini platform, a stablecoin digital bank, though official confirmation is pending.

These consecutive breaches underscore the vulnerabilities inherent in the rapidly evolving cryptocurrency landscape. As digital assets become increasingly mainstream, the imperative for robust security measures and regulatory oversight grows more pressing. The Bybit hack serves as a stark reminder of the potential risks investors face and the necessity for exchanges to implement stringent protective protocols to safeguard user funds.

In the wake of these events, the cryptocurrency market has experienced notable fluctuations. Ethereum’s value witnessed a temporary decline of approximately 4%, reflecting investor apprehension following the breach. Market analysts advise stakeholders to exercise caution and remain informed about security practices employed by exchanges to mitigate exposure to such risks.

Bybit’s commitment to reimbursing affected users and bolstering its security framework aims to restore confidence among its clientele. However, the broader implications of this unprecedented theft continue to reverberate throughout the digital currency ecosystem, prompting a reevaluation of security standards and the adoption of more resilient measures to combat the escalating threat of cyberattacks targeting cryptocurrency platforms.

As investigations proceed, the collaboration between cryptocurrency exchanges, cybersecurity firms, and regulatory bodies will be crucial in addressing the challenges posed by increasingly sophisticated cyber threats. The lessons gleaned from the Bybit incident are poised to inform future strategies aimed at fortifying the security of digital assets and ensuring the integrity of the burgeoning cryptocurrency market.

Dubai-based cryptocurrency exchange Bybit has successfully replenished its Ethereum reserves following a massive security breach that resulted in the theft of approximately $1.5 billion worth of Ether . CEO Ben Zhou announced that the exchange has “fully closed the ETH gap,” ensuring all client assets are backed 1:1.

The unprecedented hack occurred during a routine transfer from Bybit’s cold wallet to a warm wallet. Hackers exploited vulnerabilities in the process, gaining control of the cold wallet and siphoning 401,000 ETH to an unknown address. This incident is considered the largest cryptocurrency theft to date, surpassing previous records.

In response to the breach, Bybit took immediate action to secure its platform and reassure its users. The company collaborated with blockchain forensic experts to trace the stolen funds and launched a recovery bounty program, offering up to 10% of the recovered amount to ethical hackers assisting in the retrieval efforts. Despite the scale of the theft, Zhou emphasized that Bybit remains solvent, with unaffected wallets and withdrawals operating normally.

To address the shortfall caused by the hack, Bybit obtained approximately 446,870 ETH through a combination of loans, large investor deposits, and direct purchases. Notably, the exchange acquired 157,660 ETH from crypto investment firms Galaxy Digital, FalconX, and Wintermute via over-the-counter transactions. An additional $304 million in ETH was purchased through centralized and decentralized exchanges.

Bybit plans to publish a new audited proof-of-reserves report to verify that client assets are fully backed on a 1:1 basis. This move aims to restore user confidence and demonstrate the exchange’s commitment to transparency and security.

The hack has raised concerns within the cryptocurrency community, particularly regarding the potential involvement of North Korea’s Lazarus Group, a state-backed hacking organization known for previous cyberattacks on financial institutions. While blockchain analytics firms Arkham Intelligence and Elliptic have traced the hack to the Lazarus Group, official confirmation is still pending.

Following the incident, Bybit experienced a surge in withdrawal requests, processing over 350,000 transactions as users reacted to the news. The exchange assured customers that all assets are safe and that it has the necessary reserves to cover the losses.

This event highlights the ongoing security challenges faced by cryptocurrency exchanges. In 2024 alone, over $2.2 billion was stolen from crypto platforms, underscoring the need for robust security measures and industry-wide cooperation to combat cyber threats.

Bybit’s swift response and proactive measures to address the breach demonstrate its resilience and commitment to user security. As the exchange continues to enhance its security infrastructure, it remains focused on maintaining trust within the cryptocurrency community.

The broader market impact of the hack has been relatively contained. Ethereum’s price experienced a temporary decline of approximately 4% following the news but has since shown signs of recovery. Analysts attribute this resilience to the prompt actions taken by Bybit and the overall maturity of the cryptocurrency market.

As investigations continue, the incident serves as a stark reminder of the importance of security in the rapidly evolving digital asset landscape. Exchanges and users alike are urged to remain vigilant and adopt best practices to safeguard against potential threats.

Bybit’s efforts to restore its reserves and enhance security protocols are steps toward reinforcing trust and stability in the cryptocurrency ecosystem. The exchange’s commitment to transparency and user protection will be closely monitored by industry stakeholders in the coming months.

In the aftermath of the hack, Bybit has also engaged with international law enforcement agencies to aid in the investigation and potential recovery of the stolen funds. The collaboration aims to bring the perpetrators to justice and deter future attacks on cryptocurrency platforms.

While the incident has undoubtedly posed significant challenges, Bybit’s decisive actions reflect a broader industry trend toward strengthening security measures and fostering a culture of accountability. As the cryptocurrency sector continues to grow, such incidents underscore the critical need for continuous improvement in safeguarding digital assets.

Bybit’s experience serves as a case study for other exchanges, highlighting both the vulnerabilities inherent in digital asset management and the effective strategies that can be employed to mitigate risks and protect user interests.


A massive security breach at cryptocurrency exchange Bybit has resulted in the theft of approximately $1.4 billion in Ethereum , marking one of the largest heists in the digital currency sector to date. The incident has ignited a contentious debate within the Ethereum community regarding the feasibility and ethics of implementing a blockchain rollback to recover the stolen assets.

Bybit disclosed that during a routine transfer between digital wallets, an attacker managed to exploit the process, diverting the substantial sum to an unidentified address. Despite the significant loss, CEO Ben Zhou assured users that the platform remains solvent and that customer funds are secure. However, he cautioned that withdrawal requests might experience delays as the company addresses the breach.

In response to the theft, prominent figures in the cryptocurrency space have proposed drastic measures. Arthur Hayes, co-founder of BitMEX, suggested rolling back the Ethereum blockchain to invalidate the illicit transaction. He referenced the 2016 DAO hack, where a similar rollback was executed, stating, “ETH stopped being a form of money in 2016 after the DAO hack hard fork. If the community is willing to do it again, I would support it.”

Samson Mow, CEO of JAN3, echoed this sentiment, advocating for the creation of a new Ethereum token, “ETHNK,” to prevent the stolen funds from benefiting North Korea, the suspected perpetrator behind the hack. Mow emphasized the potential geopolitical ramifications, suggesting that allowing the hackers to retain the funds could lead to regulatory scrutiny and sanctions against Ethereum.

Despite these calls for intervention, Ethereum’s core developers have dismissed the idea of a rollback. Tim Beiko, a prominent Ethereum developer, described the proposal as “technically intractable,” highlighting the complexities and potential unintended consequences of such an action. He explained that the interconnected nature of Ethereum’s blockchain, coupled with the myriad on-chain and off-chain transactions, makes reversing the chain a formidable challenge.

The broader Ethereum community has also expressed resistance to the rollback idea. Many argue that altering the blockchain undermines the principles of immutability and decentralization that are foundational to Ethereum and other cryptocurrencies. Critics contend that setting a precedent for reversing transactions could erode trust in the network and open the door to future manipulations.

In the aftermath of the hack, Bybit has initiated several measures to address the situation. The exchange is collaborating with law enforcement agencies and blockchain analytics firms to trace the stolen funds. Additionally, Bybit has announced a bounty program, offering rewards to individuals who provide information leading to the recovery of the assets.

The incident has also had immediate repercussions on the cryptocurrency market. Ethereum’s price experienced a decline of approximately 7% following the news of the hack, reflecting investor concerns over security vulnerabilities within the ecosystem. Market analysts suggest that such events could prompt tighter regulatory scrutiny and potentially influence future policy decisions regarding digital assets.

This event serves as a stark reminder of the persistent security challenges facing the cryptocurrency industry. As exchanges and platforms continue to evolve, the balance between maintaining decentralization and implementing protective measures remains a critical and ongoing debate.

VISHNU RAJA
RYO YAMADA
HITORI GOTOH
IKUYO KITA