News related to
threats

WordPress.org has taken the significant step of denying service to WP Engine, a major managed WordPress hosting provider. This decision raises alarms regarding the security and operational stability of websites reliant on WP Engine’s services, as they could face challenges in maintaining performance and security without direct support from the WordPress.org team. The conflict stems from unresolved issues regarding the way WP Engine handles updates and plugins […]

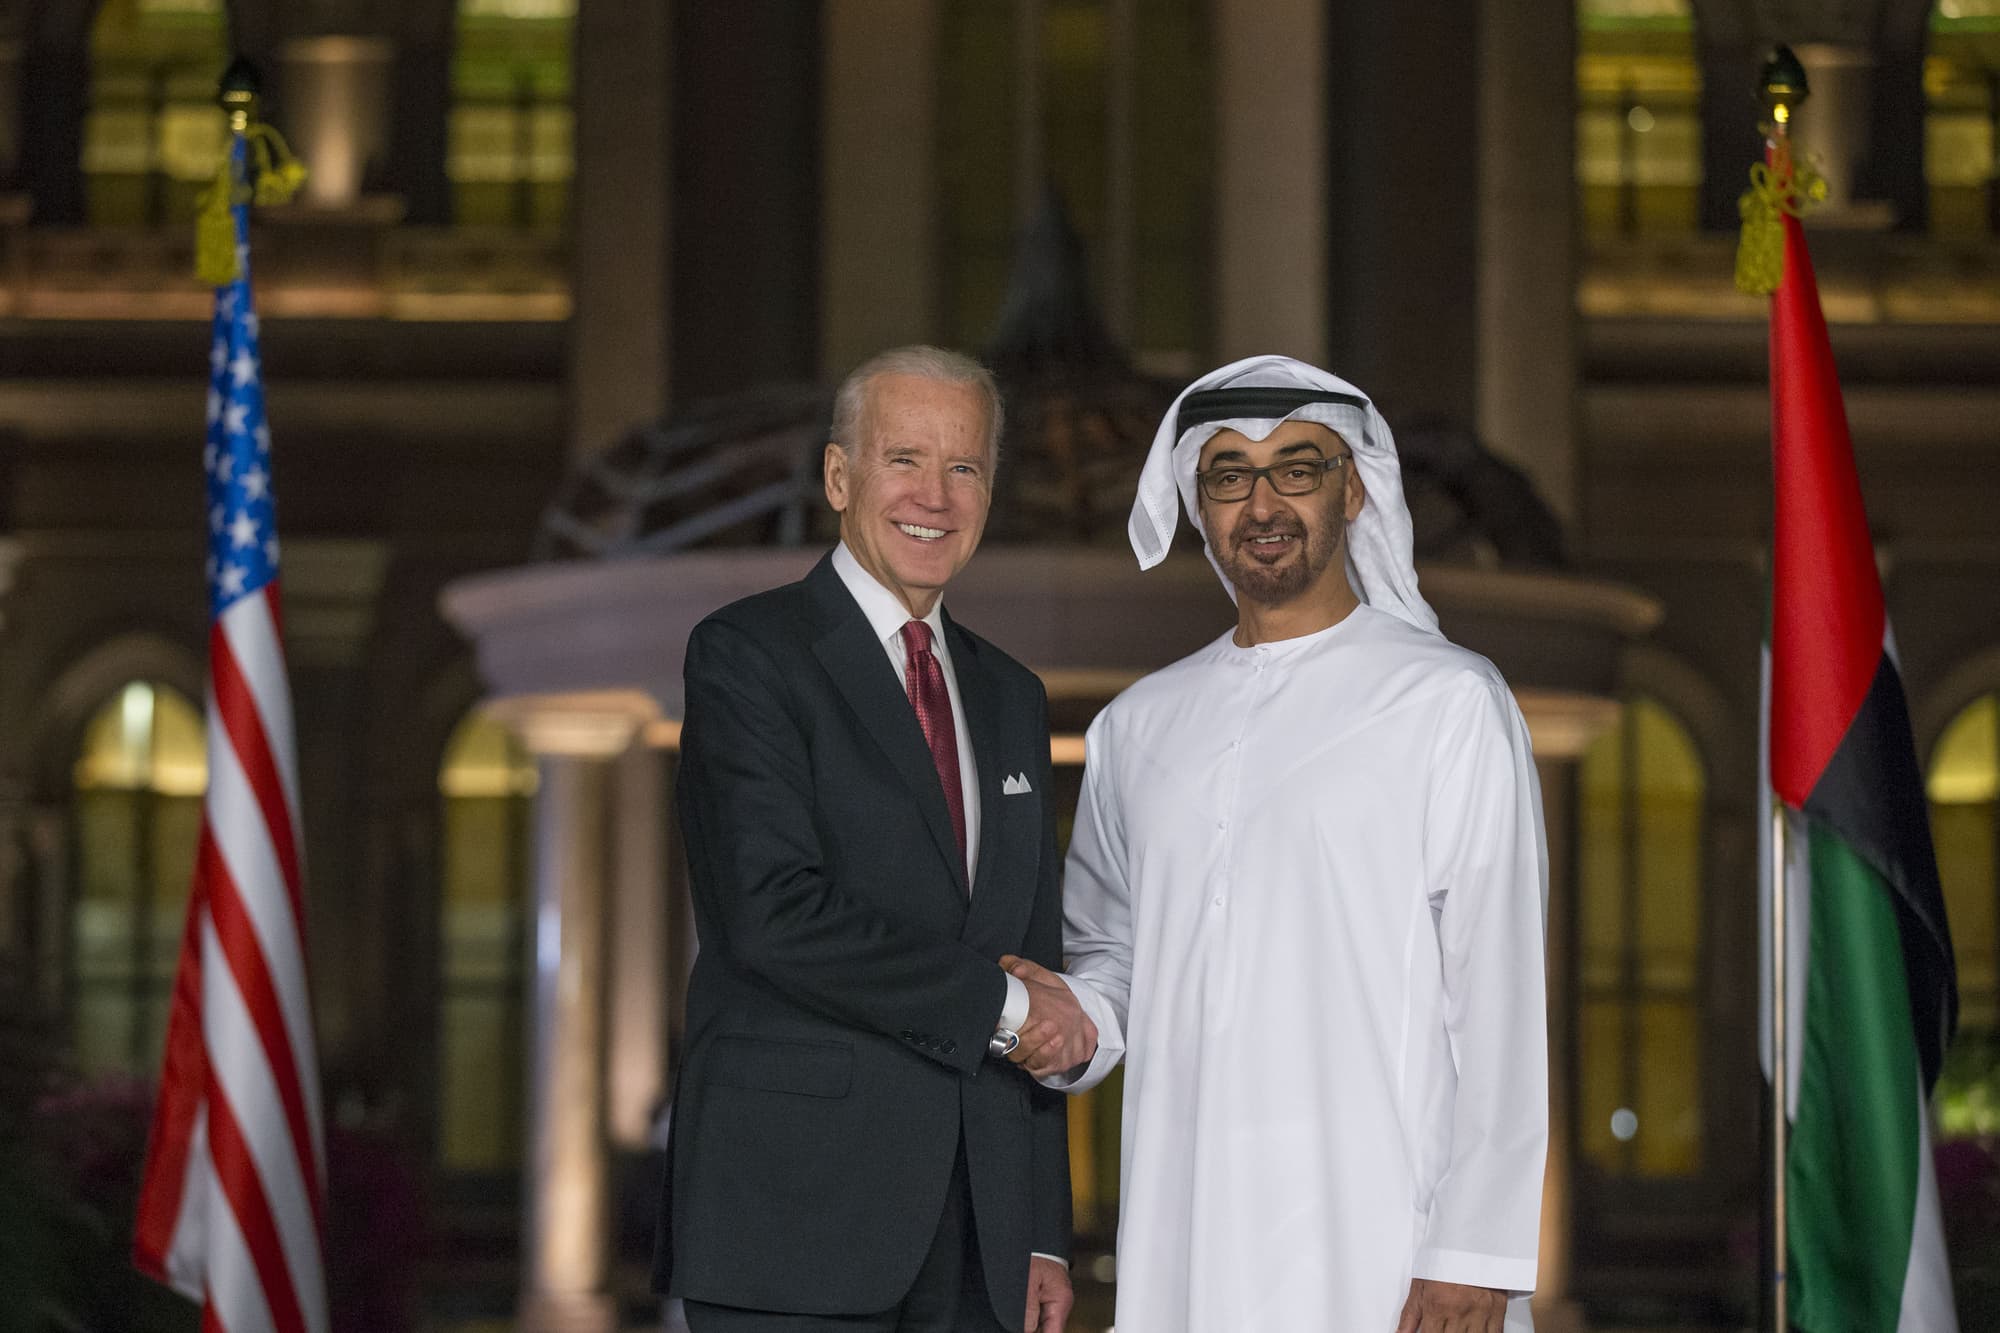
President Joe Biden has officially designated the United Arab Emirates as a major defense partner of the United States, solidifying the nation’s strategic role in the region. This move comes shortly after a similar designation was awarded to India, underscoring Washington’s efforts to build stronger alliances with Gulf and South Asian powers in the face of shifting global security dynamics. The announcement marks a significant step in US-UAE relations, enhancing defense cooperation and reaffirming the UAE’s importance in American military strategy.

The decision highlights the UAE’s evolving role as a critical player in regional security. With this designation, the UAE joins a select group of countries that enjoy preferential treatment when it comes to military cooperation with the United States. The relationship allows for greater access to advanced defense technology, streamlined military sales processes, and deeper intelligence collaboration. These developments come amid ongoing efforts by the US to recalibrate its security commitments in the Middle East, pivoting towards nations capable of contributing more significantly to their own defense.

Biden’s formal recognition of the UAE as a defense partner builds on decades of close military ties between the two nations. The UAE has long been a hub for US military operations in the region, hosting troops and serving as a staging ground for operations in neighboring conflict zones. The move is also seen as part of Washington’s broader strategy to reinforce its influence in the Gulf, where rising geopolitical tensions and the involvement of foreign powers like Russia and China continue to shape the security landscape.

For the UAE, this designation is not merely symbolic. It solidifies the nation’s status as a regional security leader and elevates its position on the global stage. It also provides the UAE with more direct access to sophisticated US defense systems, which will be critical in enhancing its defense capabilities amidst growing concerns over missile threats and other regional challenges. The UAE has long sought to upgrade its military arsenal, focusing on cutting-edge technology such as advanced fighter jets and missile defense systems. This new designation could accelerate these procurements, allowing for a faster, more seamless process.

The US government has been increasingly focused on forging deeper security ties with countries it sees as vital to countering both state and non-state actors. The UAE has been a crucial partner in US-led efforts to combat terrorism and ensure maritime security in the Gulf, particularly through its involvement in anti-piracy and anti-smuggling operations. The nation’s strategic location and military infrastructure have made it an indispensable ally in addressing threats posed by extremist groups and hostile states in the region.

Meanwhile, this development coincides with broader geopolitical shifts, as the US grapples with its role in a multipolar world. The Biden administration’s defense policy has focused on reducing its military footprint in some traditional hotspots while doubling down on partnerships that bolster regional security autonomously. The designation of both the UAE and India as major defense partners reflects a recalibrated approach to ensuring stability through cooperation, rather than direct military involvement.

The strategic importance of the UAE extends beyond the Middle East. Its influence in Africa, Central Asia, and the Indian Ocean region makes it a key player in a wider arc of geopolitical interests. With major global powers vying for influence in the Middle East, Washington’s decision to deepen its defense ties with Abu Dhabi also signals its intention to counter growing Russian and Chinese influence. China’s Belt and Road Initiative and increasing arms sales to Gulf countries, including the UAE, are clear indicators that the region is a key battleground for global influence.

The UAE’s defense relationship with the United States has grown in complexity in recent years. The two nations have regularly conducted joint military exercises, and the UAE has made substantial purchases of US-made defense equipment, including F-16 fighter jets, missile defense systems, and advanced drones. More recently, the UAE has expressed interest in acquiring next-generation US fighter jets, including the F-35, as part of its efforts to enhance its military edge. The partnership also extends to counterterrorism operations, where the two nations collaborate closely in intelligence sharing and tactical support to neutralize extremist threats.

The decision to elevate the UAE’s status comes against the backdrop of broader regional realignments. The Abraham Accords, which normalized diplomatic relations between the UAE and Israel, have reshaped the strategic landscape of the Middle East, offering new opportunities for cooperation between key US allies. This trilateral relationship between the US, UAE, and Israel is likely to deepen in the defense sphere, with potential collaborations in areas like missile defense and cybersecurity.

At the same time, the UAE faces growing security concerns closer to home. The conflict in Yemen, where the UAE has been heavily involved, continues to pose risks to regional stability. Iranian-backed Houthi rebels have launched missile and drone attacks against UAE infrastructure, raising the stakes for Abu Dhabi’s defense posture. The new designation from Washington could pave the way for more robust US support in addressing such threats, with the potential for more advanced defense systems aimed at countering missile and drone attacks.

US defense experts have praised the move, calling it a logical step in strengthening bilateral ties with a trusted partner in the Gulf. They argue that bolstering the UAE’s defense capabilities is not only in the interest of regional stability but also aligns with the US strategy of building self-reliant regional security partners. The UAE’s growing military spending and its focus on modernizing its armed forces further bolster the case for Washington’s decision.

Vercel, a prominent player in the web development ecosystem, positions itself as a pivotal solution for developers seeking speed and efficiency. Known for its Frontend as a Service (FaaS) model, Vercel enables developers to build, deploy, and optimize applications seamlessly, catering to the growing demands of modern web users. The platform has gained traction for its ability to deliver high-performance websites with minimal latency, a critical factor […]

The crypto market presents a myriad of investment opportunities, particularly for those looking to acquire affordable assets with potential for growth. Amidst a backdrop of fluctuating market conditions, investors are increasingly focusing on lower-priced cryptocurrencies that exhibit strong fundamentals and promising market activity. Several key players have emerged as noteworthy options for investors this month. Among them is Cardano (ADA), which has garnered attention for its innovative […]

Huawei has unveiled significant advancements in its fiber to the office (FTTO) technology, launching FTTO 2.0 and a suite of new products tailored for various industries, including education, healthcare, and hospitality. These innovations were announced at HUAWEI CONNECT 2024, with a strong emphasis on enhancing campus networks and transitioning to Wi-Fi 7 standards. The FTTO 2.0 system integrates cutting-edge optical networking technology to support the evolving demands […]

President Joe Biden convened with key Indo-Pacific leaders on Saturday, reaffirming the United States’ commitment to bolstering regional maritime cooperation and countering the growing strategic influence of China. During the summit with the leaders of India, Australia, and Japan, Biden underscored the importance of the Quadrilateral Security Dialogue (Quad), a security coalition increasingly focused on ensuring the stability of the Indo-Pacific region, both economically and militarily. Biden’s […]

The rising tensions in the Red Sea, particularly due to Houthi rebel threats against shipping vessels, have led to a sharp increase in insurance premiums for maritime companies operating in the region. The volatile security environment, combined with the risk of targeted attacks on vessels linked to countries like the UK, US, or those having called at Israeli ports, has left insurers increasingly cautious about providing war-risk cover for ships transiting the waters.

War-risk insurance premiums have skyrocketed to as much as 2% of a vessel’s value for a single transit through the Red Sea. This steep increase reflects heightened concerns following several incidents, most notably the August 21 strike on the oil tanker Sounion, which was carrying about one million barrels of crude oil at the time. Though the tanker was safely towed without spillage, the attack underscored the vulnerability of maritime assets in the region, adding pressure on insurers and shipping companies alike.

The market for insuring ships passing through this critical shipping route has narrowed as smaller insurers retreat from offering coverage. A limited number of firms, mostly high-risk underwriters, continue to offer protection, but at significantly elevated costs. Industry insiders have noted that some vessels, especially those perceived as high-value targets for potential attacks, are struggling to secure any coverage at all.

The risks have intensified with the Houthis’ declaration that ships with certain affiliations would face potential attacks. While traditionally, war-risk cover has been available, the situation is unprecedented with underwriters outright refusing coverage, citing the region’s escalating risks. For shipping operators, this poses not only financial but also operational challenges, as the necessity of traversing the Red Sea for global oil and goods trade remains critical despite the threats.

A consortium of insurance underwriters led by Brit provided the war-risk cover for the Sounion, alongside firms such as Antares, Iquw, Hamilton, and others. However, many of these insurers have been notably silent regarding the details of coverage, which underscores the sensitivity and complexities of offering insurance in such a volatile region. The consortium’s willingness to continue offering protection contrasts with smaller players who are increasingly unwilling to take on such risks.

The situation has compounded concerns for global shipping companies, especially with the strategic importance of the Red Sea in connecting Europe, the Middle East, and Asia. As attacks threaten to disrupt not just oil shipments but broader trade routes, the rising insurance costs may further exacerbate existing challenges for global supply chains.

Maritime experts are urging caution as geopolitical tensions in the region show little sign of abating, with insurers increasingly exercising selective underwriting processes to minimize exposure. Ships perceived as having higher exposure to attacks are now finding it exceedingly difficult to secure coverage at any price. This selective process not only reflects the complexities of the situation but also highlights the unpredictable nature of risk in conflict-prone areas like the Red Sea.

As shipping companies scramble to mitigate these rising costs, the long-term impact on global trade remains a looming concern. Many in the industry are questioning how long they can sustain operations under such financial pressure and whether alternative routes or additional security measures might provide a viable solution in the coming months.

Advertisements

Aruba has expanded its collaboration with NetApp, a leader in data infrastructure solutions, to bolster its capabilities in the rapidly growing digital services sector. The Italian web hosting firm, known for its extensive range of cloud services, domain registration, and email hosting solutions across Europe, is leaning heavily on NetApp’s technology to enhance its data center operations and improve the efficiency of its services. This partnership marks […]

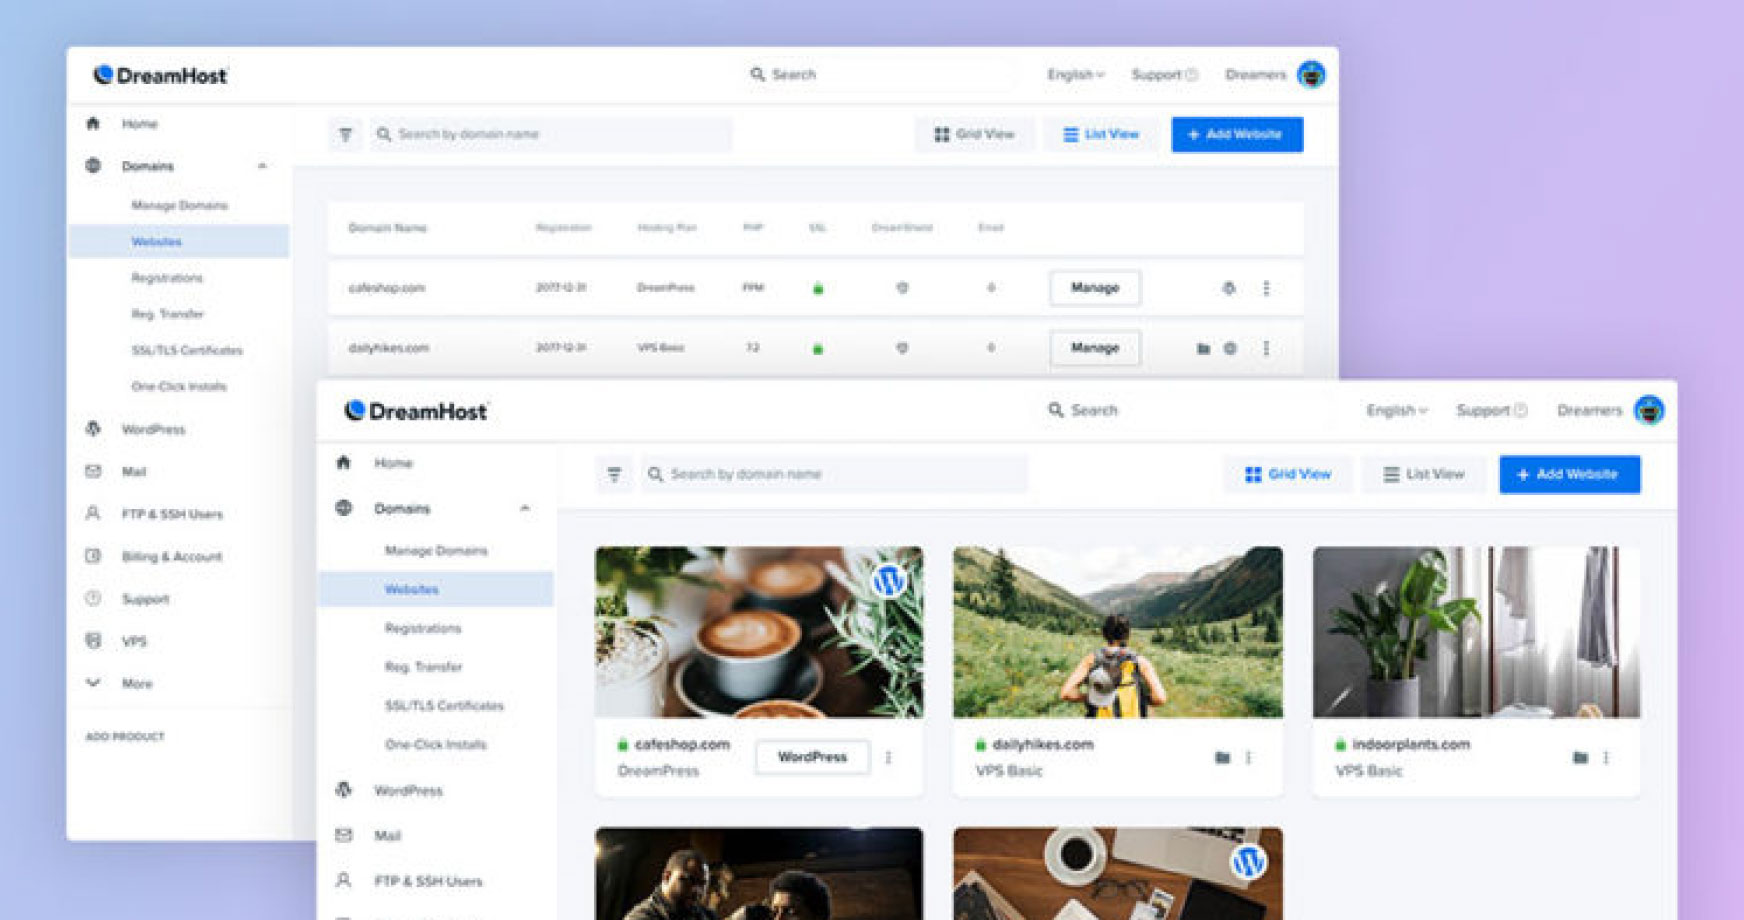
DreamHost has launched DreamHost Liftoff, an innovative AI-powered website builder designed to simplify the process of creating WordPress sites. This tool aims to empower users of all skill levels to effortlessly design professional-looking websites in a matter of minutes, responding to the growing demand for user-friendly web solutions.

Liftoff leverages artificial intelligence to guide users through the website creation process. The platform features a conversational interface that helps users select templates, customize designs, and incorporate content with ease. This approach minimizes the need for extensive technical knowledge, making website creation accessible to entrepreneurs, small business owners, and individuals seeking an online presence.

The launch of Liftoff aligns with a broader trend in the tech industry, where companies are increasingly integrating AI into their services to enhance user experience. As competition intensifies in the web hosting market, DreamHost’s introduction of this tool positions it strategically against rivals such as Wix and Squarespace, which have also embraced AI to streamline website building.

Liftoff not only simplifies design but also optimizes websites for performance and search engine visibility. By automatically generating SEO-friendly content and providing suggestions for improving site speed and accessibility, the tool ensures that users can create websites that meet industry standards without needing advanced expertise.

The AI-driven approach is particularly relevant in today’s digital landscape, where businesses are recognizing the importance of a strong online presence. According to a recent survey, nearly 70% of small businesses reported that having a website is crucial for their growth. DreamHost’s Liftoff aims to address this need by providing a solution that combines efficiency with functionality.

Moreover, the demand for website builders that cater to diverse user needs has grown significantly. The COVID-19 pandemic accelerated the digital transformation, prompting many individuals and organizations to establish or enhance their online platforms. Liftoff’s design caters not only to beginners but also to users who may have experience but are looking for a faster and more efficient way to build and manage their sites.

DreamHost has emphasized the importance of security and performance in Liftoff. The tool incorporates advanced security features, including automated updates and SSL certificates, which protect websites from potential threats. This focus on security is essential, as cyber threats continue to evolve, and website owners must remain vigilant to safeguard their online assets.

User feedback has played a crucial role in the development of Liftoff. DreamHost conducted extensive testing and gathered insights from potential users to refine the tool’s features. This iterative process ensured that the final product not only meets but exceeds user expectations. Testimonials from early adopters highlight the tool’s intuitive design and the ease with which they were able to create functional websites.

The introduction of DreamHost Liftoff also reflects the company’s commitment to innovation and customer satisfaction. As a leading provider of managed WordPress hosting, DreamHost aims to equip users with the tools necessary to thrive in a digital-first world. By harnessing AI technology, the company is poised to redefine how individuals and businesses approach website creation.

Market analysts anticipate that AI-driven website builders will continue to gain traction as more users seek quick and efficient solutions for establishing their online presence. DreamHost’s strategic move into this space signals its intent to be at the forefront of this evolving trend, catering to the needs of both novice and experienced web builders.

As users increasingly prioritize convenience and speed in website creation, DreamHost Liftoff positions itself as a compelling option. The combination of AI technology, user-friendly features, and a commitment to security establishes Liftoff as a valuable asset for those looking to create a professional online presence.

In a landscape where digital presence is more critical than ever, DreamHost’s Liftoff emerges as a timely solution for users seeking to navigate the complexities of website creation. The tool’s capabilities reflect an understanding of the current market demands and the future direction of web development.

Ethena Labs, the issuer of the USDe stablecoin, has confirmed a security breach involving its website domain. Although the underlying USDe protocol remains intact, the company has issued a warning advising users to avoid interacting with its front-end interface until further notice. The attack on Ethena Labs’ website came to light after users reported unusual activity. According to the company’s statement, the breach affected only the website’s […]

Cybersecurity research reveals a staggering 70% increase in Distributed Denial of Service (DDoS) attacks across Gulf countries since the beginning of the year. The escalation highlights a troubling trend, with the UAE and Saudi Arabia being the primary targets. The UAE faces 40% of the region’s total DDoS incidents, while Saudi Arabia encounters 26%, indicating a concentrated focus of cybercriminal activities on the region’s most significant economies. […]

A landmark study has revealed the presence of microplastics in human brains, marking a significant breakthrough in environmental and health research. This finding emerged from an examination of 15 adult cadavers in Brazil, where eight were found to contain microplastic particles in their brain tissue. The study, published in JAMA Network Open, represents the first documented evidence of such contamination in human neurological tissue.

The research team, comprising scientists from Germany and Brazil, including the University of São Paulo, meticulously identified and characterized microplastics in brain samples. These particles, known to originate from various everyday plastic products, are believed to enter the brain through inhalation of airborne microplastics. This novel discovery underscores the urgent need to understand the broader health implications of such pollution.

Toxicologists have expressed growing concern over the potential health risks associated with microplastics. Dr. Wells Brambl, a specialist in medical toxicology, pointed out the emerging threats posed by microplastic pollution, emphasizing the need for increased vigilance. While the study did not establish a direct link between microplastics in the brain and specific health conditions, the potential for adverse effects warrants further investigation.

The International Agency for Research on Cancer (IARC) has already classified microplastics as a possible carcinogen, which adds to the urgency of addressing this issue. Dr. Robert Schwaner, an expert in environmental health, has called for heightened attention to the prevalence of microplastics and their potential health consequences. He advocates for more comprehensive research to better understand the risks and to develop strategies to mitigate exposure.

The discovery of microplastics in the brain highlights the pervasive nature of plastic pollution. Microplastics are not only found in environmental settings but have also infiltrated human tissues, raising concerns about their long-term impact on health. The potential pathways for microplastic entry into the body include ingestion of contaminated food and water, as well as inhalation of airborne particles.

The study’s findings have prompted calls for urgent action to address plastic pollution. Despite the widespread use of plastics in food containers, bottle caps, and clothing, there is a growing movement towards adopting alternative materials. Aluminum, for instance, is emerging as a viable substitute in various applications to reduce reliance on plastics.

Sparkle, Italy’s premier international telecommunications provider, has joined forces with Nexim Global, an Italo-American telecom firm, to enhance global internet connectivity and cybersecurity services. This partnership, announced during the IBC2024 conference, aims to offer a comprehensive suite of internet protocol (IP) services and distributed denial-of-service (DDoS) protection to clients worldwide. The collaboration between Sparkle and Nexim Global is set to significantly impact the telecommunications landscape, integrating Sparkle’s […]

A man charged in connection with an alleged assassination attempt on former President Donald Trump was in close proximity to his golf course for 12 hours before his arrest, according to authorities. This extended period of surveillance has raised questions about security and the effectiveness of protective measures at high-profile events.

The suspect, identified as an individual with a known history of erratic behavior, was first observed around the golf course perimeter early Sunday morning. Reports indicate that he was initially unnoticed as he made his way onto the grounds, evading detection by security personnel. It wasn’t until later in the day, following a tip-off from a vigilant observer, that law enforcement intervened and took him into custody.

Authorities have revealed that the suspect was found carrying multiple weapons and materials believed to be intended for a more extensive attack. His prolonged presence near the venue, coupled with the type of equipment discovered, has intensified concerns about how such a breach could occur despite stringent security protocols.

Security agencies are currently reviewing their procedures and the effectiveness of their coordination with event organizers. Investigators are also scrutinizing whether there were any lapses in communication or misjudgments that allowed the suspect to remain undetected for so long. This review is part of a broader effort to enhance security measures for future events involving high-profile figures.

The incident has prompted a wider discussion on the need for improved security at public and private events where high-profile individuals are present. Experts argue that the existing security frameworks may need to be reassessed to prevent similar occurrences in the future. They emphasize the importance of integrating advanced surveillance technologies and better coordination between various security agencies to address potential threats more effectively.

This event follows a series of high-profile security incidents that have underscored the challenges faced by law enforcement in protecting prominent figures. The incident at the golf course, however, stands out due to the unusually long duration the suspect was able to remain in close proximity without detection. It highlights potential vulnerabilities that could be exploited by individuals with malicious intent.

The suspect is expected to face multiple charges, including attempted assassination and possession of illegal weapons. Legal experts anticipate that the case will involve a thorough examination of the suspect’s motives and any potential connections to broader extremist networks. The legal proceedings are likely to shed more light on the details of the suspect’s plans and any possible accomplices.

Meanwhile, the golf course and surrounding areas have been cleared and secured as the investigation continues. Local authorities have assured the public that measures are being taken to prevent such incidents in the future. They have also expressed a commitment to addressing any security gaps that may have contributed to the breach.

NL-ix and Nokia have launched a significant upgrade to their network security, introducing Nokia’s Deepfield Defender to combat distributed denial-of-service (DDoS) attacks. This deployment, one of the largest of its kind in Europe, aims to bolster the resilience of NL-ix’s internet exchange infrastructure. The collaboration focuses on deploying Nokia’s advanced Deepfield Defender, a system designed to identify and neutralize DDoS threats in real-time. The solution enhances NL-ix’s […]

A new feature introduced for Chromebook devices, known as ‘Sanitize’, is drawing attention for its promise to enhance security and privacy. The ‘Sanitize’ tool offers an additional layer of protection aimed at maintaining data integrity, a growing concern in the age of cyber threats. With Chromebooks already widely recognized for their secure infrastructure, this latest enhancement seems to underscore Google’s commitment to fortifying its devices against digital […]

Operant AI, a key player in the field of runtime AI application protection, has successfully secured $10 million in Series A funding. The investment round was co-led by SineWave Ventures and Felicis, with additional contributions from Alumni Ventures, Massive, Calm Ventures, and Gaingels. This latest funding will bolster Operant AI’s mission to enhance security measures for cloud APIs and applications, addressing an increasing demand for robust cybersecurity solutions.

Founded in 2020, Operant AI focuses on safeguarding cloud environments through its innovative approach to application protection. The company’s technology integrates machine learning algorithms to monitor and secure API interactions in real time, offering advanced defenses against emerging threats. This Series A funding will enable the company to expand its team, enhance its product offerings, and accelerate go-to-market efforts.

The need for sophisticated cloud security solutions has never been more pressing. As organizations increasingly rely on cloud-based infrastructure, the attack surface for potential cyber threats expands. Operant AI’s technology addresses this challenge by providing a proactive defense mechanism that anticipates and neutralizes threats before they can cause harm. This proactive approach is crucial as traditional security measures often lag behind the rapidly evolving threat landscape.

SineWave Ventures and Felicis, both renowned for their strategic investments in cybersecurity, bring extensive experience and resources to Operant AI’s growth. SineWave Ventures is known for its focus on investing in high-potential, early-stage companies, while Felicis has a track record of nurturing innovative startups in the tech sector. Their co-leadership in this funding round reflects confidence in Operant AI’s potential to make significant strides in cloud security.

Alumni Ventures, Massive, Calm Ventures, and Gaingels, each bringing unique expertise and networks, further strengthen Operant AI’s investment base. Alumni Ventures, with its deep connections within the academic and entrepreneurial communities, will support Operant AI’s recruitment and research efforts. Massive, known for its investments in scalable tech solutions, aligns well with Operant AI’s growth strategy. Calm Ventures, with its focus on emerging technologies, will help drive innovation, while Gaingels offers valuable connections and support for diversity and inclusion in tech.

The cybersecurity landscape is evolving rapidly, with cloud environments becoming increasingly complex and targeted by sophisticated attacks. Operant AI’s solution stands out by leveraging AI to provide dynamic, real-time protection. This method contrasts with traditional static security measures that may not adequately address the fast-paced nature of modern cyber threats.

One of the notable aspects of Operant AI’s technology is its ability to adapt to new threat vectors. By continuously learning from ongoing data and threat patterns, Operant AI’s system evolves to address new security challenges, offering a level of adaptability that is crucial in today’s cyber threat environment.

This funding round positions Operant AI to capitalize on a growing market for cloud security solutions. The global cybersecurity market is projected to continue its robust growth, driven by increasing cyber threats and the expanding use of cloud services. Operant AI’s innovative approach aligns well with these trends, positioning it as a significant player in the cybersecurity space.

As Operant AI moves forward, it will focus on expanding its product capabilities and market reach. The additional funding will support initiatives to enhance its technology stack, develop new features, and scale its operations to meet the demands of a growing customer base. With a solid foundation of investment and expertise, Operant AI is poised to advance its mission of providing cutting-edge protection for cloud-based applications and APIs.

A pioneering quantum-secure data center network has been launched in the UK, marking a significant leap in data security and connectivity. The collaboration between BT Group, Equinix, and Toshiba is set to transform the landscape of data protection and access across key locations in London.

This groundbreaking network involves the deployment of quantum-secure technologies at two prominent Equinix colocation data centers located in Slough and Canary Wharf. The initiative introduces a new era of data security by leveraging quantum encryption to safeguard communications against potential future threats from quantum computing.

BT Group, a leader in global telecommunications, is providing the advanced quantum-secured metro network, which will enable clients to access secure data connections. This network will be integrated with Equinix’s data centers, known for their robust infrastructure and high connectivity standards, ensuring enhanced security and efficiency.

Toshiba’s role in this partnership involves supplying quantum encryption technology that underpins the security framework of the network. Toshiba’s quantum key distribution (QKD) technology is crucial for protecting data transmitted over BT’s network, offering an unprecedented level of encryption that is theoretically immune to future advancements in quantum computing.

The integration of quantum security measures is a proactive step towards addressing potential vulnerabilities that could arise with the advent of quantum computers capable of breaking traditional encryption methods. This development is particularly timely, as the UK and other nations are investing heavily in quantum technologies to stay ahead of cyber threats.

The quantum-secure network will offer a variety of services, including secure data storage, transmission, and connectivity options for businesses across different sectors. This initiative is expected to attract a diverse range of clients, from financial institutions seeking to protect sensitive transactions to government agencies requiring enhanced security for classified information.

Equinix’s data centers in Slough and Canary Wharf are strategically chosen due to their central locations and state-of-the-art facilities, which provide an ideal environment for deploying advanced security technologies. The choice of these locations also ensures that the network can efficiently serve a broad spectrum of clients in the London metropolitan area.

BT Group’s investment in quantum security reflects its commitment to leading the way in advanced telecommunications and data protection. By partnering with Equinix and Toshiba, BT is positioning itself at the forefront of the industry’s efforts to develop secure communication infrastructures capable of withstanding emerging cyber threats.

Toshiba’s contribution extends beyond technology supply; the company is also involved in the ongoing development and refinement of quantum security solutions. This collaboration underscores the critical role that technology providers play in enhancing the security and resilience of data networks against future threats.

The deployment of this quantum-secure network represents a significant milestone in the evolution of data security, with the potential to set new standards for protection and privacy in the digital age. As businesses and institutions increasingly recognize the importance of safeguarding their data, innovations such as this are expected to become integral to global data infrastructure.

In an increasingly digital world, online security and privacy have become paramount, especially in regions like the Middle East, where business, politics, and technology are booming. As more individuals and companies in the UAE and surrounding countries embrace digital tools, the demand for secure internet access has risen sharply. One solution that has gained popularity is the use of a free VPN (Virtual Private Network), offering users […]

Microsoft’s ambitious leap into the world of generative AI with its Copilot tool has garnered widespread attention. Positioned as an AI-powered assistant integrated into nearly all Microsoft 365 services, Copilot promises to revolutionize the way businesses operate. The company is marketing Copilot as a game-changer, boosting productivity and potentially transforming enterprise workflows. Its integration into Microsoft’s suite of products suggests a long-term commitment to AI-powered solutions. However, as Copilot’s adoption accelerates, security concerns are casting a shadow over its potential. Industry analysts and cybersecurity experts are sounding the alarm about the security vulnerabilities this generative AI assistant may introduce, especially when utilized alongside Microsoft 365.

For Microsoft, Copilot has already proven to be a substantial revenue driver. Reports of a 60% surge in sales within a single quarter show that enterprises are interested in leveraging its capabilities. The tool’s rapid expansion into organizations of all sizes highlights the growing demand for AI-driven solutions in enhancing productivity. According to Microsoft’s CEO, the growth of Copilot for Microsoft 365 has outpaced all other software launches for the office suite, an indication that businesses are embracing the potential efficiency gains. This uptake is not surprising, given the promise of Copilot to automate tasks, simplify workflows, and assist employees with complex processes.

Despite these impressive sales figures, the challenges ahead may undermine Copilot’s continued growth. Experts have flagged several security vulnerabilities that could derail its adoption, particularly for enterprise users handling sensitive data. The integration of AI into essential productivity tools opens up a host of security questions, and researchers are urging caution as organizations explore the use of Copilot in their operations. While the technology has significant upside, its security risks must be addressed to ensure long-term success.

One of the primary concerns surrounding Copilot is the nature of its access to corporate data. Given that Copilot functions as an AI assistant, it requires extensive access to company files, emails, documents, and other sensitive information stored within Microsoft 365. The scope of this access is where the security risks begin. By design, the AI needs to draw upon vast amounts of data to provide relevant and contextually appropriate assistance to users. However, this same feature could potentially open up new vulnerabilities.

The potential for misuse of this access is a major worry. Hackers, insiders, or even external parties could exploit security gaps, gaining unauthorized access to confidential information. The AI’s deep integration with core systems provides an appealing target for bad actors. This is compounded by the fact that AI systems like Copilot can be difficult to monitor. Their operation often involves learning and making decisions based on the data they interact with, making it challenging for organizations to fully control or predict their actions.

While Microsoft has stressed that Copilot’s design includes stringent security measures, including encryption and advanced threat detection, some experts remain skeptical. Security protocols that might be effective for conventional software may not fully protect systems that rely on generative AI. The sheer volume of data that Copilot processes raises additional concerns about how well security measures can keep pace. Analysts from cybersecurity firms are warning that traditional security strategies may need to evolve to address these unique risks.

There’s also concern about the risks posed by inadvertent misuse within companies. Employees using Copilot could unintentionally expose sensitive data or trigger breaches without realizing it. The AI’s ability to pull from a wide array of corporate resources means it could retrieve or expose information that should remain confidential, even if done unintentionally. Ensuring that Copilot’s access is limited appropriately and that users understand the security implications of their interactions with the AI is essential. Organizations must invest in rigorous training and develop protocols to prevent accidental data leaks or breaches.

Another layer of concern relates to how Copilot integrates with existing Microsoft 365 features. Many organizations have already invested heavily in Microsoft’s cloud services, and Copilot’s introduction adds another complex layer to their systems. This interconnectedness, while beneficial for workflow automation, creates a situation where vulnerabilities in one part of the system could compromise the entire infrastructure. If Copilot becomes an entry point for cyberattacks, the potential damage could extend across the entirety of an organization’s Microsoft ecosystem.

Gartner has added to the chorus of concerns, with warnings about the potential security challenges that enterprises could face when using Copilot in conjunction with Microsoft 365. Their assessment has caught the attention of IT professionals, some of whom are hesitant to fully embrace the technology. Despite Microsoft’s assurances that Copilot is secure, there’s a growing belief that the risk environment for AI-powered productivity tools is still evolving. Enterprises that operate in sectors requiring strict data protection standards, such as finance or healthcare, may find it particularly difficult to justify adopting Copilot without robust security guarantees.

Additionally, the complexity of generative AI introduces concerns about transparency. AI systems, by their nature, can be opaque. Their decision-making processes are often not fully understood, even by the engineers who design them. This creates a dilemma for organizations that need to ensure compliance with regulations and internal security policies. If Copilot makes a decision or provides an output that leads to a security issue, it may be difficult to trace the root cause or assign responsibility. This lack of transparency could make some organizations wary of trusting their most sensitive information to a generative AI system.

There are also issues of compliance and regulatory challenges. For companies that operate in highly regulated industries, the introduction of AI assistants like Copilot may require new compliance strategies. Questions surrounding data privacy, user consent, and cross-border data transfers could complicate the use of AI tools, particularly in regions with stringent privacy laws such as the European Union’s General Data Protection Regulation (GDPR). Companies will need to ensure that Copilot’s operation aligns with these legal frameworks to avoid regulatory pitfalls.

Microsoft, for its part, appears to be aware of these concerns and is likely working to address them. The company has a track record of adapting its security practices in response to emerging threats, and it’s reasonable to assume that they will continue to improve Copilot’s security as new risks emerge. However, until these improvements are fully realized, the apprehension surrounding Copilot’s security is unlikely to dissipate entirely.

Despite these warnings, it’s also possible that fears of Copilot’s security vulnerabilities are overstated. Microsoft has long been a dominant player in enterprise software, and its reputation for securing its platforms is strong. The company is no stranger to navigating security concerns, and its investment in AI safety and security research could lead to breakthroughs that mitigate the risks associated with Copilot. Furthermore, early adopters of Copilot may find that the productivity gains outweigh the security risks, particularly if their operations don’t involve handling highly sensitive data.

Yet, the caution expressed by cybersecurity experts and analysts cannot be ignored. The introduction of AI-powered tools like Copilot represents a significant shift in how businesses manage their data and productivity. The allure of AI-enhanced workflows is undeniable, but the accompanying security risks could be enough to slow Copilot’s momentum, especially among large enterprises that prioritize data security above all else.


Check Point Software Technologies has been distinguished as a leader in the GigaOm Radar report for Security Policy as Code. The company’s recognition highlights its significant advancements in automating security policy management through code, reflecting an increasing trend towards integrating security into the development lifecycle. Security Policy as Code (SPaC) has emerged as a critical component in modern cybersecurity strategies, providing organizations with a means to define, […]

Tenable has unveiled “AI Aware,” a new security solution aimed at addressing the growing cybersecurity risks posed by artificial intelligence (AI) technologies and large language models (LLMs). The rapid adoption of AI has introduced unique vulnerabilities, and organizations are now scrambling to secure their environments. AI Aware is Tenable’s response to the critical challenges companies face when managing AI systems, offering proactive detection and risk management solutions. […]

The International Monetary Fund (IMF) has released its comprehensive research assessing the cyber resilience of the ecosystem supporting central bank digital currencies (CBDCs). The study, published at the end of August, addresses the growing need for updated payment systems and highlights both the opportunities and challenges presented by CBDCs. As central banks worldwide explore digital currencies, the IMF’s report stresses the critical importance of cybersecurity. According to […]

Hurricane Francine made landfall in Louisiana as a Category 2 storm, packing winds up to 100 mph and leaving significant damage in its wake. The storm struck the coast near Terrebonne Parish late on Wednesday, with widespread power outages reported across the region, impacting more than 245,000 residents. The storm brought with it torrential rains, resulting in flash flooding and the threat of deadly storm surges across […]

VISHNU RAJA
RYO YAMADA
HITORI GOTOH
IKUYO KITA